
Over 14,000 F5 BIG-IP APM Instances Exposed Amid CVE-2025-53521 Attacks
Summary
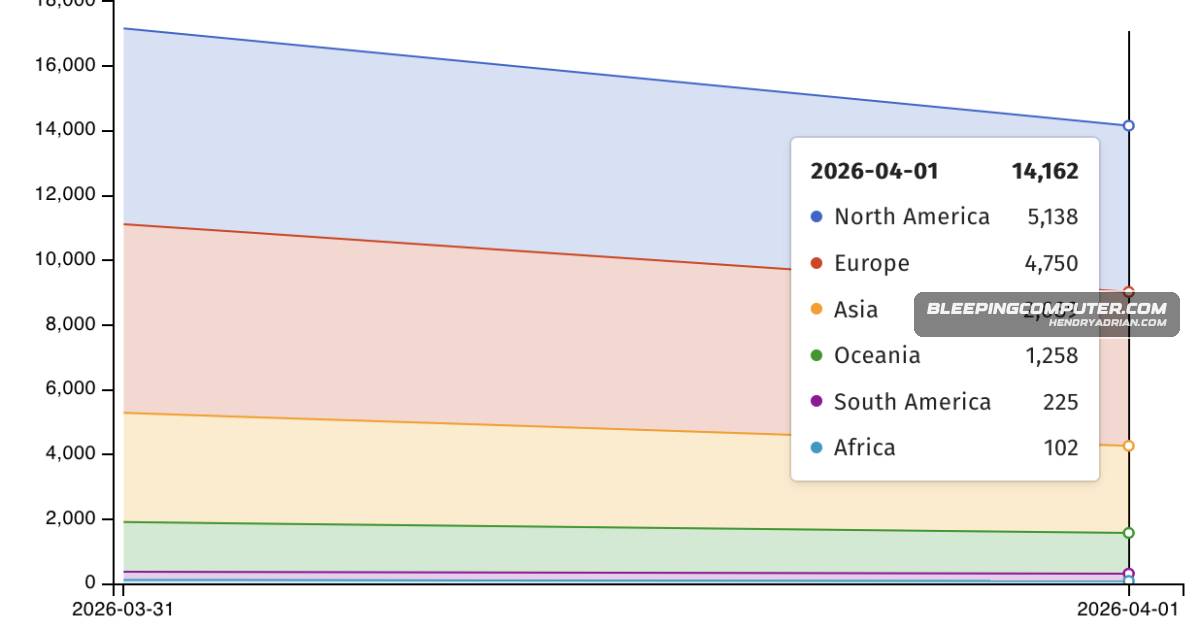
Shadowserver reports over 14,000 BIG-IP APM instances remain exposed amid active exploitation of CVE-2025-53521, recently reclassified as an RCE flaw. F5 advises investigating devices and rebuilding from known-good sources.
Key points
- Shadowserver reports over 14,000 BIG-IP APM systems remain exposed; it tracks more than 17,100 IPs with BIG-IP APM fingerprints.
- CVE-2025-53521 was initially disclosed as a denial-of-service flaw and later reclassified as remote code execution based on new information.
- F5 says the vulnerability has been exploited in vulnerable BIG-IP versions. Unprivileged attackers can execute code on unpatched systems with access policies configured on a virtual server.
- F5 published indicators of compromise and advises checking device disks, logs, and terminal history for malicious activity.
- F5 recommends rebuilding affected systems from a known-good source; UCS backups created after compromise may contain persistent malware.
- CISA ordered federal agencies to secure affected BIG-IP APM systems.
Article Details
- Vulnerability Types
- Remote code execution (RCE)
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available