cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · bleepingcomputer.com

Apache ActiveMQ Classic flaw enables remote command execution

Researchers disclosed CVE-2026-34197, an ActiveMQ Classic RCE involving Jolokia and remote Spring XML loading. Apache fixed it in 5.19.4 and 6.2.3; CVE-2024-32114 leaves some affected versions exposed without authentication.
Apr 8, 2026
Vulnerability & Exploit · securityweek.com

OpenSSL Patches CVE-2026-31790 Data Leakage Vulnerability

OpenSSL patched seven vulnerabilities, including moderate-severity CVE-2026-31790, which can expose uninitialized memory in applications using RSASVE key encapsulation. The flaws affect OpenSSL 3.0 through 3.6; versions 1.0.2 and 1.1.1 are not affected.

Apr 8, 2026
Vulnerability & Exploit · securityweek.com

13-Year-Old RCE Vulnerability Found in Apache ActiveMQ Classic

Horizon3.ai reports that CVE-2026-34197 enables RCE in Apache ActiveMQ Classic through Jolokia and VM transport mechanisms. The flaw is fixed in versions 5.19.4 and 6.2.3; a separate flaw can expose Jolokia without authentication on some versions.

Apr 8, 2026
Vulnerability & Exploit · thecyberexpress.com

Flowise CVE-2025-59528 Exploited via CustomMCP JavaScript Injection

VulnCheck reportedly detected exploitation of Flowise CVE-2025-59528, which enables code execution through unsafe CustomMCP configuration handling. The flaw is fixed in versions 3.0.6 and 3.1.1; the number of vulnerable public instances is unclear.

Apr 8, 2026
Vulnerability & Exploit · thehackernews.com

Docker Engine Flaw Can Bypass Authorization Plugins and Enable Host Access

CVE-2026-34040 lets a padded HTTP request bypass Docker Engine authorization plugins, potentially enabling privileged container creation and host access. Docker fixed the flaw in version 29.3.1; recommended workarounds include restricting API access and rootless mode.

Apr 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

Ninja Forms WordPress Flaw Exploited; Version 3.3.27 Fixes Critical RCE Risk

Wordfence reports active exploitation of CVE-2026-0740, an unauthenticated file-upload flaw in the Ninja Forms File Upload add-on that can enable PHP execution and site takeover. Version 3.3.27 fixes the issue.

Apr 7, 2026
Vulnerability & Exploit · bleepingcomputer.com

Flowise CVE-2025-59528 RCE Vulnerability Exploited in the Wild

VulnCheck reports limited in-the-wild exploitation of Flowise’s CVE-2025-59528, an unvalidated JavaScript injection flaw in the CustomMCP node. Upgrade to 3.1.1 or at least 3.0.6, and limit public exposure.

Apr 7, 2026
Vulnerability & Exploit · thecyberexpress.com

Two FortiClientEMS Flaws Under Active Exploitation Enable Unauthenticated Code Execution

The article reports active exploitation of two FortiClientEMS flaws that allow unauthenticated code execution. It outlines affected versions and Fortinet’s upgrade and hotfix guidance; CISA added CVE-2026-35616 to its KEV catalog.

Apr 7, 2026
Vulnerability & Exploit · kudelskisecurity.com

BlueHammer Windows Defender Zero-Day Enables Local Privilege Escalation

BlueHammer is a publicly disclosed Windows Defender zero-day with a public proof of concept that can let a local low-privilege user escalate access. The article says no official patch is available.

Apr 7, 2026
Vulnerability & Exploit · cloudsek.com

Hardcoded Android App Keys Can Expose Gemini API Access and User Files

CloudSEK found 32 hardcoded Google API keys with Gemini access across 22 popular Android apps. It confirmed that one key exposed files, including audio recordings, in the ELSA Speak project.

Apr 7, 2026
Vulnerability & Exploit · bleepingcomputer.com

BlueHammer Windows Zero-Day Exploit Leaked After Microsoft Disclosure Dispute

A researcher released BlueHammer, an unpatched Windows local privilege escalation exploit. Researchers say it can access the SAM database and enable SYSTEM-level compromise, though the proof of concept has bugs and is less reliable on Windows Server.

Apr 6, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited FortiClient EMS Flaw by April 9

CISA ordered federal agencies to patch FortiClient EMS against CVE-2026-35616 by April 9. Fortinet says the flaw is being exploited and released hotfixes for EMS 7.4.5 and 7.4.6.

Apr 6, 2026
Vulnerability & Exploit · securityonline.info

Check Point Reports DNS Tunneling Flaw in ChatGPT Runtime

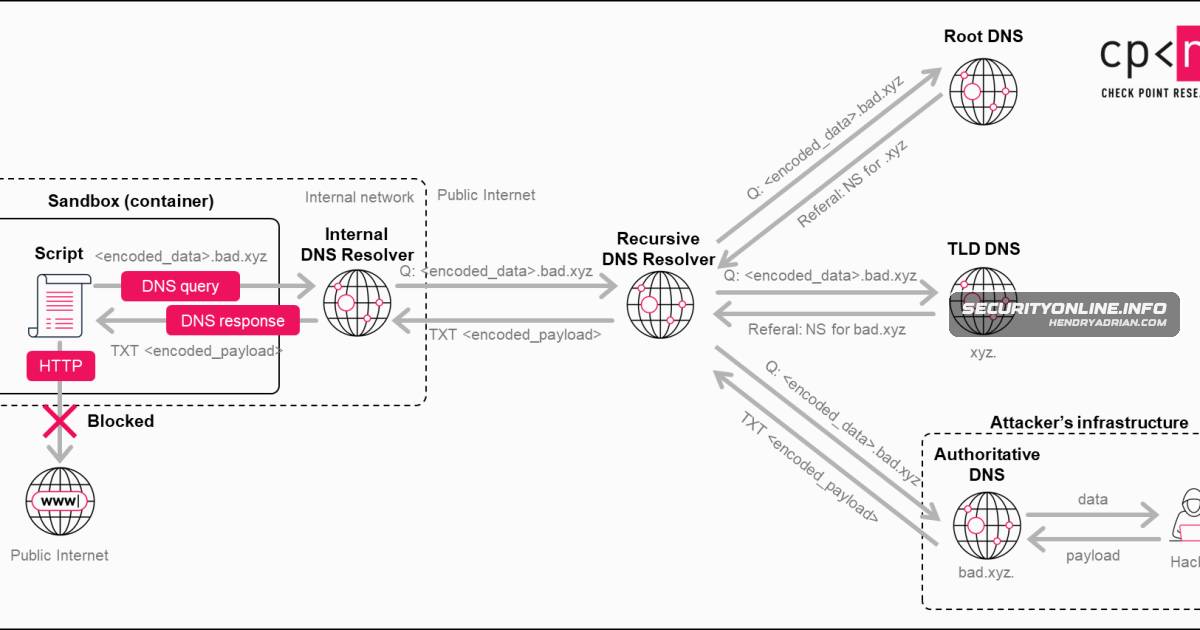
Check Point Research reported that DNS tunneling in ChatGPT’s Linux code-execution runtime could enable data exfiltration and a remote shell. A proof of concept leaked medical-document details; OpenAI deployed a fix on February 20, 2026.

Apr 6, 2026
Vulnerability & Exploit · bleepingcomputer.com

Fortinet Patches Actively Exploited FortiClient EMS Flaw CVE-2026-35616

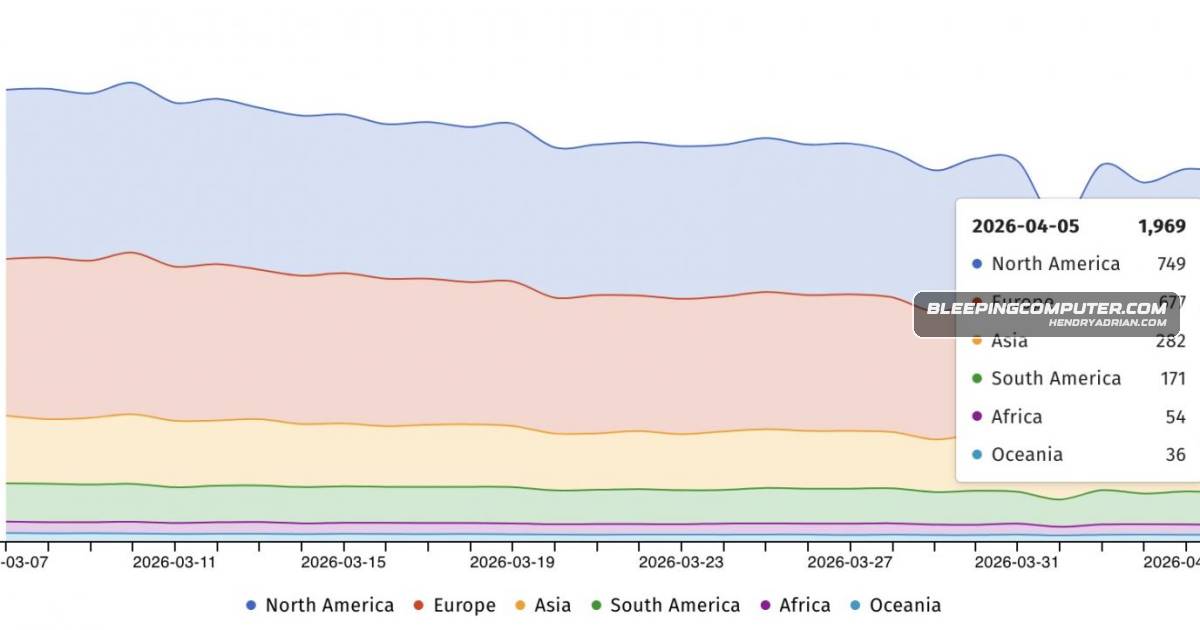
Fortinet says CVE-2026-35616, a pre-authentication access-control flaw in FortiClient EMS 7.4.5 and 7.4.6, is exploited in the wild. Hotfixes are available; 7.4.7 will include the fix. Shadowserver found over 2,000 exposed instances.

Apr 5, 2026
Vulnerability & Exploit · thehackernews.com

Fortinet Patches Actively Exploited CVE-2026-35616 in FortiClient EMS

Fortinet says CVE-2026-35616, a critical pre-authentication access-control flaw in FortiClient EMS 7.4.5–7.4.6, is being exploited. Hotfixes are available; a full fix is expected in version 7.4.7.

Apr 5, 2026
Vulnerability & Exploit · therecord.media

CISA Gives Agencies Two Weeks to Patch Exploited TrueConf Vulnerability

CISA set an April 16 deadline for federal agencies to patch actively exploited CVE-2026-3502 in TrueConf. Check Point says the TrueChaos campaign used compromised on-premises servers to distribute malicious updates.

Apr 3, 2026
Vulnerability & Exploit · securityweek.com

Check Point Says TrueConf Zero-Day Was Used in Asian Government Attacks

Check Point says attackers exploited CVE-2026-3502 by replacing updates on a compromised on-premises TrueConf server, distributing malware to government clients in Asia. TrueConf fixed the flaw in client 8.5.3.

Apr 3, 2026
Vulnerability & Exploit · securityweek.com

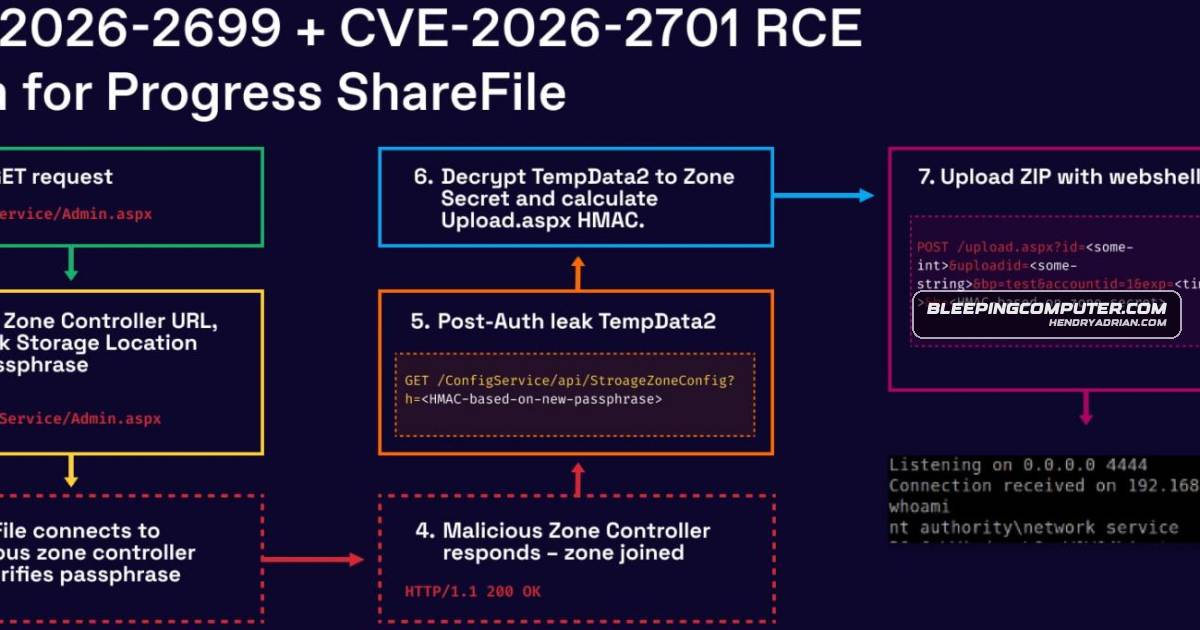
ShareFile Flaws Could Enable Unauthenticated Remote Code Execution

WatchTowr says two ShareFile flaws can be chained for unauthenticated RCE. ShareFile addressed them in version 5.12.4; versions 6.x are not affected.

Apr 3, 2026
Vulnerability & Exploit · thehackernews.com

Cisco Patches Critical IMC Authentication Bypass and SSM On-Prem RCE

Cisco patched two unauthenticated, remote vulnerabilities rated CVSS 9.8: an IMC authentication bypass and an SSM On-Prem flaw allowing root-level command execution. No exploitation in the wild was reported.

Apr 3, 2026
Vulnerability & Exploit · securityweek.com

Adversa AI Finds Claude Code Permission-Rule Bypass in Long Command Pipelines

Adversa AI says Claude Code may skip deny-rule and command-injection checks when command analysis exceeds 50 subcommands, potentially allowing prompt-injected repository instructions to run harmful commands.

Apr 2, 2026
Vulnerability & Exploit · securityweek.com

Apple Extends iOS 18.7.7 DarkSword Protections to More Devices

Apple has made iOS and iPadOS 18.7.7 available for additional devices, bringing DarkSword protections and fixes for other flaws. iVerify previously estimated roughly 200 million devices running iOS 18.4–18.6.2 may have been vulnerable.

Apr 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Patches Critical IMC Authentication Bypass Enabling Admin Access

Cisco says unauthenticated attackers can exploit CVE-2026-20093 to bypass authentication and gain Admin access to unpatched IMC systems. No workaround is available; Cisco urges customers to update. The article also covers patches for two other vulnerabilities.

Apr 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

Progress ShareFile Flaws Enable Unauthenticated RCE Through Chained Exploits

watchTowr says two ShareFile Storage Zones Controller flaws can be chained for unauthenticated access and remote code execution. Progress fixed them in version 5.12.4; no active exploitation was observed.

Apr 2, 2026
Vulnerability & Exploit · securityweek.com

Cisco Patches Critical and High-Severity Flaws Affecting Enterprise Products

Cisco patched eight critical and high-severity vulnerabilities affecting products including SSM On-Prem, EPNM, and IMC. The flaws could enable command execution, authentication bypass, privilege escalation, or information disclosure; Cisco reports no known exploitation.

Apr 2, 2026
PreviousPage 56 of 65 Next
© 2026 cyber.hendryadrian.com