
watchTowr Reports Active Exploitation of Citrix NetScaler CVE-2026-3055
Summary
watchTowr reports attackers have exploited CVE-2026-3055 in Citrix NetScaler ADC and Gateway since at least March 27, potentially leaking authentication and administrative session IDs. The flaw affects SAML identity provider-configured appliances.
Key points
- watchTowr reports exploitation since at least March 27, citing honeypot evidence of activity from known threat actor IPs.
- The flaw comprises at least two memory overread bugs affecting the /saml/login and /wsfed/passive endpoints.
- Exploitation can expose sensitive information, including authenticated administrative session IDs, potentially enabling appliance takeover.
- Affected versions are before 14.1-60.58, 13.1-62.23, and 13.1-37.262; Citrix says remediation is required for on-premises appliances configured as SAML identity providers.
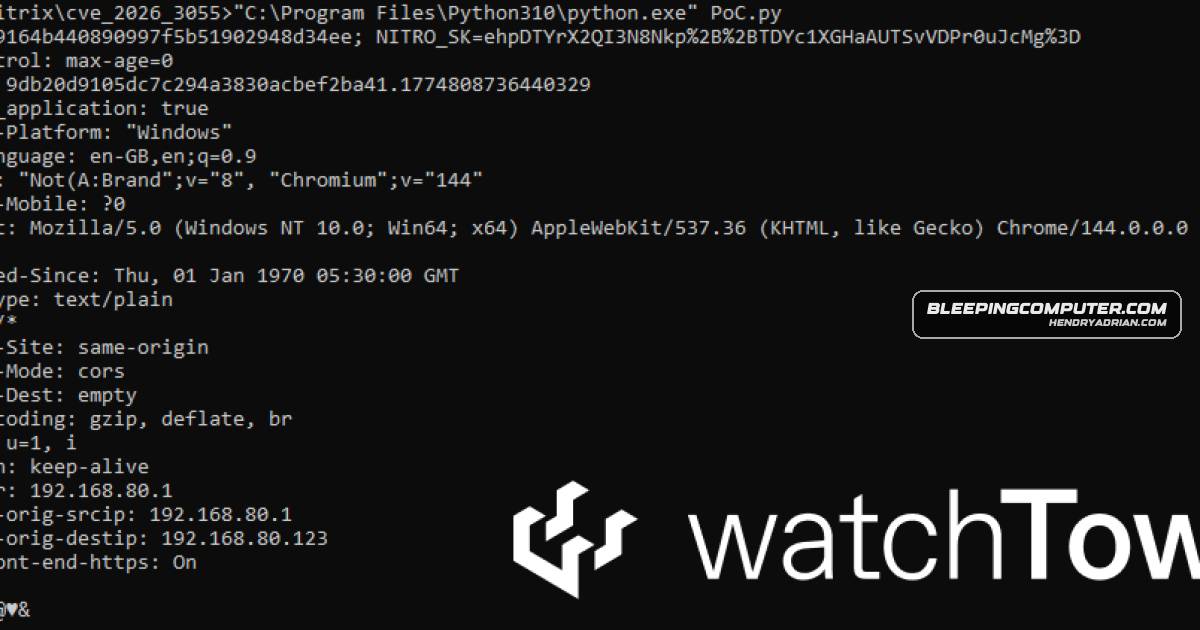
- watchTowr published a Python script to help defenders identify vulnerable hosts.
- Citrix's bulletin did not mention active exploitation, and the company had not responded to BleepingComputer by publication time.
Article Details
- Vulnerability Types
- Memory overread
- Severity
- Critical
- Affected Versions
- NetScaler ADC: versions before 14.1-60.58, 13.1-62.23, and 13.1-37.262
- NetScaler Gateway: versions before 14.1-60.58, 13.1-62.23, and 13.1-37.262
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- unknown
MITRE ATT&CK
CVE
Vendors
Products
NetScaler ADCA critical CVE-2026-3055 vulnerability in Citrix NetScaler ADC and NetScaler Gateway appliances is being actively exploited to extract sensitive authentication and administrative session IDs.NetScaler GatewayA critical CVE-2026-3055 vulnerability in Citrix NetScaler ADC and NetScaler Gateway appliances is being actively exploited to extract sensitive authentication and administrative session IDs.