
Datadog Details AiTM Phishing Campaign Targeting AWS Console Credentials
Summary
Datadog describes an active AiTM campaign using AWS-lookalike domains and reverse-proxy phishing to harvest validated AWS Console credentials and likely OTPs. It observed console logins from Mullvad VPN infrastructure within 20 minutes; AWS is coordinating takedown work
Key points
- The phishing kit proxies authentication to the legitimate AWS sign-in service in real time, validating submitted credentials and likely capturing OTPs and session material; OTP capture is unconfirmed.
- Two active infrastructure clusters used cloud-recovery[.]net and cloud-policy[.]com, with a related cloud-recovery[.]us domain. The domains share Registrar ID 3254; one cluster was registered and deployed on the day it was observed.
- Lures used AWS SES click-tracking links on awstrack[.]me and redirects through post[.]spmailtechnolo[.]com before reaching AWS-lookalike credential pages.
- Both phishing-kit servers exposed an administrative panel on TCP port 3000, which Datadog says could provide visibility into captured credentials and campaign management.
- Datadog observed AWS Console authentication from a Mullvad VPN egress IP within 20 minutes of credential submission; this suggests rapid use of harvested credentials, but does not establish how it was automated.
- The campaign remained active at the time of reporting. Datadog observed updated redirect logic and expanded anti-analysis controls, and said it reported the infrastructure to AWS, which was coordinating disruption efforts.
- Datadog recommends monitoring CloudTrail authentication events, MFA anomalies, privilege escalation, and DNS activity involving the identified domains.
Article Details
- Attack Vectors
- A phishing lure impersonated an AWS Security Hub notification and directed victims through AWS SES click-tracking and a multi-stage redirect chain.
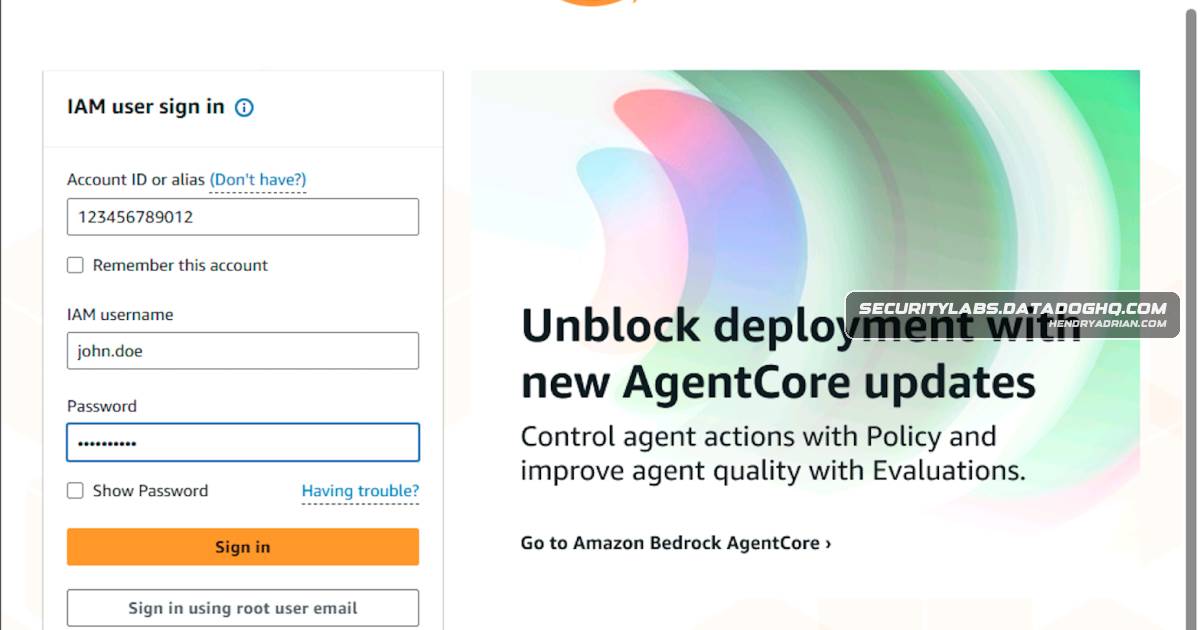
- Typosquatted domains hosted high-fidelity AWS sign-in pages that proxied authentication to the legitimate AWS endpoint in real time, harvesting validated credentials and likely OTPs and session material.
- The attacker used harvested credentials to access a compromised AWS Console account; access was observed within 20 minutes of credential submission from a Mullvad VPN egress IP.
- Defensive Notes
- Monitor CloudTrail ConsoleLogin events from the reported phishing-kit server IPs and investigate authentication from Mullvad VPN IPs.
- Hunt for DNS activity involving the reported cloud-recovery.net and cloud-policy.com domains.
- Review MFA anomalies and privilege-escalation activity for signs of post-phishing credential abuse.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cloud-policy[.]com | Phishing infrastructure root domain associated with Cluster 2. |
| DOMAIN | cloud-recovery[.]net | Phishing infrastructure root domain associated with Cluster 1. |
| HOSTNAME | signin[.]aws[.]cloud-policy[.]com | Credential-harvesting hostname associated with Cluster 2. |
| HOSTNAME | signin[.]aws[.]cloud-recovery[.]net | Credential-harvesting hostname serving a phishing page that mimicked AWS sign-in. |
| IPV4 | 178[.]16[.]54[.]142 | Phishing-kit server associated with Cluster 1. |
| IPV4 | 185[.]209[.]196[.]132 | Mullvad VPN egress IP from which the attacker accessed a compromised AWS Console account. |
| IPV4 | 69[.]67[.]172[.]30 | Phishing-kit server associated with Cluster 2. |
MITRE ATT&CK
T1036 · MasqueradingTyposquatted domains and AWS-like subdomain patterns were used to impersonate AWS services.T1078 · Valid AccountsThe attacker used harvested credentials to authenticate to a compromised AWS Console account.T1539 · Steal Web Session CookieA transparent reverse proxy relayed the AWS authentication flow and captured session material; real-time OTP capture was considered likely but not confirmed.T1566 · PhishingThe campaign used an email lure impersonating an AWS Security Hub notification.T1566.002 · Spearphishing LinkThe lure delivered phishing links through AWS SES click-tracking and a multi-stage redirect chain.T1583 · Acquire InfrastructureThe operators registered and rapidly deployed phishing domains and related infrastructure using a shared registrar.
Vendors
Products
AWS Identity and Access ManagementAWS Identity and Access Management product landing page served from the phishing domain (click to enlarge)AWS Management Consolephishing campaign using typosquatted domains and a reverse-proxy phishing kit to harvest validated AWS Console credentials and likely one-time passwords (OTPs).AWS Security Hub[T1566 ] Phishing – Delivery of credential-harvesting lure impersonating AWS Security Hub.AWS SESThe operation used AWS SES click-tracking links, rapid infrastructure rotation, and post-compromise access from a Mullvad VPN egress node with console logins observed within 20 minutes of credential submission.CloudTrailDatadog includes out-of-the-box security rules for monitoring suspicious behavior related to AWS cloudtrail: