
PixRevolution Android Trojan Uses Live Screen Monitoring to Redirect Brazil PIX Transfers
Summary
Zimperium describes PixRevolution, an Android trojan that uses fake app pages, Accessibility and MediaProjection APIs, and live operator control to replace PIX recipients and confirm transfers.
Key points
- Zimperium says its analysis of 14 samples found PixRevolution droppers impersonating Brazilian brands and distributing a payload through fake Google Play Store pages.
- The malware requests Android Accessibility access to monitor screen text and interact with interface elements across apps.
- MediaProjection screen capture streams the victim’s display to an operator, while transaction-related Portuguese phrases trigger alerts.
- During a PIX transfer, the operator can direct the trojan to replace the recipient field using ACTION_SET_TEXT and confirm the transfer with a simulated gesture.
- The trojan uses a persistent TCP connection on port 9000 and a secondary HTTP telemetry endpoint on port 3030.
- The article says the malware is designed to work across financial apps rather than relying on a fixed list of target banks.
Article Details
- Attack Vectors
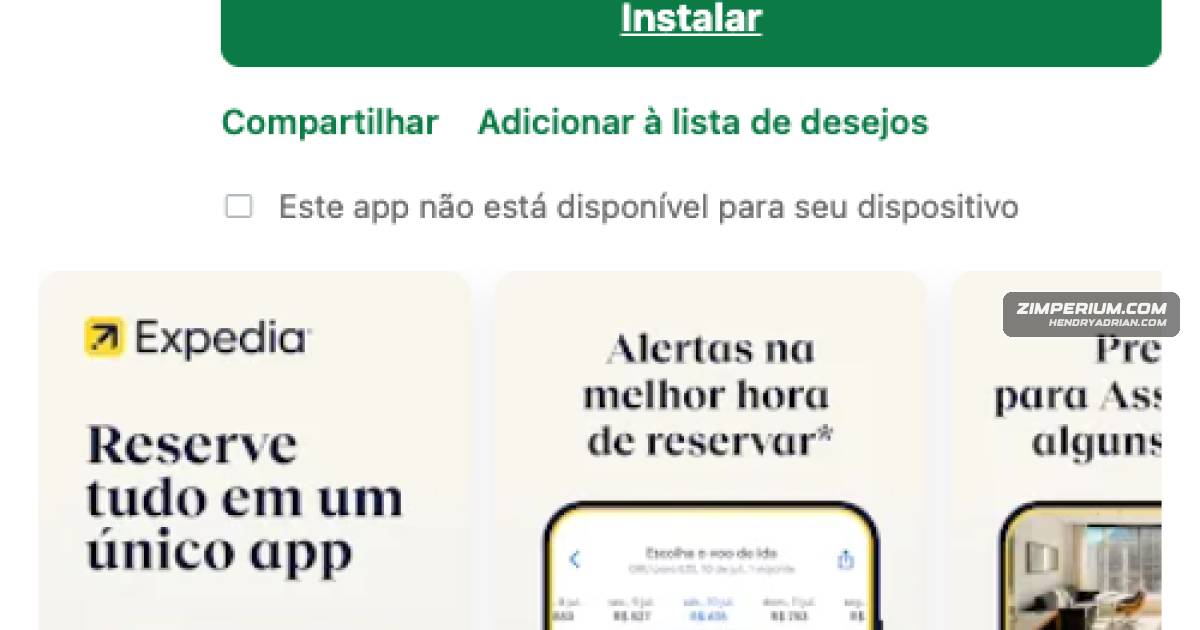
- Fake Google Play Store pages on attacker-controlled domains distribute malicious APKs.
- The campaign impersonates Brazilian brands, including Expedia, Correios, Sicredi, STJ, and AVG, to make malicious apps appear legitimate.
- Dropper APKs embed the PixRevolution payload as assets/update.apk and use Android's PackageInstaller API to install it.
- Social engineering prompts victims to enable the malware's Accessibility service.
- An operator monitors the victim's screen through MediaProjection, then uses Accessibility actions to replace a PIX recipient and confirm the transfer.
- Defensive Notes
- Use on-device behavioral detection to identify the combination of Accessibility service abuse, unauthorized MediaProjection screen capture, and persistent C2 communication.
- Treat requests to enable Accessibility services from apps obtained through unofficial or impersonated store pages as suspicious.
- The article identifies Zimperium's Mobile Threat Defense (MTD) and zDefend as providing behavioral detection for this threat.
MITRE ATT&CK
T1417The Accessibility service reads on-screen text across applications using a typeAllMask configuration.T1426C2 heartbeat messages include device ID, battery level, and network type.T1437The malware maintains a TCP C2 connection on port 9000 and uses a secondary HTTP endpoint on port 3030 for telemetry.T1476Fake Google Play Store pages on attacker-controlled domains distribute malicious APKs to victims.T1513The malware uses MediaProjection to capture screen frames and stream them to C2 in real time.T1516The malware replaces a PIX recipient field with the attacker's key using ACTION_SET_TEXT and simulates transaction confirmation with dispatchGesture().T1541The malware starts a foreground service to keep MediaProjection screen capture running.T1628.001The dropper conceals its icon after installing the RAT payload.T1655.001Dropper APKs use familiar brand names, icons, and descriptions to appear legitimate.T1660Attacker-controlled pages impersonate Brazilian brands to lure users into installing malicious apps.
Malware
Vendors
Products
AndroidPixRevolution is a novel Android banking trojan that streams victims’ screens in real time and uses an operator (human or AI) to replace PIX recipients during a transfer, redirecting funds instantly.Google Play StoreIt is distributed via convincing fake Google Play Store pages and impersonated Brazilian brands, exploiting Accessibility and MediaProjection APIs to operate stealthily and evade signature-based detection.Mobile Runtime Protection (zDefend)Zimperium’s Mobile Threat Defense (MTD) and Mobile Runtime Protection (zDefend) provide on-device, behavioral detection that identifies PixRevolution the moment it activates on a device.Mobile Threat DefenseZimperium’s Mobile Threat Defense (MTD) and Mobile Runtime Protection (zDefend) provide on-device, behavioral detection that identifies PixRevolution the moment it activates on a device.PixPixRevolution is a novel Android banking trojan that streams victims’ screens in real time and uses an operator (human or AI) to replace PIX recipients during a transfer, redirecting funds instantly.