
Rust-Based VENON Banking Trojan Targets 33 Brazilian Financial and Digital-Asset Platforms
Summary
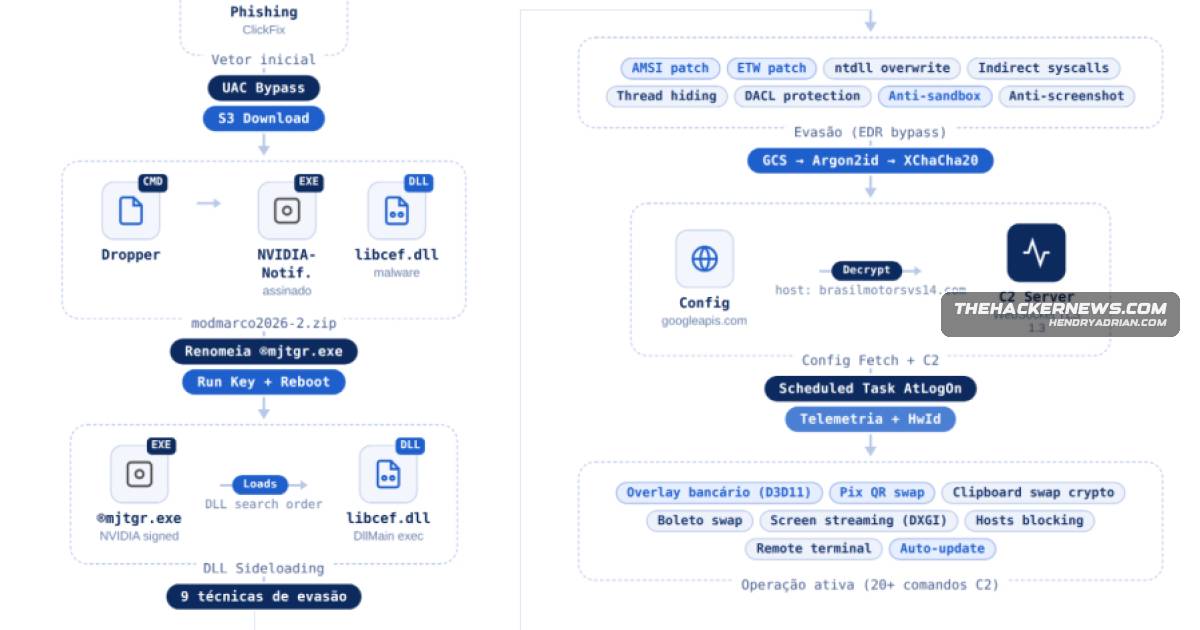
Researchers describe VENON, a Rust-based banking trojan targeting Brazilian Windows users. It uses DLL side-loading, evasion techniques, Itaú shortcut hijacking and credential-stealing overlays; attribution remains unknown.
Key points
- VENON is a newly disclosed Rust-based banking trojan targeting Brazilian Windows users; researchers have not attributed it to a known group or campaign.
- Its suspected delivery chain uses social engineering, possibly ClickFix, to deliver a ZIP archive and launch a malicious DLL through DLL side-loading.
- The malware performs nine reported evasion techniques, including anti-sandbox checks, indirect syscalls, ETW bypass and AMSI bypass.
- It retrieves configuration from Google Cloud Storage, installs a scheduled task and establishes a WebSocket command-and-control connection.
- VENON monitors active window titles and browser domains to target 33 financial institutions and digital-asset platforms with credential-stealing overlays.
- Its Itaú-specific LNK hijacking replaces legitimate shortcuts to redirect users to an attacker-controlled webpage; an uninstall step can restore the shortcuts.
Article Details
- Attack Vectors
- VENON is distributed through DLL side-loading to launch a malicious DLL.
- The article says the campaign is suspected of using ClickFix-style social engineering to trick users into downloading a ZIP archive containing payloads delivered through a PowerShell script.
- VENON retrieves configuration from a Google Cloud Storage URL and establishes a WebSocket connection to a command-and-control server.
- VENON monitors window titles and active browser domains, then displays fake overlays to steal credentials when targeted banking or digital asset services are opened.
- VENON replaces shortcuts associated with the Itaú banking application with tampered shortcuts that redirect victims to a web page controlled by the threat actor.
- Separately, SORVEPOTEL is reported to spread through WhatsApp's desktop web version by abusing previously authenticated chats to send malicious lures.
MITRE ATT&CK
T1010 · Application Window DiscoveryVENON monitors window titles and active browser domains to detect targeted banking and digital asset services.T1053.005 · Scheduled TaskVENON installs a scheduled task after retrieving its configuration.T1056.002 · GUI Input CaptureVENON uses fake banking overlays to facilitate credential theft.T1059.001 · PowerShellThe suspected delivery chain uses a PowerShell script to deliver payloads in a ZIP archive.T1071.001 · Web ProtocolsVENON establishes a WebSocket connection to its command-and-control server.T1497.001 · System ChecksVENON performs anti-sandbox checks before initiating malicious actions.T1547.009 · Shortcut ModificationVENON replaces shortcuts associated with the Itaú banking application with tampered versions.T1574.002 · DLL Side-LoadingVENON uses DLL side-loading to launch a malicious DLL.
Malware
AstarothThe attack hinges on abusing previously authenticated chats to deliver malicious lures directly to victims, ultimately resulting in the deployment of banking malware such as Maverick, Casbaneiro, or Astaroth.CasbaneiroThe attack hinges on abusing previously authenticated chats to deliver malicious lures directly to victims, ultimately resulting in the deployment of banking malware such as Maverick, Casbaneiro, or Astaroth.Coyotemonitoring, and LNK hijacking techniques from Latin American families like Grandoreiro, Mekotio, and Coyote.Grandoreirooverlay, active window monitoring, and LNK hijacking techniques from Latin American families like Grandoreiro, Mekotio, and Coyote.MaverickThe attack hinges on abusing previously authenticated chats to deliver malicious lures directly to victims, ultimately resulting in the deployment of banking malware such as Maverick, Casbaneiro, or Astaroth.Mekotioactive window monitoring, and LNK hijacking techniques from Latin American families like Grandoreiro, Mekotio, and Coyote.SORVEPOTELThe campaign uses DLL side-loading, nine evasion techniques, Google Cloud Storage-hosted configs, Itaú-specific shortcut hijacking, and has links to WhatsApp-distributed SORVEPOTEL lure chains.VENONResearchers disclosed VENON, a Rust-written banking trojan targeting Brazilian Windows users that borrows overlay, active window monitoring, and LNK hijacking techniques from Latin American families like Grandoreiro,
Products
Google Cloud StorageThe campaign uses DLL side-loading, nine evasion techniques, Google Cloud Storage-hosted configs, Itaú-specific shortcut hijacking, and has links to WhatsApp-distributed SORVEPOTEL lure chains.Microsoft WindowsResearchers disclosed VENON, a Rust-written banking trojan targeting Brazilian Windows users that borrows overlay, active window monitoring, and LNK hijacking techniques from Latin American families like Grandoreiro,PowerShellDistribution leverages DLL side-loading and social engineering (ZIP/PowerShell lures), with configs pulled from Google Cloud Storage and a WebSocket C2 channel.WhatsAppThe campaign uses DLL side-loading, nine evasion techniques, Google Cloud Storage-hosted configs, Itaú-specific shortcut hijacking, and has links to WhatsApp-distributed SORVEPOTEL lure chains.