
MicroStealer Uses Layered NSIS, Electron and Java Chain to Steal Data
Summary
ANY.RUN reports observing MicroStealer in more than 40 sandbox sessions in under a month. Its NSIS-to-Electron-to-Java chain steals browser data, screenshots and wallet files, with obfuscation and redundant exfiltration channels.
Key points
- ANY.RUN says it observed MicroStealer in more than 40 sandbox sessions in less than a month; compromised or impersonated accounts were among the reported distribution methods.
- The analyzed chain uses an NSIS installer, an Electron loader, an embedded JRE disguised as miicrosoft.exe, and the soft.jar payload.
- The analysis describes LZ-String compression and control-flow obfuscation in the Node.js component, ZKM obfuscation in Java, and checks for virtual-machine processes.
- MicroStealer targets browser credentials and cookies, screenshots, cryptocurrency wallet files, and Discord account data; it also attempts LSASS token manipulation when LSA protection is disabled.
- It creates a Windows Task Scheduler task that runs at user logon with highest privileges.
- The malware archives collected data and sends it to a Discord webhook and an attacker-controlled server. The article recommends behavioral sandbox analysis, infrastructure monitoring, and threat hunting.
Article Details
- Attack Vectors
- Distribution was reported through compromised or impersonated accounts.
- A malicious website's “Download Now” button executes JavaScript that downloads a payload and sends victim system details to a Discord server.
- The infection chain uses the RocobeSetup.exe NSIS installer, Game Launcher.exe Electron loader, disguised miicrosoft.exe JRE executable, and soft.jar stealer.
- The installer presents a UAC elevation prompt; the malware also creates an ONLOGON scheduled task with highest privileges.
- MicroStealer steals browser credentials and session cookies, collects wallet files and screenshots, and exfiltrates collected data to a Discord webhook and attacker-controlled servers.
- Defensive Notes
- Monitor newly observed infrastructure and suspicious connections to Discord webhooks and external servers.
- Execute suspicious files in a controlled sandbox to confirm behavior and expose the full delivery and collection chain.
- Pivot from confirmed indicators to identify related infrastructure, samples, and variants using the same delivery chain.
- Use observed behaviors, including browser-profile access and creation of an ONLOGON task with highest privileges, to support detection and triage.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 78smp[.]com | Attacker-controlled domain hosting an endpoint used for data exfiltration. |
| DOMAIN | banterplugins[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | buradabmwking[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | buradakimvar[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | churilend[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | crushfall[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | dashlune[.]xyz | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | eldrynworld[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | kittenscraft[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | kittiesmc[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | kittycraftmc[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | slumpcute[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | velyonar[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | vrcpluginhub[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | welarith[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
| DOMAIN | zarvethion[.]com | Domain listed as attacker infrastructure used for distribution or exfiltration. |
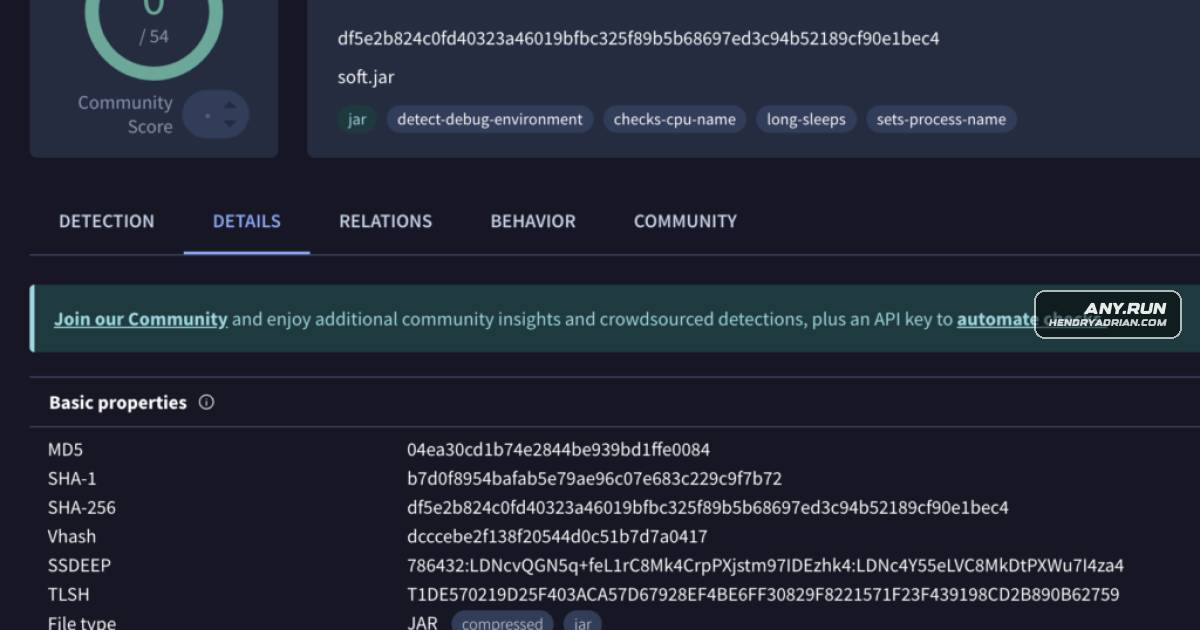
| MD5 | 04ea30cd1b74e2844be939bd1ffe0084 | MD5 of soft.jar, identified as the MicroStealer core. |
| MD5 | 23a705fa71da6a9191618aedc1144c4a | MD5 of the malicious RocobeSetup.exe NSIS installer. |
| MD5 | a137bf79a2d5f1c8104af40ec93e4e66 | MD5 of the malicious Game Launcher.exe Electron loader. |
| SHA1 | 755c21dd36a49086f98c87a172b900e6424f467a | SHA-1 of the malicious RocobeSetup.exe NSIS installer. |
| SHA1 | b7d0f8954bafab5e79ae96c07e683c229c9f7b72 | SHA-1 of soft.jar, identified as the MicroStealer core. |
| SHA1 | c83d75bf9f9fda4e6ef7b2c575bc9d3d82d6590b | SHA-1 of the malicious Game Launcher.exe Electron loader. |
| SHA256 | 05f0c8e89248d3477115d9f62b20ca8a95d925140c727e975ab9f3025a5ad01d | SHA-256 of the malicious Game Launcher.exe Electron loader. |
| SHA256 | 9cf1d4f87d9f2edf53ce681b59c209f57a805e6157693e784d9d946fc3b17a04 | SHA-256 of the malicious RocobeSetup.exe NSIS installer. |
| SHA256 | df5e2b824c0fd40323a46019bfbc325f89b5b68697ed3c94b52189cf90e1bec4 | SHA-256 of soft.jar, identified as the MicroStealer core. |
| URL | hxxps[:]//78smp[.]com/m/ | Attacker-controlled server endpoint used to exfiltrate collected data. |
| URL | hxxps[:]//discord[.]com/api/webhooks/1460660027969896695/FQ2nam1vUVDwLbiTZCPen9C53eBMg_qB3-z8pGRtZ3ZerbyflDnzfmJVLpgElxMNfO41 | Specific Discord webhook URL identified as an exfiltration destination. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe Node.js component uses compressed strings and flattened control flow, while the Java module is obfuscated with ZKM.T1036.005 · Match Legitimate Resource Name or LocationThe embedded JRE executable is named miicrosoft.exe, and the Electron loader is presented as Game Launcher.exe.T1053.005 · Scheduled TaskIt creates an App_<username> scheduled task triggered at logon with a five-second delay and highest privileges.T1059.001 · PowerShellA PowerShell script launches Game Launcher.exe with Start-Process -Verb RunAs to request elevation.T1059.003 · Windows Command ShellThe malware invokes schtasks to create its ONLOGON scheduled task.T1082 · System Information DiscoveryThe malware collects host details including OS version, hostname, username, environment variables, region, and time zone.T1113 · Screen CaptureIt captures the current desktop with java.awt.Robot and saves the screenshot as a PNG.T1134.001 · Token Impersonation/TheftWhen LSA protection is disabled, the malware duplicates an LSASS token and impersonates it in the current thread.T1204.002 · Malicious FileThe victim executes the delivered NSIS installer or Game Launcher executable.T1497.001 · System ChecksThe Java module checks for VMware, VirtualBox, QEMU, Xen, and other VM-related processes and halts if a match is found.T1539 · Steal Web Session CookieIt extracts browser session cookies for exfiltration.T1552.001 · Credentials In FilesIt copies cryptocurrency wallet files and browser wallet-extension storage for exfiltration.T1555.003 · Credentials from Web BrowsersIt accesses supported browser profiles and extracts saved information, including passwords and autofill data, using DPAPI.T1560.001 · Archive via UtilityCollected screenshots and other stolen data are packaged into ZIP archives before exfiltration.T1567.004 · Exfiltration Over WebhookIt sends collected archives and beacon information to a Discord webhook.
Malware
Vendors
Products
Coinbaseput("Coinbase", "Local Extension Settingshnfanknocfeofbddgcijnmhnfnkdnaad"); Discordbrowser credentials, session cookies, screenshots, and wallet files, exfiltrating collected data to Discord webhooks and attacker-controlled servers.Exodusput("Exodus", appData + "Exodusexodus.wallet"); Google Chromeput("Chrome", localAppData + "GoogleChromeUser Data"); MetaMaskput("Metamask", "Local Extension Settingsnkbihfbeogaeaoehlefnkodbefgpgknn"); OperaThe stealer targets Chromium-based browsers, Opera/Opera GX, Discord (via injection), and both browser and desktop cryptocurrency wallets, extracting credentials, session cookies, screenshots, and wallet files.Opera GXThe stealer targets Chromium-based browsers, Opera/Opera GX, Discord (via injection), and both browser and desktop cryptocurrency wallets, extracting credentials, session cookies, screenshots, and wallet files.Phantomput("Phantom", "Local Extension Settingsbfnaelmomeimhlpmgjnjophhpkkoljpa"); Steamand TI feeds enabled rapid behavior confirmation, IOC extraction (file hashes, domains, webhook URLs, Steam API key), and recommended triage and hunting workflows to accelerate detection and containment.Trust Walletput("Trust Wallet", "Local Extension Settingsegjidjbpglichdcondbcbdnbeeppgdph");
Tools
Detect It EasyRocobeSetup is an NSIS installer (Nullsoft Scriptable Install System), which becomes immediately apparent when analyzing the binary using Detect It Easy (DIE) (Detect It Easy).Ghidradirectory containing an ASAR archive and a Node.js project indicates the use of Electron. Analysis in Ghidra confirms this: a modal window prompts to load electron.pdb, and both the strings and the entry pointThreadtearIn this case, Threadtear was used with a set of ZKM-focused modules, including string deobfuscation, access restoration, flow deobfuscation, and several additional modules for bytecode cleanup.
Countries
GermanyAnalysis of MicroStealer-related submissions to the ANY.RUN sandbox shows that 50% of observed sample uploads originated from the United States and Germany, pointing to notable activity in these regions.United StatesAnalysis of MicroStealer-related submissions to the ANY.RUN sandbox shows that 50% of observed sample uploads originated from the United States and Germany, pointing to notable activity in these regions.
Industries
EducationEarly activity points to distribution through compromised or impersonated accounts, with education and telecommunications among the affected sectors.TelecommunicationsEarly activity points to distribution through compromised or impersonated accounts, with education and telecommunications among the affected sectors.