
ClickFix Campaign Uses Trojanized Shotcut ZIPs to Deliver REMCOS RAT
Summary
Cybereason GSOC reports REMCOS 7.1.0 campaigns using ClickFix lures and trojanized portable Shotcut ZIPs. A DLL loader chain uses callback-based shellcode execution to load the RAT, which can steal credentials and enable surveillance.
Key points
- Cybereason GSOC reports observing increased REMCOS infections delivered through trojanized portable Shotcut ZIP packages.
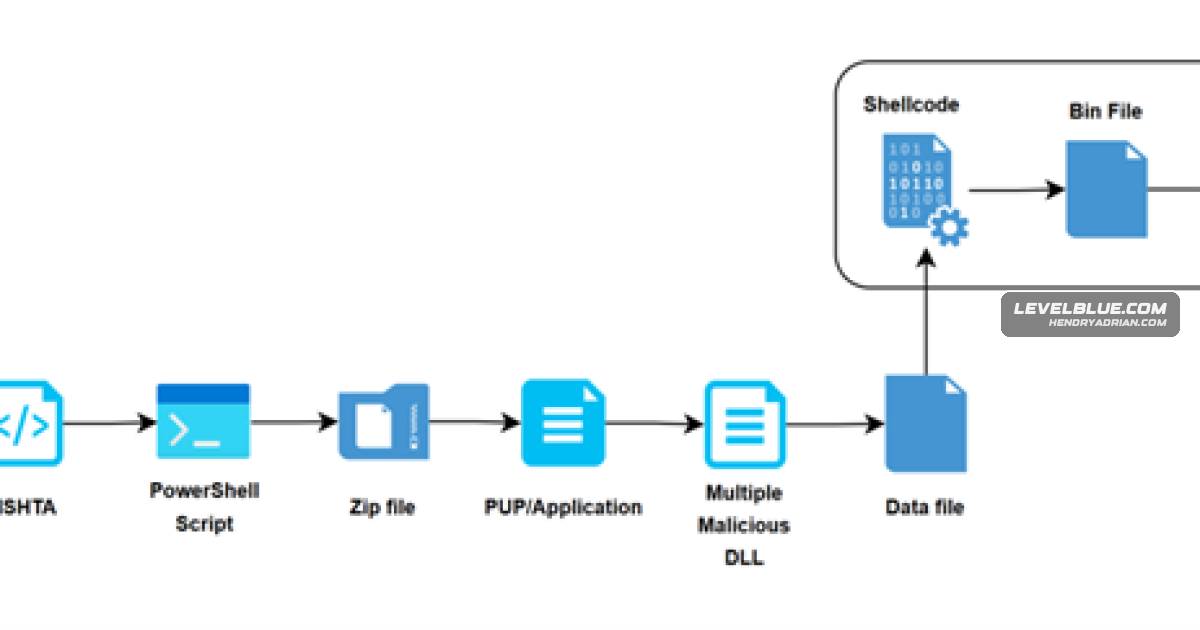
- The described infection chain uses a ClickFix lure, mshta.exe, PowerShell, and a ZIP archive disguised with a .pdf extension.
- The legitimate Shotcut executable is reportedly unchanged; malicious DLLs, including libmlt-7.dll, load additional components that stage the payload.
- The analysis describes shellcode execution through callback-style APIs such as EnumSystemCodePagesW, followed by in-memory loading of the final REMCOS payload from across.bin.
- The observed REMCOS 7.1.0 capabilities include keylogging, browser credential and cookie theft, clipboard capture, screenshots, and microphone or webcam access.
- The article recommends isolating and investigating affected endpoints, resetting credentials, reimaging systems, verifying software hashes, and blocking identified indicators, including the reported C2 domain pro.ip-api[.]com.
Article Details
- Attack Vectors
- ClickFix social engineering uses a fake CAPTCHA to prompt victims to execute a malicious command.
- The mshta.exe process downloads remote JavaScript, which spawns PowerShell to download a ZIP archive disguised with a .pdf extension.
- A trojanized portable Shotcut package replaces the legitimate libmlt-7.dll with a malicious loader that loads additional DLLs and the REMCOS payload.
- The loader uses callback-based shellcode execution through EnumSystemCodePagesW to run shellcode that loads across.bin into memory.
- REMCOS communicates persistently with its C2 server and is used for credential theft, keylogging, surveillance, and data exfiltration.
- Defensive Notes
- Download software from official sources and verify package hashes against values published by the official source.
- Isolate affected endpoints; preserve a forensic image if an investigation will be conducted, or restore the system from a trusted baseline.
- Reset credentials associated with affected accounts, especially administrative accounts, and investigate potentially exposed data.
- Block the identified C2 indicator across endpoints, networks, and security appliances.
- Reimage infected systems to ensure eradication.
- Educate users about supply-chain compromises and ClickFix/social-engineering lures.
- Restrict remote-access tool installation to explicitly approved software and audit new installations.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | pro[.]ip-api[.]com | Identified as the C2 and callback domain used by the REMCOS campaign. |
| URL | hxxps[:]//pro[.]ip-api[.]com/line/?key=QPVvv1rHQJD2pd2&fields=25948155 | C2 URL identified in the article for persistent REMCOS communications. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe loader surrounds the deobfuscated payload with random junk bytes to hinder memory analysis.T1055 · Process InjectionThe loader executes shellcode through a callback-style enumeration API, using the shellcode address as the callback pointer.T1056.001 · KeyloggingThe REMCOS payload captures keystrokes with an online/offline keylogger.T1059.001 · PowerShellPowerShell downloads the second-stage archive disguised as a .pdf and extracts it using TAR.T1071.001 · Web ProtocolsREMCOS uses persistent encrypted communications with its C2 server over HTTPS.T1105 · Ingress Tool TransferThe infection downloads remote JavaScript and a second-stage archive from attacker C2 infrastructure.T1112 · Modify RegistryREMCOS modifies the registry, including changing the EnableLUA value.T1113 · Screen CaptureThe article reports that REMCOS captures screenshots and sends them to its operator.T1115 · Clipboard DataREMCOS captures clipboard contents, including copied passwords and other sensitive text.T1123 · Audio CaptureThe article reports REMCOS access to the victim's microphone for surveillance.T1125 · Video CaptureThe article reports REMCOS access to the webcam for surveillance or capture.T1218.005 · Mshtamshta.exe downloads remote JavaScript that spawns the PowerShell stage.T1548.002 · Bypass User Account ControlThe payload sets the EnableLUA registry value to 0 to suppress UAC prompts and enable privileged actions.T1555.003 · Credentials from Web BrowsersREMCOS extracts stored logins, passwords, cookies, autofill data, and profiles from Chrome and Firefox.T1574.001 · DLLThe attackers replaced Shotcut's legitimate libmlt-7.dll with a malicious DLL that loads additional malicious libraries.
Malware
Products
Microsoft WindowsWindows offers several enumeration APIs designed to iterate over system resources such as windows, locales, fonts, date formats, processes, and more.ShotcutCybereason GSOC observed a rise in REMCOS RAT campaigns that trojanize legitimate software packages (notably portable Shotcut ZIPs) by replacing genuine DLLs with malicious ones to load multi-stage payloads.