
BlackSanta EDR Killer Targets HR in Resume-Themed ISO Campaign
Summary
Aryaka researchers describe a Russian-speaking actor’s year-long campaign targeting HR departments with resume-themed ISO files. The infection chain deploys BlackSanta, which weakens Defender and terminates security processes; the actor and target organizations remain未明
Key points
- Aryaka researchers say a Russian-speaking threat actor targeted HR departments for over a year; the targeted organizations and actor’s identity were not disclosed.
- The researchers suspect spear-phishing delivered ISO files disguised as resumes, though the initial access method is unclear.
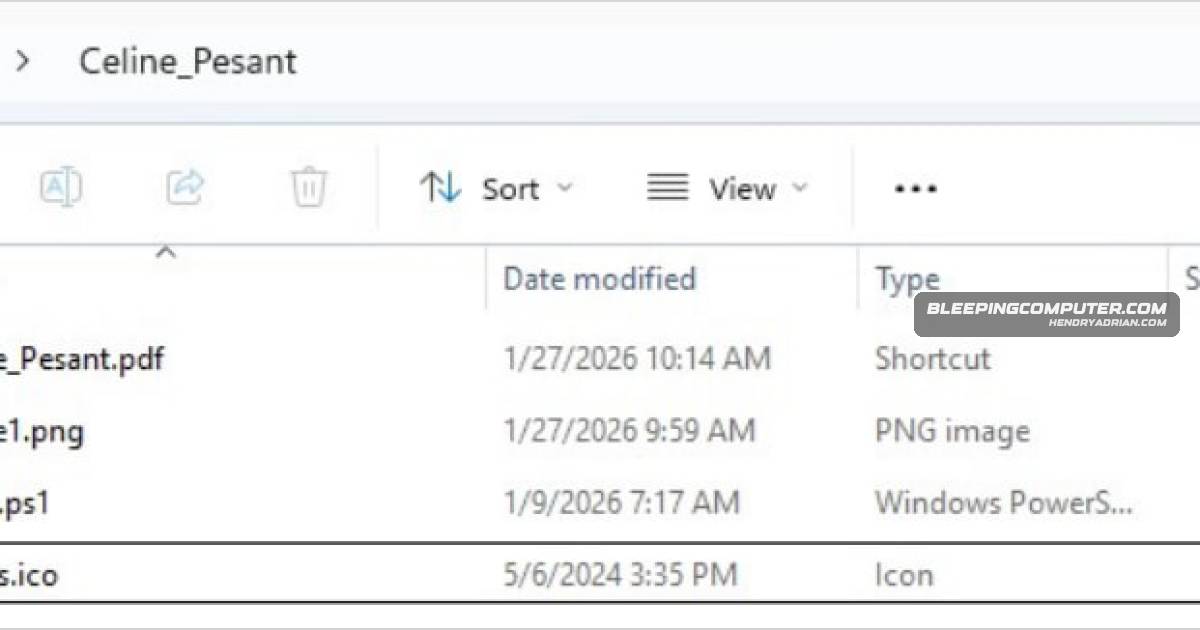
- An analyzed ISO contained a disguised Windows shortcut that launched PowerShell, extracted code hidden in an image using steganography, and ran it in memory.
- The infection chain used DLL sideloading with a legitimate SumatraPDF executable and malicious DWrite.dll.
- BlackSanta modifies Microsoft Defender settings, suppresses Windows notifications, and uses a hardcoded list to identify security processes for kernel-level termination.
- The campaign also downloaded RogueKiller and IObitUnlocker drivers, which researchers say provide low-level access to memory and processes.
- Researchers could not retrieve the final payload because the command-and-control server was unavailable during their examination.
Article Details
- Attack Vectors
- Researchers suspect spear-phishing emails directed HR targets to ISO files masquerading as resumes, potentially hosted on cloud storage.
- A shortcut inside an analyzed ISO launched PowerShell, which extracted code hidden in an image using steganography and executed it in memory.
- A legitimate SumatraPDF executable loaded a malicious DWrite.dll through DLL sideloading.
- The malware fingerprinted systems, checked for sandboxes, virtual machines, and debugging tools, and communicated with a command-and-control server to download additional payloads.
- BlackSanta altered Microsoft Defender settings, suppressed notifications, and used loaded drivers to identify and terminate security processes at the kernel level.
- The campaign used process hollowing to execute downloaded payloads inside legitimate processes and downloaded signed drivers including RogueKiller Antirootkit and IObitUnlocker.
MITRE ATT&CK
T1027.003 · SteganographyThe PowerShell script extracted code hidden in an image using steganography.T1036.008 · Masquerade File TypeAn ISO contained a Windows shortcut disguised as a PDF file.T1055.012 · Process HollowingAdditional downloaded payloads were executed through process hollowing inside legitimate processes.T1057 · Process DiscoveryBlackSanta enumerated running processes and matched their names against a hardcoded list of security tools.T1059.001 · PowerShellThe shortcut launched PowerShell to execute a script.T1082 · System Information DiscoveryThe malware performed system fingerprinting before continuing its execution.T1105 · Ingress Tool TransferThe malware downloaded a ZIP archive and additional payloads from its C2 server.T1112 · Modify RegistryBlackSanta modified a Registry value to reduce telemetry and automatic sample submission.T1497.001 · System ChecksThe malware checked for sandboxes, virtual machines, and debugging tools to avoid execution in those environments.T1562.001 · Disable or Modify ToolsBlackSanta added Microsoft Defender exclusions and used drivers to terminate security processes.T1566.001 · Spearphishing AttachmentResearchers suspect spear-phishing emails delivered ISO files masquerading as resumes.T1574.002 · DLL Side-LoadingA legitimate SumatraPDF executable loaded a malicious DWrite.dll.
Malware
Vendors
Products
Microsoft Defender Antimalware PlatformBlackSanta adds Microsoft Defender exclusions for ‘.dls’ and ‘.sys’ files, and modifies a Registry value to reduce telemetry and automatic sample submission to Microsoft security cloud endpoints.SumatraPDFAttackers used DLL sideloading with a legitimate SumatraPDF executable to load a malicious DWrite.dll and deploy further components.
Tools
IObitUnlockerThe campaign downloaded signed drivers like RogueKiller and IObitUnlocker to gain kernel privileges and evade detection, and operated unnoticed for over a year.RogueKiller Antirootkitthat the malware also downloaded Bring Your Own Driver (BYOD) components that included the RogueKiller Antirootkit driver v3.1.0 from Adlice Software, and IObitUnlocker.sys v1.2.0.1 from IObit.