cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2493 articles

Threat Research · securityweek.com

Palo Alto Networks Details China-Linked Espionage Campaign Targeting Southeast Asian Militaries

Palo Alto Networks reports that CL-STA-1087 has targeted Southeast Asian military organizations since at least 2020, using custom backdoors, credential theft and long periods of dormant access to seek sensitive military files.
Mar 16, 2026
Threat Research · opensourcemalware.com

GlassWorm Campaign Links Malicious GitHub Repositories, npm Packages and VS Code Extensions

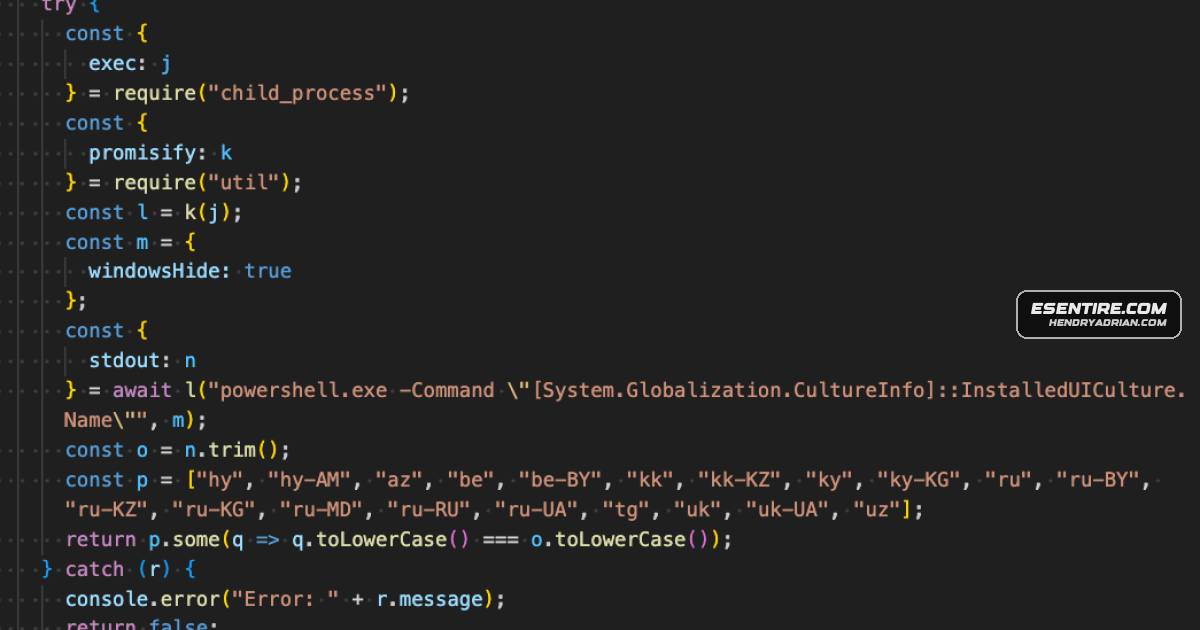
OpenSourceMalware links GlassWorm activity across GitHub, npm, VS Code and Python through shared Solana and server infrastructure, describing its obfuscation, Node.js infostealer and indicators. The Python campaign was still active on March 14, 2026.

Mar 16, 2026
Threat Research · lumen.com

Black Lotus Labs Details Volt Typhoon’s Silent Train and Zero-Day Campaigns

Black Lotus Labs says Volt Typhoon used Silent Train, rotating chains of compromised devices, to reach enterprise management and SD-WAN platforms. Its three-year monitoring identified four confirmed and one likely zero-day campaigns.

Mar 16, 2026
Threat Research · lumen.com

Lumen Maps a Resilient Ecosystem of Malicious Residential Proxy Botnets

Lumen says it tracks over 30 malicious proxy botnet clusters, with nearly 20 million distinct IPs daily. Its analysis describes how operators share and resell access, enabling abuse and rapid recovery after disruptions.

Mar 16, 2026
Threat Research · lumen.com

Lumen Details China-Nexus Cyber Operation’s Shared Proxy and Scanning Infrastructure

Lumen’s Black Lotus Labs describes a China-nexus infrastructure provider that combines target scanning, commercial proxy relays and operator access systems. Its telemetry links reconnaissance with later proxy traffic to high-value networks.

Mar 16, 2026
Threat Research · lumen.com

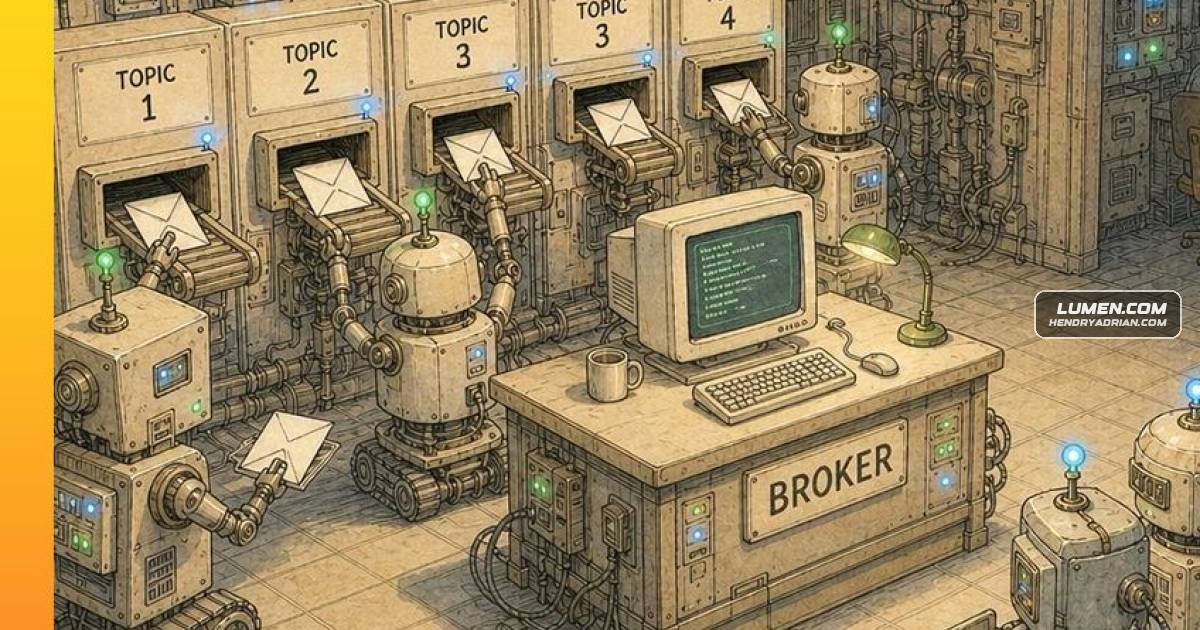
Lumen Details BambooToken Malware Campaign Using MQTT to Target Windows and Linux Systems

Lumen researchers describe BambooToken, a Windows and Linux malware family active since at least 2023 that uses MQTT for command and control. Their telemetry links the campaign to targets in Asia and South America.

Mar 16, 2026
Threat Research · lumen.com

PoeLLM Malware Targets Exposed AI Services with Poem-Based Command-and-Control

Black Lotus Labs details PoeLLM, a campaign exploiting exposed AI and other services to mine cryptocurrency and scan for more victims. Its malware derives changing command-and-control addresses from a poem on GitHub.

Mar 16, 2026
Threat Research · dmpdump.github.io

Analysis Details netd Linux Backdoor’s RC4 C2 and Shell Capabilities

The analysis details netd, a statically linked Linux backdoor with an encrypted configuration, custom RC4 C2 protocol, interactive shell, and file-transfer commands. A Mach-O variant named ChromeUpdates was also observed on VirusTotal.

Mar 16, 2026
Threat Research · stepsecurity.io

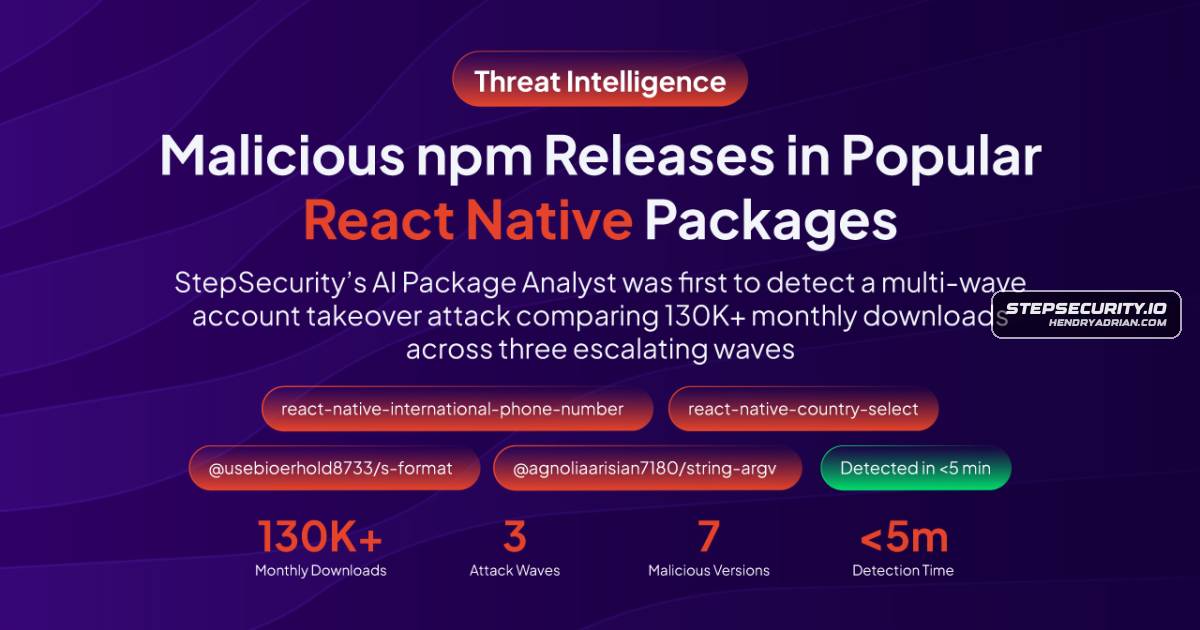
Malicious React Native npm Releases Used a Solana-Based C2 for Malware Delivery

StepSecurity traced three waves of malicious React Native npm releases to a maintainer account takeover and a dependency-chain loader for obfuscated malware using Solana for C2. It said technical overlaps suggest a link to GlassWorm.

Mar 16, 2026
Threat Research · trendmicro.com

Warlock Ransomware Expands Its Attack Chain With Tunnels and Vulnerable-Driver Abuse

Trend Micro details Warlock’s use of compromised SharePoint servers, web shells, remote-access and tunneling tools, DCSync, and a vulnerable NSec driver to evade security controls, exfiltrate data, and deploy ransomware across victim networks.

Mar 16, 2026
Threat Research · genians.co.kr

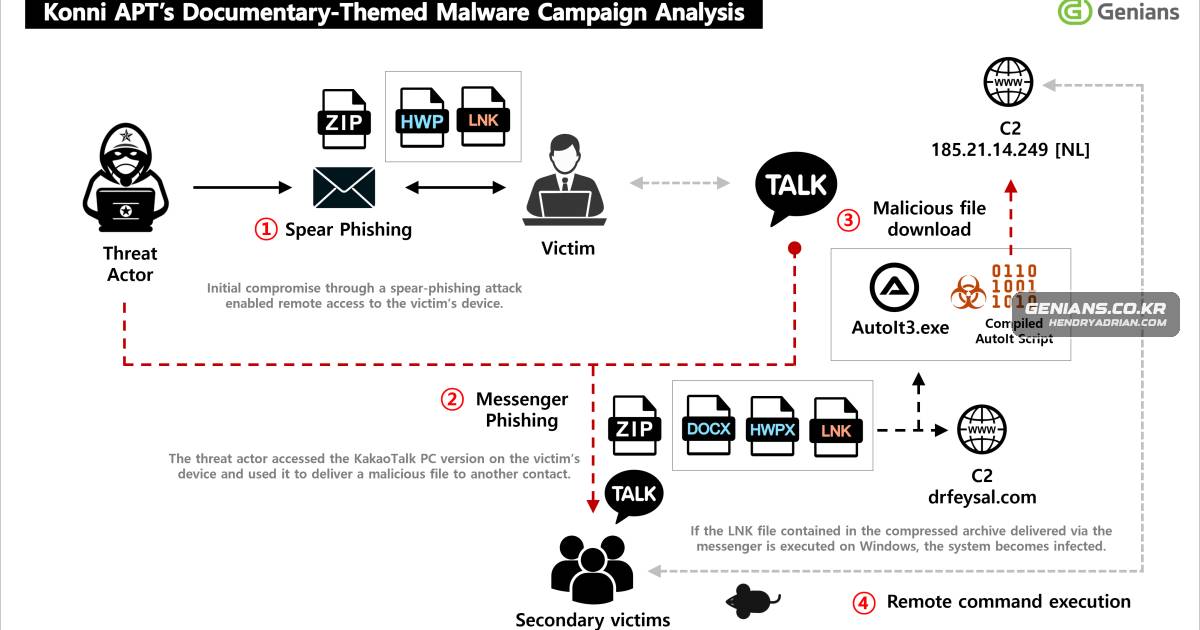
Konni Campaign Uses Spear-Phishing, RATs and KakaoTalk to Spread Malware

Genians analyzes a Konni campaign that used spear-phishing and malicious LNK files to install RATs, steal information, persist on victims’ systems, and spread additional malware through compromised KakaoTalk sessions.

Mar 15, 2026
Threat Research · socket.dev

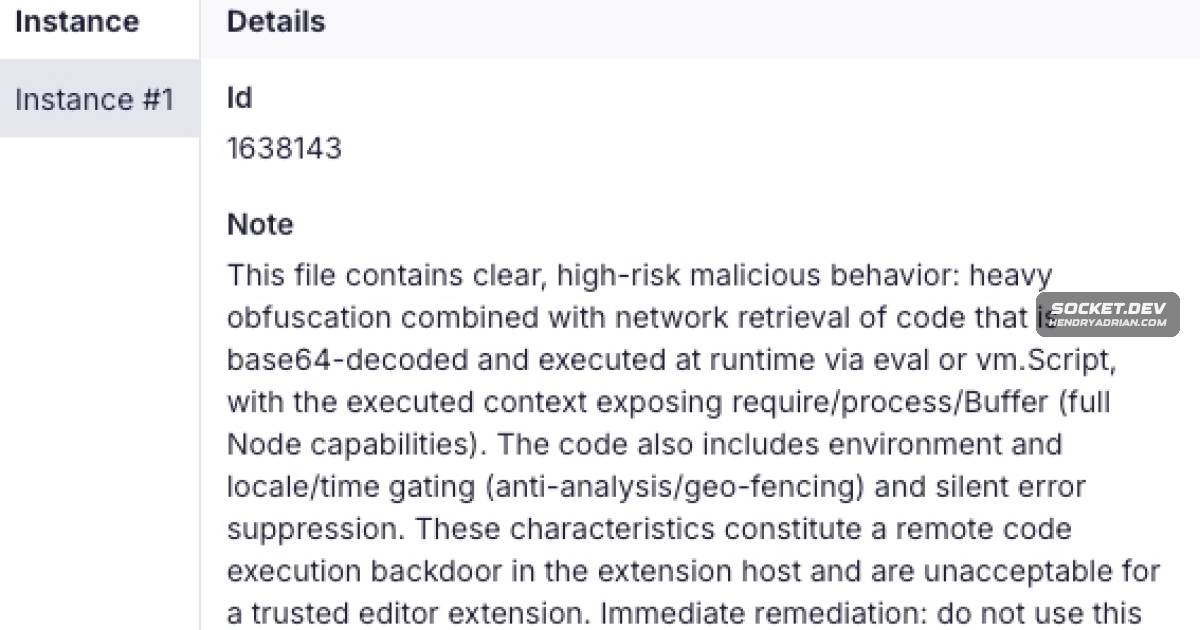
GlassWorm Uses Open VSX Extension Dependencies for Transitive Malware Delivery

Socket reports GlassWorm-linked Open VSX extensions using later-added extensionPack and extensionDependencies entries to install malicious extensions transitively. The campaign also rotates infrastructure and obfuscates staged JavaScript loaders, making version-history

Mar 15, 2026
Threat Research · stepsecurity.io

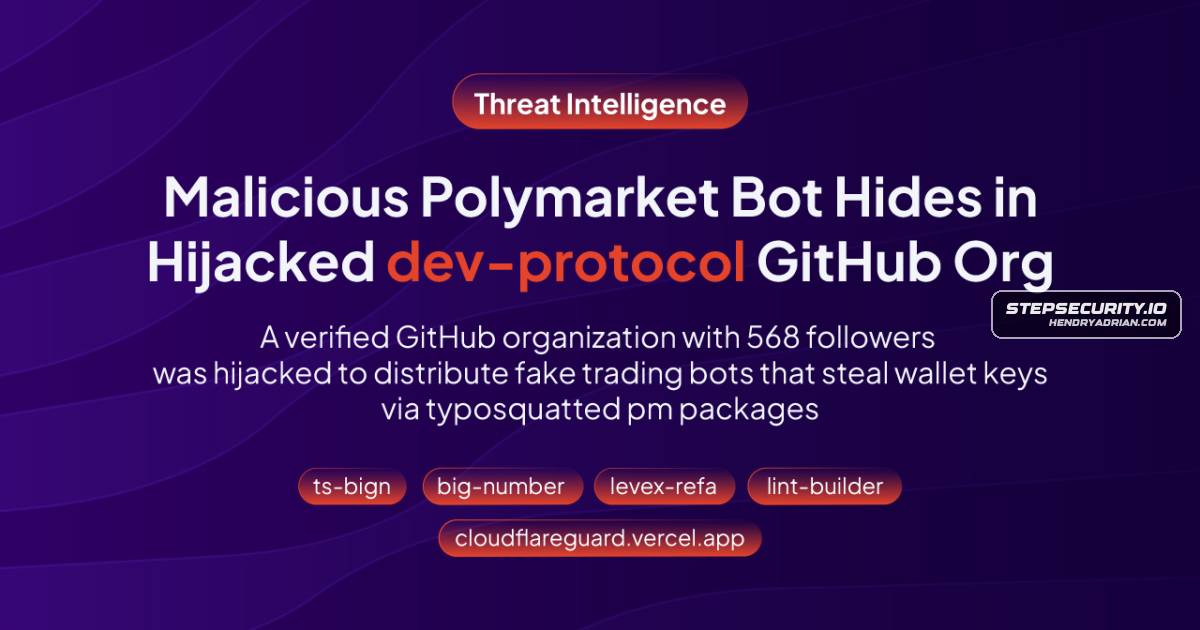
StepSecurity Traces Malicious Polymarket Bot to Hijacked GitHub Organization

StepSecurity says a Polymarket trading bot in the dev-protocol GitHub organization uses typosquatted npm packages to steal wallet and configuration files and install an SSH backdoor; sandbox testing captured exfiltration and firewall changes.

Mar 15, 2026
Threat Research · socradar.io

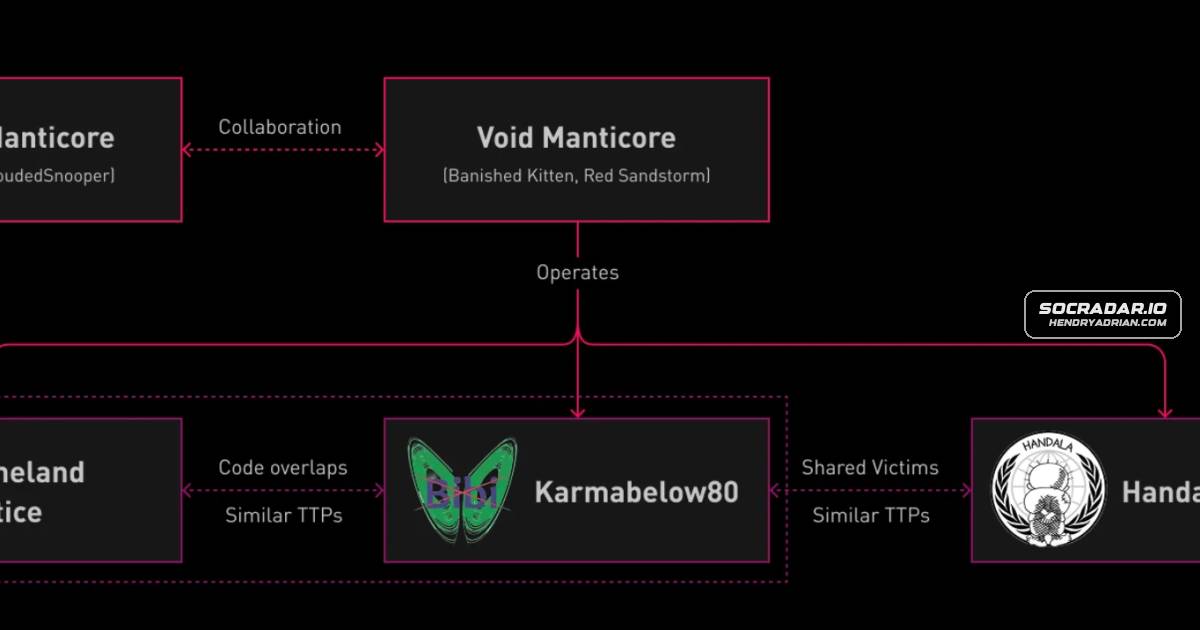
Handala Profile Details MOIS Links, Wiper Campaigns and Tradecraft

SOCRadar profiles Handala, which multiple vendors assess as an Iran MOIS-linked destructive persona. It details claimed operations, a phishing-to-wiper chain, and mitigations; Stryker confirmed global disruption, while Handala's wipe and data-theft figures remain claims

Mar 14, 2026
Threat Research · seqrite.com

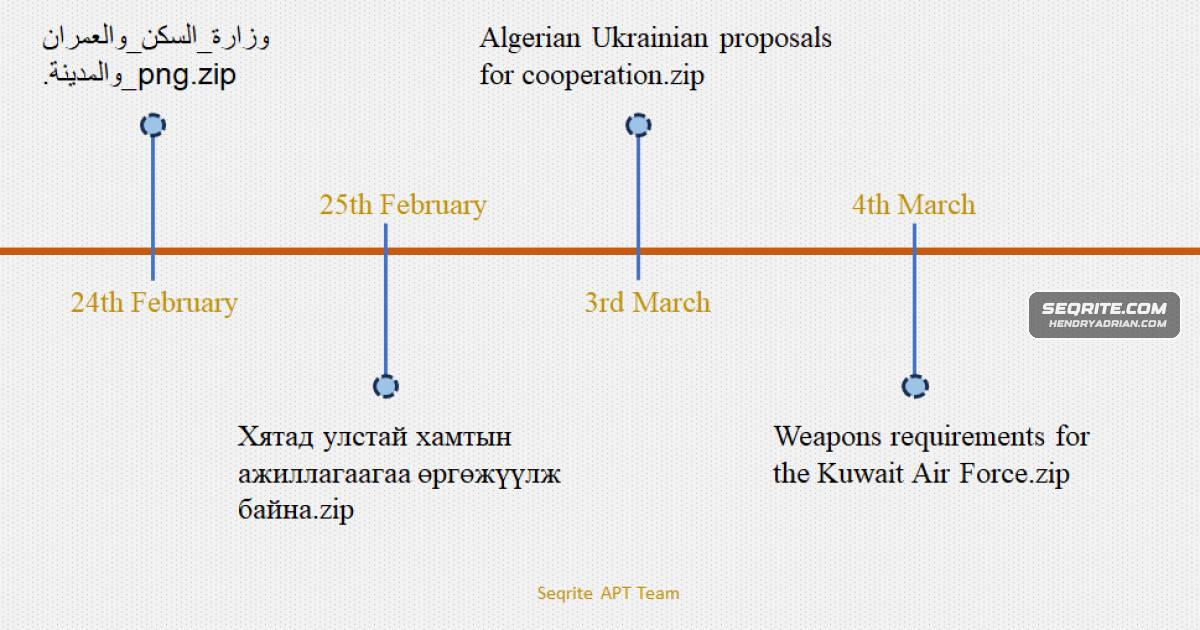
Seqrite Details Operation CamelClone Espionage Campaign Using HOPPINGANT and Rclone

Seqrite Labs links campaigns targeting government, defense, diplomatic, and energy entities in four countries through a shared HOPPINGANT loader and Rclone configuration. The researchers say the activity is likely coordinated but do not attribute it to a known actor.

Mar 14, 2026
Threat Research · circleid.com

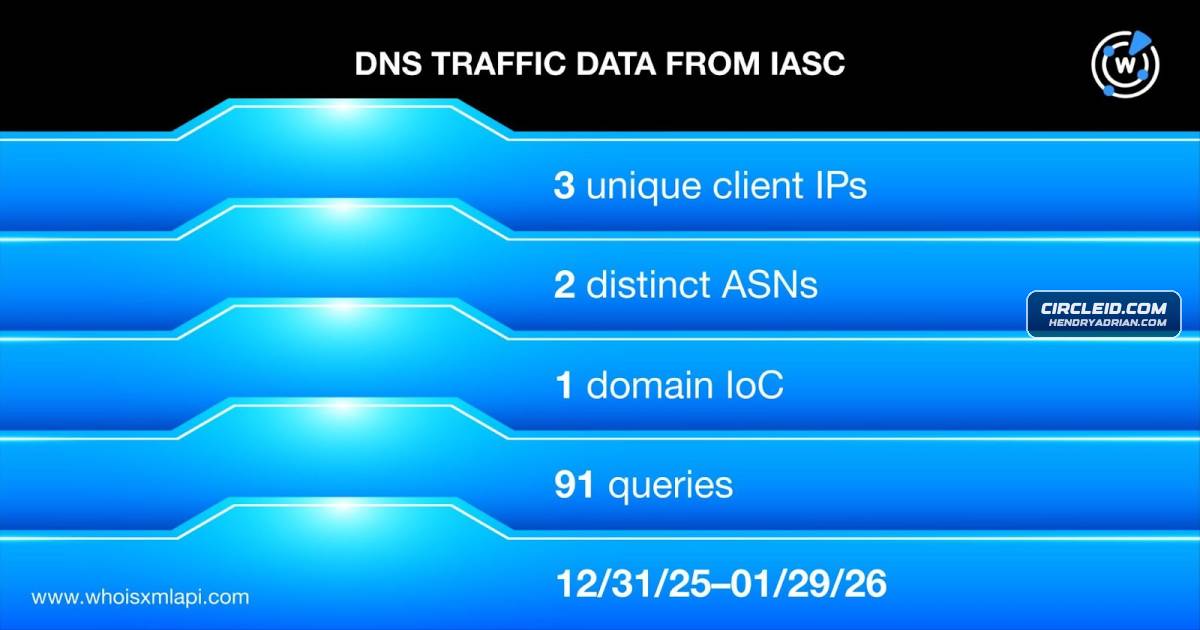
Researchers Trace PeckBirdy Infrastructure Through DNS and WHOIS Analysis

An investigation of PeckBirdy-related indicators analyzed DNS, WHOIS and threat-intelligence data, linking domains and IPs to phishing and malware activity and identifying additional infrastructure. The article attributes the framework to China-aligned APTs.

Mar 14, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details Suspected China-Nexus Espionage Campaign Targeting Southeast Asian Military

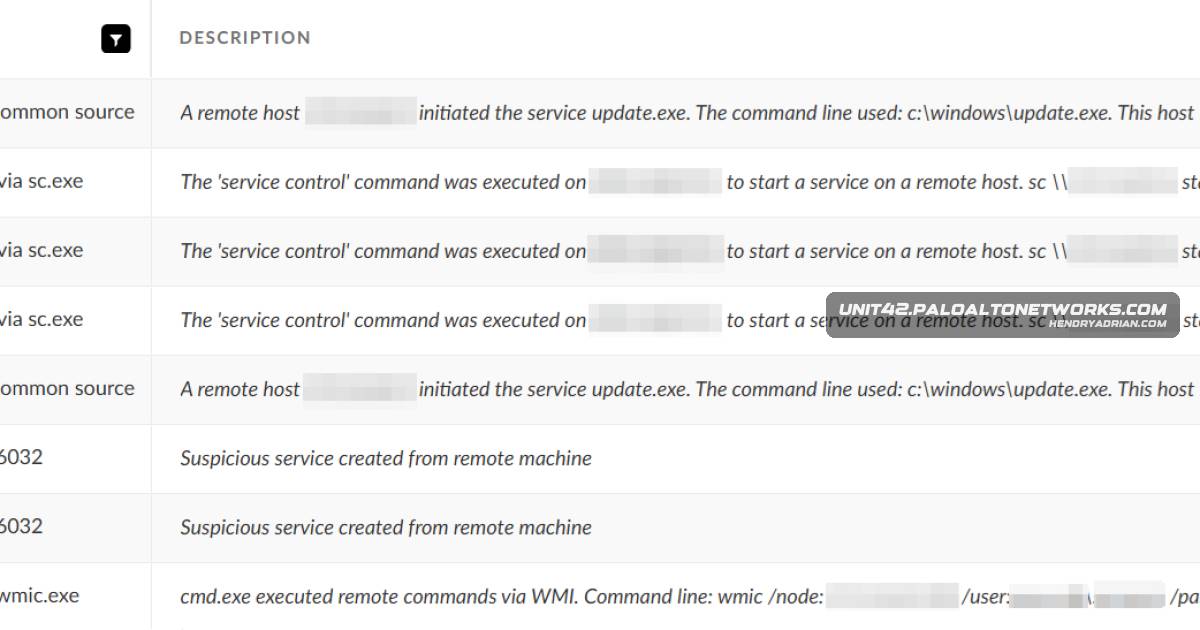
Unit 42 describes CL-STA-1087, a suspected China-nexus espionage cluster targeting Southeast Asian military organizations since at least 2020, and analyzes its AppleChris and MemFun backdoors, Getpass credential harvester, and evasion methods.

Mar 14, 2026
Threat Research · thehackernews.com

Unit 42 Details CL-STA-1087 Espionage Campaign Targeting Southeast Asian Militaries

Unit 42 reports that suspected China-based operators have targeted Southeast Asian military organizations since at least 2020, using AppleChris, MemFun, and Getpass for stealthy access and targeted intelligence collection.

Mar 14, 2026
Threat Research · stepsecurity.io

ForceMemo Uses Account Takeovers and Force-Pushes to Infect Hundreds of GitHub Python Repositories

StepSecurity reports that ForceMemo is injecting malware into hundreds of GitHub Python repositories via account takeovers and stealthy force-pushes. Its analysis traces the payload to Solana-memo C2 and observes Node.js-based execution in a controlled run.

Mar 14, 2026
Threat Research · esentire.com

eSentire Analyzes MuddyWater-Attributed Tsundere Botnet Deployment

eSentire’s analysis of an open directory attributed to MuddyWater found a PowerShell stager deploying Tsundere, which retrieves C2 addresses from Ethereum smart contracts, uses AES-encrypted WebSockets, fingerprints hosts and persists via a Windows Run key.

Mar 13, 2026
Threat Research · malwarebytes.com

Fake $TEMU Airdrop Uses ClickFix to Deploy In-Memory Python Backdoor

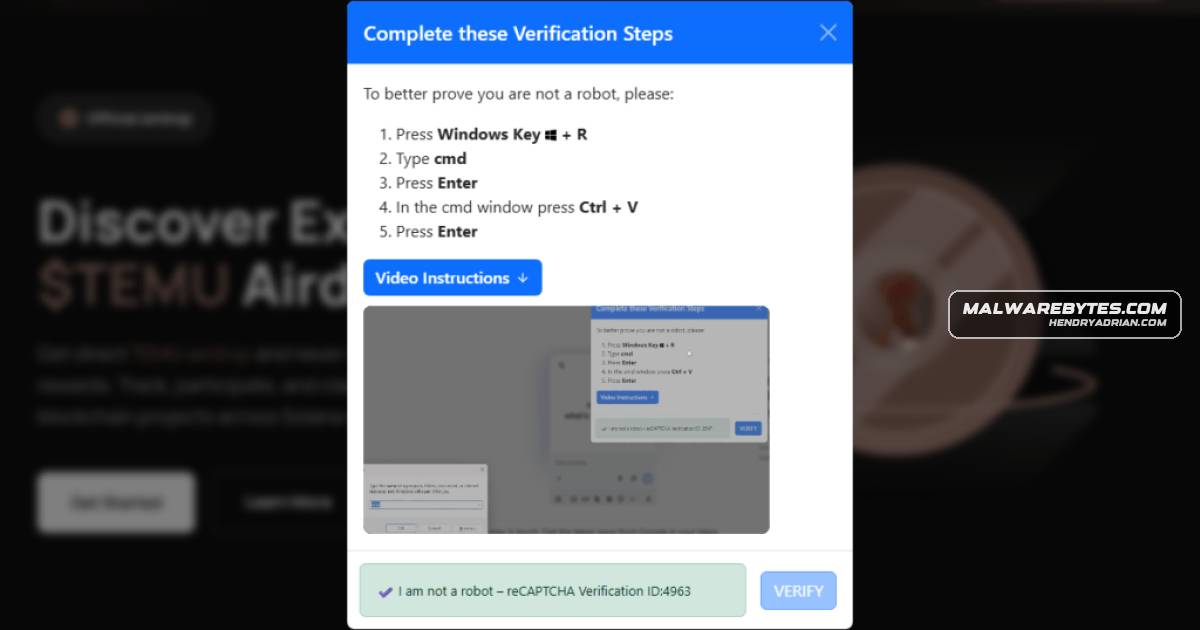
Researchers describe a fake $TEMU airdrop using ClickFix to trick users into running a command, then deploy a victim-specific Python backdoor that retrieves and executes code in memory.

Mar 13, 2026
Threat Research · thecyberexpress.com

Researchers Link Suspected AI-Generated Slopoly Malware to Hive0163 Ransomware Intrusion

IBM X-Force researchers linked suspected LLM-generated PowerShell C2 tool Slopoly to a 2026 Hive0163 ransomware intrusion. Slopoly maintained access and ran commands; ClickFix, NodeSnake and InterlockRAT preceded Interlock ransomware.

Mar 13, 2026
Threat Research · securityonline.info

Unit 42 Details CL-STA-1087 Espionage Campaign Targeting Southeast Asian Militaries

Unit 42 describes CL-STA-1087, a suspected China-linked espionage cluster active in Southeast Asian military networks since at least 2020, using custom tools to maintain access and collect targeted C4I-related intelligence.

Mar 13, 2026
Threat Research · socket.dev

Socket Finds Six Malicious Packagist Themes Bundling Trojanized JavaScript

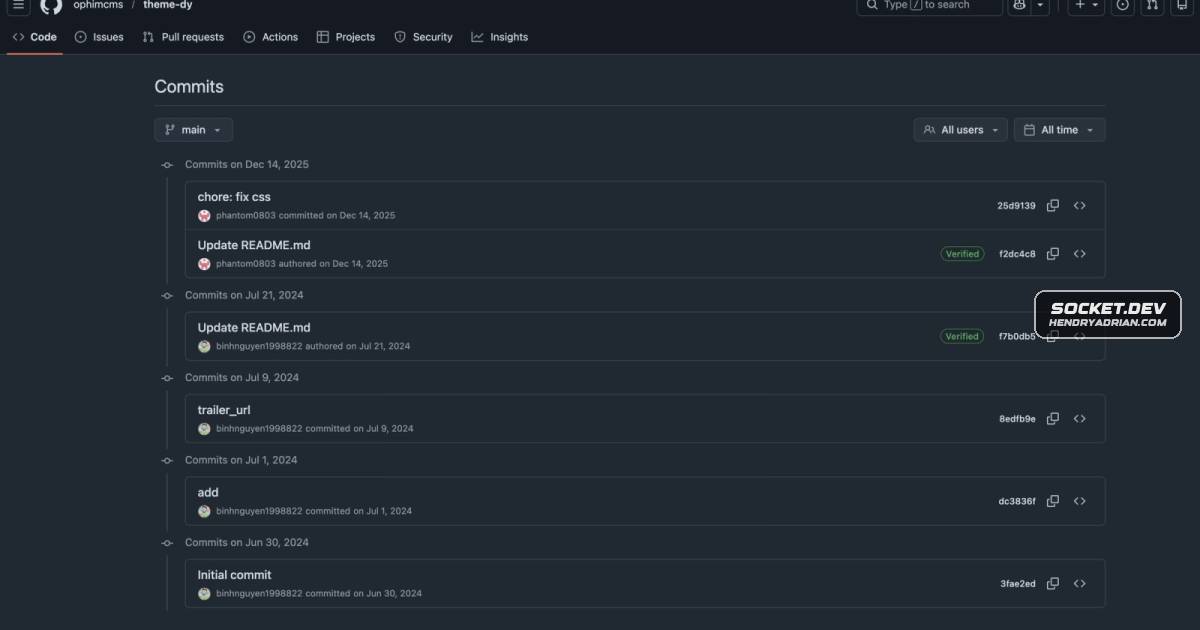
Socket researchers identified six malicious ophimcms Composer themes on Packagist that bundle JavaScript for URL exfiltration, redirects, ad injection and click hijacking. One redirect chain uses infrastructure linked to FUNNULL.

Mar 13, 2026
PreviousPage 79 of 104 Next
© 2026 cyber.hendryadrian.com