
Iran Conflict Drives Espionage Campaigns Targeting Middle East Entities
Summary
Proofpoint details six campaigns observed in early March 2026, in which state-aligned and opportunistic actors used Iran-conflict lures to target Middle Eastern governments and a U.S. think tank with credential phishing and malware, including Cobalt Strike and a Rust 📄
Key points
- From March 1–8, actors used conflict-themed emails to target Middle Eastern government and diplomatic organizations and a U.S. think tank.
- Suspected China-aligned UNK_InnerAmbush used LNK files in archives to launch a DLL-sideloaded loader that decrypted and loaded a Cobalt Strike payload.
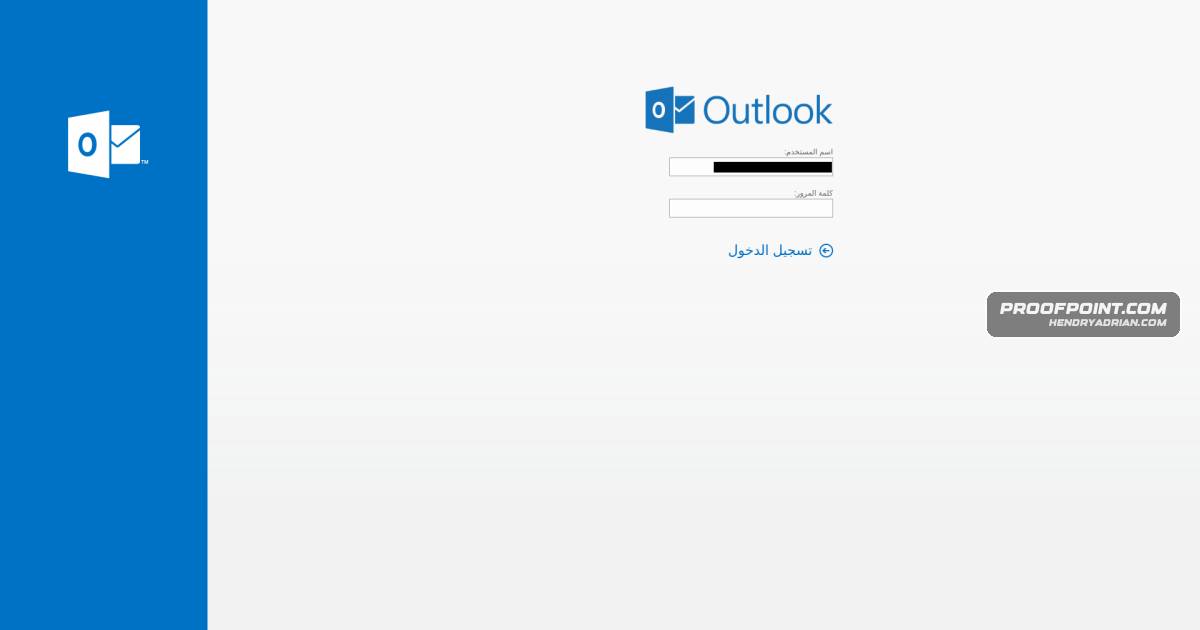
- TA402 used a compromised Iraqi Ministry of Foreign Affairs account for OWA-themed credential phishing, serving decoys or credential-harvesting pages based on geolocation.
- Suspected Pakistan-aligned UNK_RobotDreams delivered a .NET loader through a PDF lure; PowerShell retrieved a Rust backdoor from Azure Front Door infrastructure.
- UNK_NightOwl and TA473 used compromised or spoofed senders and attachments or links to track engagement or direct targets to credential-harvesting pages.
- TA453’s campaign against a U.S. think tank began before the conflict and continued its intelligence-collection efforts using a benign OneDrive lure before redirecting to credential phishing.
- Proofpoint assesses that some actors used the conflict as an opportunistic lure, while others appeared to broaden intelligence collection against regional government and diplomatic targets.
Article Details
- Attack Vectors
- Conflict-themed spearphishing emails targeted Middle Eastern government and diplomatic organizations and a US think tank, using links, archive attachments, PDFs, and HTML attachments.
- Password-protected ZIP or RAR archives contained LNK files disguised as images; a LNK launched a loader that used DLL sideloading to load a Cobalt Strike payload.
- A PDF attachment used a fake Adobe Reader button to redirect targets to a geofenced executable download; the .NET loader used PowerShell to retrieve a Rust backdoor.
- OWA- and OneDrive-themed credential-phishing pages selectively served decoys or credential-harvesting content, with entered credentials sent to an authentication endpoint.
- HTML attachments and tracking pixels generated HTTP requests to monitor target engagement.
- TA453 established rapport with a benign OneDrive lure before sending a link through an attacker-controlled domain that redirected to a credential-harvesting page.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 1drvms[.]store | Attacker-used domain hosting UNK_NightOwl's OneDrive-spoofed OWA credential-harvesting page. |
| DOMAIN | iwsmailserver[.]com | TA402-controlled domain hosting an OWA-themed credential-phishing page. |
| DOMAIN | transfergocompany[.]com | TA453-controlled redirect domain used in the credential-phishing sequence. |
| DOMAIN | unityprogressall[.]org | TA473-controlled domain contacted by its HTML attachment for target-engagement tracking. |
ali[.]mo@med[.]gov[.]sy | Likely compromised sender account used in the UNK_NightOwl campaign. | |
ban[.]ali@mofa[.]gov[.]iq | Compromised Iraqi Ministry of Foreign Affairs sender account used by TA402 for phishing. | |
jscop[.]mea[.]gov[.]in@outlook[.]com | Sender address used by UNK_RobotDreams to impersonate India's Ministry of External Affairs. | |
maria[.]tomasik@denika[.]se | Sender address listed for the TA473 campaign, whose messages originated from likely compromised infrastructure. | |
mcmanus[.]michael@hotmail[.]com | Attacker-owned freemail account used by TA453 to impersonate a think-tank research head. | |
nqandeel04@gmail[.]com | Attacker-controlled account used by TA402 to send credential-phishing emails. | |
uzbembish@elcat[.]kg | Likely compromised sender address used in the UNK_InnerAmbush phishing campaign. | |
war[.]analyse[.]ltd@outlook[.]com | Attacker-owned freemail account associated with the fake War Analyse Ltd identity used by UNK_NightOwl. | |
| HOSTNAME | fileportalshare[.]netlify[.]app | Specific Netlify-hosted hostname serving the OneDrive-themed credential-phishing page used by TA453. |
| HOSTNAME | support[.]almersalstore[.]com | Cobalt Strike command-and-control hostname used in the UNK_InnerAmbush campaign. |
| IPV4 | 72[.]60[.]90[.]32 | Hosting IP address for unityprogressall[.]org, used in the TA473 campaign. |
| SHA256 | 14efa1194cc4c6aa5585d63c032268794364123d41a01121cbd5e56f7c313399 | Hash identified for WinHlp.hlp, which contained the encrypted Cobalt Strike payload in the UNK_InnerAmbush campaign. |
| SHA256 | 4b9661092051839496c04169ccb52b659c0f65cefd14a990e23565a0c0e8eeaf | Hash listed for an LNK file delivered in the UNK_InnerAmbush campaign. |
| SHA256 | 7b6d69a249fe2adf43eefc31cdeca62cf48ab428fcbf199322feeb99d24fb001 | Hash listed for nvdaHelperRemote.dll, the malicious loader DLL used in the UNK_InnerAmbush sideloading chain. |
| SHA256 | 9477d9cd1435dc465b4047745e9c71103a114d65ed0d5f02ac3c97ac3f1dbf47 | Hash listed for gulf_disruption_advisory_march2026.pdf, a lure associated with the UNK_RobotDreams campaign. |
| SHA256 | a8acb9864e6f64323ed75e69038ca9bfe76f7b1b0d24ec7df8ac07b6dbd641a3 | Hash listed among indicators for the UNK_InnerAmbush campaign. |
| SHA256 | a9de383c6a1b00c9bd5a09ef87440d72ec7fc4bcd781207b3cace2f246788d4d | Hash listed for the UNK_InnerAmbush archive named Strike at Gulf oil and gas facilities.zip. |
| SHA256 | a9f4f4bc12896d0f0d2eeff02dd3e3e1c1406d8a6d22d59aa85f151d806ba390 | Hash for Reader_en_install.exe, the UNK_RobotDreams .NET loader. |
| SHA256 | d518262dd687a48f273966853f3ed4eb7404eb918b165bb71ff83f75962c0104 | Hash listed for LaunchWlnApp.exe, a file associated with the UNK_InnerAmbush loader chain. |
| SHA256 | dfaaaf75147afbd57844382c953ec7ef36f68a9c17c66a47a847279a6b1109c9 | Hash listed for an LNK file delivered in the UNK_InnerAmbush campaign. |
| SHA256 | ea1d98a41ad9343d017fa72f4baeeca0daa688bec6e0508e266c5e37e9d330de | Hash for VLCMediaPlayer.exe, the Rust backdoor deployed by UNK_RobotDreams. |
| SHA256 | fed6ebb87f7388adf527076b07e81dfa432bac4e899b0d7af17b85cc0205ffad | Hash listed for the UNK_InnerAmbush archive named Photos from the scene.rar. |
| URL | hxxps[:]//defenceprodindia[.]site/server.php?file=Reader_en_install | UNK_RobotDreams delivery URL that served a geofenced executable payload to intended targets. |
| URL | hxxps[:]//endpoint1-b0ecetbuabcdg9cp[.]z01[.]azurefd[.]net/download.php?file=cnVzdHVwaW5pdA | Azure Front Door staging URL used to retrieve the Rust backdoor in the UNK_RobotDreams campaign. |
MITRE ATT&CK
T1059.001 · PowerShellThe UNK_RobotDreams .NET loader used PowerShell via conhost.exe to retrieve a Rust backdoor.T1071.001 · Web ProtocolsThe article reports Cobalt Strike and the Rust backdoor communicating with command-and-control infrastructure over HTTP/S.T1078 · Valid AccountsCampaigns used likely compromised government sender accounts, including accounts used by TA402 and UNK_NightOwl.T1204.002 · Malicious FileTargets had to open LNK files or HTML attachments to display decoys and initiate follow-on activity.T1566.001 · Spearphishing AttachmentUNK_InnerAmbush delivered password-protected archives containing LNK files disguised as images.T1566.002 · Spearphishing LinkPhishing emails linked to Google Drive archives and credential-phishing pages.T1574.001 · DLLnvdaHelperRemoteLoader.exe loaded the malicious nvdaHelperRemote.dll in the UNK_InnerAmbush loader chain.
Threat Actors
CALANQUE IONThe article identifies APT42 as an alias of TA453, which it reports conducted credential phishing and continued intelligence collection.Charming KittenProofpoint reports that Iran-aligned TA453 continued intelligence-collection activity and conducted a credential-phishing attempt against a US think-tank target.Cruel JackalThe article identifies Cruel Jackal as an alias of TA402, which it reports conducted credential phishing against a Middle Eastern government entity.FrankensteinThe article identifies Frankenstein as an alias of TA402, which it reports conducted credential phishing against a Middle Eastern government entity.HamasThe article lists Hamas among the suspected attributions for campaigns targeting Middle Eastern government organizations; it does not identify a specific campaign as attributable to Hamas.Mint SandstormThe article identifies Mint Sandstorm as an alias of TA453, which it reports conducted credential phishing and continued intelligence collection.TA402Proofpoint reports that TA402 conducted OWA-themed credential phishing against a Middle Eastern government entity using a compromised sender account and an attacker-controlled account.TA473Proofpoint reports that TA473 sent phishing emails to government organizations in Europe and the Middle East; the article describes the actor as Belarus-aligned.UNK_InnerAmbushProofpoint attributes a phishing and malware-delivery campaign against Middle Eastern government and diplomatic organizations to this cluster, which it describes as suspected China-aligned.UNK_NightOwlProofpoint attributes an OWA-themed credential-phishing campaign against a Middle Eastern government ministry to this newly tracked cluster; the article describes it as suspected state-aligned.UNK_RobotDreamsProofpoint attributes a spearphishing and backdoor-delivery campaign targeting India-based offices of Middle Eastern government organizations to this cluster, which it describes as suspected Pakistan-aligned.Winter VivernThe article identifies Winter Vivern as an alias of TA473, which it reports sent phishing emails to government organizations in Europe and the Middle East.
Vendors
GoogleUNK_InnerAmbush (suspected China-aligned) used Google Drive-hosted archives containing LNK files that launched a loader which DLL-sideloaded nvdaHelperRemote.dll to decrypt and load a Cobalt Strike payload communicatingMicrosoft[T1566.001] Spearphishing Attachment – Archive contained Microsoft Shortcut (LNK) files disguised as images that initiated the loader (‘archives contained several Microsoft Shortcut (LNK) files disguised as JPG images,Microsoft AzureUNK_RobotDreams (suspected Pakistan-aligned) delivered a .NET loader via a PDF attachment that used PowerShell to fetch a Rust backdoor from Azure Front Door infrastructure, writing a VLCMediaPlayer.exe backdoor to disk.
Products
Azure Front DoorUNK_RobotDreams (suspected Pakistan-aligned) delivered a .NET loader via a PDF attachment that used PowerShell to fetch a Rust backdoor from Azure Front Door infrastructure, writing a VLCMediaPlayer.exe backdoor to disk.Google DriveUNK_InnerAmbush (suspected China-aligned) used Google Drive-hosted archives containing LNK files that launched a loader which DLL-sideloaded nvdaHelperRemote.dll to decrypt and load a Cobalt Strike payload communicatingMicrosoft OneDriveUNK_NightOwl and TA473 used compromised accounts or spoofed senders and tracking HTTP requests/HTML attachments to monitor engagement and harvest credentials via OneDrive- or OWA-themed pages.Microsoft Outlook Web ApplicationThe actor-controlled site was designed to impersonate Microsoft Outlook Web Application (OWA):
Tools
Cobalt StrikeTracked activity includes clusters UNK_InnerAmbush, TA402, UNK_RobotDreams, UNK_NightOwl, TA473, and TA453 leveraging LNK-based loaders, DLL sideloading, PowerShell-retrieved Rust backdoors, and Cobalt Strike C2.PowerShellTracked activity includes clusters UNK_InnerAmbush, TA402, UNK_RobotDreams, UNK_NightOwl, TA473, and TA453 leveraging LNK-based loaders, DLL sideloading, PowerShell-retrieved Rust backdoors, and Cobalt Strike C2.
Countries
BelarusThese campaigns were conducted by both known groups and previously unobserved actors, with suspected attribution to China, Belarus, Pakistan, and Hamas.ChinaUNK_InnerAmbush (suspected China-aligned) used Google Drive-hosted archives containing LNK files that launched a loader which DLL-sideloaded nvdaHelperRemote.dll to decrypt and load a Cobalt Strike payload communicatingIndiaOn 5 March 2026, a suspected Pakistan-aligned actor Proofpoint calls UNK_RobotDreams sent spearphishing emails to India-based offices of Middle East government organizations.IranProofpoint observed multiple state-aligned and opportunistic threat actors using Iran-conflict-themed lures to conduct credential-phishing, malware delivery, and intelligence-collection campaigns against Middle EasternIraqThe actor used a compromised Ministry of Foreign Affairs of Iraq sender account (“[email protected][.]iq”) and an attacker-controlled account (“nqandeel04@gmail[.]com”) to send the phishing emails.PakistanUNK_RobotDreams (suspected Pakistan-aligned) delivered a .NET loader via a PDF attachment that used PowerShell to fetch a Rust backdoor from Azure Front Door infrastructure, writing a VLCMediaPlayer.exe backdoor to disk.SyriaThe compromised account appears to belong to the Ministry of Emergency and Disaster Management in Syria (“[email protected][.]sy”), and the freemail account was for a fake organization called War Analyse LtdUnited StatesThe theme of phishing emails observed in this initial wave was Ayatollah Khamenei’s death with an attempt to share sensitive images from the US “Department of Foreign Affairs”.
Industries
Diplomaticmalware delivery, and intelligence-collection campaigns against Middle Eastern governments, diplomatic entities, and Western think tanks.GovernmentIranian espionage-focused threat groups remain somewhat active despite the Iranian government’s shutdown of the internet immediately following the initial US and Israeli attacks.Think tanksintelligence-collection campaigns against Middle Eastern governments, diplomatic entities, and Western think tanks.