cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2480 articles

Threat Research · huntress.com

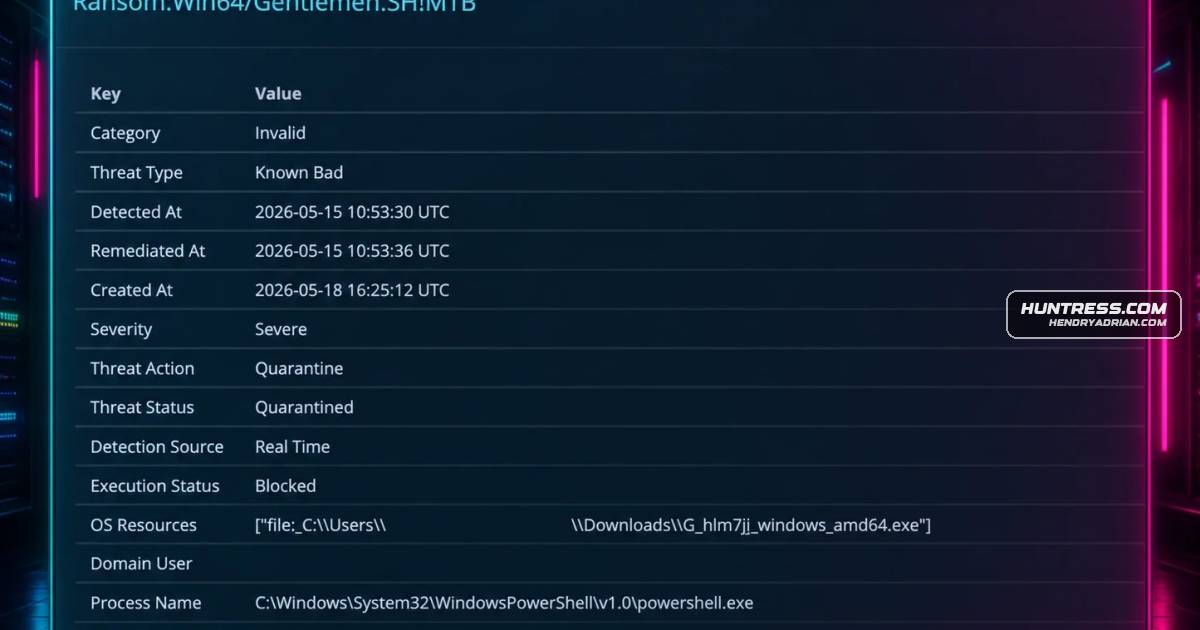
Huntress Details Defense Evasion Tactics in Two Gentlemen Ransomware Incidents

Huntress analyzed two Gentlemen ransomware incidents involving scheduled tasks, PowerShell, Windows log clearing, and attempts to disable Microsoft Defender. One incident included a SOCKS proxy connecting to attacker-controlled IP addresses.

May 21, 2026
Threat Research · trendmicro.com

Research Details AI-Assisted ‘Patriot Bait’ Campaign Using Telegram Scams and Credential Theft

Trend Micro details a five-year Telegram operation in which a Russian-speaking actor used jailbroken AI to automate political-themed content, cryptocurrency fraud, infrastructure management, and credential theft against American audiences.

May 21, 2026
Threat Research · socket.dev

Compromised npm Package Delivered Coruna-Like iOS Exploit Framework

Researchers traced malicious art-template npm versions 4.13.5 and 4.13.6 to a Safari-focused framework targeting iOS 11–17.2. It resembles Coruna, but analysis of the final exploit payload is ongoing.

May 20, 2026
Threat Research · sysdig.com

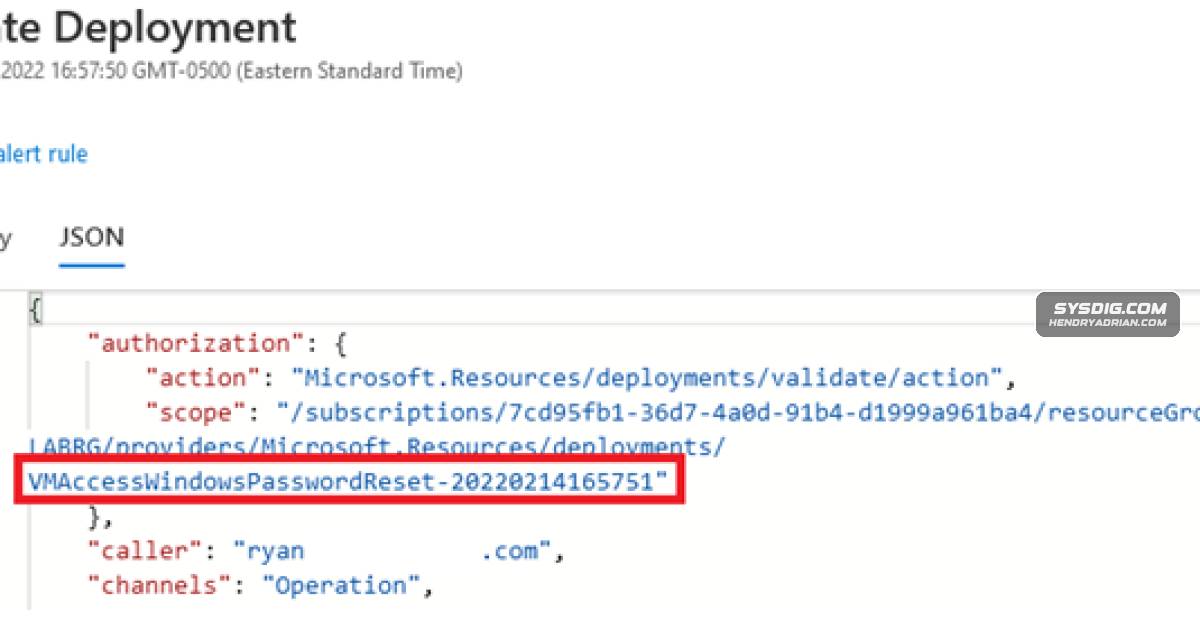
Caller-Controlled Azure VM Extension Names Can Evade Password-Reset Detection

Sysdig TRT demonstrated that a custom Azure VM extension name can bypass name-based password-reset alerts. Successful extension-write logs omit the publisher and type, and Microsoft’s documented validation event did not appear in testing. Microsoft said this is not a se

May 20, 2026
Threat Research · seqrite.com

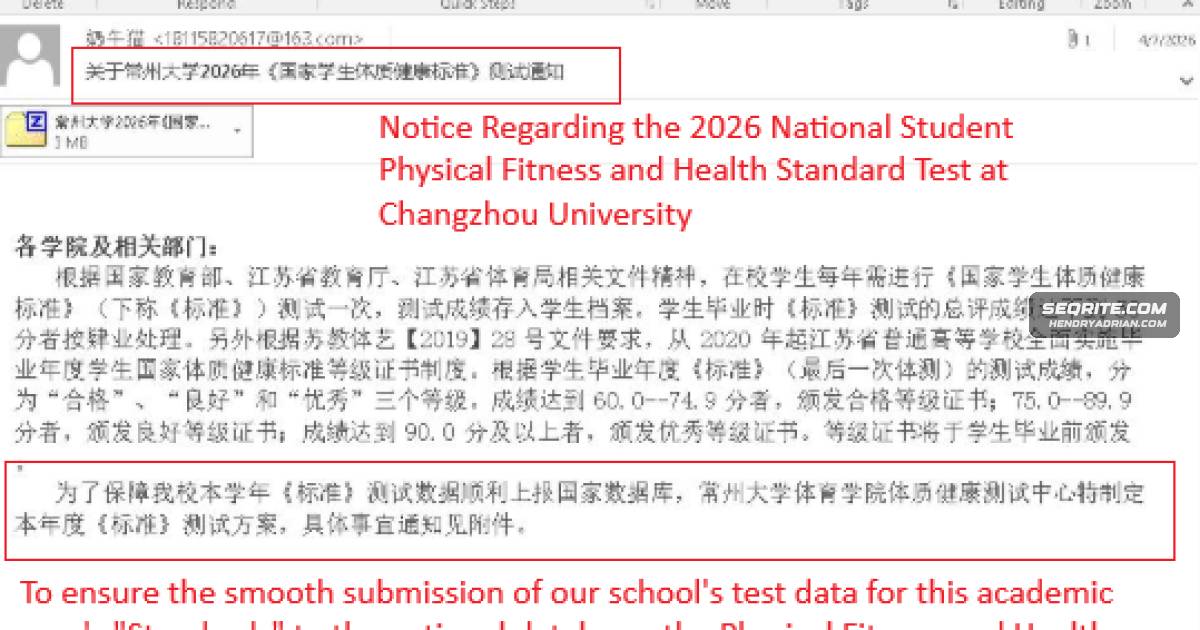
Seqrite Details Operation Dragon Whistle Spear-Phishing Campaign Targeting Chinese University

Seqrite Labs reports that Operation Dragon Whistle used a fake Changzhou University fitness notice and a ZIP/LNK/VBScript chain to sideload a DLL and deliver an in-memory Cobalt Strike Beacon; it attributes the activity to UNG0002 with medium-high confidence.

May 20, 2026
Threat Research · hexastrike.com

CodeStorm AiTM Kit Targets Microsoft 365, Steals MFA and Session Tokens

Hexastrike details CodeStorm, an ongoing Microsoft 365 AiTM phishing campaign linked with moderate confidence to Storm-1167. The kit intercepts credentials, MFA and session material; over 100 tenant compromises were confirmed in incident-response telemetry.

May 20, 2026
Threat Research · unit42.paloaltonetworks.com

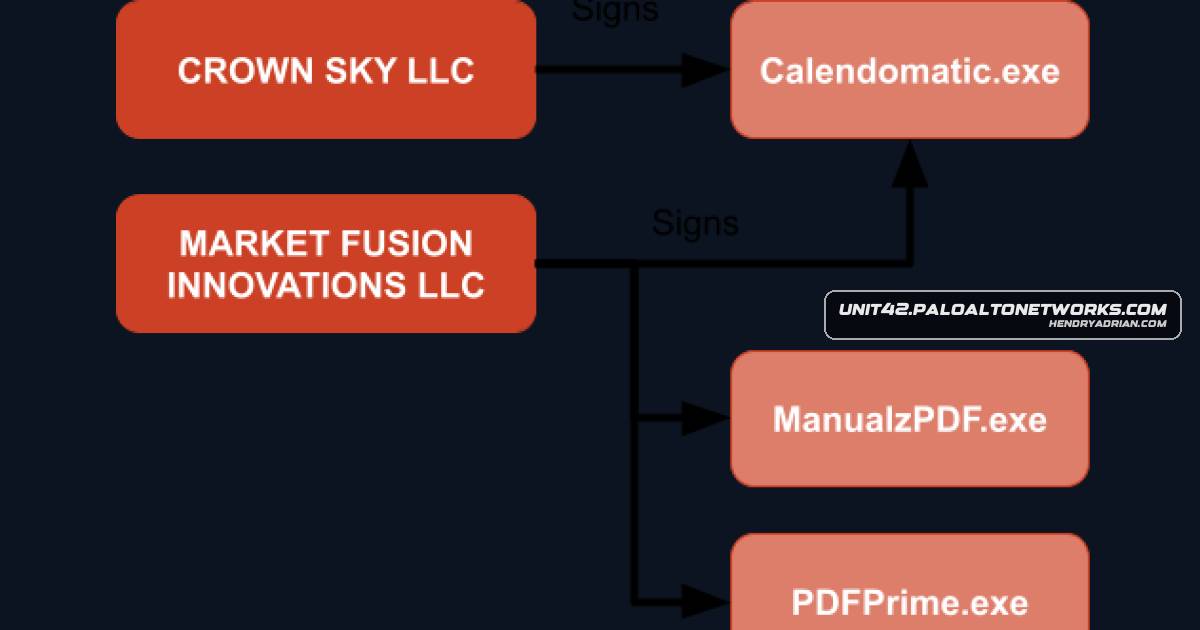
Researchers Map Three TamperedChef-Style Malware Clusters Through Code and Certificate Reuse

Unit 42 researchers mapped three TamperedChef-style clusters using code-signing, code reuse, advertising and corporate links. They tracked over 4,000 samples and describe fake productivity apps that can activate after long delays to deliver malicious payloads.

May 20, 2026
Threat Research · labs.k7computing.com

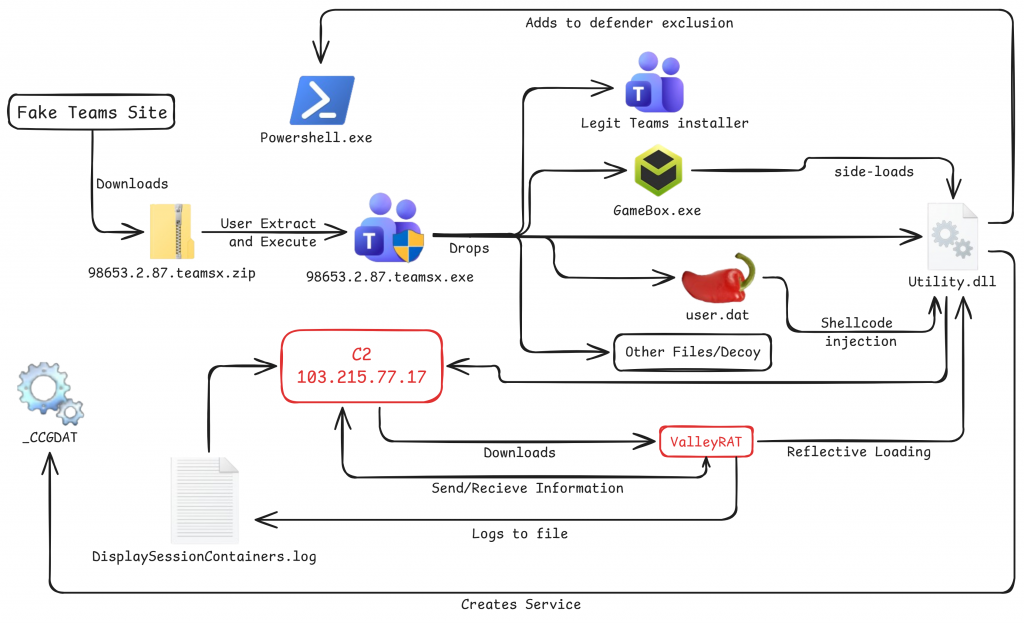
Fake Teams Sites Deliver ValleyRAT Through NSIS and DLL Sideloading

Researchers traced a fake Teams campaign to a multistage ValleyRAT infection using an NSIS installer and GameBox.exe DLL sideloading. The malware evaded Defender, captured clipboard and log data, and communicated with a C2 server.

May 20, 2026
Threat Research · sophos.com

Sophos Details WantToCry Ransomware’s Remote SMB Encryption Attacks

SophosLabs says WantToCry operators brute-force exposed SMB services, exfiltrate files to attacker-controlled systems, encrypt them remotely, then write them back over SMB. The report details infrastructure, detection challenges and mitigations.

May 20, 2026
Threat Research · reversinglabs.com

Researchers Detail Google Family Link Abuse in Account-Hijacking Campaign

Researchers describe a Discord-led malware campaign that allegedly hijacks Google accounts by abusing Family Link. Their tests found age changes could lack reauthentication, but supervision setup results varied; they offer account-security recommendations.

May 20, 2026
Threat Research · opensourcemalware.com

TeamPCP Campaign Republished 324 npm Packages Across 645 Versions

Researchers report TeamPCP compromised two npm maintainer accounts and republished 324 packages across 645 versions, putting packages with about 16 million weekly downloads at risk. Payload analysis is ongoing; the article recommends pinning known-good versions and aud

May 20, 2026
Threat Research · cloudsek.com

CloudSEK Maps IPL Betting Scams, Deepfake Promotions and Compromised Government Sites

CloudSEK’s investigation found more than 1,200 domains promoting illegal IPL betting, operators rejecting thousands of withdrawals, and an underground ecosystem using deepfakes, money mules, compromised government sites and fake loan apps.

May 20, 2026
Threat Research · bleepingcomputer.com

Microsoft Says Storm-2949 Abused SSPR in Azure Data-Theft Attacks

Microsoft reports that Storm-2949 used social engineering and allegedly abused SSPR to access privileged accounts, then stole data and credentials from Microsoft 365 and Azure. Microsoft recommends stronger access controls, phishing-resistant MFA and cloud monitoring.

May 19, 2026
Threat Research · wiz.io

TeamPCP-Linked Attack Compromises Microsoft DurableTask Python Packages

Wiz reports that TeamPCP-linked attackers used compromised GitHub credentials and a PyPI token to publish malware in durabletask 1.4.1–1.4.3. PyPI quarantined the packages; the payload steals credentials and can spread through AWS SSM and Kubernetes.

May 19, 2026
Threat Research · levelblue.com

Nightmare-Eclipse Publishes YellowKey and GreenPlasma Windows Zero-Days

Nightmare-Eclipse publicly released YellowKey, a WinRE-based BitLocker bypass requiring physical access, and GreenPlasma, a CTFMON-based privilege-escalation flaw. The article says neither was patched at publication and details their mechanics, related toolkit activity,

May 19, 2026
Threat Research · socket.dev

Typosquatted Go Decimal Library Hid a DNS Command-Execution Backdoor

A malicious release of the typosquatted Go module github.com/shopsprint/decimal used an init() function to poll DNS TXT records and execute commands. The Go security team has withdrawn the module from its proxy.

May 19, 2026
Threat Research · cyberscoop.com

Mini Shai-Hulud Worm Resurfaces Across Hundreds of npm Packages

Researchers report that the TeamPCP-linked Mini Shai-Hulud worm is spreading through hundreds of npm packages, stealing credentials, poisoning accessible packages and planting persistent backdoors that can remain after package removal.

May 19, 2026
Threat Research · bitdefender.com

Bitdefender Details Malware Campaigns Abusing Windows’ MSHTA Utility

Bitdefender researchers analyzed campaigns using Windows’ built-in MSHTA utility to deliver stealers, loaders and other malware through multi-stage script chains, often aided by social engineering.

May 19, 2026
Threat Research · opensourcemalware.com

Researchers Link Three Malicious npm Packages to the Axios Attacker

OpenSourceMalware reports three npm packages that steal developer credentials and use a command-and-control server distinct from the Axios attack’s infrastructure. Shared cryptographic artifacts are cited as evidence linking the campaigns.

May 19, 2026
Threat Research · reliaquest.com

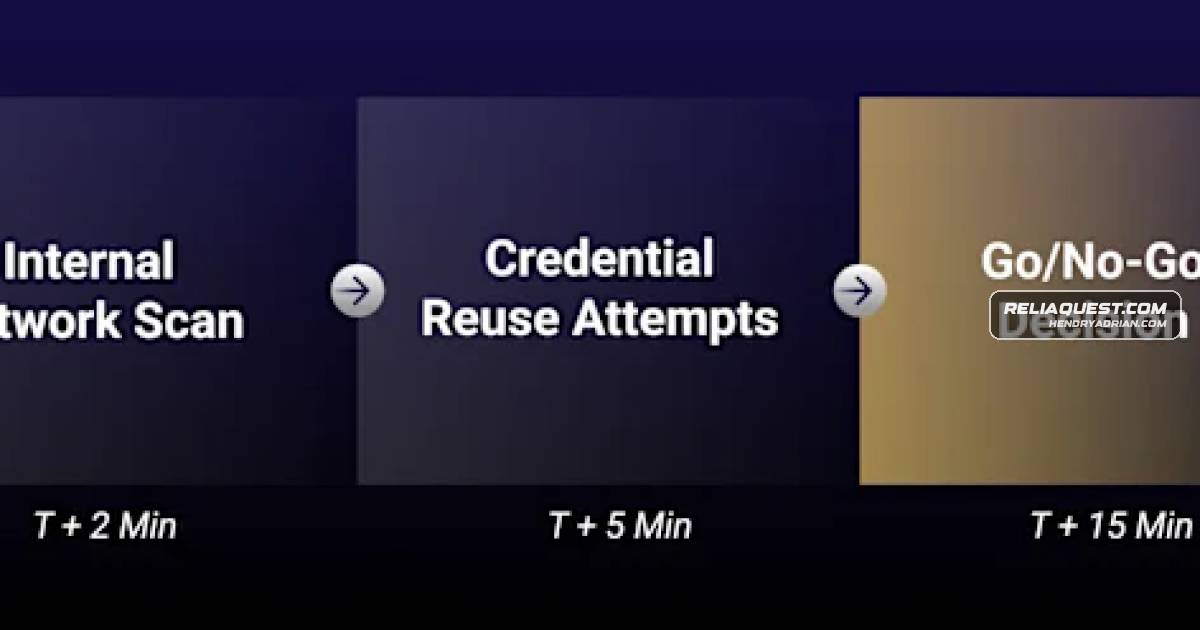
ReliaQuest Details SonicWall VPN Exploitation Despite Patching

ReliaQuest says, with medium confidence, it observed the first known in-the-wild exploitation of CVE-2024-12802 in SonicWall SSL VPNs. Gen6 devices require six manual LDAP reconfiguration steps after patching; attackers brute-forced credentials and bypassed MFA.

May 19, 2026
Threat Research · thehackernews.com

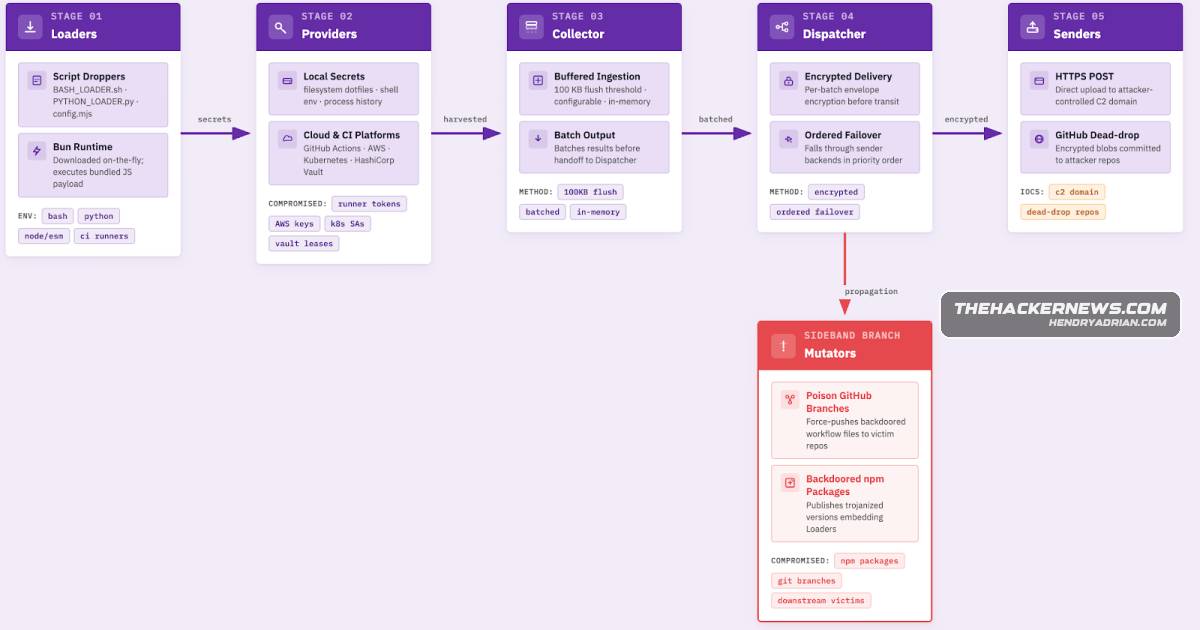
Mini Shai-Hulud Campaign Hits Hundreds of npm Packages, Including @antv

Researchers report 639 malicious releases across 323 npm packages, including @antv projects. The Mini Shai-Hulud payload steals credentials, propagates via stolen npm tokens, exfiltrates data, and abuses CI-issued Sigstore attestations.

May 19, 2026
Threat Research · wiz.io

TeamPCP Supply-Chain Campaign Targets npm Packages, GitHub Actions and a VSCode Extension

Wiz researchers detail a TeamPCP-attributed campaign that compromised developer tools to steal credentials, exfiltrate data and install a persistent backdoor. The investigation is ongoing; organizations are advised to check affected components and rotate exposed secrets

May 19, 2026
Threat Research · any.run

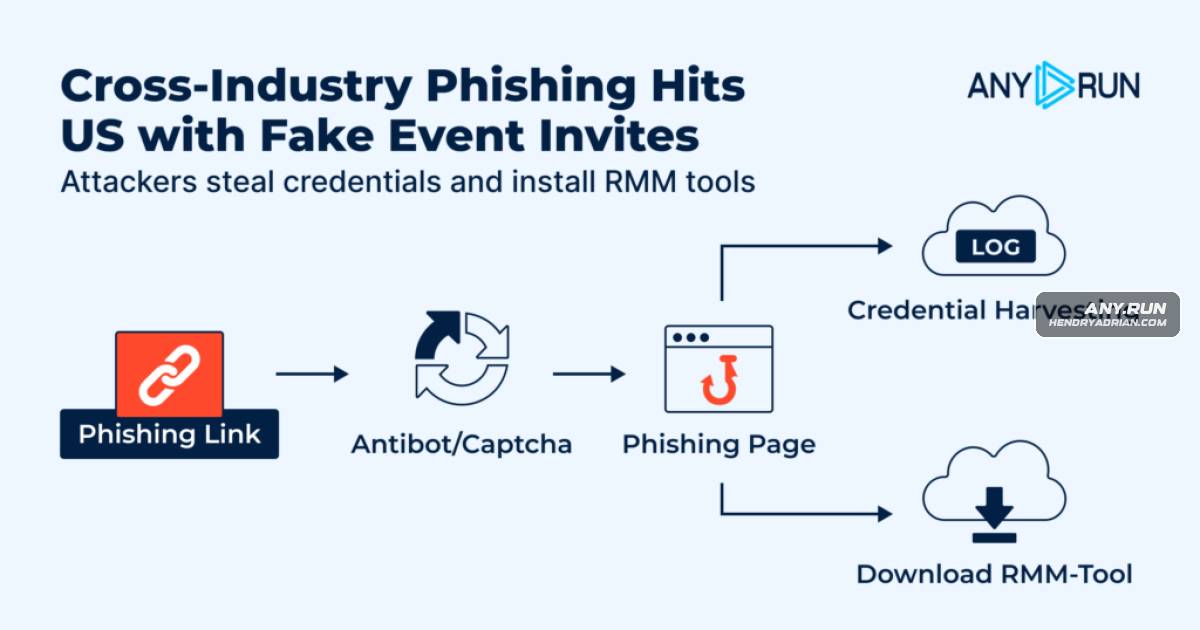
Researchers Detail Fake-Invitation Phishing Campaign Targeting U.S. Organizations

ANY.RUN researchers describe a fake-invitation phishing campaign targeting U.S. organizations. They report nearly 160 suspicious links and 80 domains, with pages that steal credentials and OTPs or deliver remote management tools.

May 19, 2026
Threat Research · any.run

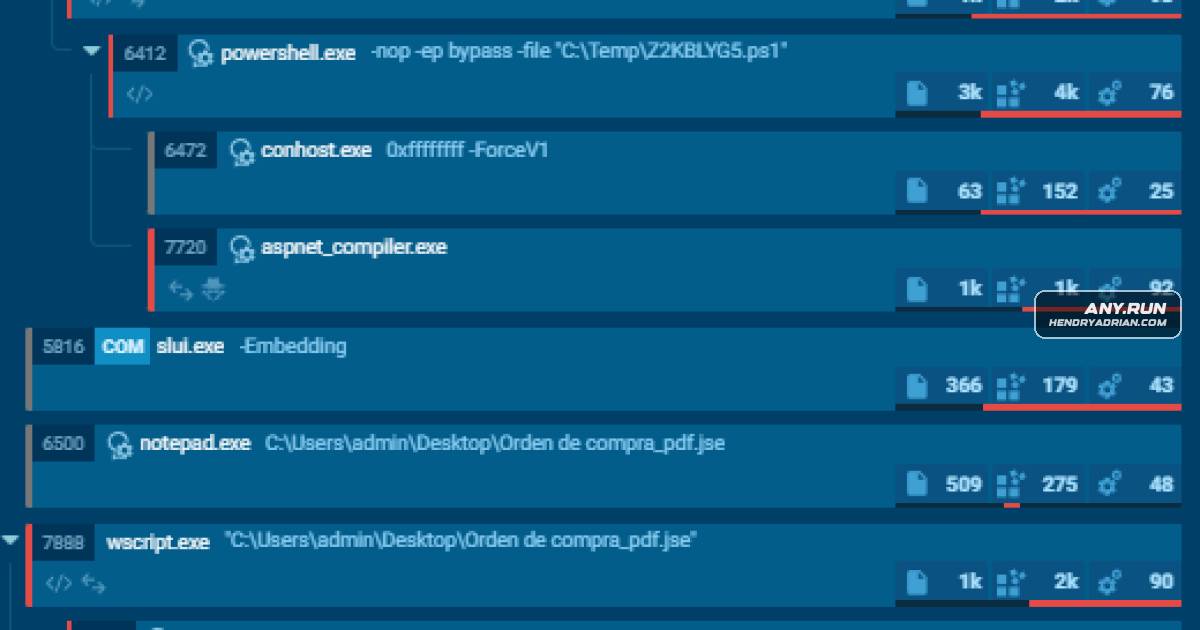
Investigation Details Agent Tesla Credential-Theft Campaign Targeting Chilean and LATAM Businesses

ANY.RUN's investigation links 80+ samples to an Agent Tesla campaign targeting Chilean and broader LATAM businesses since at least mid-2024, using procurement phishing, process hollowing and cleartext FTP credential exfiltration.

May 19, 2026
PreviousPage 60 of 104 Next
© 2026 cyber.hendryadrian.com