
Seqrite Details Operation Dragon Whistle Spear-Phishing Campaign Targeting Chinese University
Summary
Seqrite Labs reports that Operation Dragon Whistle used a fake Changzhou University fitness notice and a ZIP/LNK/VBScript chain to sideload a DLL and deliver an in-memory Cobalt Strike Beacon; it attributes the activity to UNG0002 with medium-high confidence.
Key points
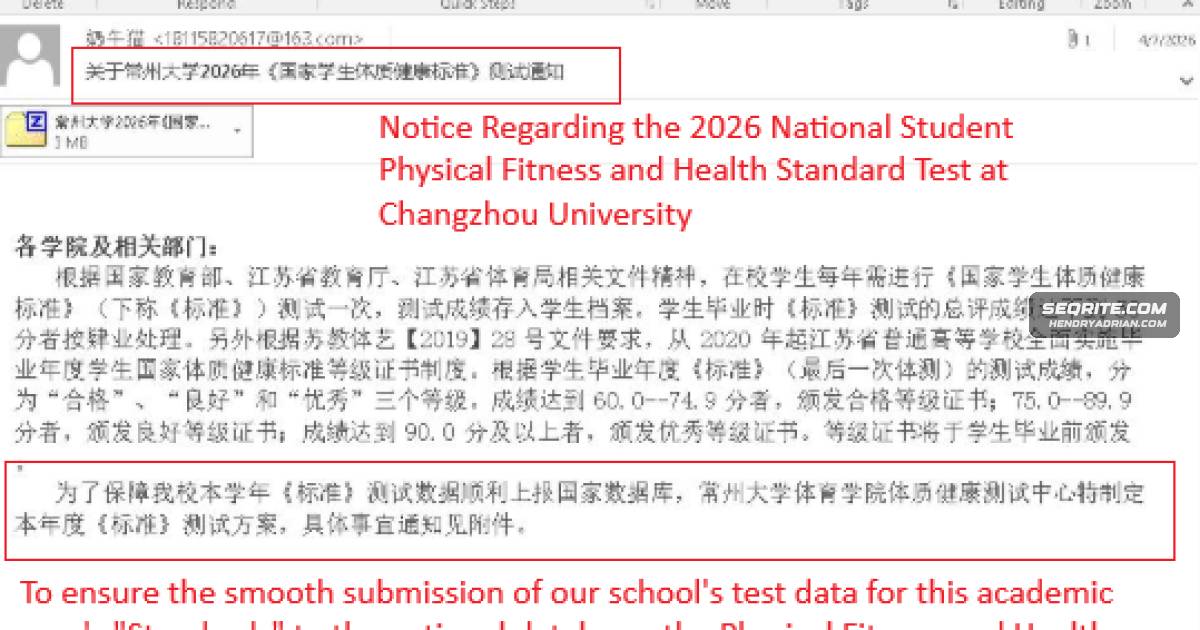
- Seqrite Labs says the campaign targeted Changzhou University students and staff with a spear-phishing email and a fake 2026 fitness-testing notice.
- The ZIP contained a disguised LNK file that launched a VBScript, opened a decoy PDF, and silently started Bandizip.
- Bandizip loaded the malicious ark.x64.dll through DLL sideloading; the DLL used encrypted strings and checks for debugging and monitoring tools.
- A staged payload interfered with AMSI and ETW, then decrypted and loaded a Cobalt Strike Beacon in memory.
- The Beacon attempted C2 communication with infrastructure hosted on Alibaba Cloud; the report identifies 60[.]205[.]186[.]162 and lysander[.]asia.
- Seqrite attributes the campaign to UNG0002 with medium-high confidence, citing TTP overlap with Operation Cobalt Whisper and infrastructure findings.
Article Details
- Attack Vectors
- A spear-phishing email impersonated a Changzhou University fitness-testing notice and delivered a malicious ZIP attachment.
- The ZIP contained a double-extension LNK disguised as a PDF; opening it triggered a VBScript execution chain.
- The VBScript opened a decoy PDF and silently launched Bandizip.exe, which sideloaded the malicious ark.x64.dll.
- The DLL used anti-debugging and process checks, then decrypted and loaded a Cobalt Strike Beacon in memory for C2 communication.
- Defensive Notes
- Inspect email attachments and archives for double-extension LNK files disguised as documents and files concealed in nested folders.
- Monitor for Bandizip.exe loading an unexpected ark.x64.dll from its local directory.
- Investigate suspicious VBScript activity that opens a decoy document while launching an archive utility in the background.
- Look for process enumeration targeting analysis and monitoring utilities, as well as attempts to interfere with AMSI or ETW.
- Hunt for the reported C2 indicators and for Cobalt Strike Beacon activity loaded directly into memory.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | lysander[.]asia | Reported C2 domain resolving to 60[.]205[.]186[.]162. |
18115820617@163[.]com | Reported sender address for the spear-phishing email. | |
| IPV4 | 60[.]205[.]186[.]162 | Reported C2 infrastructure used by the Beacon and hosted on Alibaba Cloud. |
| SHA256 | 35a478f53f64bd412f374c65360fdba0518749537193669a8fe08d14bed65a2a | SHA-256 of the malicious ark.x64.dll used for DLL sideloading. |
| SHA256 | cd99e83d241cfbb41bfcd0bc622a87d16268e710ca7d736d0c5f44774e0056e2 | SHA-256 of the disguised LNK file that initiates the infection chain. |
| SHA256 | e7aff6a55a7866776272d9913dfbf9d7db33fc9de6aced22f2a195feebb0e85f | SHA-256 of the malicious ZIP attachment. |
| SHA256 | eb14d9e35a3bf0a933297f861bee0be9e6b9061fe4573a81ac92b71d55b6474f | Hash listed by the article as an artifact of the spear-phishing email. |
| SHA256 | ed7087e3afba4b320bdf04f32d3a6c567effd3d18a97682968e567000e70b335 | SHA-256 of the Cobalt Strike Beacon payload. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe DLL decrypted strings and payloads at runtime to conceal them from static analysis.T1036 · MasqueradingThe LNK file used a PDF filename and icon to masquerade as a document.T1057 · Process DiscoveryThe DLL enumerated running processes to identify debugging, monitoring, and network-analysis tools.T1059.005 · Visual BasicThe chromedo.vbs script opened the decoy PDF and launched Bandizip.exe.T1106 · Native APIThe process-enumeration routine used Windows APIs including CreateToolhelp32Snapshot, Process32First, and Process32Next.T1129 · Shared ModulesThe legitimate Bandizip process loaded the malicious DLL as a shared module.T1204.002 · Malicious FileThe victim had to open the disguised LNK file to trigger the execution chain.T1497.001 · System ChecksThe malware checked for analysis environments by enumerating processes and comparing them against a blacklist.T1564.001 · Hidden Files and DirectoriesThe article reports that payload files were concealed in nested folders and a hidden directory.T1566.001 · Spearphishing AttachmentThe spear-phishing email delivered the malicious ZIP attachment.T1574.002 · DLL Side-LoadingBandizip.exe loaded the attacker-controlled ark.x64.dll from its local directory.T1622 · Debugger EvasionThe DLL used debugger checks including CheckRemoteDebuggerPresent and IsDebuggerPresent.