
Investigation Details Agent Tesla Credential-Theft Campaign Targeting Chilean and LATAM Businesses
Summary
ANY.RUN's investigation links 80+ samples to an Agent Tesla campaign targeting Chilean and broader LATAM businesses since at least mid-2024, using procurement phishing, process hollowing and cleartext FTP credential exfiltration.
Key points
- The investigation reports Spanish-language purchase-order and other finance-themed lures delivered in RAR archives, including one with a misleading .uu extension.
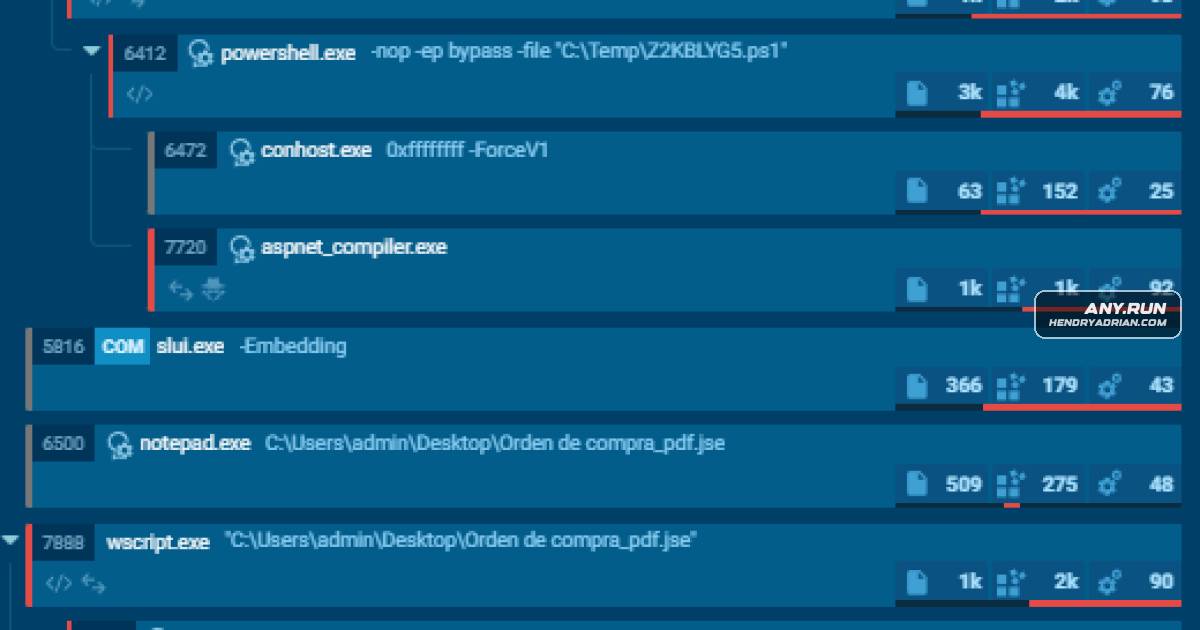
- The observed chain used a JScript dropper and PowerShell stagers to load ALTERNATE.dll and hollow the trusted aspnet_compiler.exe process.
- Analysis found the loader protected with .NET Reactor 6.x and using obfuscation, encrypted payload loading and in-memory execution.
- The Agent Tesla payload targeted credentials from browsers, email and other applications, and could capture keystrokes, clipboard contents and screenshots.
- Sandbox analysis captured cleartext FTP exfiltration to ftp.horeca-bucuresti[.]ro; the investigation links the infrastructure to more than 80 related samples.
- The article provides Suricata, YARA and Sigma detection examples, along with guidance on monitoring outbound FTP and suspicious procurement attachments.
Article Details
- Attack Vectors
- Spanish-language procurement and finance-themed spear-phishing delivered a RAR archive named Orden de compra_pdf.uu.
- The archive yielded a JScript-encoded .jse dropper executed by wscript.exe; it launched PowerShell stagers with ExecutionPolicy Bypass and modified registry keys for persistence.
- The PowerShell stager loaded the .NET Reactor-protected ALTERNATE.dll and used process hollowing to run Agent Tesla inside aspnet_compiler.exe.
- Agent Tesla stole browser and other application credentials, recorded keystrokes, monitored clipboard contents, and captured screenshots.
- Stolen data was exfiltrated over cleartext FTP to infrastructure the article identifies as a compromised Romanian hospitality website.
- Defensive Notes
- Submit suspicious attachments for interactive sandbox analysis, particularly RAR archives with unusual extensions and procurement-themed lures.
- Monitor outbound FTP, including port 21 traffic and STOR commands with the PW_*.html exfiltration naming pattern.
- Alert on PowerShell launching aspnet_compiler.exe and investigate suspected process hollowing.
- Quarantine unexpected external attachments with .uu, .jse, or .vbe extensions, and scrutinize macro-enabled Office files received in procurement contexts.
- Provide targeted security-awareness training for finance and procurement teams.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | email[.]elrif[.]com | Passive DNS analysis linked this hostname to email-relay infrastructure on the C2 IP; the article describes the pattern as consistent with relay abuse for phishing delivery. |
| DOMAIN | email[.]v[.]todotramitesperu[.]com[.]elgartizocon[.]ro | Passive DNS analysis linked this hostname to email-relay infrastructure on the C2 IP; the article describes the pattern as consistent with relay abuse for phishing delivery. |
| DOMAIN | ftp[.]horeca-bucuresti[.]ro | Hostname of the compromised FTP server used as the credential drop zone. |
| IPV4 | 89[.]39[.]83[.]184 | IP address of the compromised host used for Agent Tesla FTP credential exfiltration. |
| MD5 | 78ba57f4a164bedc26204296ea09bb8f | MD5 hash of the decrypted Agent Tesla payload. |
| MD5 | a7eeead9c868d9944ed1c1f113328f32 | MD5 hash of the malicious RAR archive. |
| SHA1 | b50b3800b17ad7ad5c4483c0b6b24d1d151a9d10 | SHA-1 hash of the malicious RAR dropper. |
| SHA256 | 43d09743a69c9afa7156bf4e2bf7423b3d5f5ad7d54c4c3fb8a698d526778057 | SHA-256 hash of the decrypted Agent Tesla payload recovered from memory. |
| SHA256 | 7929355856a2a85d48f95d230cd74fbb5ad554bed49e73b1800136c4bcccd1a8 | SHA-256 hash listed for the malicious RAR dropper. |
| SHA256 | 948c8c69fe02eda9231aebfa5c626335307058ac74a5c3c40b346179a1bfc982 | SHA-256 hash identified for the malicious RAR campaign archive. |
| SHA256 | 96ad1146eb96877eab5942ae0736b82d8b5e2039a80d3d6932665c1a4c87dcf7 | SHA-256 hash shared by the campaign's PowerShell stager scripts. |
| SHA256 | cd83f5ceb2d014badfa991106a9d37a6aeab9043d60d796ad0f16d36cdfa5703 | SHA-256 hash of the JScript-encoded dropper. |
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryThe payload queried ip-api.com/line/?fields=hosting before exfiltration to check the victim's hosting environment.T1027 · Obfuscated Files or InformationThe dropper used JScript encoding and a misleading .uu archive extension to hinder inspection and detection.T1027.002 · Software PackingALTERNATE.dll used .NET Reactor 6.x virtualization and control-flow obfuscation.T1048.003 · Exfiltration Over Unencrypted Non-C2 ProtocolThe malware exfiltrated stolen data over cleartext FTP to the compromised FTP server.T1055.012 · Process HollowingThe stager hollowed aspnet_compiler.exe and ran the Agent Tesla payload in that process.T1056.001 · KeyloggingThe payload implemented system-wide keylogging using Windows hook APIs.T1059.001 · PowerShellPowerShell stagers were launched with ExecutionPolicy Bypass.T1059.007 · JavaScriptwscript.exe executed the JScript-encoded .jse dropper.T1082 · System Information DiscoveryThe payload collected CPU, RAM, OS version, hostname, and username information.T1113 · Screen CaptureThe payload captured periodic desktop screenshots and included them in the exfiltration report.T1115 · Clipboard DataThe payload used clipboard hooks to collect copied text and include it in the exfiltration report.T1547.001 · Registry Run Keys / Startup FolderThe dropper modified registry keys for persistence; the payload's documented persistence options include a Registry Run key.T1555.003 · Credentials from Web BrowsersThe payload accessed Chrome and Firefox credential stores to steal saved credentials.T1566.001 · Spearphishing AttachmentThe campaign delivered a procurement-themed malicious RAR attachment by email.
Malware
Vendors
ANY.RUNfull investigation methodology, from initial triage to infrastructure correlation, and demonstrates how ANY.RUN’s interactive sandbox and threat intelligence capabilities accelerated key phases of the analysis.MicrosoftTheft of browser credential databases can therefore expose Microsoft 365, Google Workspace, Salesforce, SAP, and other critical business systems without the attacker needing to deploy ransomware or exploit
Products
.NET FrameworkThe choice of injection target is deliberate: aspnet_compiler.exe is a trusted .NET Framework component, and its network activity is rarely flagged by endpoint security tools..NET Reactor 6.xThe loader ALTERNATE.dll was protected with .NET Reactor 6.x, control-flow obfuscation, virtualization, and anti-decompilation measures.Google Chrome[T1555.003 ] Credentials from Web Browsers – The payload accessed Chrome and Firefox credential stores to steal saved passwords [‘Chrome, Firefox credential store access confirmed’]Interactive Sandboxmethodology, from initial triage to infrastructure correlation, and demonstrates how ANY.RUN’s interactive sandbox and threat intelligence capabilities accelerated key phases of the analysis.Microsoft Windows[T1059.007 ] JavaScript – The .jse dropper was executed by Windows Script Host via wscript.exe [‘wscript.exe executes .jse dropper’]Mozilla Firefox[T1555.003 ] Credentials from Web Browsers – The payload accessed Chrome and Firefox credential stores to steal saved passwords [‘Chrome, Firefox credential store access confirmed’]PowerShellThe infection chain used a JScript encoded dropper, PowerShell stagers, and process hollowing into aspnet_compiler.exe to execute the payload in memory.Threat Intelligence LookupPivoting on the campaign in ANY.RUN Threat Intelligence Lookup with the query submissionCountry:”cl” AND threatLevel:”malicious” confirms Chile as the primary submission country, and surfaces correlated behavioral
Tools
de4dotThe use of .NET Reactor 6.x explains why standard tools like de4dot fail without additional flags.Detect It EasyStatic analysis with Detect-It-Easy reveals a sophisticated protection stack: NETReactorSlayerThe correct tool for this protection version is NETReactorSlayer: SnortNetwork-Level (Suricata/Snort)SuricataANY.RUN flagged this request with the Suricata rule: “ET MALWARE Common Stealer Behavior — Source IP Associated with Hosting Provider Check via ip-api.com”, confirming the pre-exfiltration fingerprinting behavior.VirusTotalQuerying the IP on VirusTotal reveals 80 malicious files that have communicated with this server, with the earliest samples dating to September 2024 — confirming the infrastructure has been actively maintained for at