cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2484 articles

Threat Research · socket.dev

Mini Shai-Hulud Compromises 639 npm Package Versions in AntV-Heavy Campaign

Socket reports 639 compromised npm package versions across 323 packages in a Mini Shai-Hulud wave. The obfuscated install-time payload targets developer secrets, exfiltrates data, and can republish malicious packages using stolen npm tokens.
May 19, 2026
Threat Research · stepsecurity.io

StepSecurity Details Mini Shai-Hulud Attack on AntV npm Ecosystem

StepSecurity details a Mini Shai-Hulud campaign that it says poisoned npm packages across AntV and related projects, stealing CI/CD credentials. Its analysis traces package-install execution, credential theft and exfiltration, persistence, and runner defenses.

May 19, 2026
Threat Research · stepsecurity.io

Durabletask Supply-Chain Attacks Hit PyPI Package and Azure GitHub Repository

Microsoft confirmed malicious durabletask PyPI versions 1.4.1–1.4.3 were uploaded and yanked; analysis traced a credential-stealing cloud framework. The article also reports a June 5 Azure/durabletask commit that added malware triggered by AI coding tools and VS Code.

May 19, 2026
Threat Research · trendmicro.com

Researchers Map Banana RAT’s End-to-End Operation Targeting Brazilian Banks

Trend Micro researchers mapped Banana RAT’s delivery infrastructure and victim-side execution, detailing its polymorphic PowerShell payloads, remote-control capabilities, Pix QR interception, and targeting of Brazilian financial institutions.

May 19, 2026
Threat Research · bleepingcomputer.com

SHub ‘Reaper’ macOS Infostealer Uses Fake Apple Updates to Steal Data

SentinelOne describes Reaper, a SHub macOS infostealer that uses a fake Apple update and malicious AppleScript to steal credentials, wallet and browser data, and files, while establishing LaunchAgent persistence and enabling additional payloads.

May 18, 2026
Threat Research · forcepoint.com

TeamPCP Used Malicious LiteLLM Releases to Steal Credentials

Forcepoint traces how TeamPCP used a compromised Trivy build tool to publish malicious LiteLLM versions that stole AI, cloud and developer credentials, exfiltrated data, and installed a persistent backdoor.

May 18, 2026
Threat Research · securityonline.info

Leaked Rocket Database Reveals The Gentlemen Ransomware Group’s Operations

Check Point Research analyzed a reported 16 GB leak of The Gentlemen’s Rocket database, detailing the group’s structure, tools, edge-device exploitation, NTLM relay workflows, AI use, and an alleged UK-to-Turkey intrusion.

May 18, 2026
Threat Research · stepsecurity.io

Compromised GitHub Actions Tags Redirect Workflows to Credential-Stealing Commits

StepSecurity reports that all tags for actions-cool/issues-helper and actions-cool/maintain-one-comment were moved to malicious commits. The payload reads Runner.Worker memory to harvest secrets and attempts exfiltration to t[.]m-kosche[.]com.

May 18, 2026
Threat Research · stepsecurity.io

Nx Console VS Code Extension Compromise Deployed Credential-Stealing Payload

Step Security details how malicious Nx Console v18.95.0 used a stolen contributor token and hidden orphan commit to run a payload targeting developer secrets and persistence. It recommends rotating all accessible credentials and rebuilding affected machines.

May 18, 2026
Threat Research · bleepingcomputer.com

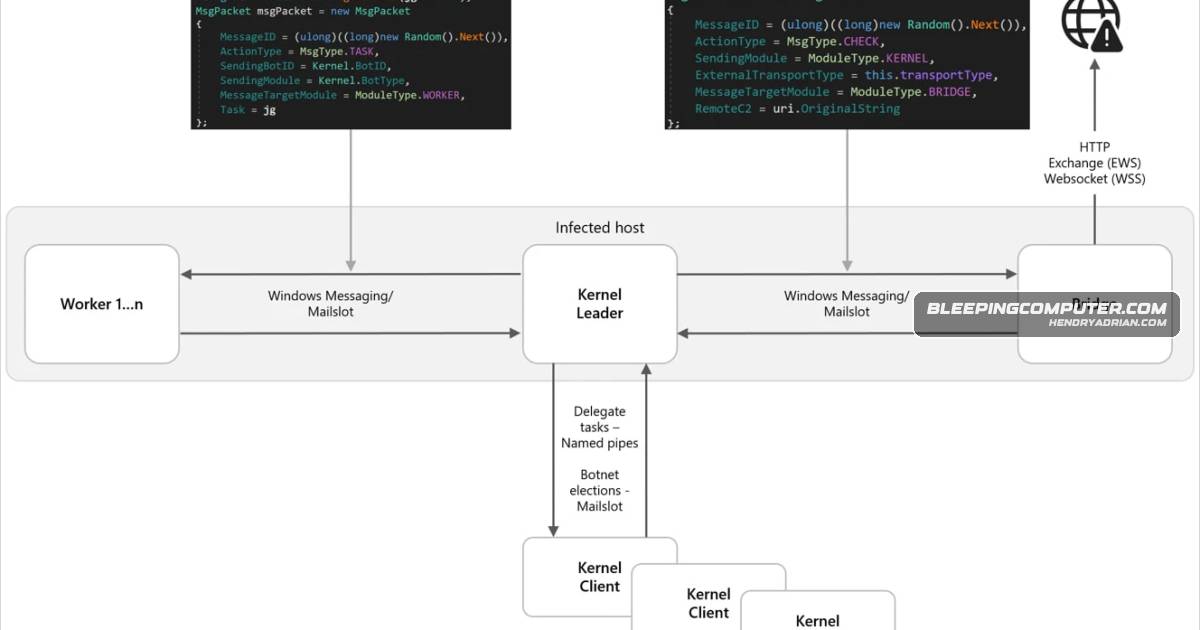
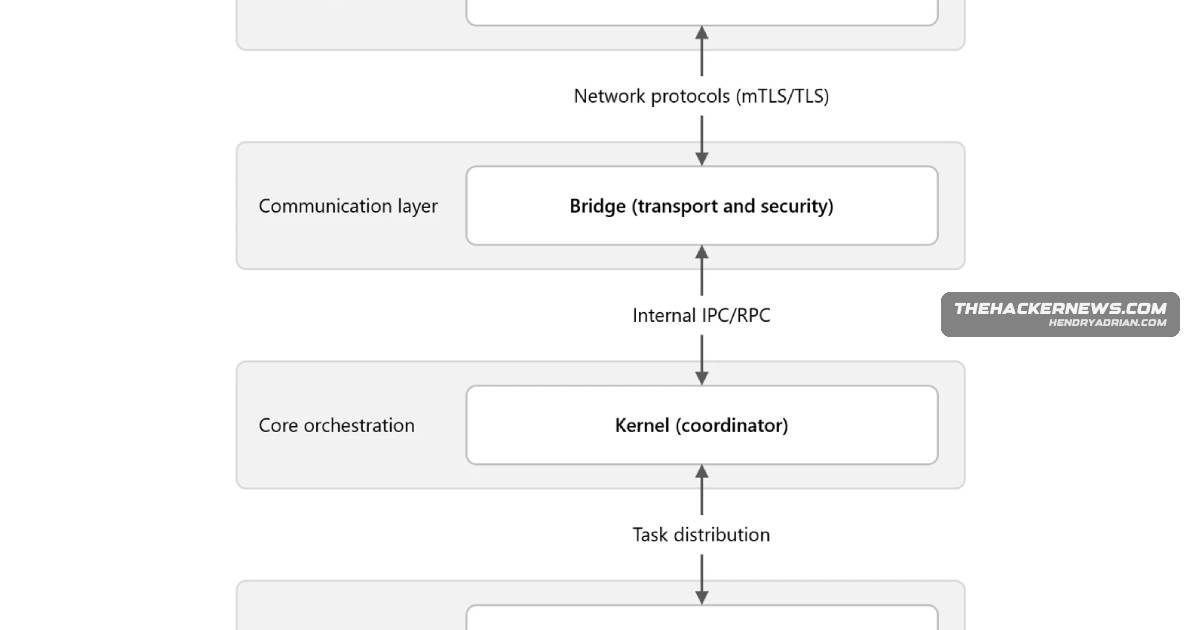
Microsoft Details Kazuar’s Modular Peer-to-Peer Espionage Botnet

Microsoft researchers say a recent Kazuar variant uses kernel, bridge, and worker modules in a leader-based P2P botnet. It collects data and uses configurable defense bypasses, with non-leader systems staying silent to reduce visibility.

May 16, 2026
Threat Research · security.com

Fast16 Malware Was Built to Alter Nuclear-Weapons Simulations, Researchers Say

Researchers say Fast16, whose components may date to around 2005, used tailored hooks to alter LS-DYNA and AUTODYN high-explosive and uranium simulation outputs. It spread within networks through services, IFEO persistence and remote shares.

May 16, 2026
Threat Research · welivesecurity.com

FrostyNeighbor Uses PDF Lures and PicassoLoader Against Ukrainian Government Targets

ESET reports that FrostyNeighbor targeted Ukrainian government organizations from March 2026 with spearphishing PDF lures, a JavaScript PicassoLoader chain, server-side victim checks, and a Cobalt Strike payload.

May 16, 2026
Threat Research · feeds.fortinet.com

PawsRunner Uses PNG Steganography to Deliver PureLogs Infostealer

FortiGuard Labs details a Windows phishing chain using an invoice-themed TXZ attachment, hidden JavaScript commands and the PawsRunner loader to deploy PureLogs, which collects browser, wallet and app data and exfiltrates it over HTTPS.

May 16, 2026
Threat Research · cloud.google.com

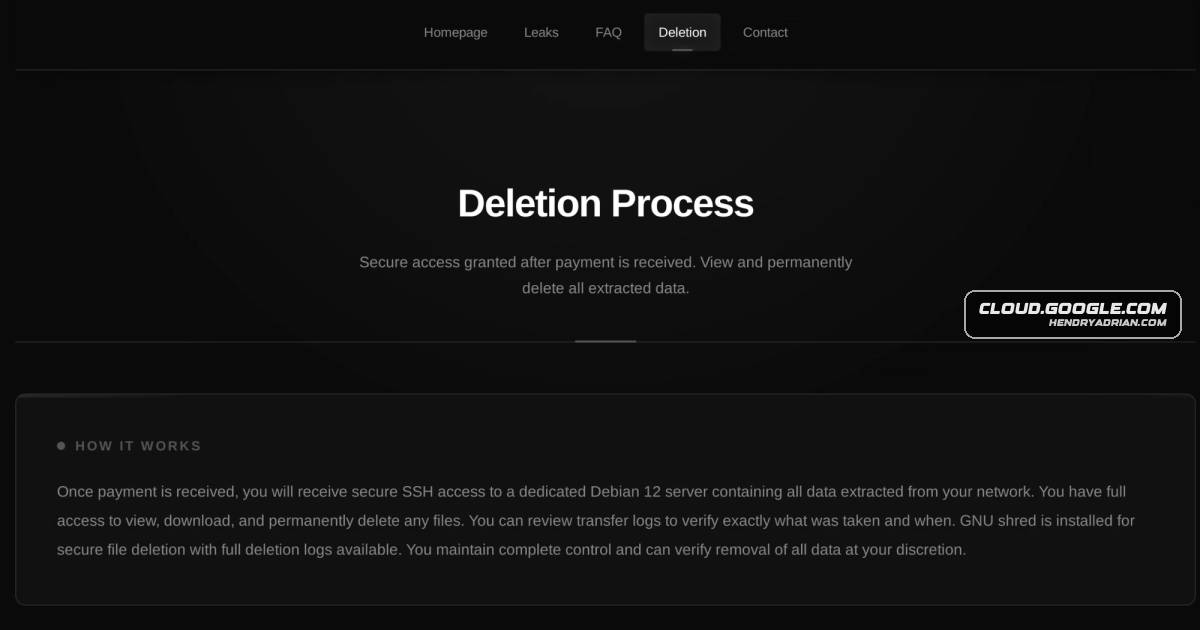
Google Details UNC6671’s BlackFile Vishing and SaaS Extortion Operations

Google GTIG details UNC6671’s vishing and AiTM attacks against Microsoft 365 and Okta, scripted SaaS data theft, and extortion tactics. It also shares forensic indicators and defensive guidance; the BlackFile leak site’s shutdown may signal a rebrand.

May 16, 2026
Threat Research · bleepingcomputer.com

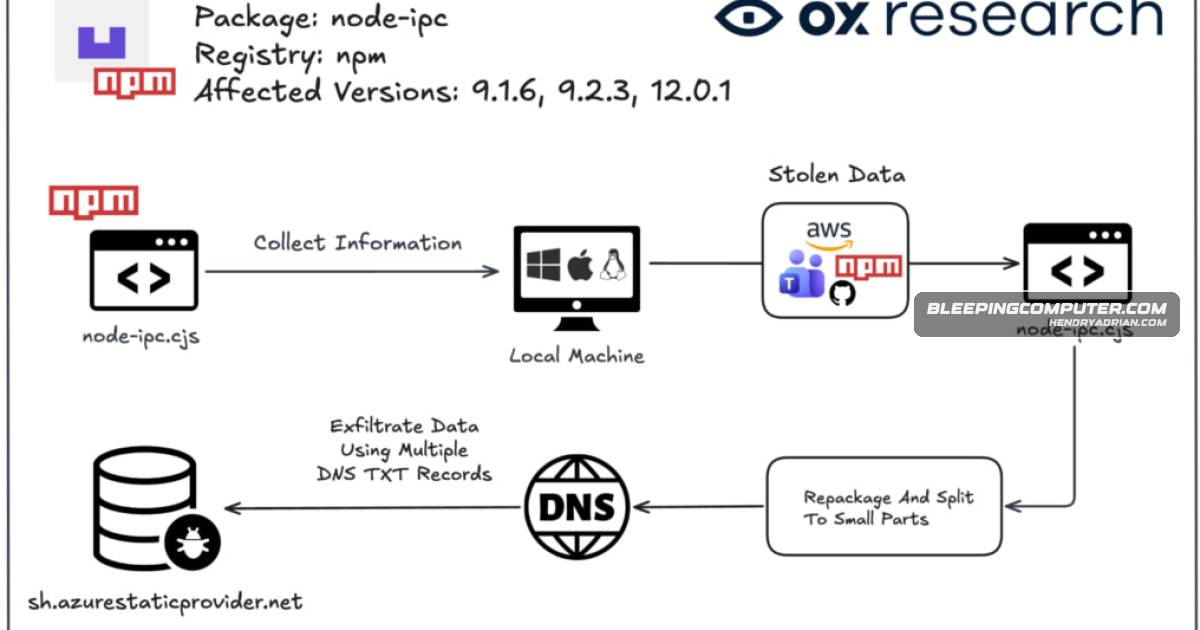
Malicious node-ipc npm Versions Steal Developer Credentials via DNS

Researchers identified malicious node-ipc versions 9.1.6, 9.2.3 and 12.0.1 that reportedly steal developer and cloud credentials and exfiltrate archives through DNS TXT queries after a maintainer account was compromised.

May 15, 2026
Threat Research · thehackernews.com

Microsoft Details Turla’s Modular Kazuar P2P Botnet

Microsoft reports that Turla evolved Kazuar into a modular P2P botnet. Its Kernel, Bridge, and Worker modules coordinate tasks, communicate with command-and-control infrastructure, collect data, and support stealthy persistence.

May 15, 2026
Threat Research · unit42.paloaltonetworks.com

Gremlin Stealer Adds Resource-Hidden Payloads and Live-Session Hijacking

Unit 42 compares Gremlin Stealer variants, detailing .NET resource and XOR payload concealment, virtualization and staged loading, plus theft of browser credentials, Discord tokens and clipboard data, crypto clipping, and live-session hijacking.

May 15, 2026
Threat Research · guardsix.com

Qilin Ransomware Group Expands Cross-Platform Operations and Extortion Tactics

An analysis of Qilin’s growth as a ransomware-as-a-service operation details its Windows, Linux, and ESXi capabilities, intrusion techniques, extortion methods, targeted sectors, and recommended defenses.

May 15, 2026
Threat Research · thehackernews.com

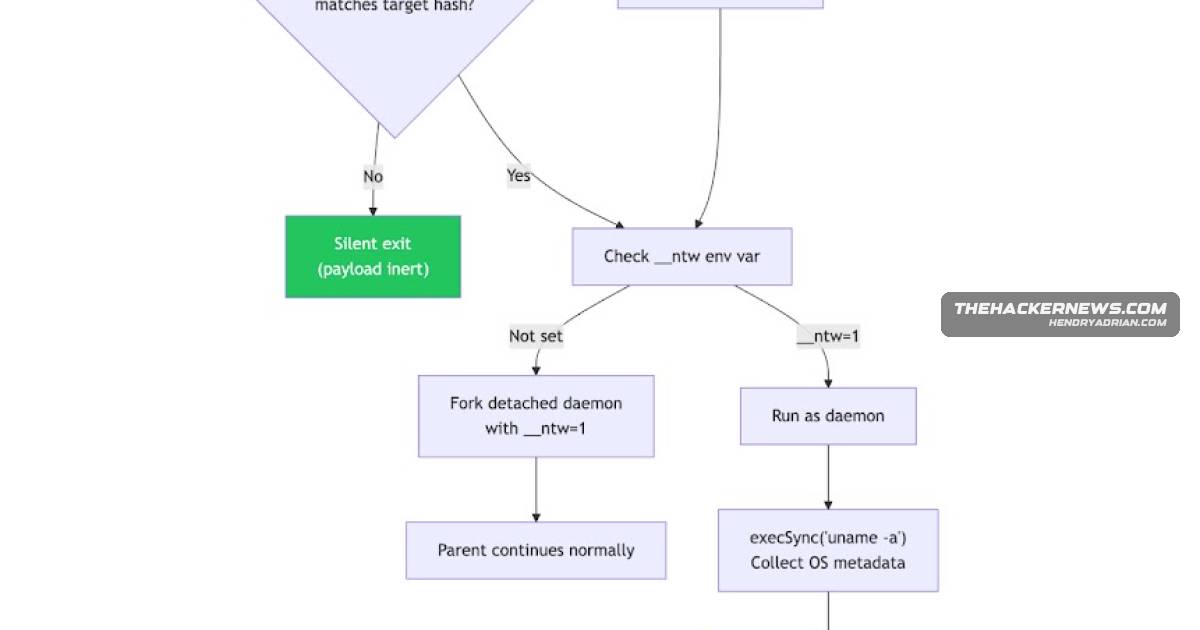
Researchers Detail Malicious node-ipc Versions That Steal Developer Secrets

Socket and StepSecurity report that node-ipc versions 9.1.6, 9.2.3, and 12.0.1 contain credential-stealing code, with version 12.0.1 gated by a system fingerprint. The malware uses HTTPS and DNS exfiltration.

May 15, 2026
Threat Research · validin.com

Six-Month Review Finds C2 Fingerprints Outlast YouTube DMCA Phishing Indicators

A six-month review found IP, CSS and favicon pivots from a YouTube DMCA phishing campaign quickly went stale, while C2 banner/header hashes and newer title-tag and redirect patterns exposed related infrastructure.

May 15, 2026
Threat Research · labs.beazley.security

Beazley Details CMD Organization Ransomware Intrusion and Public Data-Bidding Model

Beazley Security details a CMD Organization intrusion involving an SEO-poisoned lure, a 25-day dwell, backdoor persistence and GPO/SYSVOL ransomware deployment; the group’s leak site also offers crypto bidding for stolen data.

May 14, 2026
Threat Research · socket.dev

Malicious node-ipc npm Versions Steal Developer Credentials via DNS

Three malicious node-ipc versions execute a credential-stealing payload when loaded through CommonJS. The malware collects developer and CI secrets and exfiltrates them via DNS TXT queries; developers are urged to remove affected versions and rotate exposed credentials.

May 14, 2026
Threat Research · bleepingcomputer.com

KongTuke Uses Microsoft Teams to Deploy ModeloRAT and Establish Persistence

ReliaQuest reports that KongTuke uses Microsoft Teams social engineering to deliver ModeloRAT via PowerShell. The campaign can establish persistent access in under five minutes and uses multiple access paths and persistence mechanisms.

May 14, 2026
Threat Research · proofpoint.com

Device Code Phishing Surges as Criminal Kits Expand OAuth Token Theft

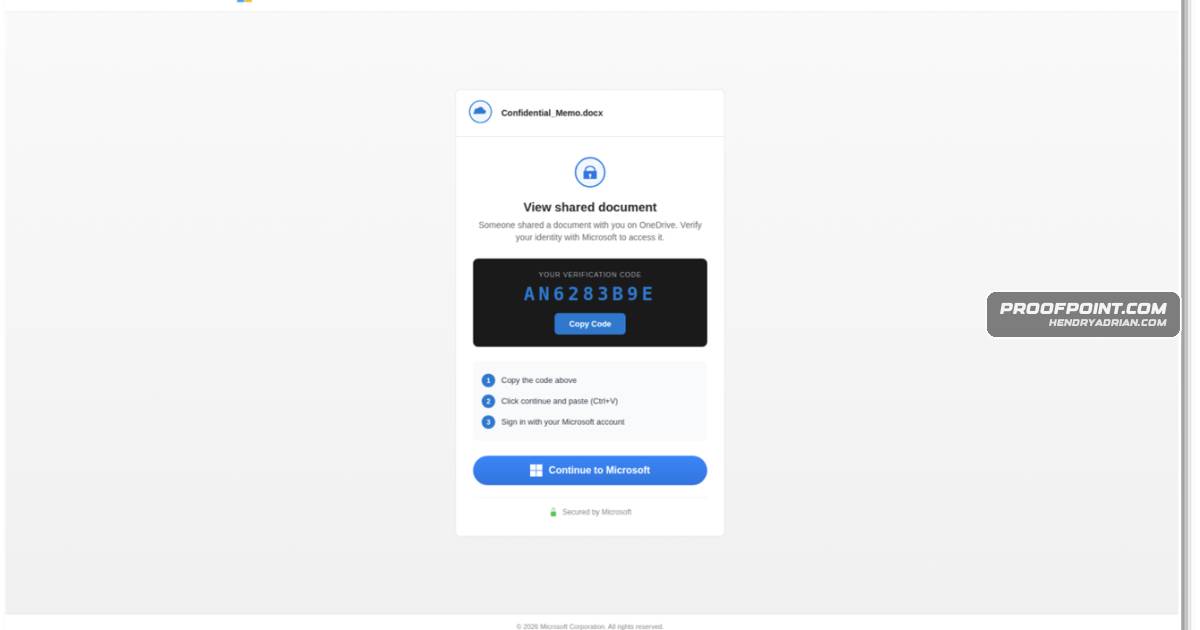
Proofpoint reports a surge in device code phishing using public kits and PhaaS offerings to abuse OAuth 2.0 and steal account tokens. Campaigns target mainly Microsoft 365, with Google-themed activity also observed; recommended defenses include blocking device code flow

May 14, 2026
PreviousPage 61 of 104 Next
© 2026 cyber.hendryadrian.com