
Fake Teams Sites Deliver ValleyRAT Through NSIS and DLL Sideloading
Summary
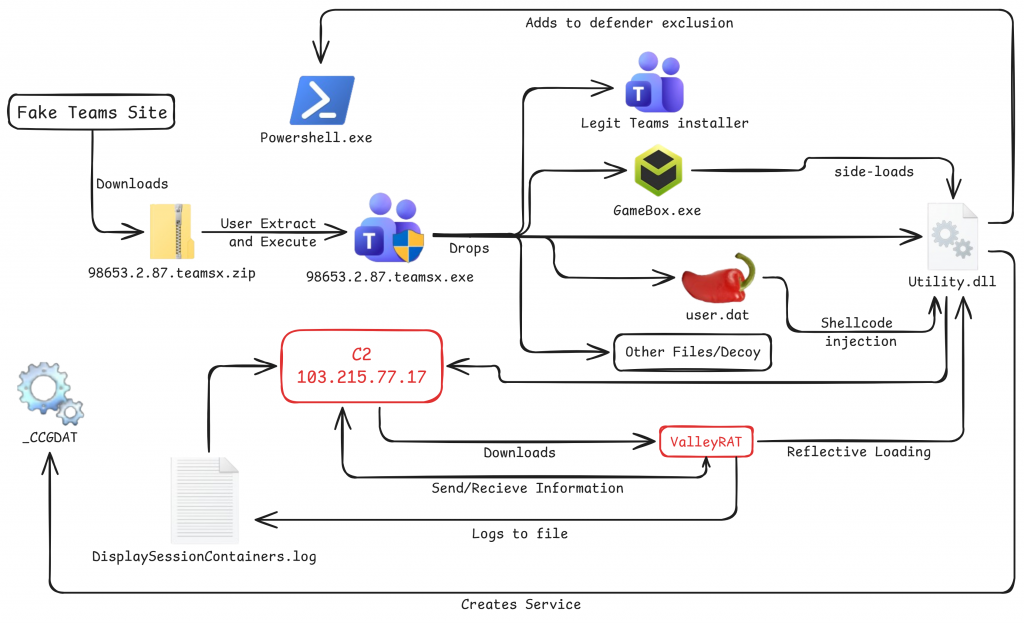
Researchers traced a fake Teams campaign to a multistage ValleyRAT infection using an NSIS installer and GameBox.exe DLL sideloading. The malware evaded Defender, captured clipboard and log data, and communicated with a C2 server.
Key points
- Fake Teams download sites distributed ZIP archives that launched a malicious NSIS installer alongside a legitimate Teams installer.
- The installer abused Tencent’s GameBox.exe to sideload utility.dll.
- The malware added Windows Defender exclusions and hid components in ProgramData.
- Researchers captured an AES-decrypted shellcode loader in memory; later stages used XOR decryption, API hashing, and reflective loading.
- The final payload was identified as a ValleyRAT variant. Registry and behavioral similarities led researchers to assess a likely connection to SilverFox activity.
- The malware accessed clipboard contents, recorded activity in local logs, and communicated with C2 infrastructure at 103.215.77.17.
Article Details
- Attack Vectors
- Fake Microsoft Teams download sites lured users into downloading trojanized ZIP archives containing a malicious NSIS installer.
- The installer abused the legitimate Tencent GameBox.exe to sideload utility.dll and deploy a ValleyRAT variant.
- The malware weakened Windows Defender by adding exclusion paths and processes through PowerShell.
- The loader decrypted payloads in memory, injected shellcode into the current process, and used reflective loading for the final payload.
- The malware captured clipboard contents and keystrokes, stored collected data in local logs, and sent data to its C2 server.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | teams-securecall[.]com | Fake Microsoft Teams lure site used to distribute a trojanized archive. |
| DOMAIN | teamszs[.]com | Fake Microsoft Teams lure site used to distribute a trojanized archive. |
| IPV4 | 103[.]215[.]77[.]17 | C2 server used for outbound communication and reported transfer of collected data. |
| MD5 | 18f3e85d7237e3cac0ad13bdcf513f0f | Hash reported for the malicious sideloaded file Utility.dll. |
| MD5 | 709604ce58e3f8255587ac9253db6994 | Hash reported for the malicious ZIP archive 98653.2.87.teamsx.zip. |
| MD5 | 8f9de887e9aed9d580f386ba2d191319 | Hash reported for the malicious payload file User.dat. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationPayloads were AES- or XOR-encrypted and decrypted in memory.T1027.007 · Dynamic API ResolutionThe loader and final payload used API hashing to resolve Windows APIs at runtime.T1036 · MasqueradingThe fake download sites and installer were made to resemble legitimate Microsoft Teams downloads.T1041 · Exfiltration Over C2 ChannelThe malware reportedly sent collected logs and data back to its C2 server.T1055 · Process InjectionThe loader allocated memory in the current process, wrote decrypted shellcode there, and executed it.T1056.001 · KeyloggingLocal logs reportedly contained captured keystrokes.T1105 · Ingress Tool TransferUsers downloaded a malicious archive, and a later payload stage was retrieved dynamically from the C2 server.T1106 · Native APIThe malware used Windows APIs including CreateThread, GetClipboardData, SetFileAttributes, and BcryptDecrypt.T1115 · Clipboard DataThe malware accessed clipboard contents through GetClipboardData.T1543.003 · Windows ServiceThe sideloaded DLL created the auto-start service _CCGDAT for persistence.T1562.001 · Disable or Modify ToolsPowerShell commands added Windows Defender exclusion paths and processes.T1574.002 · DLL Side-LoadingThe legitimate GameBox.exe loaded the malicious utility.dll through DLL sideloading.T1620 · Reflective Code LoadingThe final payload used reflective loading to map its PE into memory.
Threat Actors
Malware
Vendors
Products
GameBox.exeThe campaign abuses GameBox.exe for DLL sideloading, evades Windows Defender, steals clipboard and log data, and communicates with a C2 server at 103.215.77.17.Microsoft TeamsFake Microsoft Teams download sites were used to distribute a trojanized ZIP archive that installs a multistage loader chain ending in ValleyRAT.Windows DefenderThe campaign abuses GameBox.exe for DLL sideloading, evades Windows Defender, steals clipboard and log data, and communicates with a C2 server at 103.215.77.17.