
TeamPCP Campaign Republished 324 npm Packages Across 645 Versions
Summary
Researchers report TeamPCP compromised two npm maintainer accounts and republished 324 packages across 645 versions, putting packages with about 16 million weekly downloads at risk. Payload analysis is ongoing; the article recommends pinning known-good versions and aud
Key points
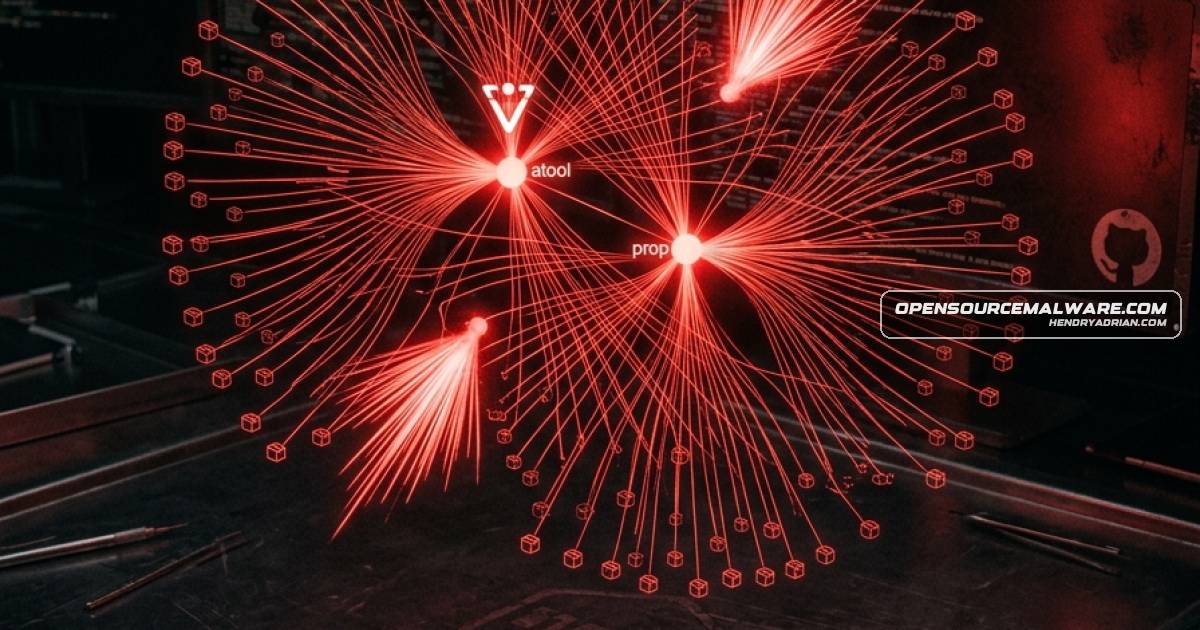
- The investigation attributes the npm campaign to TeamPCP and reports compromised maintainer accounts atool and prop.
- The atool account published new versions of 318 packages in two concentrated waves; prop published six more packages.
- In total, 324 packages were republished across 645 package-version artifacts, with about 16 million combined weekly downloads.
- The article cites rapid publishing across unrelated repositories as evidence consistent with automated use of stolen publishing credentials.
- The malicious payloads had not yet been fully analyzed; the article says tarball analysis was in progress.
- Recommended steps include pinning pre-wave versions, auditing lockfiles and CI caches, temporarily blocking install scripts, and rotating exposed credentials.
Article Details
- Attack Vectors
- TeamPCP compromised the npm maintainer accounts atool and prop and used their publishing access to republish 324 packages across 645 package-version artifacts.
- The article says the burst pattern is consistent with token-based automated publishing; phishing credentials, leaked automation tokens, and compromised CI secrets are described as possible routes, not confirmed initial-access methods.
- The republished tarballs' payload analysis was still in progress; injected code, postinstall hooks, obfuscated blobs, and outbound network calls were listed as items to investigate, not confirmed findings.
- Defensive Notes
- Pin affected dependencies to a known-good version published before 2026-05-19T01:39:31Z and hold them there until the republished versions are cleared.
- Audit lockfiles and CI caches for any of the 645 affected versions resolved after the first publish wave.
- Use npm install --ignore-scripts to block install scripts until the tarballs are confirmed clean.
- Rotate credentials exposed to builds that ran an affected version.