
Researchers Detail Fake-Invitation Phishing Campaign Targeting U.S. Organizations
Summary
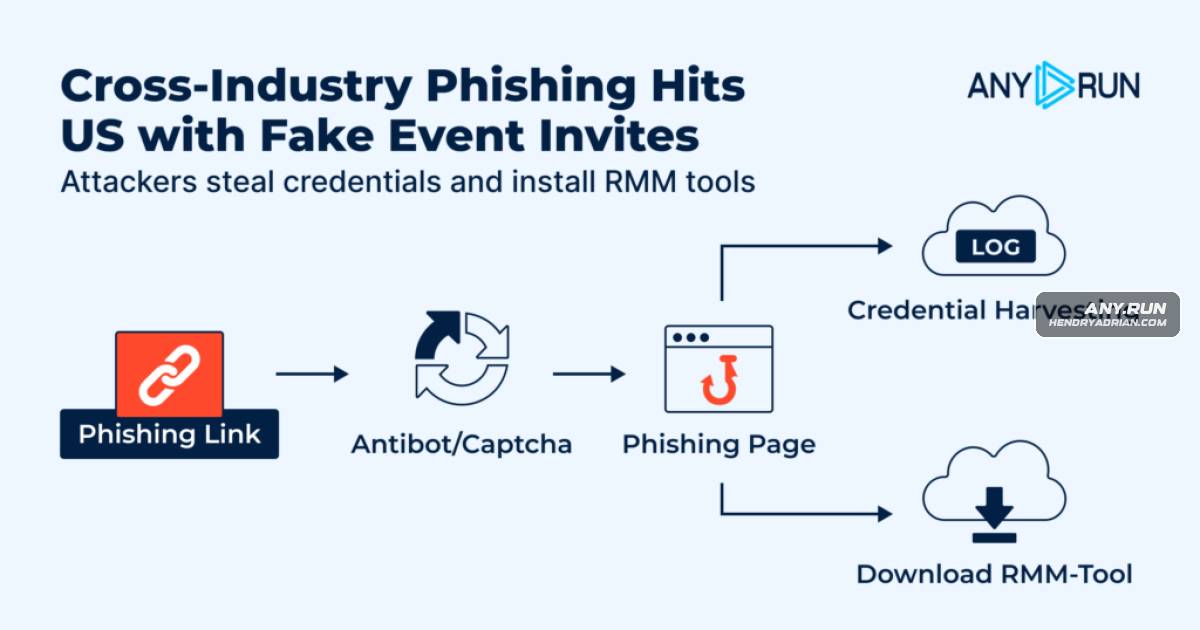
ANY.RUN researchers describe a fake-invitation phishing campaign targeting U.S. organizations. They report nearly 160 suspicious links and 80 domains, with pages that steal credentials and OTPs or deliver remote management tools.
Key points
- ANY.RUN researchers reported nearly 160 suspicious links and around 80 phishing domains associated with the campaign as of April 27, 2026.
- The lures use CAPTCHA checks and fake event invitations, then direct users to credential-harvesting pages or remote management tool downloads.
- Researchers observed pages collecting passwords and OTP codes through POST requests; some non-Google flows prompt users to enter their password a second time.
- The campaign reportedly delivers legitimate RMM tools, including ScreenConnect, ITarian, Datto RMM, ConnectWise, and LogMeIn Rescue.
- Shared indicators include /Image/*.png assets and a repeated request sequence involving /favicon.ico and /blocked.html. ANY.RUN says these patterns can help identify related activity.
- Example domains cited by the researchers include festiveparty[.]us, getceptionparty[.]de, and celebratieinvitiee[.]de.
Article Details
- Attack Vectors
- Fake event-invitation phishing pages, often preceded by a CAPTCHA check, lure victims to credential forms or RMM-tool downloads.
- Credential-theft pages collect email addresses, passwords, and OTP codes through submission forms; some prompt users to enter their password a second time.
- Some lure pages initiate remote management software downloads automatically or provide a download button.
- Defensive Notes
- Safely analyze suspicious links in an interactive sandbox and inspect page behavior, network requests, credential-submission endpoints, downloads, and execution.
- Hunt for related activity using the repeated request sequence involving /favicon.ico, /blocked.html, and /Image/*.png, along with recurring URL patterns.
- Assess whether credentials or OTP codes were exposed and whether remote access was established; use the findings to guide containment.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | celebratieinvitiee[.]de | Identified in the article as an event-themed phishing domain observed in analysis sessions for the campaign. |
| DOMAIN | festiveparty[.]us | Identified in the article as an event-themed phishing domain observed in analysis sessions for the campaign. |
| DOMAIN | getceptionparty[.]de | Identified in the article as an event-themed phishing domain observed in analysis sessions for the campaign. |
| SHA256 | 4c373bc25cb71dbb75e73b61dff25aa184be8d327053a97202a6b1a5919cab0d | SHA-256 of yahoo.png, an icon file listed as part of the repeated asset set on the campaign's phishing pages. |
| SHA256 | 6eaa0a448f1306bcf4159783eeafe5d37243bd8ca2728db7d90de1929241dd29 | SHA-256 of office.png, an icon file listed as part of the repeated asset set on the campaign's phishing pages. |
| SHA256 | 887bc414bdb32b83dcfccdd3c688e90d9a87a0033e3756a840f9bdd2d65c5c74 | SHA-256 of office360.png, an icon file listed as part of the repeated asset set on the campaign's phishing pages. |
| SHA256 | 8e94c18bbcad0644c4b04de4356fe37da9996fdf1c99bc984ba819862a9b1889 | SHA-256 of aol.png, an icon file listed as part of the repeated asset set on the campaign's phishing pages. |
| SHA256 | 9a53e032a6e3e79861d28568c3b6ffc97f4f3c1d3af65a703ec12966420503d9 | SHA-256 of email.png, an icon file listed as part of the repeated asset set on the campaign's phishing pages. |
| SHA256 | a838f99537d35e48e479a34086297f76db5d3363b0456f23d10d308f0d30ed82 | SHA-256 of google.png, an icon file listed as part of the repeated asset set on the campaign's phishing pages. |
MITRE ATT&CK
T1036 · MasqueradingPhishing pages imitate event invitations and, in the Google credential flow, disguise a page as a Google authorization form.T1056.003 · Web Portal CapturePhishing pages collect email addresses, passwords, and OTP codes through web forms and POST requests.T1105 · Ingress Tool TransferSome lure pages download remote management software to the victim's system, sometimes automatically.T1219 · Remote Access ToolsThe campaign delivers legitimate remote management software for attacker access to victim environments.T1566.002 · Spearphishing LinkThe campaign directs victims to fake event-invitation pages that lead to credential capture or RMM-tool delivery.
Vendors
Products
ConnectWise#ANYRUNDatto RMMSome pages steal email credentials and OTP codes, while others install legitimate remote management tools such as ScreenConnect, ITarian, Datto RMM, ConnectWise, and LogMeIn Rescue.Interactive SandboxDuring triage, analysts can open suspicious links safely inside a cloud-based, interactive sandbox and quickly confirm whether the page leads to a fake invitation, credential form, OTP prompt, or RMM download.ITarianSome pages steal email credentials and OTP codes, while others install legitimate remote management tools such as ScreenConnect, ITarian, Datto RMM, ConnectWise, and LogMeIn Rescue.LogMeIn RescueSome pages steal email credentials and OTP codes, while others install legitimate remote management tools such as ScreenConnect, ITarian, Datto RMM, ConnectWise, and LogMeIn Rescue.ScreenConnect#ANYRUNThreat Intelligence LookupAnalysts can use this pattern to find related phishing domains in ANY.RUN’s Threat Intelligence Lookup with the following query: url:”/blocked.html” AND url:”/favicon.ico” and url:”/Image/*.png”
Countries
Industries
Bankingorganizations and appears to affect Education, Banking, Government, Technology, and Healthcare sectors most heavily.Educationorganizations and appears to affect Education, Banking, Government, Technology, and Healthcare sectors most heavily.Governmentorganizations and appears to affect Education, Banking, Government, Technology, and Healthcare sectors most heavily.Healthcareorganizations and appears to affect Education, Banking, Government, Technology, and Healthcare sectors most heavily.Technologyorganizations and appears to affect Education, Banking, Government, Technology, and Healthcare sectors most heavily.