cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2479 articles

Threat Research · cloud.google.com

Google Details Chinese-Language Phishing Services Using OTP Interception and Wallet Fraud

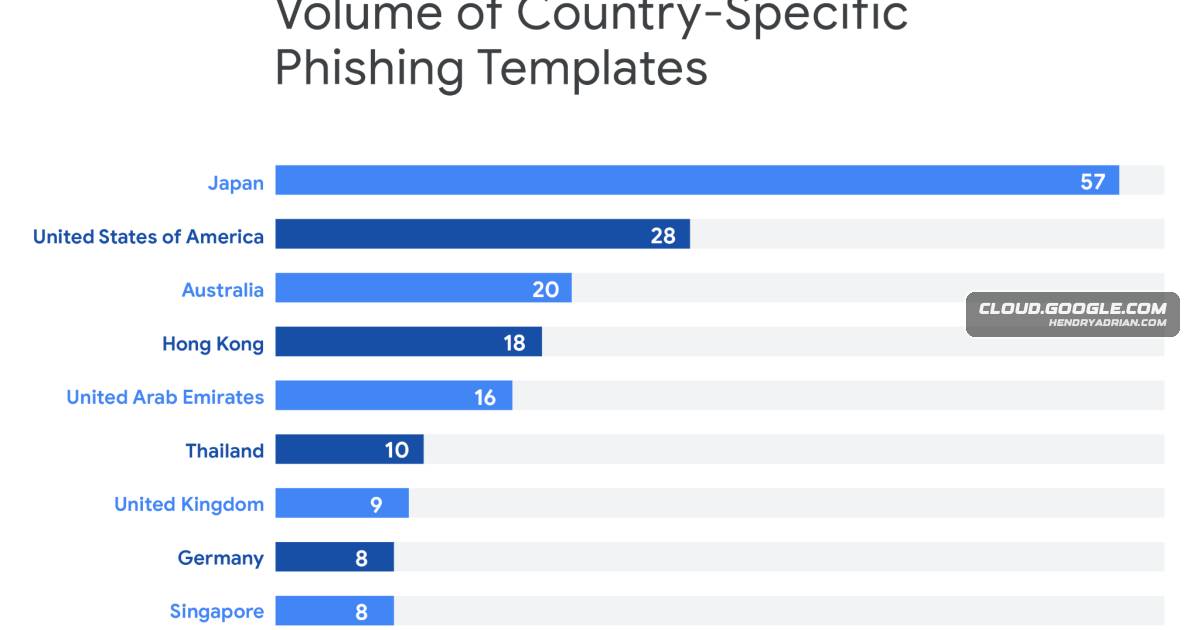
Google GTIG analyzed a mature Chinese-language PhaaS ecosystem using RCS and iMessage delivery, live OTP interception and digital-wallet provisioning to monetize stolen payment data. Darcula and YY Lai Yu illustrate AI-assisted, localized operations, including Japan.

May 25, 2026
Threat Research · socket.dev

TrapDoor Supply-Chain Campaign Targets npm, PyPI and Crates.io With Crypto Stealer

Socket researchers identified TrapDoor, a cross-registry campaign involving more than 34 malicious packages and 384+ versions and artifacts that steal developer credentials, crypto wallet data and other secrets.

May 24, 2026
Threat Research · darkreading.com

ESET Details Webworm’s Shift to European Government Targets and New C2 Backdoors

ESET reports that China-aligned Webworm has shifted toward European government targets and introduced EchoCreep, using Discord for C2, and GraphWorm, using Microsoft Graph and OneDrive. Its initial access vector remains unclear.

May 23, 2026
Threat Research · socket.dev

Malicious Laravel Lang Releases Deliver Cross-Platform Backdoor and Credential Stealer

A compromise of Laravel Lang packages introduced an automatically executed PHP backdoor and a cross-platform stealer targeting credentials and secrets. The article details the attack chain, affected packages, indicators, and recommended response.

May 23, 2026
Threat Research · socradar.io

SOCRadar Profiles CoinbaseCartel’s Credential-Theft and Data-Extortion Operations

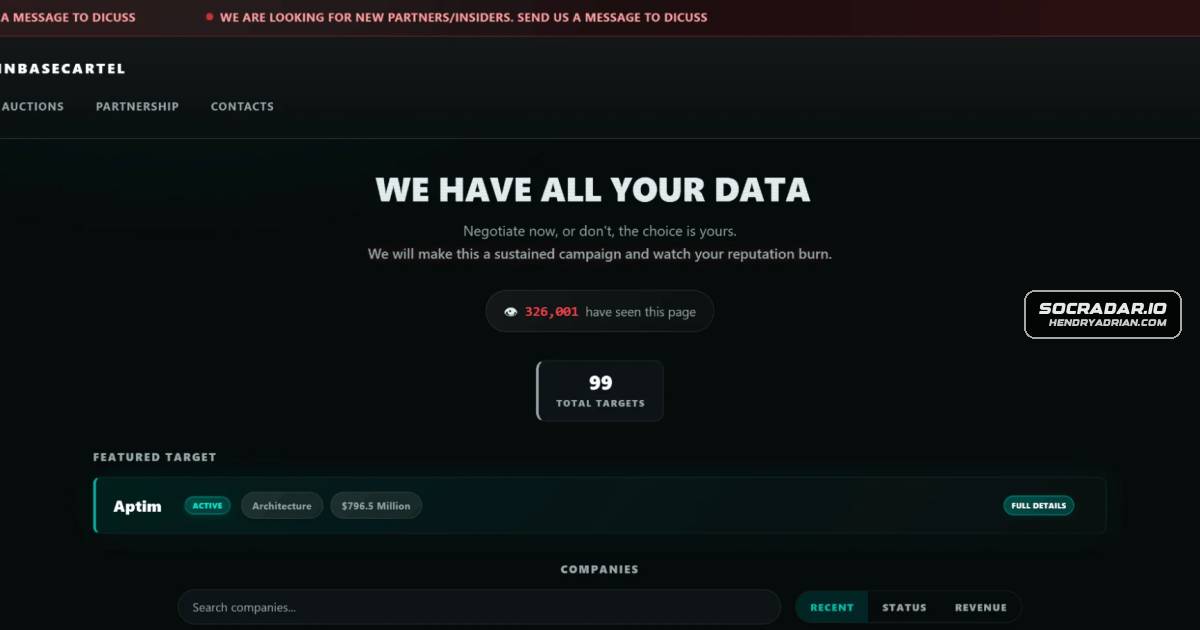
SOCRadar profiles CoinbaseCartel, an extortion actor reported to steal data using reused credentials and cloud access rather than encrypt systems. Researchers describe its tactics and defenses; proposed links to ShinyHunters, Scattered Spider and Lapsus$ remain ununfirm

May 22, 2026
Threat Research · levelblue.com

LevelBlue Details YellowKey BitLocker Bypass and Windows Privilege-Escalation Techniques

LevelBlue’s technical analysis explains how the YellowKey PoC abuses WinRE TxF replay to bypass BitLocker on TPM-only systems, and examines GreenPlasma and MiniPlasma privilege-escalation techniques, detection signals and Microsoft mitigation guidance.

May 22, 2026
Threat Research · thehackernews.com

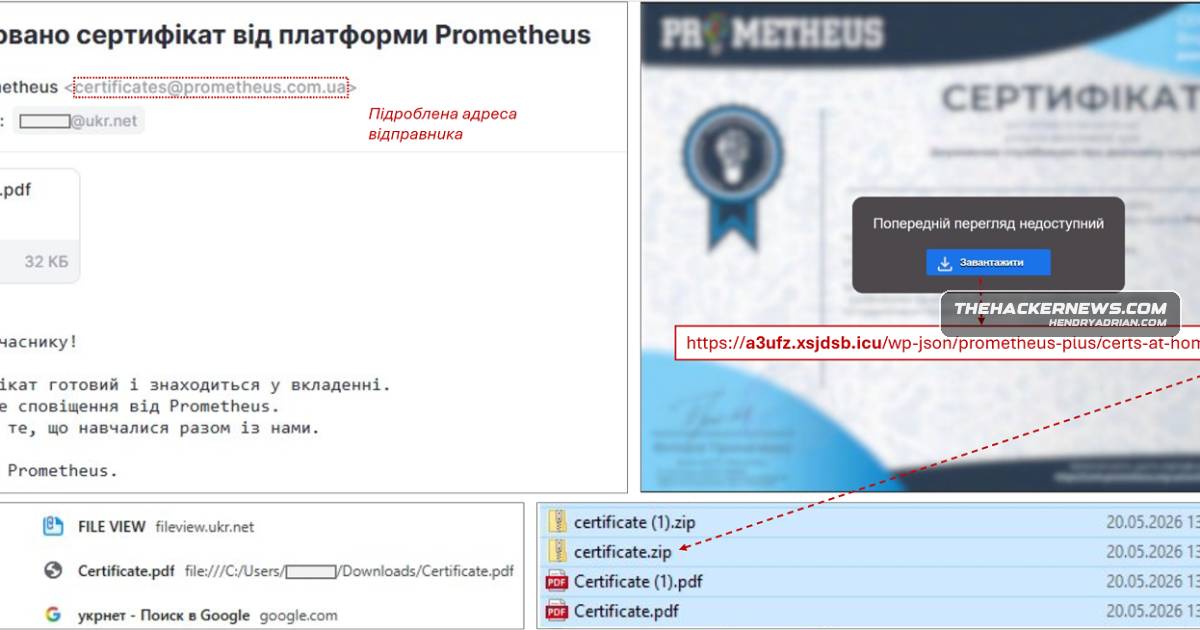
Ghostwriter Uses Prometheus-Themed Phishing to Target Ukrainian Government

CERT-UA reports that Ghostwriter has targeted Ukrainian government organizations since spring 2026 with phishing that deploys OYSTER malware and a final payload assessed to be Cobalt Strike. It advises restricting wscript.exe for standard users.

May 22, 2026
Threat Research · research.checkpoint.com

Nimbus Manticore Uses MiniFast in Campaigns Targeting Aviation and Software Organizations

Check Point says IRGC-affiliated Nimbus Manticore (UNC1549) used phishing, a trojanized Zoom installer and SEO-poisoned SQL Developer site to deliver MiniFast. Researchers detail its AppDomain hijacking, scheduled-task persistence and HTTP C2.

May 22, 2026
Threat Research · analyst1.com

Analyst1 Details DragonForce’s Shift to a Scalable Ransomware Cartel

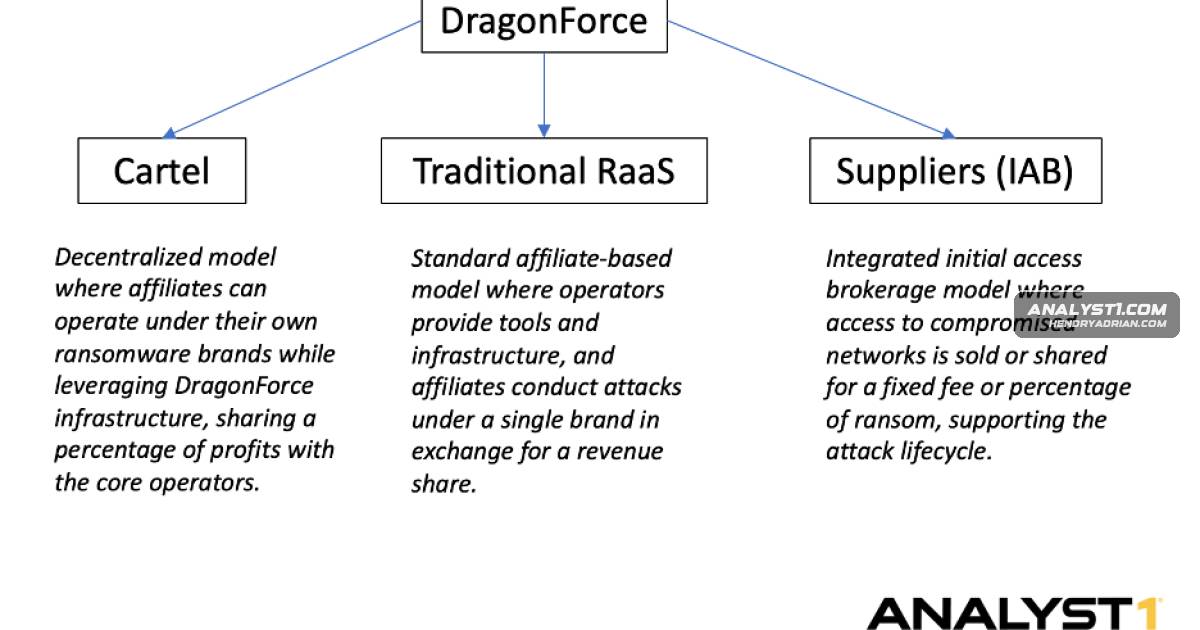
Analyst1 profiles DragonForce’s evolution from RaaS into a cartel-style platform combining affiliates, access brokers and shared services, with cross-platform ransomware, double extortion and an 80/20 payment model. It describes links with Qilin, LockBit and Scatteredsp

May 22, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details Screening Serpens’ MiniUpdate and MiniJunk V2 Espionage Campaigns

Unit 42 attributes 2026 espionage campaigns to Screening Serpens, detailing six MiniUpdate and MiniJunk V2 RAT variants, tailored lures, DLL sideloading and AppDomainManager hijacking that disables .NET security telemetry.

May 22, 2026
Threat Research · thehackernews.com

Research Shows How Some Hardware-Gated Windows Drivers Can Be Reached Without Hardware

The analysis shows how emulated devices, spoofed hardware IDs, filter restacking and forced binding can expose some Windows PnP driver code without its intended hardware, potentially expanding BYOVD risk. Generic hardware-probe bypasses may still require kernel or hyper

May 22, 2026
Threat Research · securelist.com

Cloud Atlas Adds Backdoors and Covert Access Tools in Russia and Belarus Campaigns

Kaspersky attributes campaigns targeting organizations in Russia and Belarus to Cloud Atlas with high confidence. Its investigation details phishing and malware chains, credential theft, and backup access through SSH tunnels, RevSocks, and Tor.

May 22, 2026
Threat Research · netspi.com

NetSPI Finds UEFI PNG Decoder Buffer Over-Read via Spoofed IDAT Length

NetSPI used Qiling to emulate a UEFI PNG decoder and observed an out-of-bounds read when a PNG’s IDAT length was spoofed. The flaw could expose boot-time memory, but actual sensitive-data leakage was not demonstrated.

May 22, 2026
Threat Research · stepsecurity.io

Step Security Details Megalodon’s GitHub Actions Secret-Exfiltration Campaign

Step Security reports that Megalodon injected malicious workflows into 5,561 GitHub repositories; payloads harvested CI, cloud and source-code secrets and sent them to a listed C2 IP. Tiledesk repositories and npm packages were among those affected.

May 22, 2026
Threat Research · stepsecurity.io

Laravel-Lang Composer Packages Hit by Tag-Rewriting Supply-Chain Attack

Step Security reports four Laravel-Lang Composer packages had all Git tags rewritten to point to malicious commits. A detonation of one package confirmed payload execution and an outbound exfiltration request to flipboxstudio[.]info; three others were not tested.

May 22, 2026
Threat Research · trendmicro.com

Void Dokkaebi Uses Cython-Compiled InvisibleFerret to Evade Script-Based Detection

Void Dokkaebi has shifted InvisibleFerret to Cython-compiled Windows and macOS modules, complicating script-based detection. The malware retains credential- and wallet-stealing capabilities, while binary artifacts and runtime scripts can aid analysis.

May 22, 2026
Threat Research · thehackernews.com

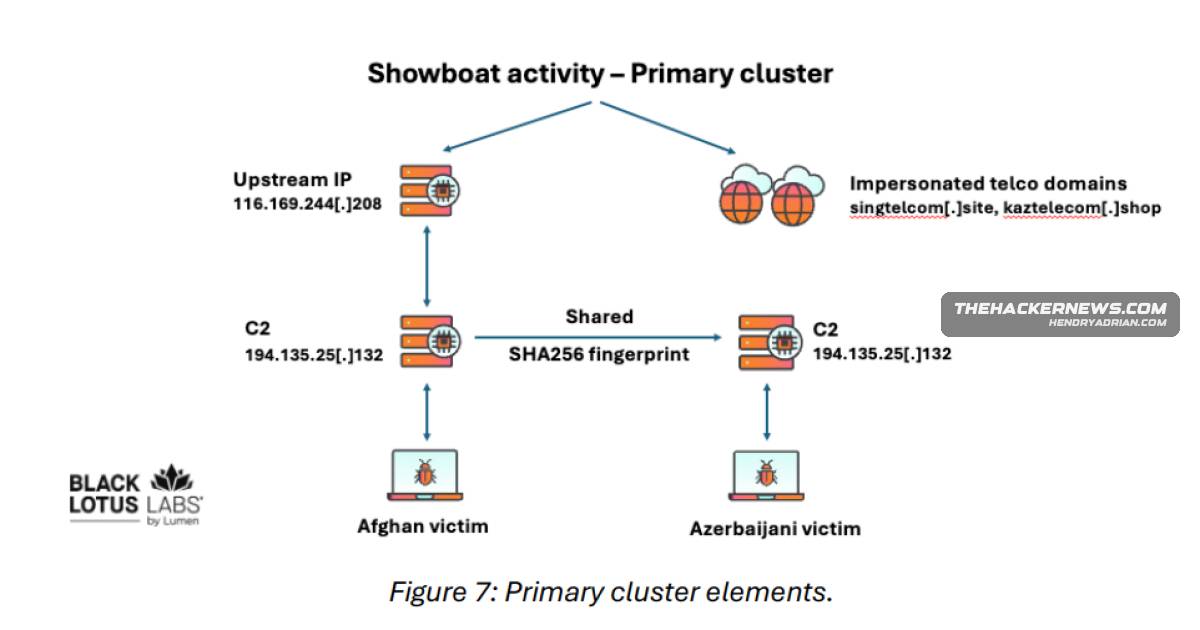
Researchers Link Showboat Linux Malware to Middle East Telecom Campaign

Researchers link the Showboat Linux post-exploitation framework, used since at least mid-2022, to attacks on a Middle East telecom provider and other possible victims. It supports remote shell, file transfer and SOCKS5 proxy functions.

May 21, 2026
Threat Research · blog.eclecticiq.com

SEO-Poisoned Fake Developer Tool Pages Deliver Fileless PowerShell Infostealer

EclecticIQ details an ongoing campaign using SEO-poisoned fake developer-tool pages to deliver a fileless PowerShell infostealer that steals credentials, tokens, cookies and files, then exfiltrates data and can run follow-on payloads.

May 21, 2026
Threat Research · bleepingcomputer.com

Researchers Detail Calypso-Linked Telecom Espionage Campaign Using Showboat and JFMBackdoor

Lumen and PwC researchers describe a Calypso-attributed campaign targeting telecom providers in Asia Pacific and the Middle East since at least mid-2022, using Linux Showboat and Windows JFMBackdoor implants. The initial infection vector is unknown.

May 21, 2026
Threat Research · bleepingcomputer.com

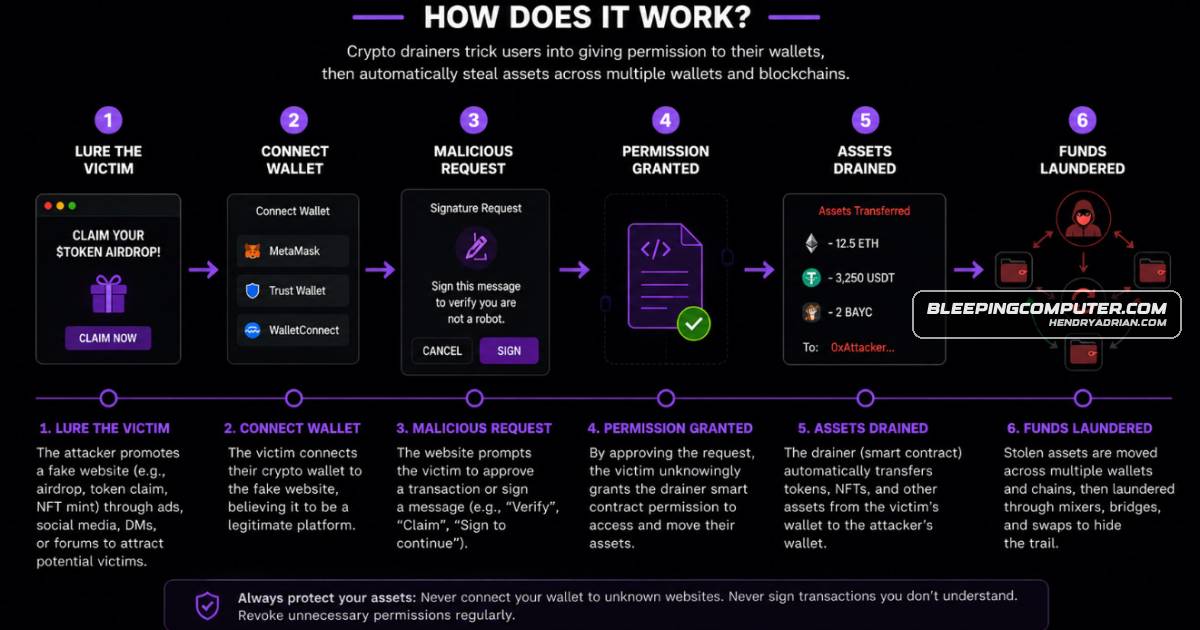
Flare Analysis Details Lucifer Crypto Drainer’s Affiliate Model and Tactics

Flare analyzed about 700 underground posts to document how Lucifer DaaS uses affiliates, wallet approvals, website cloning, and automated deployment. The article also lists warning signs of malicious wallet requests.

May 21, 2026
Threat Research · gendigital.com

JDownloader Supply-Chain Attack Delivered r77 Rootkit and Python Bot

A Gen Digital analysis details trojanized JDownloader installers delivered through compromised download links on May 6–7, 2026. The payload included an r77 rootkit, a Python bot and a WDAC policy that blocked security tools.

May 21, 2026
Threat Research · zimperium.com

zLabs Details Android Carrier-Billing Fraud Campaign Using Nearly 250 Apps

zLabs reports that nearly 250 Android apps targeted users in four countries for carrier-billing and premium SMS fraud. Its analysis describes three malware variants using WebViews, OTP interception, cookie theft and Telegram reporting.

May 21, 2026
Threat Research · welivesecurity.com

ESET Details Webworm’s New Discord and Microsoft Graph Backdoors

ESET researchers describe Webworm’s 2025 shift toward European targets, detail its EchoCreep and GraphWorm backdoors and custom proxy tools, and report GitHub staging plus a compromised S3 bucket used for configuration retrieval and data exfiltration.

May 21, 2026
Threat Research · huntress.com

Huntress Details Defense Evasion Tactics in Two Gentlemen Ransomware Incidents

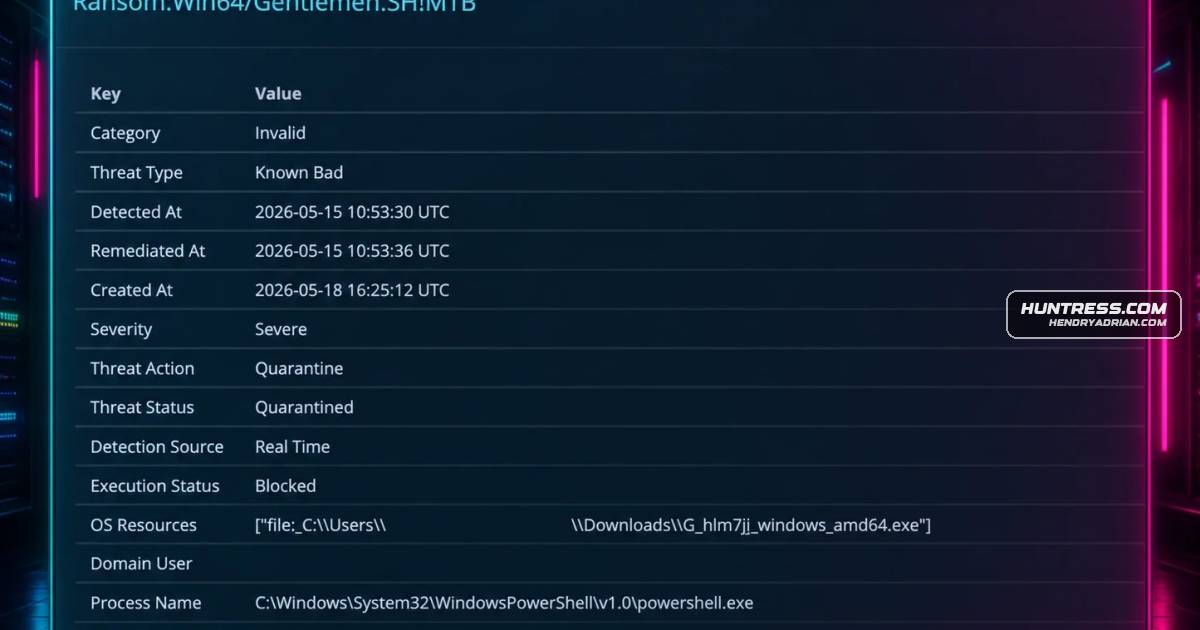
Huntress analyzed two Gentlemen ransomware incidents involving scheduled tasks, PowerShell, Windows log clearing, and attempts to disable Microsoft Defender. One incident included a SOCKS proxy connecting to attacker-controlled IP addresses.

May 21, 2026
PreviousPage 59 of 104 Next
© 2026 cyber.hendryadrian.com