cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2393 articles

Threat Research · bleepingcomputer.com

ESET Details GentleKiller Tools Used by Gentlemen Ransomware to Disable EDR

ESET says the Gentlemen ransomware group uses GentleKiller and other tools to disable EDR defenses. Its analysis describes BYOVD-based privilege escalation, targeting of more than 400 processes, and multiple tool variants.
Jun 19, 2026
Threat Research · varonis.com

Varonis MySQL Honeypots Show Exposed Cloud Database Ransomed Within Hours

Varonis Threat Labs found that attackers brute-forced an intentionally exposed Google Cloud SQL honeypot, extracted decoy data and left ransom notes. Similar AWS RDS and Azure MySQL honeypots were not compromised.

Jun 19, 2026
Threat Research · cloudsek.com

FortiBleed Analysis Finds 148 Confirmed Compromises in Credential Campaign

Analysis of an exposed attacker directory traces a campaign targeting exposed Fortinet devices. Researchers say 21,632 entries did not represent verified breaches; their review found evidence of internal traffic at 918 organisations and 148 confirmed compromises.

Jun 19, 2026
Threat Research · proofpoint.com

Operation Endgame Disrupts TA569’s SocGholish Infrastructure, Remediates 14,971 Websites

Authorities took down more than 100 servers and domains and remediated 14,971 websites in an operation targeting TA569. Proofpoint details SocGholish’s fake-update and GhoLoader chain and recommends layered defenses and WordPress hardening.

Jun 18, 2026
Threat Research · malwarebytes.com

Fake GitHub EQVita Project Targets Vita Fans With Windows Malware

A fake EQVita homebrew project lures PlayStation Vita fans into running Windows files, including a disguised Lua script that checks location and contacts attacker infrastructure. Similar fake repositories have distributed SmartLoader and Lumma Stealer.

Jun 18, 2026
Threat Research · bleepingcomputer.com

USB Worm Uses Windows Shortcuts to Spread Cryptocurrency-Stealing Malware

Microsoft reports a campaign active since at least February that uses malicious USB shortcut files and Tor to spread malware, steal cryptocurrency wallet data, capture screenshots, and execute downloaded JavaScript.

Jun 18, 2026
Threat Research · asec.ahnlab.com

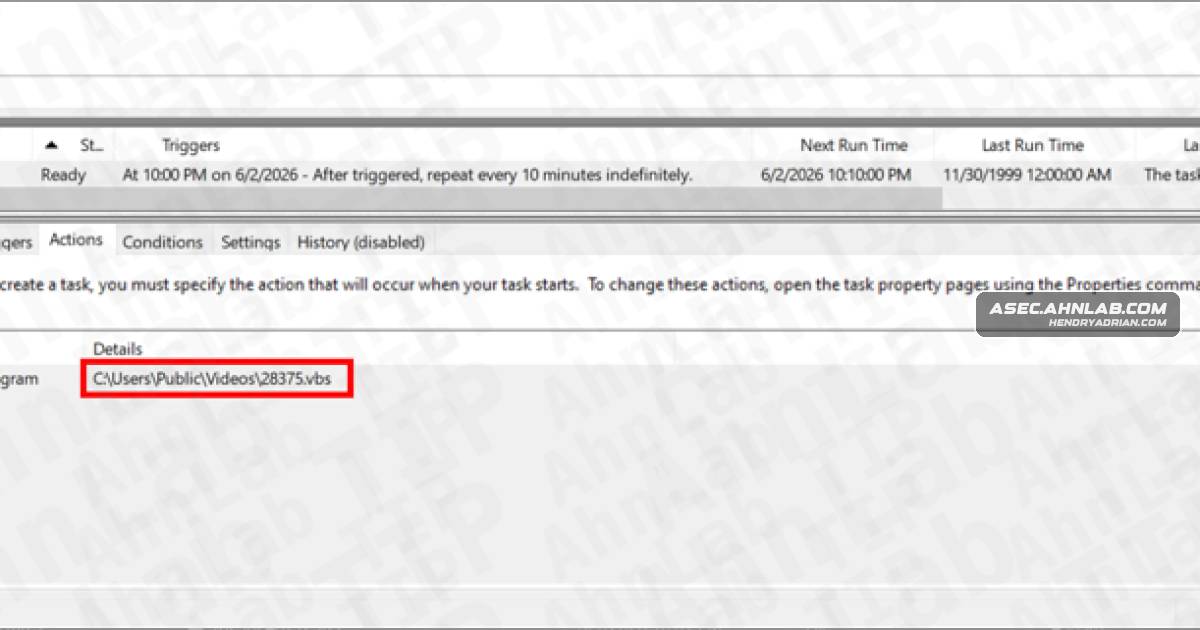
Resume-themed LNK files deliver Xctdoor through DLL side-loading

AhnLab analyzed resume-disguised LNK files that launch decoy documents while creating scripts, scheduling persistence, and downloading payloads. DLL side-loading then loads Xctdoor, which attempts to contact an external C2 server.

Jun 18, 2026
Threat Research · sysdig.com

Sysdig Finds Exposed Ollama Server Powering an Autonomous Offensive Tool

Sysdig researchers observed an actor using an exposed, unauthenticated Ollama server as inference capacity for VAPT, an evolving offensive framework. Its observed targets were private practice ranges; no public victim systems were targeted.

Jun 18, 2026
Threat Research · opensourcemalware.com

Mastra npm compromise planted malware in 140+ packages to steal browser data

A compromised Mastra npm maintainer account was used to inject a malicious dependency into more than 140 packages. The malware installs a cross-platform backdoor that steals browser data and can run attacker-supplied code; attribution remains unconfirmed.

Jun 18, 2026
Threat Research · rapid7.com

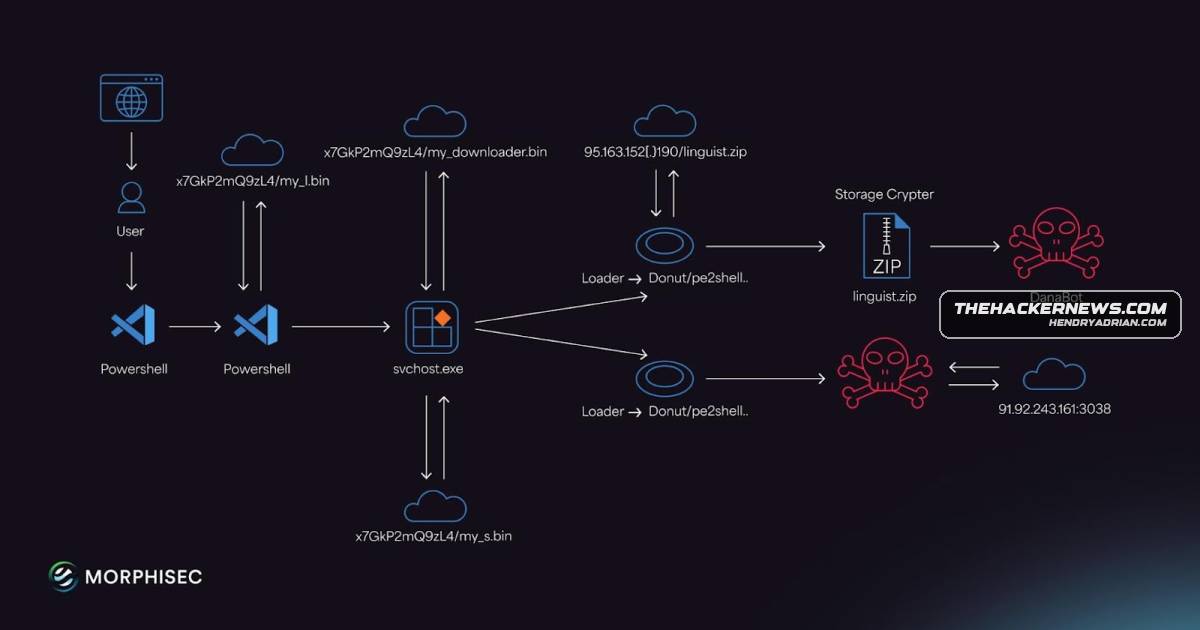
Rapid7 Links Dropping Elephant to In-Memory RAT Delivered via China-Themed Lure

Rapid7 analyzed a Dropping Elephant campaign that used a China-themed lure, DLL side-loading and Donut shellcode to run an evasive RAT in memory. The report details its tradecraft, C2 behavior and behavior-based detection opportunities.

Jun 18, 2026
Threat Research · stepsecurity.io

15 Malicious JetBrains Plugins Targeted AI API Keys Across About 70,000 Installs

StepSecurity reports that 15 JetBrains Marketplace plugins with about 70,000 installs captured AI API keys and sent them over plaintext HTTP to a hardcoded C2. JetBrains removed the plugins; StepSecurity found the server still responding on June 19, 2026.

Jun 18, 2026
Threat Research · securitylabs.datadoghq.com

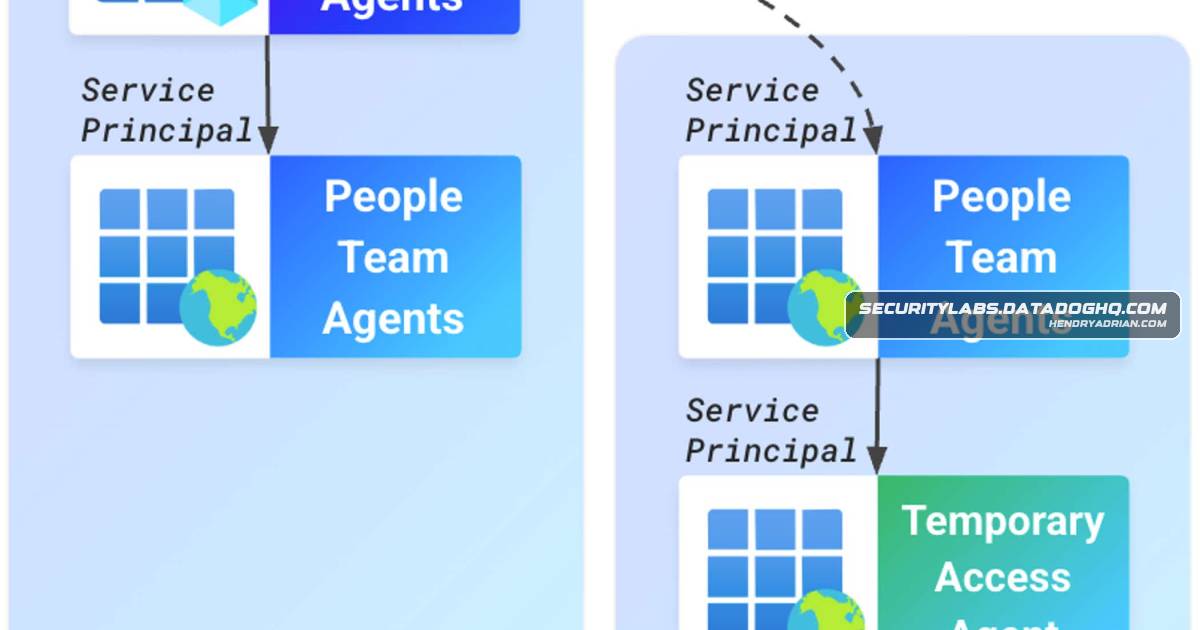
Datadog Demonstrates Cross-Tenant Entra Takeover Through Compromised Agent Blueprint

Datadog demonstrates how an attacker controlling an Entra agent blueprint could add a credential, impersonate associated agents across tenants, and use a privileged agent’s permissions to take over a Global Administrator account.

Jun 18, 2026
Threat Research · zscaler.com

SmartApeSG Compromises Okendo Reviews Widget to Deliver ClickFix Lures

ThreatLabz found SmartApeSG JavaScript injected into the Okendo Reviews widget. The obfuscated, staged loader targeted desktop visitors and could lead to ClickFix prompts and malware delivery. Okendo restored the script to a clean state.

Jun 18, 2026
Threat Research · trendmicro.com

PeopleSoft PeopleTools RCE Exploited Through PSIGW SSRF and XMLDecoder Chain

Trend Micro details in-the-wild exploitation of CVE-2026-35273 in PeopleTools 8.61 and 8.62. The chain uses PSIGW SSRF and XMLDecoder for in-JVM RCE; Oracle released an out-of-band patch on June 10, 2026.

Jun 18, 2026
Threat Research · welivesecurity.com

ESET Details Gentlemen Ransomware Gang’s EDR-Killer Toolkit

ESET researchers detail how the Gentlemen ransomware group maintains and supplies affiliates with a standardized suite of EDR killers, including its in-house GentleKiller framework and externally sourced tools.

Jun 18, 2026
Threat Research · levelblue.com

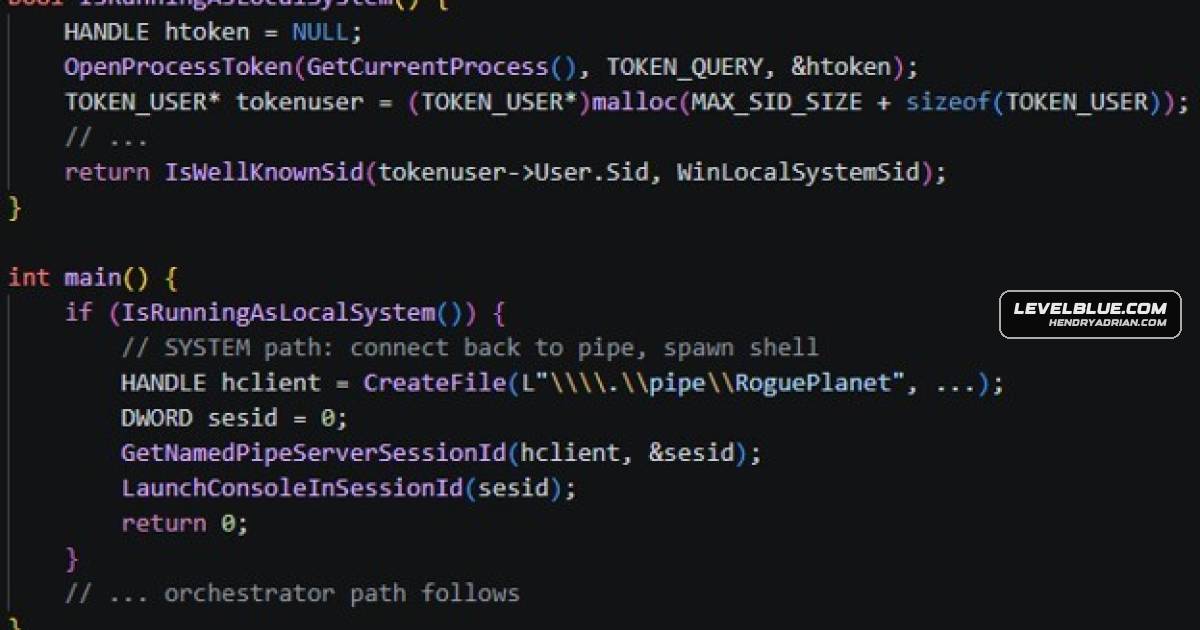
RoguePlanet and GreatXML Abuse Windows Defender and WinRE Security Boundaries

LevelBlue SpiderLabs details RoguePlanet’s Windows Defender workflow abuse to gain SYSTEM execution and GreatXML’s WinRE recovery-partition tampering to access BitLocker-protected data, with technical mechanisms and detection guidance.

Jun 17, 2026
Threat Research · asec.ahnlab.com

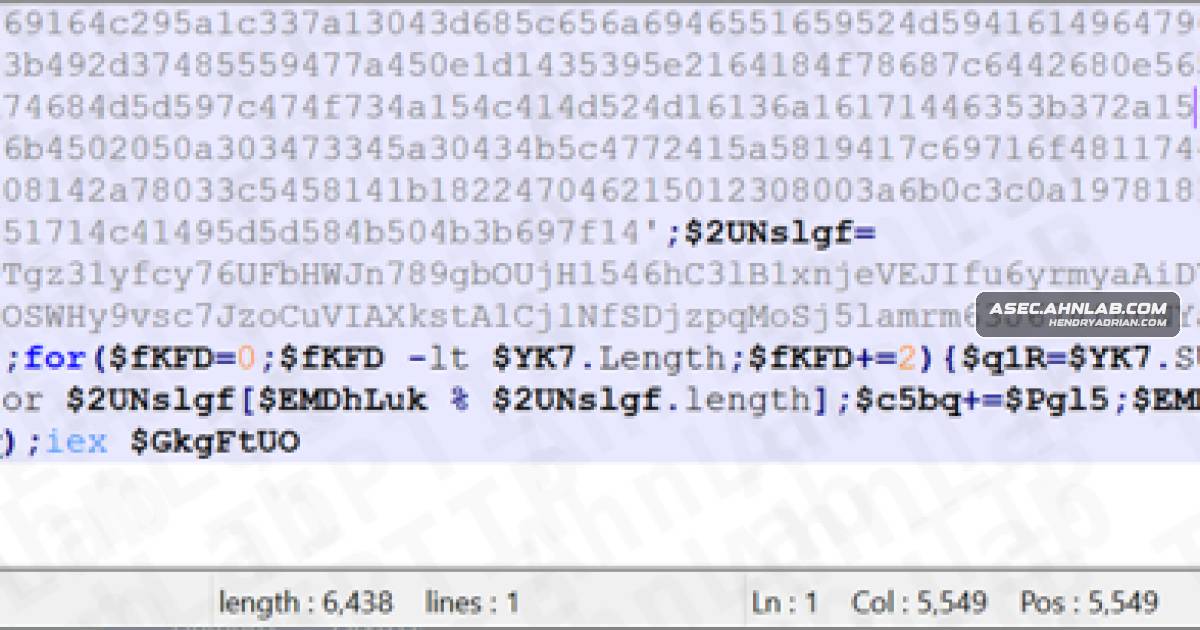
AhnLab Details Malicious Consent-Form LNKs in Activity Resembling Kimsuky

AhnLab details malicious consent-form LNK files that launch obfuscated PowerShell, run downloaded payloads in memory, establish scheduled-task persistence and collect system data. The activity resembles prior Kimsuky operations.

Jun 17, 2026
Threat Research · thehackernews.com

Poisson Used OpenSSH and Tailscale to Retain Access After Havoc C2 Went Offline

Cato Networks reconstructed an intrusion attributed to Poisson, who used OpenSSH and Tailscale to retain access to a French automotive business after its Havoc C2 went offline. The investigation also describes keylogging and persistence methods.

Jun 17, 2026
Threat Research · netskope.com

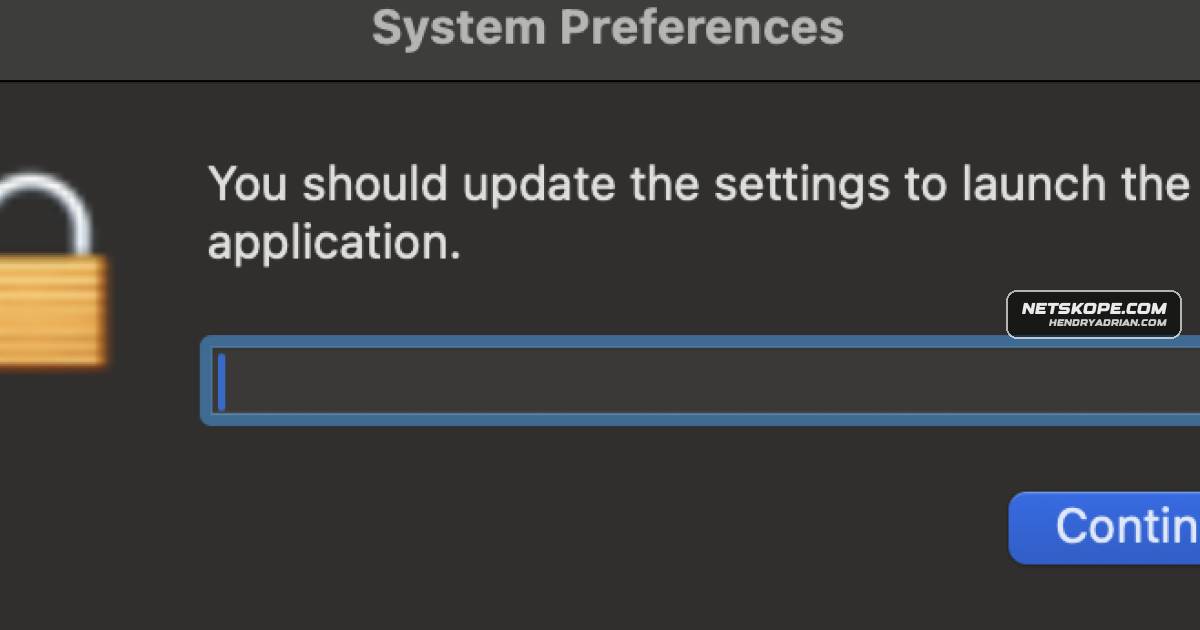
macOS ClickFix Campaign Deploys AppleScript Stealer and Persistent RAT

Netskope describes a macOS ClickFix campaign using fileless AppleScript to steal credentials and data, tamper with cryptocurrency wallets, and install persistent remote access through a fake Apple system service.

Jun 17, 2026
Threat Research · wiz.io

Red Agent Chains SSRF and URL-Validation Bypass to Read GCP Cloud Run Files

Wiz describes how its Red Agent bypassed a GitHub URL validator in a GCP Cloud Run service to read local files, exposing service-account credentials and application source code.

Jun 17, 2026
Threat Research · research.checkpoint.com

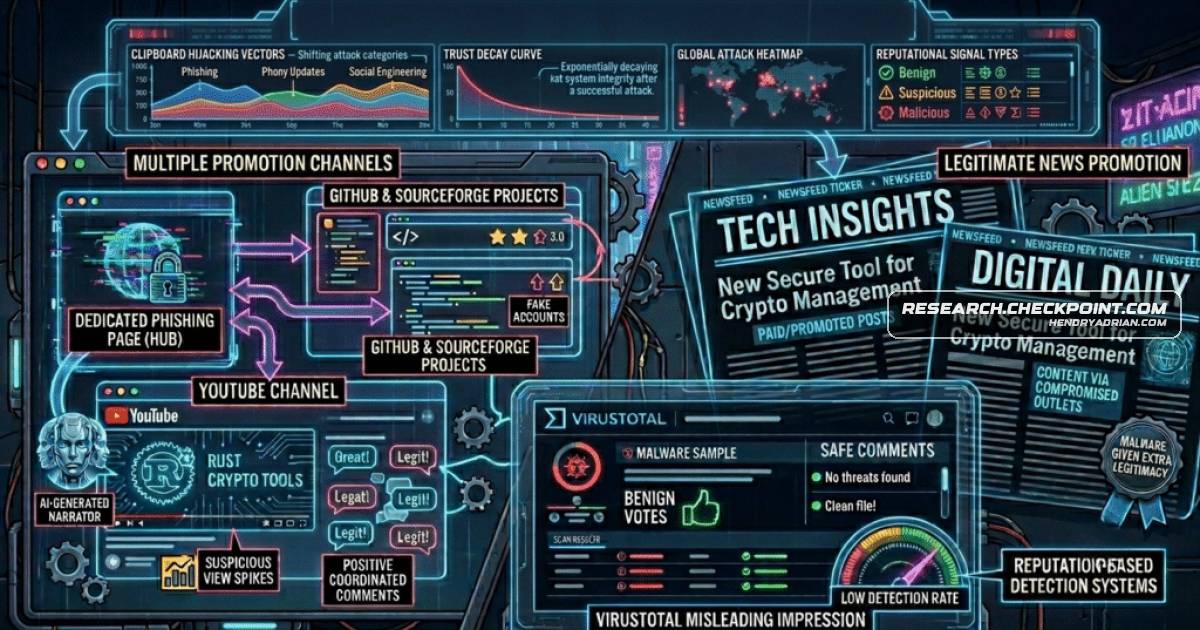
Rust Clipboard Hijacker Targets Windows and macOS Using Fake Reputation to Lure Crypto Users

Check Point researchers detail a campaign distributing Rust clipboard hijackers for Windows and macOS through fake crypto tools. The malware replaces copied wallet addresses, while manipulated engagement across platforms helps make downloads appear trustworthy.

Jun 17, 2026
Threat Research · socket.dev

Malicious Dependency Compromises 141 Mastra npm Packages in Supply-Chain Campaign

A malicious dependency added to 141 Mastra npm packages ran an install-time loader that deployed a cross-platform implant. Socket says the payload collected browser history and wallet-extension inventories, installed persistence, and enabled further remote tasking.

Jun 17, 2026
Threat Research · thehackernews.com

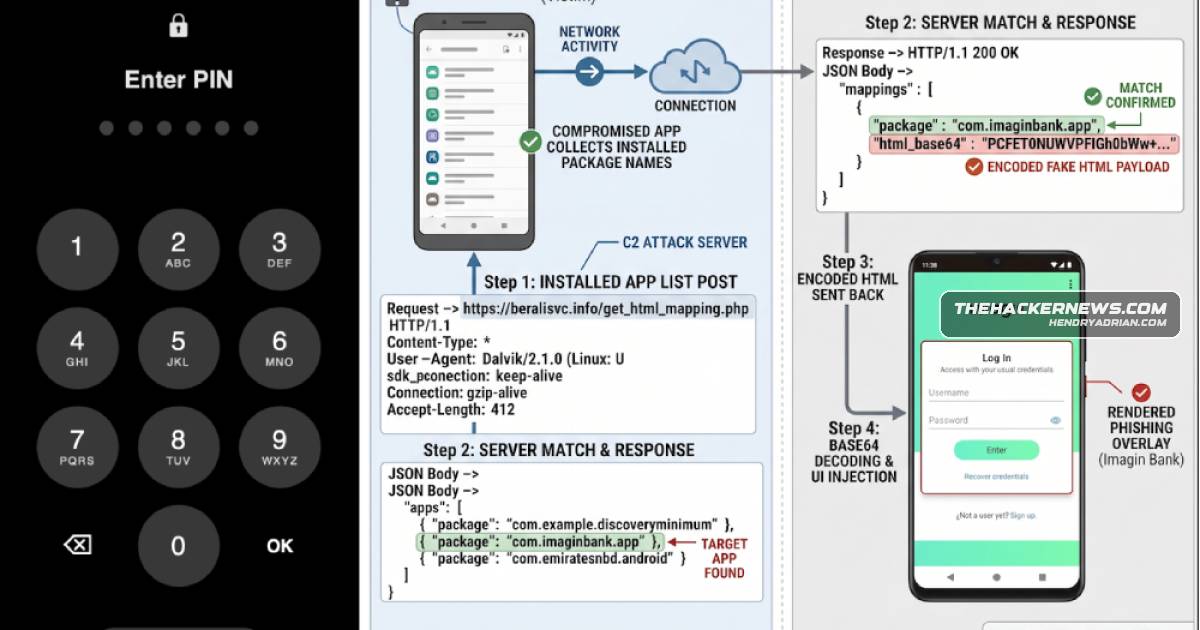
Rokarolla Android Banking Trojan Targets 217 Apps and Steals Credentials

Zimperium’s zLabs describes Rokarolla, an Android banking trojan that targets 217 banking and crypto apps. Fake-app droppers and Accessibility abuse enable credential and PIN theft, SMS interception, clipboard manipulation, and covert screenshots.

Jun 17, 2026
Threat Research · thehackernews.com

ClickFix Campaigns Deploy BabaDeda, Lorem Ipsum and Potemkin Loaders

Researchers detail three ClickFix campaigns using BabaDeda, Lorem Ipsum and Potemkin loaders to deliver stealers, RATs and backdoors through fake update lures, compromised sites, staged payloads and techniques including DLL side-loading and DGA-based C2.

Jun 17, 2026
PreviousPage 51 of 100 Next
© 2026 cyber.hendryadrian.com