Rust Clipboard Hijacker Targets Windows and macOS Using Fake Reputation to Lure Crypto Users
Summary
Check Point researchers detail a campaign distributing Rust clipboard hijackers for Windows and macOS through fake crypto tools. The malware replaces copied wallet addresses, while manipulated engagement across platforms helps make downloads appear trustworthy.
Key points
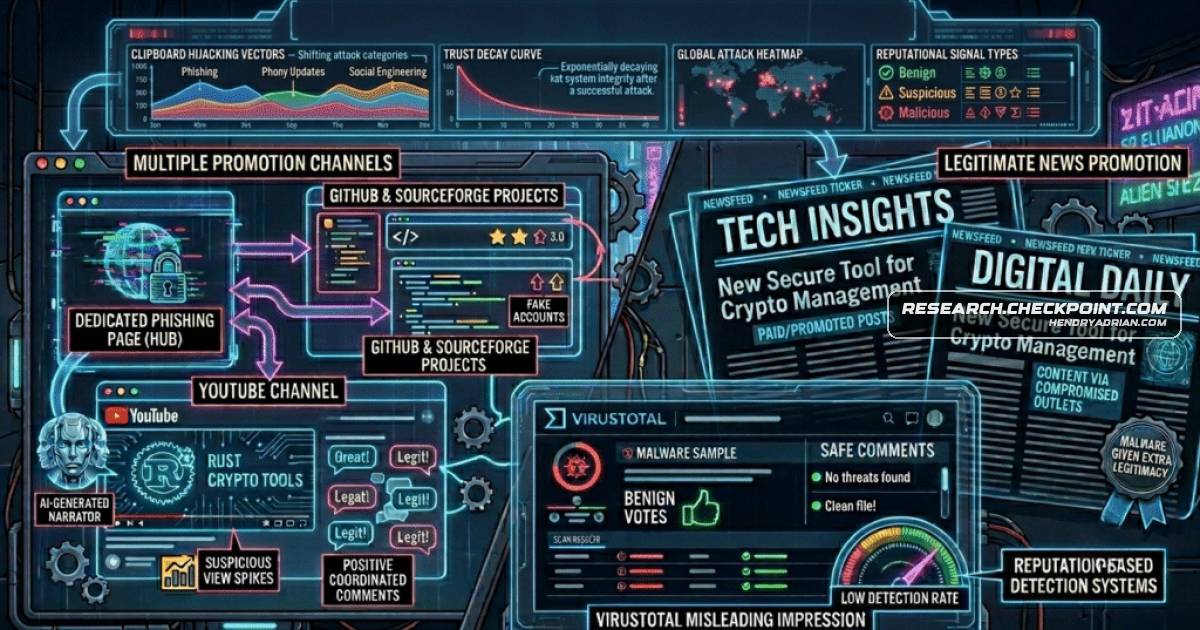
- A phishing site promotes fake crypto-trading and gambling tools, distributing malware through GitHub, SourceForge, and other channels.
- The Rust malware monitors clipboard text for cryptocurrency wallet addresses and replaces matches with attacker-controlled addresses.
- The Windows variant persists through a Startup-folder shortcut and embeds more than 15,500 wallet addresses.
- The macOS variant uses instructions to remove quarantine attributes and bypass Gatekeeper warnings, then persists through a LaunchAgent and watchdog.
- The actor allegedly inflated stars, downloads, views, comments, and VirusTotal benign votes to make the tools and samples seem legitimate.
- Researchers observed more than 5,000 GitHub downloads; SourceForge showed 44,485 downloads, many anomalously attributed to Android devices.
Article Details
- Attack Vectors
- Social engineering promotes malicious Windows and macOS downloads through a phishing site, GitHub and SourceForge projects, YouTube videos, forum posts, and posts on news-oriented websites.
- The downloaded applications act as loaders that execute Rust clipboard hijackers. The malware monitors clipboard contents for cryptocurrency wallet addresses and replaces matching text with attacker-controlled wallet addresses.
- On Windows, the malware copies itself to %APPDATA%\silke\silke.exe and creates a shortcut in the Startup folder for persistence.
- On macOS, an instructed shell script removes an application's quarantine attribute and opens it. The malware installs a LaunchAgent and a shell-script wrapper for persistence; a watchdog loop recreates these files and relaunches the binary.
- Defensive Notes
- The article reports coordinated fake engagement and benign votes or comments on VirusTotal, which can create a misleading impression of safety when detection rates are also low.
- The macOS instructions encourage users to bypass Gatekeeper warnings by removing quarantine attributes before opening the application.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 33c86ecfc324de3af97150bd009aba7925a6ba7a0842e127e94cf351013c0fe6 | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | 5518942d9d21794aaeff41a01b88606a96659fc329b481a2f0946d8163ab4d61 | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | 6f12c066a929c96104796c4ecca938754962009ebd9e4ba5329bb940bf331d0a | Hash listed as a macOS loader. |
| SHA256 | 7a7ad4ae347a3f99f3773a113d9f70ecfa967100c96e8275bd1df833caee68d1 | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | 7a9632bbecc31d02fdd0eab07e2424b3e1c9e9a3f91aac4ef6f708f2befbaa3d | Hash listed as a .NET loader. |
| SHA256 | 9c566db1ef9d08ee389d2b8cc1c50c65870096130c8bd2cf41ea14c4075e94c0 | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | a91c09e0eea610dbe5879798f9cf12e3ce51e4e6f0893278bcdf3ebe22c4730b | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | b71efdebd0ca3563e67edb7ad59358a6b8f013b219ad65033efcf48fd1c86619 | Hash listed as macOS clipboard hijacking malware. |
| SHA256 | bad8625087a7b9453c70933c0db32518ff5818e3d83f3a9e78d432a22b383edb | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | c1435847b0c437f91efb07a3a35e4468036322d7acf4ba9e6d363cec0b481241 | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | e02e60a23297692637b43ebcd7dbeb63af1e9680c551586a1ce935218e0034be | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | ef9a915c8e1d484e52b3287c94a58ecd22c07391a87f9c136eabd8397ed01ca2 | Hash listed as a clipboard hijacking malware sample. |
| SHA256 | f737e99177cc05037ff34cf6e245dd56377dc3db4e2bb46edcf039df650939d6 | Hash listed as a .NET loader. |
| SHA256 | fb8294b12f904dff2ac79b51872be7bf09ab422cde223caaf4762eadf7e0760d | Hash listed as a clipboard hijacking malware sample. |
MITRE ATT&CK
T1115 · Clipboard DataThe clipboard hijackers monitor clipboard contents for cryptocurrency wallet addresses before replacing matching text.T1204.002 · Malicious FileVictims are instructed to open the downloaded Windows or macOS software, which loads the malicious executable.T1543.001 · Launch AgentThe macOS malware installs a LaunchAgent configured to run at login and restart if it exits.T1547.001 · Registry Run Keys / Startup FolderThe Windows malware creates a shortcut in the Startup folder so it runs at logon.
Threat Actors
Products
GitHuba Rust clipboard hijacker, starting with a dedicated phishing page as the central hub and extending to GitHub and SourceForge projects promoted by fake accounts.macOSBehind this social‑engineering and promotion layer, the actual payloads delivered to victims are Rust‑based clipboard hijackers for both Windows and macOS.Microsoft WindowsBehind this social‑engineering and promotion layer, the actual payloads delivered to victims are Rust‑based clipboard hijackers for both Windows and macOS.SourceForgehijacker, starting with a dedicated phishing page as the central hub and extending to GitHub and SourceForge projects promoted by fake accounts.VirusTotalThe same illusion mechanism extends to VirusTotal, where some samples from this campaign receive benign votes and “safe” comments.WordPressA WordPress phishing site serves as the main landing page, while GitHub and SourceForge projects are used to host and distribute the files.YouTubeA dedicated YouTube channel, using AI‑generated narrators, suspicious view spikes, and highly positive (likely coordinated) comments, further reinforces the illusion of popularity and trustworthiness.
Countries
IndiaAlthough we see relatively few comments or reviews, the download statistics seem highly manipulated, with a total of 44,485 downloads, the majority of which appear to originate from Pakistan and India.PakistanAlthough we see relatively few comments or reviews, the download statistics seem highly manipulated, with a total of 44,485 downloads, the majority of which appear to originate from Pakistan and India.