
Fake GitHub EQVita Project Targets Vita Fans With Windows Malware
Summary
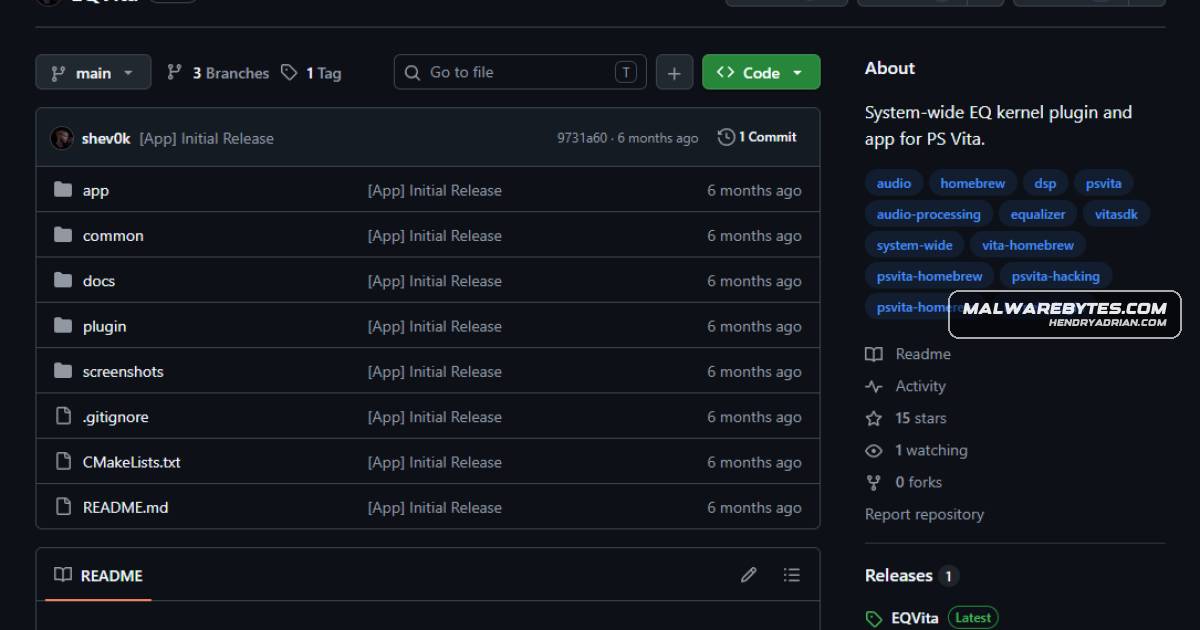
A fake EQVita homebrew project lures PlayStation Vita fans into running Windows files, including a disguised Lua script that checks location and contacts attacker infrastructure. Similar fake repositories have distributed SmartLoader and Lumma Stealer.
Key points
- The fake EQVita download is presented as a Vita audio tool but contains Windows files: Launch.bat, luajit.exe, and a disguised script named x64.txt.
- Launch.bat runs x64.txt through LuaJIT; despite its .txt extension, the file contains a hidden script.
- The script checks the computer’s location and contacts an attacker-controlled server; the article lists 85.137.52.21 as a C2 IP.
- The article says similar fake GitHub repositories have been used to distribute SmartLoader and, subsequently, Lumma Stealer; it does not establish that EQVita delivered those specific payloads.
- Users are advised to verify projects through trusted community sources and inspect downloads before running them.
- People who ran the archive are advised to scan the computer, change important passwords from a clean device, and review account and 2FA activity.
Article Details
- Attack Vectors
- A fake GitHub homebrew project called EQVita impersonates a PlayStation Vita audio tool to lure users into downloading and running a Windows archive.
- The archive contains Launch.bat, luajit.exe, and x64.txt; the batch file launches a hidden script disguised with a .txt extension through LuaJIT.
- When run, the script checks the computer’s location and contacts a server controlled by the attackers; the server can provide instructions and additional malware.
- The article says attackers have used similar fake repositories to distribute SmartLoader, which can then deliver Lumma Stealer.
- Defensive Notes
- Verify homebrew downloads against established community sources and trusted-source lists before running them.
- Check whether files match the intended device and inspect unexpected Windows files, batch files, and disguised scripts.
- Use up-to-date security software and browser protection to scan or block malicious downloads.
- If the archive was run, treat the computer as compromised; scan it, change important passwords from a clean device, review account logins and two-factor authentication settings, and rotate cryptocurrency keys or seed phrases from a clean device.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 85[.]137[.]52[.]21 | C2 server contacted by the malicious script. |
| URL | hxxps[:]//github[.]com/Voistace/EQVita | URL of the fake GitHub repository identified as distributing the malicious EQVita download. |
| URL | hxxps[:]//voistace[.]github[.]io | Related project page listed by the article as part of the fake EQVita campaign. |
MITRE ATT&CK
T1036 · MasqueradingThe fake project and Windows payload are presented as legitimate PlayStation Vita homebrew software; the script is disguised as a .txt file.T1059.003 · Windows Command ShellLaunch.bat uses a batch file to launch the hidden script.T1059.011 · LuaLuaJIT runs the hidden script contained in x64.txt.T1071.001 · Web ProtocolsThe script contacts the attacker’s server using a web address.T1105 · Ingress Tool TransferThe article says the server can provide instructions and the next piece of malware.T1204.002 · Malicious FileThe infection depends on a user running the downloaded archive and its contents.T1614 · System Location DiscoveryBefore contacting the server, the script checks where in the world the computer is.
Malware
Lumma StealerThe campaign uses a hidden script and loader behavior to contact attacker infrastructure and can lead to information-stealing payloads like SmartLoader and Lumma Stealer.SmartLoaderThe campaign uses a hidden script and loader behavior to contact attacker infrastructure and can lead to information-stealing payloads like SmartLoader and Lumma Stealer.
Vendors
Products
GitHubAttackers are using fake GitHub homebrew projects, such as EQVita, to trick PlayStation Vita fans into running Windows malware disguised as a harmless plugin or audio tool.LuaJITThe download contains three Windows files, including a disguised script named x64.txt that is executed by luaJIT.Malwarebytes Browser GuardMalwarebytes Browser Guard can help block known malicious pages and downloads before they reach you.Microsoft WindowsAttackers are using fake GitHub homebrew projects, such as EQVita, to trick PlayStation Vita fans into running Windows malware disguised as a harmless plugin or audio tool.PlayStation VitaAttackers are using fake GitHub homebrew projects, such as EQVita, to trick PlayStation Vita fans into running Windows malware disguised as a harmless plugin or audio tool.