
Rapid7 Links Dropping Elephant to In-Memory RAT Delivered via China-Themed Lure
Summary
Rapid7 analyzed a Dropping Elephant campaign that used a China-themed lure, DLL side-loading and Donut shellcode to run an evasive RAT in memory. The report details its tradecraft, C2 behavior and behavior-based detection opportunities.
Key points
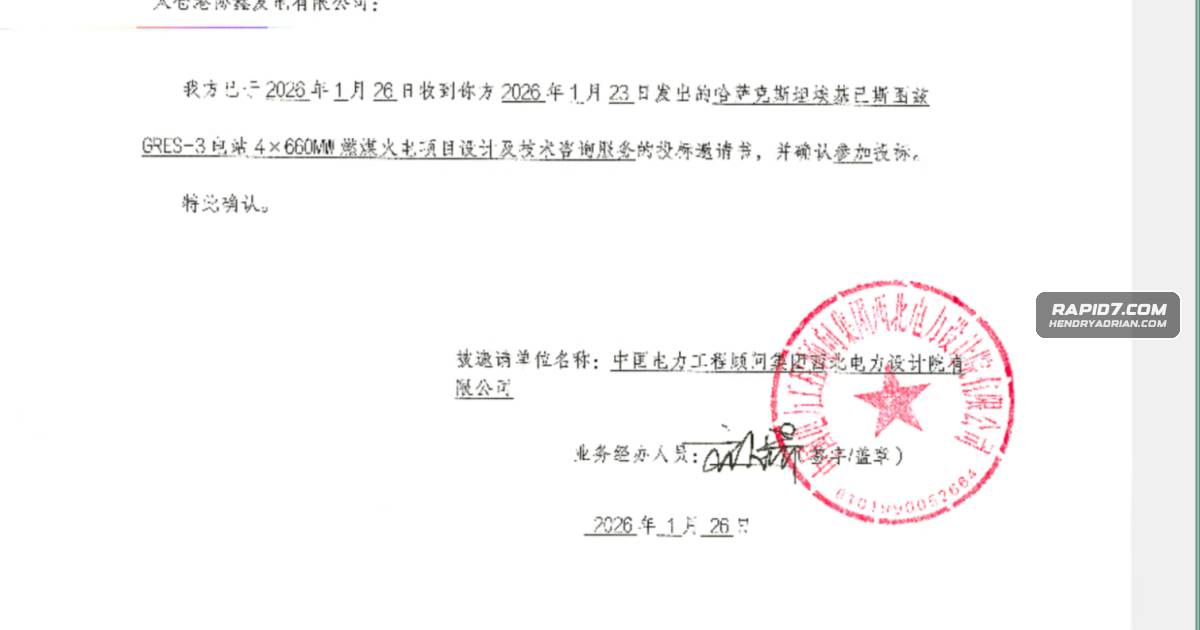
- A malicious Windows shortcut disguised as a PDF used a China energy-sector contract lure and launched an obfuscated PowerShell downloader.
- The campaign staged files in C:\Users\Public and used a scheduled task to run Fondue.exe, which side-loaded the malicious APPWIZ.cpl.
- The loader decrypted a payload containing Donut shellcode, which mapped the RAT directly into memory; Donut also patched AMSI, WLDP and ETW in-process.
- The RAT used anti-analysis checks and obfuscation, fingerprinted hosts, and supported command execution, file listing and transfer, and screenshots.
- RAT C2 used HTTPS and Salsa20-protected fields at gcl-power[.]org. During analysis, a beacon attempt returned HTTP 522, so operator follow-on actions could not be determined.
- Rapid7 linked the RAT to Dropping Elephant through shared command-handler, screenshot-capture and C2 request patterns, among other code-level overlaps.
- Rapid7 recommends behavior-based detection, including monitoring shortcut-to-PowerShell execution, the scheduled task, DLL side-loading, memory-resident payloads and in-process security-tool tampering.
Article Details
- Attack Vectors
- A malicious Windows shortcut disguised as a PDF launched an obfuscated PowerShell downloader.
- The downloader retrieved the decoy document and payload files from a staging server, then staged files in C:UsersPublic.
- A scheduled task named GoogleErrorReport ran Fondue.exe every minute, enabling DLL side-loading of the malicious APPWIZ.cpl.
- The loader decrypted an AES-wrapped payload containing Donut shellcode, which mapped the final RAT into memory.
- The RAT communicated with its C2 over HTTPS, using Salsa20-protected and Base64-wrapped fields.
- RAT handlers supported command execution, file download and execution, screenshots, directory listing, and file upload.
- Defensive Notes
- Prioritize behavior-based detection for shortcut files spawning PowerShell, including obfuscated command lines.
- Monitor for files staged in C:UsersPublic and for the GoogleErrorReport scheduled task running Fondue.exe every minute.
- Alert when Fondue.exe loads APPWIZ.cpl from C:UsersPublic rather than a legitimate Windows directory.
- Assess endpoint visibility for memory-resident payloads and in-process tampering with AMSI, WLDP, and ETW.
- Use memory-level visibility and threat hunting; the article cautions that hashes, filenames, and infrastructure may change.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | chinagreenenergy[.]org | Staging and delivery server used to retrieve the decoy document and malware files. |
| DOMAIN | gcl-power[.]org | Operational HTTPS C2 domain used by the RAT. |
| SHA256 | 56d656d684077e7b3231393f5464447cdc8eea81b6415c5f010bc52f0c8cb317 | Hash of the GRES3001.pdf decoy document delivered with the malware. |
| SHA256 | 7099c33933716c00c1f4bdb0281c230b981c76b23d7d1c83abc6f58968267d54 | Hash of the final RAT recovered from memory. |
| SHA256 | 914da75a4ad6d70db856a2bc318d8828f28894622f017ee78d470b4794faafa6 | Hash of the malicious APPWIZ.cpl loader used in the DLL side-loading chain. |
| SHA256 | a5e448af73b0ff6b6fcfe6ef7808120e1fd7e5c4c9b4edd68e1c980e5ea3406b | Hash of editor.dat, the Base64-wrapped AES-encrypted payload file. |
| SHA256 | a8ecbd9c049044ca4990a0e5960d19ce782a3b42d7763e9693d7c91ead24a0b7 | Hash of GRES3001.lnk, the malicious shortcut used to launch the downloader. |
| SHA256 | ecab0e747bff16a1163bbd9bb494e68dd4d7ca655ac7279bd4dd73221f7df57c | Hash of the AES-decrypted Donut loader blob. |
| URL | hxxps[:]//chinagreenenergy[.]org/doc/35566/SXxls | Staging URL used to deliver the decoy PDF. |
| URL | hxxps[:]//chinagreenenergy[.]org/doc/list/load-list/000bd4a8-814d-414c-8be8-f0c77a9c7e1e | Campaign staging URL used to download the encrypted editor.dat payload. |
| URL | hxxps[:]//chinagreenenergy[.]org/doc/list/load-list/8daaa3e4-c85e-40c1-a2a2-94679e94c417 | URL used to download the malicious APPWIZ.cpl loader. |
| URL | hxxps[:]//chinagreenenergy[.]org/doc/list/load-list/dfe87bbc-53e0-489f-a9e6-ab8f4be47cb9 | Payload delivery URL on the campaign's staging server. |
| URL | hxxps[:]//chinagreenenergy[.]org/doc/list/load-list/e7477b17-45f0-420b-b2b1-811d4c1556ea | Campaign staging URL used to download vcruntime140.dll. |
| URL | hxxps[:]//chinagreenenergy[.]org/doc/list/load-list/ecdc6b92-62b5-4acd-99f2-af09902938e1 | Campaign staging URL used to download msvcp140.dll. |
MITRE ATT&CK
T1005 · Data from Local SystemThe RAT enumerated local files and could upload a specified file through its uf handler.T1027 · Obfuscated Files or InformationThe chain used string-splitting obfuscation, junk file extensions, encrypted payloads, and encoded C2 fields.T1036.005 · Match Legitimate Resource Name or LocationThe campaign disguised a shortcut as a PDF and used a spoofed Edge icon and the GoogleErrorReport task name.T1041 · Exfiltration Over C2 ChannelThe RAT sent host data, screenshots, command output, and files over its C2 channel.T1053.005 · Scheduled TaskA scheduled task named GoogleErrorReport was configured to run Fondue.exe every minute.T1057 · Process DiscoveryThe RAT enumerated running processes and included the process list in its beacon.T1059.001 · PowerShellThe shortcut launched conhost.exe, which started the obfuscated PowerShell downloader.T1059.003 · Windows Command ShellThe RAT's cmx handler ran commands through cmd.exe and captured standard output.T1071.001 · Web ProtocolsThe RAT sent HTTPS POST requests to its C2 server over port 443.T1113 · Screen CaptureThe RAT's sc handler captured the virtual screen using BitBlt and encoded the image with WIC.T1204.002 · Malicious FileThe attack began when a user opened the malicious GRES3001.lnk shortcut.T1497.001 · System ChecksThe RAT checked CPUID, VM artifacts, running processes, and public-IP geolocation.T1562.001 · Disable or Modify ToolsBefore payload execution, Donut patched AMSI, WLDP, and ETW functions inside the process.T1574.002 · DLL Side-LoadingFondue.exe loaded the malicious APPWIZ.cpl staged alongside it.T1620 · Reflective Code LoadingDonut mapped and executed the final RAT in memory without writing the RAT to disk.
Threat Actors
Vendors
Products
Microsoft WindowsThe initial lure was a malicious Windows shortcut, GRES3001.lnk, disguised as a PDF and paired with a China energy-sector contract decoy document.PowerShellDefenders are advised to focus on behavior-based detections such as PowerShell launch chains, scheduled tasks, memory-resident payloads, and in-process defense tampering.
Tools
BinDiffBinDiff produced low signal, with 8.6% overall similarity.DiaphoraTherefore we also compared the samples with Diaphora, using pseudocode and AST-level features less affected by control-flow flattening.DonutRapid7 uncovered a Dropping Elephant campaign that used a China-themed lure, DLL side-loading, and Donut shellcode to deliver a heavily modified RAT that runs entirely in memory.