cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2392 articles

Threat Research · welivesecurity.com

ESET Details Its Role in Operation Endgame Disruption of Amadey and Stealc

ESET shared malware analysis, indicators, and affiliate-clustering data with Operation Endgame, which targeted about 50 domains and nearly 200 active command-and-control IPs used by Amadey and Stealc.
Jun 24, 2026
Threat Research · thehackernews.com

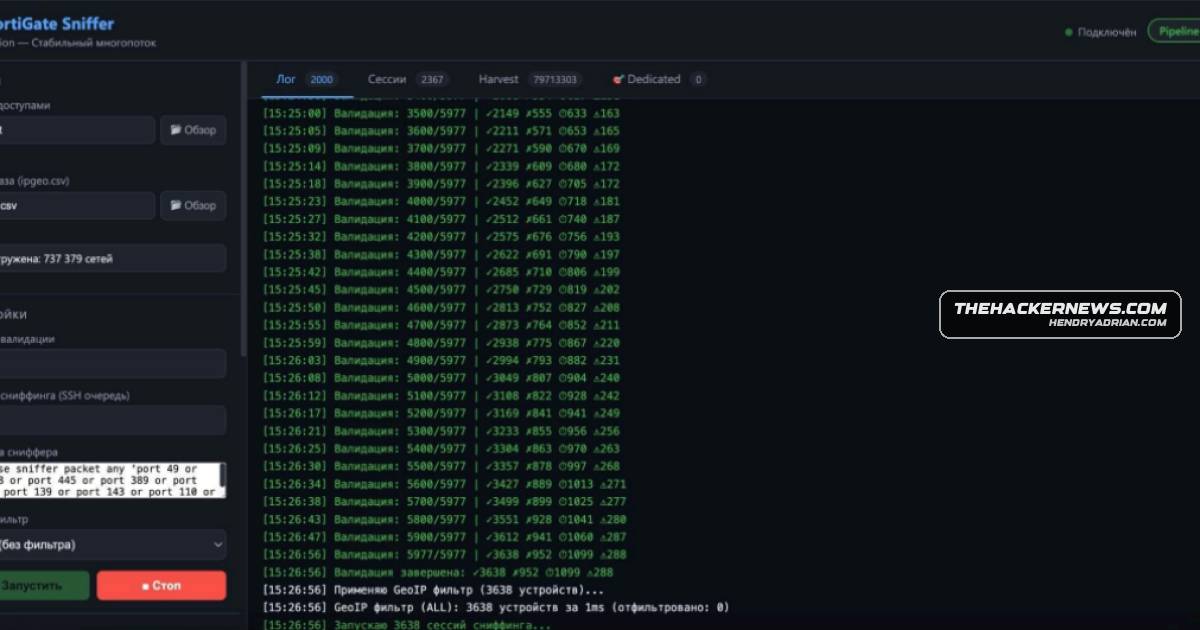
Report: FortiBleed Campaign Targets 430,000 FortiGate Firewalls, Identifies 110 Million Credentials

Researchers describe FortiBleed, a campaign active since February 2026 that reportedly brute-forces exposed devices and uses FortigateSniffer to capture credentials. The operation is estimated to have identified over 110 million credentials.

Jun 23, 2026
Threat Research · sentinelone.com

macOS.Gaslight Uses Prompt Injection to Disrupt AI-Assisted Malware Analysis

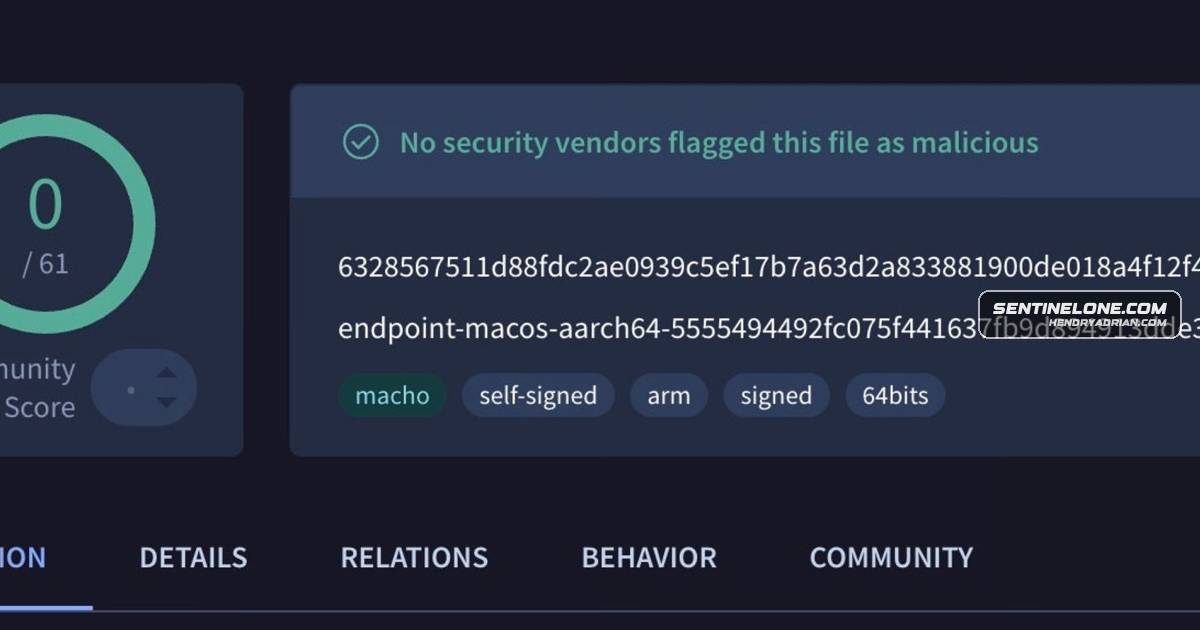
Researchers analyzed macOS.Gaslight, a Rust implant linked with high confidence to DPRK-aligned activity. It combines data theft and interactive access over Telegram C2 with fabricated system messages designed to mislead LLM-assisted triage.

Jun 23, 2026
Threat Research · dti.domaintools.com

Leaked APT35 Records Link Infrastructure Procurement to Moses Staff Operations

Analysis of leaked spreadsheets, payment records, and infrastructure data links APT35 procurement practices to Moses Staff, while exposing credentials and operational details left accessible after the leak.

Jun 23, 2026
Threat Research · darkreading.com

SOCRadar Details FortiBleed Campaign Using FortiGate Firewalls to Steal Credentials

SOCRadar describes FortiBleed as an ongoing campaign using FortigateSniffer to harvest credentials from compromised FortiGate firewalls. Researchers report 659 harvesting pipelines and more than 110 million stolen credentials.

Jun 23, 2026
Threat Research · thehackernews.com

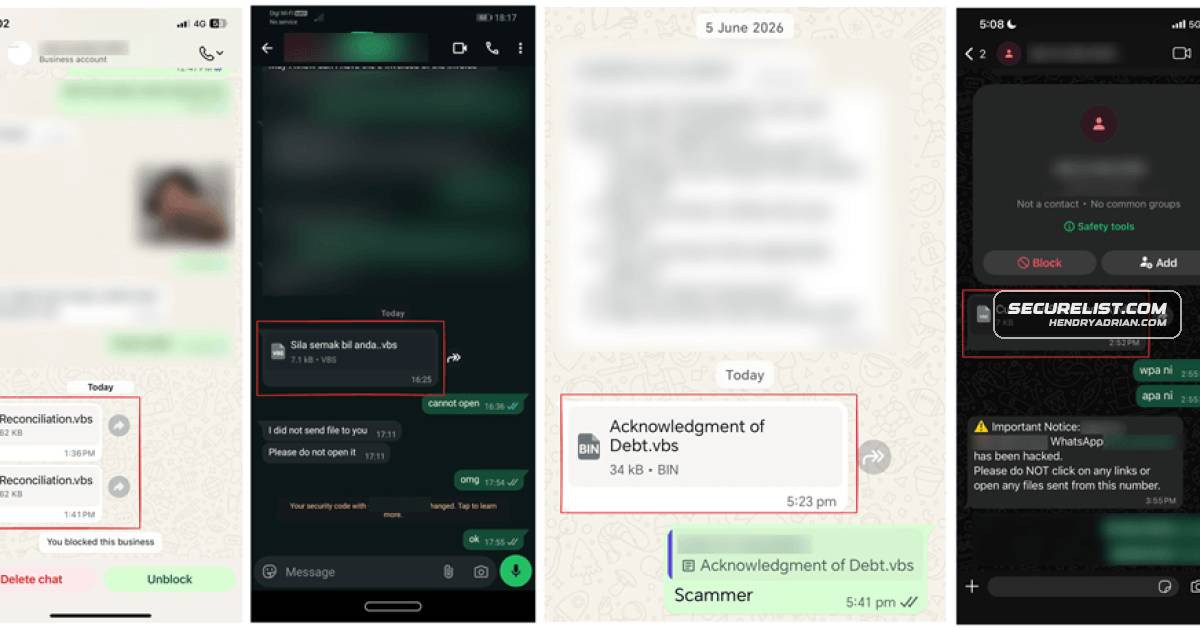
Kaspersky Finds WhatsApp VBScript Campaign Installing ManageEngine RMM Central

Kaspersky reports a WhatsApp campaign using disguised VBScript attachments to install ManageEngine RMM Central. The infection chain varies by WhatsApp Web or Desktop; account compromise is suspected, but the method is unclear.

Jun 23, 2026
Threat Research · any.run

EvilTokens Uses Browser-Decrypted Phishing to Gain Microsoft 365 Account Access

EvilTokens hides phishing content with AES-GCM encryption and uses Microsoft’s device login flow to gain account access. The analysis traces its browser requests and shows how investigators can uncover related activity.

Jun 23, 2026
Threat Research · recordedfuture.com

Compromised Websites Funnel World Cup Shoppers to Purchase Scams

Recorded Future describes scammers compromising legitimate websites to redirect search visitors to unindexed purchase-scam domains. The tactic uses cloaking, rotating domains, and multiple merchant accounts, and is appearing in World Cup-themed fraud.

Jun 23, 2026
Threat Research · zscaler.com

Payouts King-Linked Broker Uses Edgecution Malware to Gain Host Access

ThreatLabz reports that a Payouts King-linked initial access broker uses fake IT update prompts to install a hidden Edge extension and Python backdoor, enabling C2-driven system access and command execution.

Jun 23, 2026
Threat Research · trendmicro.com

Langflow Flaw CVE-2026-33017 Used to Deliver Linux Cryptominer

Trend Micro analyzed a campaign exploiting unauthenticated Langflow RCE to deploy a Monero miner, disable Linux security controls, establish persistence, and spread using SSH keys. It recommends updating Langflow and restricting public access.

Jun 23, 2026
Threat Research · thehackernews.com

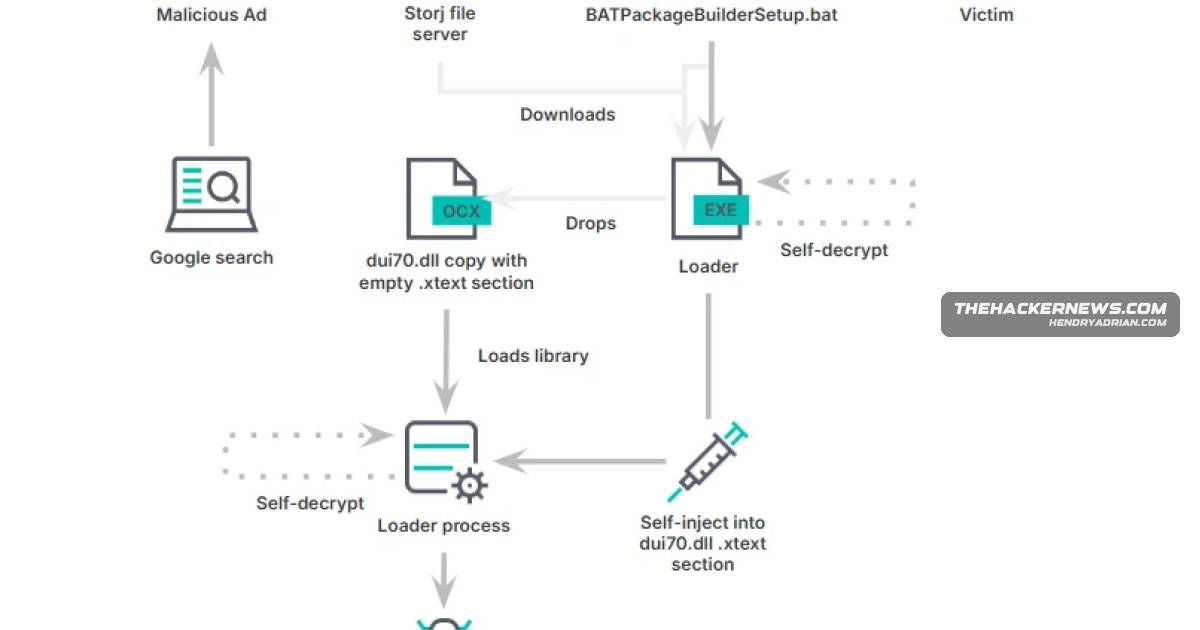
OXLOADER Uses Malicious Google Ads to Deliver CastleStealer

Elastic Security Labs described REF8372, a campaign using malicious Google Ads and a fake Node.js download site to deliver CastleStealer via OXLOADER. The loader uses obfuscation, anti-sandbox checks, Storj staging and DLL side-loading.

Jun 22, 2026
Threat Research · securelist.com

WhatsApp VBScript Campaign Installs ManageEngine Endpoint Central for Remote Access

A June 2026 campaign used financial-themed VBScript attachments sent via WhatsApp to install ManageEngine Endpoint Central for remote access. Victims were observed in multiple countries, with 80% in Malaysia; attribution remains uncertain.

Jun 22, 2026
Threat Research · threatdown.com

ThreatDown Details Prinz Eugen Ransomware’s Encryption and Anti-Forensic Tactics

ThreatDown analyzes Prinz Eugen, a Go ransomware sample observed on an infected customer, detailing recursive encryption, suspected RDP access, RemotePC-assisted payload staging, and self-deletion. The report links activity to ROOTBOY but notes attribution caveats.

Jun 22, 2026
Threat Research · elastic.co

Elastic Details OXLOADER Loader Delivering CASTLESTEALER Through Malicious Ads

Elastic Security Labs details OXLOADER, a Windows loader delivered through malicious Google Ads and Storj-hosted files to deploy CASTLESTEALER. Analysis describes its obfuscation, environment checks, .reloc shellcode staging, and in-memory payload execution.

Jun 21, 2026
Threat Research · infostealers.com

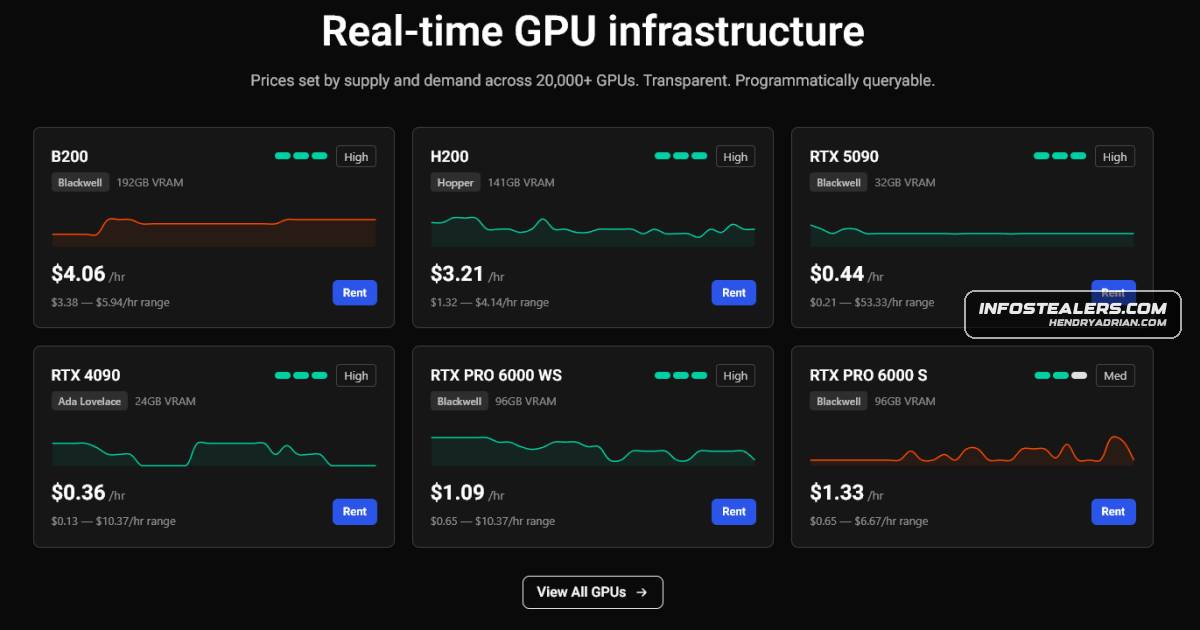
Report Details FortiBleed’s GPU-Powered Password-Cracking Campaign Against Fortinet Firewalls

The article describes Hudson Rock’s FortiBleed reporting: credentials exposed from nearly 75,000 FortiGate firewalls across 21,632 domains, and attackers reportedly using rented GPU clusters and Hashtopolis to crack hashes and pursue access to internal networks.

Jun 21, 2026
Threat Research · bleepingcomputer.com

Prinz Eugen Ransomware Targets Recent Files and Avoids On-System Ransom Notes

ThreatDown researchers describe Prinz Eugen ransomware’s file-prioritizing encryption, likely stolen-RDP access, and use of legitimate tools. The malware leaves no ransom note; researchers identified at least five victims.

Jun 20, 2026
Threat Research · seqrite.com

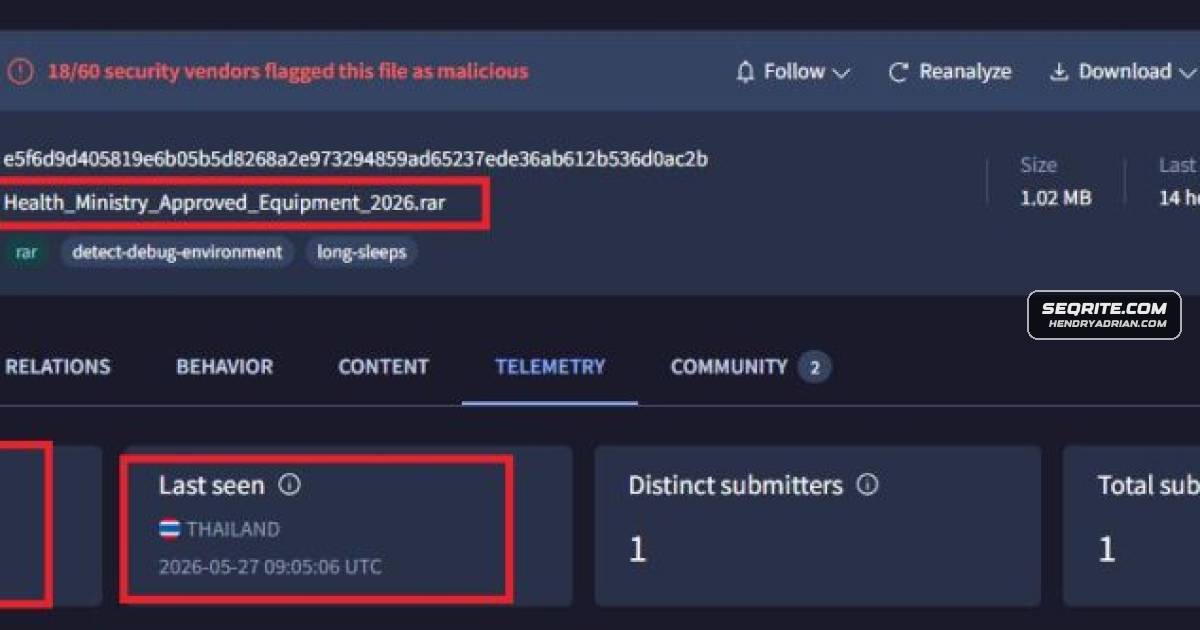
Seqrite Details Multi-Stage Stealer Campaign Targeting Thailand’s Healthcare Sector

Seqrite TRU describes a healthcare-themed phishing campaign using obfuscated batch loaders, Startup-folder persistence and a Python stealer to harvest browser data. Attempts to exfiltrate data through the Telegram Bot API failed due to connectivity timeouts.

Jun 20, 2026
Threat Research · circleid.com

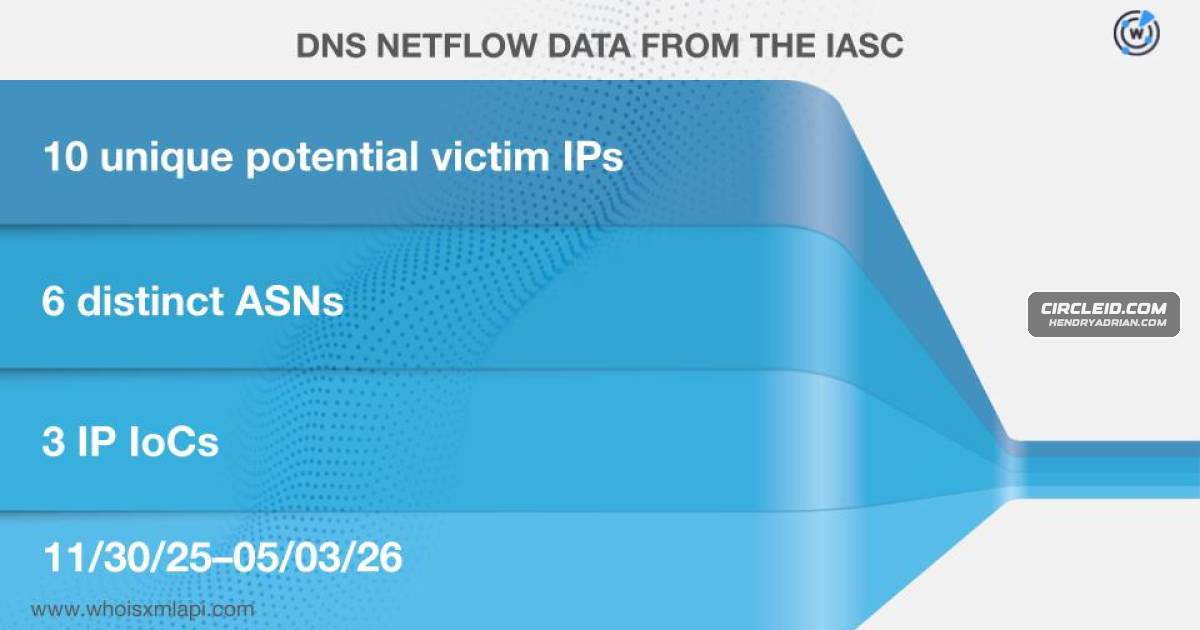
DNS Investigation Examines Shadow-Earth-053 Infrastructure

A DNS/WHOIS investigation of the China-aligned Shadow-Earth-053 campaigns examined 31 core indicators and related infrastructure, alongside reported Exchange and IIS exploitation, GODZILLA persistence, and ShadowPad DLL sideloading.

Jun 19, 2026
Threat Research · thehackernews.com

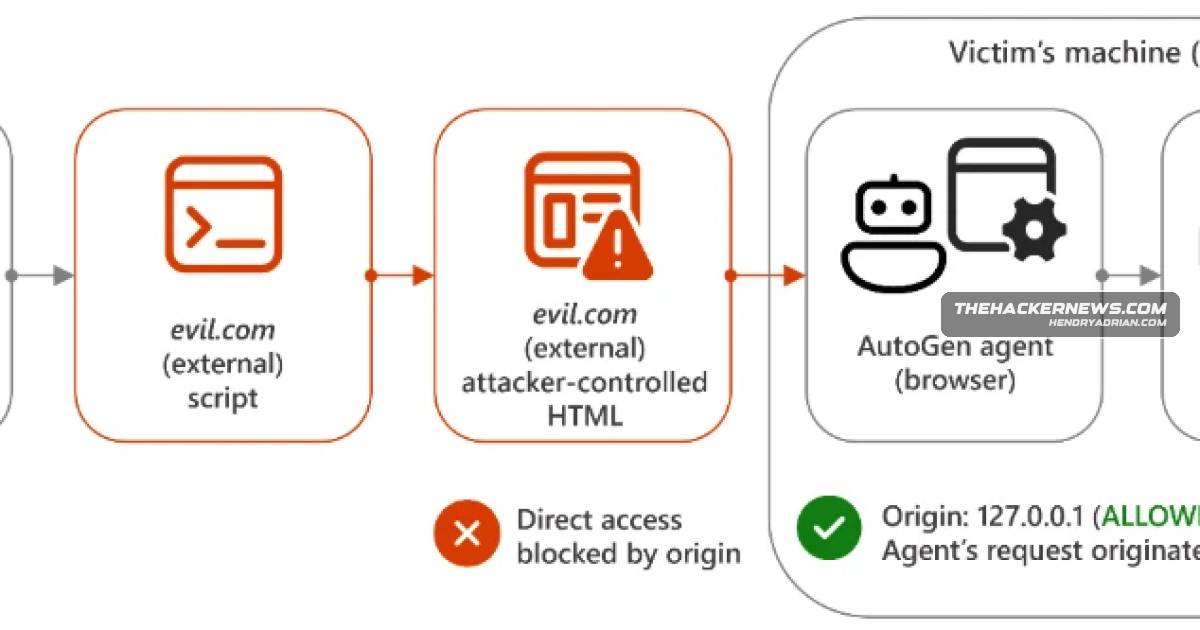
AutoJack Uses AI Browsing Agent to Trigger Host RCE in AutoGen Studio Pre-Releases

AutoJack chains localhost trust, skipped authentication, and unauthenticated command execution in AutoGen Studio prereleases to let a page loaded by an AI browsing agent trigger host code execution. Stable 0.4.2.2 is unaffected; a fix is in the main branch.

Jun 19, 2026
Threat Research · thehackernews.com

usbliter8 Exploit Enables Unpatchable SecureROM Code Execution on Apple A12 and A13

Paradigm Shift published usbliter8, a physical DFU-mode USB exploit for Apple A12/A13 SecureROM. It requires an RP2350-based board, can boot unsigned iBoot images, and cannot be fixed by software updates; no in-the-wild use had been publicly reported.

Jun 19, 2026
Threat Research · cyfirma.com

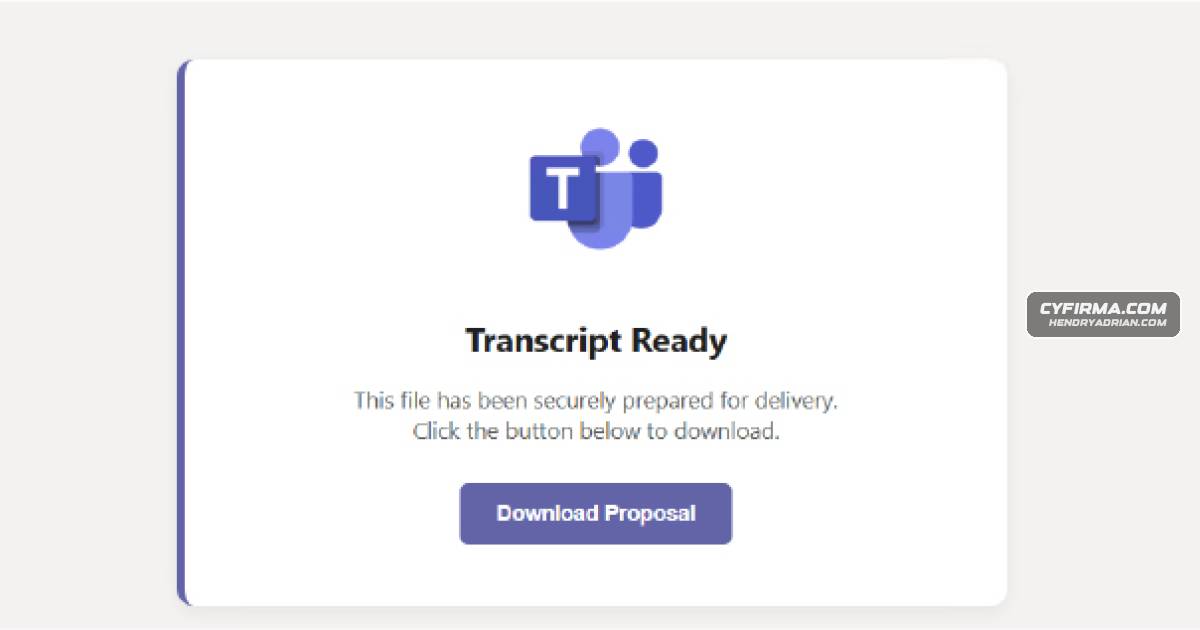
CYFIRMA Details Teams-Themed Phishing Campaign Using Signed Remote-Access Tool

CYFIRMA describes a Teams-themed phishing campaign delivering a signed installer for a legitimate remote-access tool. It reports compromised websites and Cloudflare-hosted lures, MSI execution, credential-theft capabilities and layered Windows persistence.

Jun 19, 2026
Threat Research · securityweek.com

CryptoBandits Malware Uses Tor for C2 and Acts as a Backdoor

Microsoft reports that the Windows-based CryptoBandits malware steals cryptocurrency wallet data, substitutes clipboard addresses, and uses a bundled Tor client for command-and-control and remote tasking.

Jun 19, 2026
Threat Research · cyble.com

Operation FanTrap Tracks FIFA 2026 Fraud Network With Nearly 4,000 Domains

Cyble’s CRIL investigation describes nearly 4,000 FIFA-themed domains linked to ticket and VIP scams, phishing, and streaming lures, plus fraud conducted through messaging platforms. Football-sector identity leak claims remain unverified.

Jun 19, 2026
Threat Research · bleepingcomputer.com

ESET Details GentleKiller Tools Used by Gentlemen Ransomware to Disable EDR

ESET says the Gentlemen ransomware group uses GentleKiller and other tools to disable EDR defenses. Its analysis describes BYOVD-based privilege escalation, targeting of more than 400 processes, and multiple tool variants.

Jun 19, 2026
PreviousPage 50 of 100 Next
© 2026 cyber.hendryadrian.com