
RoguePlanet and GreatXML Abuse Windows Defender and WinRE Security Boundaries
Summary
LevelBlue SpiderLabs details RoguePlanet’s Windows Defender workflow abuse to gain SYSTEM execution and GreatXML’s WinRE recovery-partition tampering to access BitLocker-protected data, with technical mechanisms and detection guidance.
Key points
- RoguePlanet combines Microsoft Defender, NTFS reparse points, opportunistic locks, VSS, and Windows Error Reporting to run attacker-controlled code as SYSTEM without kernel exploitation or memory corruption.
- Detection clues include a fake System32 directory under %TEMP%, the wermgr.exe:WDFOO alternate data stream, high-frequency file churn, and SYSTEM processes operating on attacker-controlled paths.
- GreatXML requires prior administrator access to place files on the recovery partition; an offline-scan state and WinRE boot can then expose a shell with access to the BitLocker-protected volume.
- GreatXML does not provide initial access. Its trigger can occur later from the login screen through Shift+Restart, requiring physical or console access.
- The article identifies recovery-partition file placement as GreatXML’s main detection opportunity and notes reduced visibility in some EDR platforms.
- The researchers report that no patch addressing GreatXML’s root cause had been released at the time of writing.
Article Details
- Attack Vectors
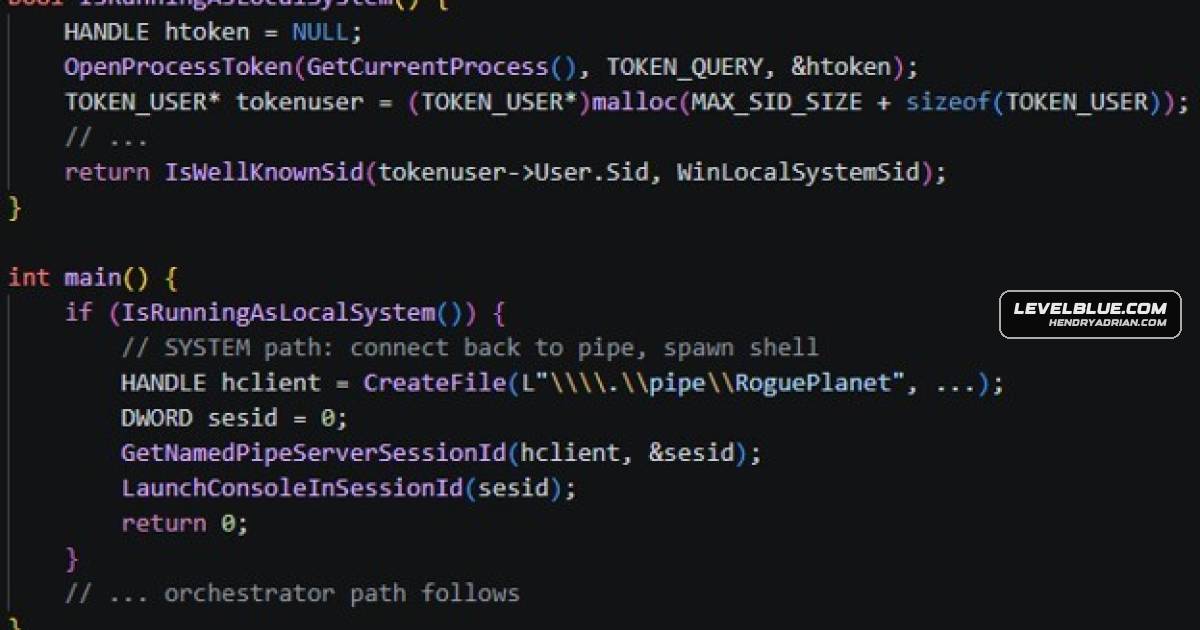
- RoguePlanet uses a local privilege-escalation chain: it coordinates Microsoft Defender scanning and quarantine with NTFS reparse-point junction swaps, opportunistic locks, and VSS activity, then triggers the Windows Error Reporting QueueReporting scheduled task to run attacker-controlled code as SYSTEM. The article says it can be started by a standard user and does not require kernel exploitation or memory corruption.
- GreatXML requires prior administrative access to place a malicious unattend.xml file and modified recovery files on the recovery partition, and an offline-scan WinRE state. A later physical or console user at the login screen can trigger WinRE, where the answer file runs commands before OS boot and provides access to the BitLocker-protected volume. The article says GreatXML does not provide initial access.
- Defensive Notes
- Prioritize detecting a System32-like directory under %TEMP% and creation of the wermgr.exe:WDFOO alternate data stream; the article describes these as reliable RoguePlanet indicators.
- Correlate high-frequency writes and file churn in UUID-named temporary paths with Defender activity, VSS shadow-copy discovery, raw device paths, mount-point activity, and junction-related behavior.
- Alert on SYSTEM processes, including Microsoft Defender, operating on user-controlled temporary paths; also investigate wermgr.exe execution outside C:\Windows\System32 and QueueReporting task execution initiated from a non-SYSTEM context.
- Monitor recovery-partition integrity and writes, including unattend.xml and modified Recovery or WindowsRE files. Correlate recovery-partition drive-letter assignment and manual offline-scan activity with a subsequent WinRE boot.
- The article reports reduced visibility for some EDR platforms during WMI use and recovery-partition manipulation; it recommends filesystem monitoring and recovery-partition integrity validation rather than relying only on process lineage or command-line logging.
- At the time of writing, the article reports that no patch addressing GreatXML's root cause had been released.
MITRE ATT&CK
T1036 · MasqueradingRoguePlanet creates a System32-like directory under %TEMP% and uses the wermgr.exe name and path structure to make attacker-controlled content resemble a trusted Windows binary.T1053.005 · Scheduled TaskRoguePlanet uses the Windows Task Scheduler COM interface to trigger the QueueReporting scheduled task, which runs the redirected wermgr.exe payload as SYSTEM.T1106 · Native APIRoguePlanet uses low-level Windows APIs, including NtSetInformationFile with FileRenameInformationEx, during its file manipulation and redirection stages.T1211 · Exploitation for StealthRoguePlanet manipulates Microsoft Defender's scan and quarantine workflow, redirecting its file operations so a SYSTEM-owned quarantine file can be replaced with attacker-controlled code.
Vendors
Products
BitLockerThe article also covers GreatXML, which abuses WinRE answer-file processing and offline-scan state to access BitLocker-protected data through the recovery partition.Microsoft Defender Antimalware PlatformLevelBlue SpiderLabs analyzed RoguePlanet, a multi-stage Windows exploit chain that abuses Microsoft Defender, NTFS reparse points, VSS, and Windows Error Reporting to achieve SYSTEM execution on fully patched WindowsWindows 10RoguePlanet is a local privilege escalation technique that can turn a standard user into SYSTEM on patched Windows 10 and Windows 11 systems.Windows 11RoguePlanet is a local privilege escalation technique that can turn a standard user into SYSTEM on patched Windows 10 and Windows 11 systems.
Tools
GreatXMLThe article also covers GreatXML, which abuses WinRE answer-file processing and offline-scan state to access BitLocker-protected data through the recovery partition.RoguePlanetLevelBlue SpiderLabs analyzed RoguePlanet, a multi-stage Windows exploit chain that abuses Microsoft Defender, NTFS reparse points, VSS, and Windows Error Reporting to achieve SYSTEM execution on fully patched WindowsSchneegans unattend-generator[Tooling artifact] Proof-of-concept names – RoguePlanet.exe, Schneegans unattend-generator