macOS ClickFix Campaign Deploys AppleScript Stealer and Persistent RAT
Summary
Netskope describes a macOS ClickFix campaign using fileless AppleScript to steal credentials and data, tamper with cryptocurrency wallets, and install persistent remote access through a fake Apple system service.
Key points
- Victims are lured into copying and running a Terminal command from fake utility, GitHub-style, or IT-support pages; the staged AppleScript runs in memory.
- The loader checks for a Russian keyboard layout and exits if detected, while reporting host and environment telemetry to its command-and-control server.
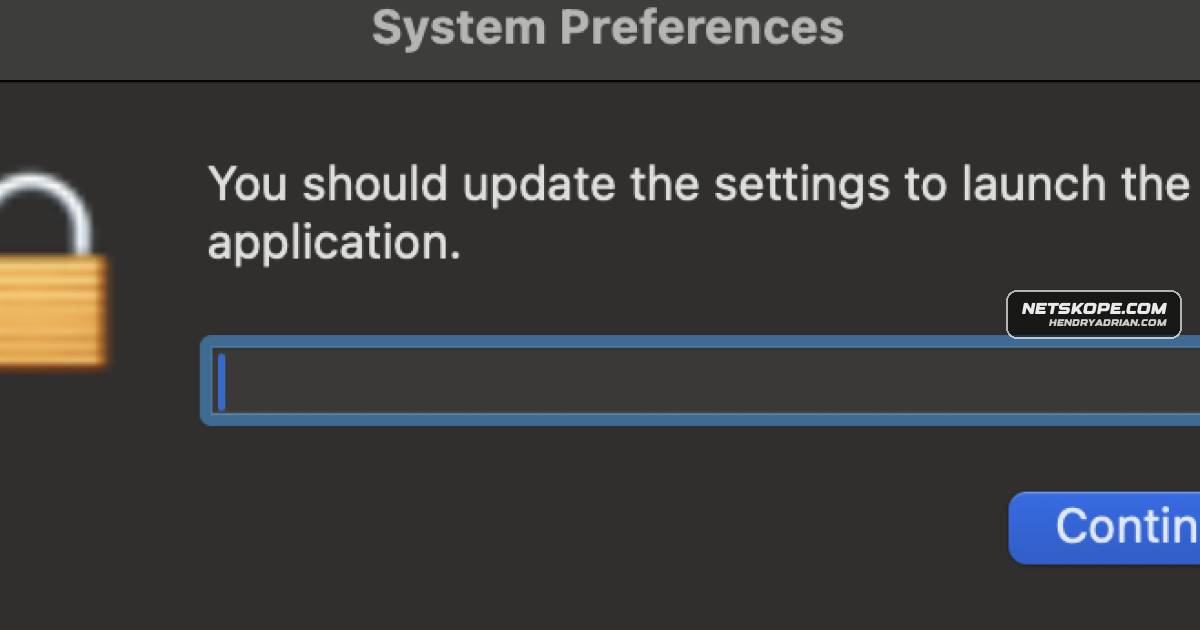
- The malware uses a fake macOS system dialog to harvest passwords and collects browser credentials, cookies, keychain contents, cryptocurrency wallet data, messaging sessions, files, and Apple Notes.
- It replaces app.asar files in five desktop cryptocurrency wallets with trojanized versions and ad-hoc re-signs the applications; the injected code's behavior is unknown.
- A LaunchDaemon or LaunchAgent disguised as com.apple.accountsd persists and checks in every 60 seconds, enabling the operator to execute commands on infected hosts.
- Netskope observed 25 short-lived lure domains, with activity targeting victims mainly in Asia, North America, and Oceania.
- Netskope recommends blocking lure domains and investigating the com.apple.accountsd persistence files and /tmp/shub_ staging paths; potentially affected wallet apps should be reinstalled from verified sources.
Article Details
- Attack Vectors
- ClickFix social engineering directs macOS users to copy and execute a terminal command, which downloads and runs a gzip-compressed, base64-encoded zsh loader.
- The loader fetches an AppleScript payload and pipes it directly to osascript in memory.
- The payload uses a fake macOS system dialog to solicit the victim's login password, then collects browser credentials, cookies, keychain contents, cryptocurrency wallet data, messaging and gaming session data, and selected files.
- The malware replaces app.asar files in targeted desktop cryptocurrency wallets with trojanized components and ad-hoc re-signs the bundles.
- It establishes LaunchDaemon or LaunchAgent persistence under the label com.apple.accountsd and polls its C2 every 60 seconds to receive and execute code.
- Defensive Notes
- Prioritize detecting and blocking the lure domains and page-loader.js delivery path before users copy the clipboard command.
- For potentially compromised hosts, investigate com.apple.accountsd LaunchDaemon or LaunchAgent persistence, /Library/Application Support/.com.apple.accountsd/, and /tmp/shub_ staging paths.
- Treat desktop wallet installations on potentially affected Macs as untrusted and reinstall them from a verified source.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | crystalfilehaven[.]com | Lure domain used in the ClickFix campaign. |
| DOMAIN | cyberdriftmatrix8[.]cyou | Lure domain used in the ClickFix campaign. |
| DOMAIN | cyberdriftmatrix9[.]cyou | Lure domain used in the ClickFix campaign. |
| DOMAIN | fileautumncastle[.]com | Lure domain used in the ClickFix campaign. |
| DOMAIN | filecedarcanvas[.]com | Lure domain used in the ClickFix campaign. |
| DOMAIN | filecobaltharbor[.]sbs | Lure domain used in the ClickFix campaign. |
| DOMAIN | filecopperforest[.]online | Lure domain used in the ClickFix campaign. |
| DOMAIN | fileivoryharbor[.]cyou | Lure domain used in the ClickFix campaign. |
| DOMAIN | filejadewallet[.]online | Lure domain used in the ClickFix campaign. |
| DOMAIN | filemintcastle[.]sbs | Lure domain used in the ClickFix campaign. |
| DOMAIN | fileopalvoyage[.]cyou | Lure domain used in the ClickFix campaign. |
| DOMAIN | filepearlsignal[.]com | Lure domain used in the ClickFix campaign. |
| DOMAIN | fileprairiestudio[.]com | Lure domain used in the ClickFix campaign. |
| DOMAIN | filesapphirecanvas[.]sbs | Lure domain used in the ClickFix campaign. |
| DOMAIN | filesapphiretower[.]cyou | Lure domain used in the ClickFix campaign. |
| DOMAIN | filesilverharbor[.]com | Lure domain used in the ClickFix campaign. |
| DOMAIN | meadowfileengine[.]com | Lure domain used in the ClickFix campaign. |
| DOMAIN | pa2373[.]com | Lure domain used in the ClickFix campaign. |
| DOMAIN | qwqerrqwr2145qw[.]com | C2 domain used for victim telemetry, payload delivery, data exfiltration, and RAT heartbeats. |
| DOMAIN | scope-quest[.]com | Domain identified in the article as a second C2 domain tied to the same operator. |
| DOMAIN | stellarnodegrid1[.]cyou | Lure domain used in the ClickFix campaign. |
| DOMAIN | stellarnodegrid8[.]cyou | Lure domain used in the ClickFix campaign. |
| DOMAIN | tensorforgegrid1[.]lol | Lure domain used in the ClickFix campaign. |
| DOMAIN | tensorforgegrid3[.]lol | Lure domain used in the ClickFix campaign. |
| DOMAIN | tensorforgegrid4[.]lol | Lure domain used in the ClickFix campaign. |
| DOMAIN | tensorforgegrid5[.]lol | Lure domain used in the ClickFix campaign. |
dbc9a6801423efc7s@ghastlier[.]com | Registrar admin contact email shared by the lure domains and linked by the article to the C2 domains. | |
| MD5 | 3447ad192726ee391881be6e86c7eeab | Campaign build hash sent in victim telemetry and included in the payload-delivery URL. |
| URL | hxxps[:]//qwqerrqwr2145qw[.]com/api/bot/heartbeat | C2 heartbeat endpoint polled by the persistent RAT. |
| URL | hxxps[:]//qwqerrqwr2145qw[.]com/api/debug/event | C2 endpoint receiving victim telemetry. |
| URL | hxxps[:]//qwqerrqwr2145qw[.]com/debug/payload[.]applescript?build=3447ad192726ee391881be6e86c7eeab | C2 URL delivering the AppleScript payload. |
| URL | hxxps[:]//qwqerrqwr2145qw[.]com/gate | C2 gate endpoint used to receive the collected data archive and provide wallet replacement archives. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe collected archive is sent to the C2 gate endpoint.T1056.002 · GUI Input CaptureA spoofed macOS dialog prompts victims for their login password.T1059.002 · AppleScriptThe second-stage payload is AppleScript executed through osascript.T1059.004 · Unix ShellThe staged zsh loader runs shell commands, including curl and eval.T1105 · Ingress Tool TransferThe loader downloads the AppleScript payload, and the wallet-injection routine downloads replacement archives from the C2.T1204.004 · Malicious Copy and PasteVictims are tricked into copying and manually executing a terminal command supplied by a lure page.T1539 · Steal Web Session CookieThe payload copies browser cookies and session data.T1543.001 · Launch AgentThe malware persists by installing a LaunchAgent or LaunchDaemon plist.T1555.001 · KeychainThe payload unlocks the login keychain and retrieves stored browser Safe Storage keys.T1560.001 · Archive via UtilityCollected data is compressed into an archive using ditto before exfiltration.
Malware
Products
Atomic Walletto overwrite the core app.asar files across five specific desktop wallets, including Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, and Trezor Suite.BraveThe payload targets a broad array of browsers, including Chrome, Brave, Edge, Opera, OperaGX, Vivaldi, Orion, Sidekick, Chrome Canary, Chromium, Chrome Dev, Arc, Coccoc, Chrome Beta, Firefox, Safari.DiscordDiscord – Enumerates four Discord installation variants (discord, discordcanary, discordptb, discorddevelopment), and copies Local Storage/leveldb/ from each, the location of Discord authentication tokens.Exodusset walletMap to walletMap & {{"Wallets/Desktop/Exodus", library & "Exodus/"}}Google Chromeexec 2>/dev/null), detaches to the background, and fetches the AppleScript payload with a spoofed Chrome user-agent string.Ledger Liveapp.asar files across five specific desktop wallets, including Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, and Trezor Suite.Ledger Walletthe core app.asar files across five specific desktop wallets, including Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, and Trezor Suite.macOSIn April 2026, Netskope Threat Labs reported a ClickFix campaign delivering an AppleScript-based infostealer to macOS users, pilfering sensitive data through a persistent fake system dialog.MetaMaskThe payload targets over 100 Chromium browser extension IDs associated with cryptocurrency wallets, MetaMask (nkbihfbeogaeaoehlefnkodbefgpgknn) among them, copying Local Extension Settings and IndexedDB for each matchedMicrosoft EdgeTo bypass this, the payload abuses the victim’s harvested password to unlock the login keychain, allowing it to extract the Safe Storage keys for Chrome, Brave, and Microsoft Edge directly.Mozilla FirefoxThe payload targets a broad array of browsers, including Chrome, Brave, Edge, Opera, OperaGX, Vivaldi, Orion, Sidekick, Chrome Canary, Chromium, Chrome Dev, Arc, Coccoc, Chrome Beta, Firefox, Safari.SafariThe payload targets a broad array of browsers, including Chrome, Brave, Edge, Opera, OperaGX, Vivaldi, Orion, Sidekick, Chrome Canary, Chromium, Chrome Dev, Arc, Coccoc, Chrome Beta, Firefox, Safari.SteamSteam – Copies config/loginusers.vdf, config/config.vdf, and any ssfn* files, and the session and authentication files for Steam’s “Remember Me” functionality.TelegramTelegram – Copies the tdata/ directory from ~/Library/Application Support/Telegram Desktop/, specifically targeting 16-character hexadecimal subdirectories and the key_datas file, and the session storage format forTrezor Suiteacross five specific desktop wallets, including Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, and Trezor Suite.
Tools
codesignIt then runs codesign -f -d -s to force an ad-hoc re-sign.curlVictims are socially engineered into executing a curl command that fetches a gzip-compressed stager, which pipes the second-stage AppleScript directly into osascript memory.osascriptVictims are socially engineered into executing a curl command that fetches a gzip-compressed stager, which pipes the second-stage AppleScript directly into osascript memory.
Industries
business servicesmainly in Asia, North America, and Oceania, across multiple segments led by technology, media, and business services sectors.Mediatargeting victims mainly in Asia, North America, and Oceania, across multiple segments led by technology, media, and business services sectors.Technologydomains, targeting victims mainly in Asia, North America, and Oceania, across multiple segments led by technology, media, and business services sectors.