Datadog Demonstrates Cross-Tenant Entra Takeover Through Compromised Agent Blueprint
Summary
Datadog demonstrates how an attacker controlling an Entra agent blueprint could add a credential, impersonate associated agents across tenants, and use a privileged agent’s permissions to take over a Global Administrator account.
Key points
- The scenario begins with an attacker who has compromised an Agent ID Administrator in a corporate Entra tenant.
- The attacker adds a credential to a third-party agent blueprint and uses it to authenticate as blueprint-associated identities in a subsidiary tenant.
- A blueprint principal can enumerate associated agent identities and exchange tokens to act as a privileged agent.
- The demonstrated Temporary Access Agent has Microsoft Graph permissions to read users and manage temporary access passes.
- An attacker could set a temporary access pass on a Global Administrator account, bypassing its password and MFA to gain access.
- The article highlights that a compromised blueprint can expose associated agent identities and their permissions across tenants.
Article Details
- Attack Vectors
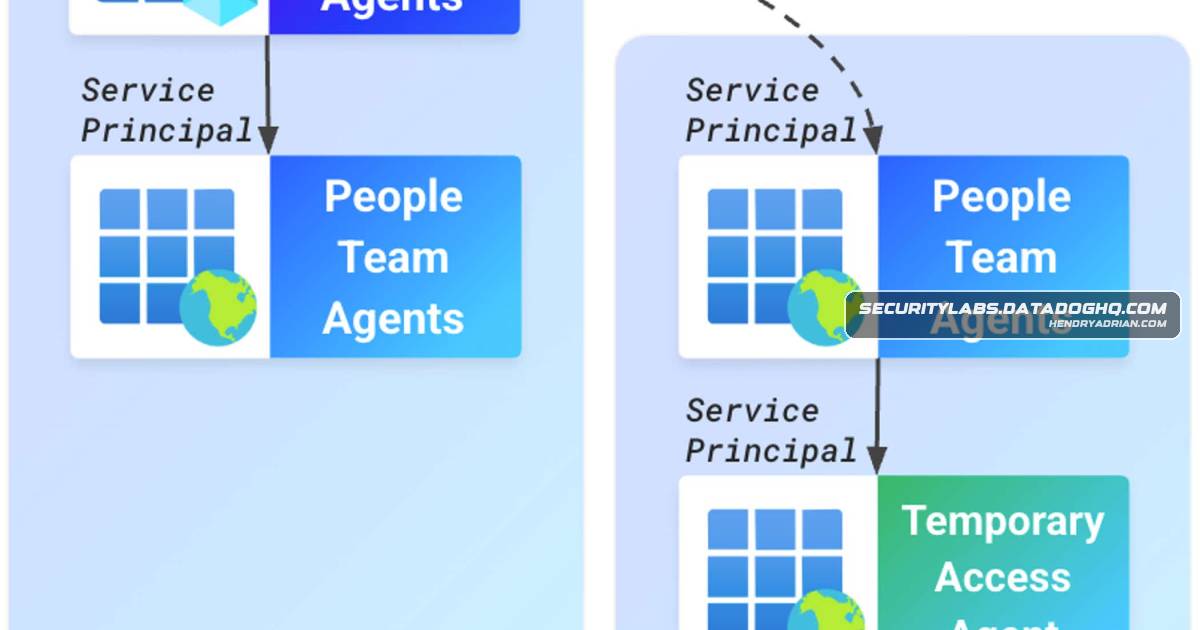
- An attacker with a compromised Agent ID Administrator account adds a credential to the People Team Agents blueprint.
- Using the blueprint credential, the attacker authenticates as its principal in a subsidiary tenant, enumerates associated agent identities, and exchanges tokens to impersonate the Temporary Access Agent.
- The attacker uses the agent's UserAuthMethod-TAP.ReadWrite.All permission to set a temporary access pass for a Global Administrator account, bypassing its password and MFA.
- Defensive Notes
- Treat third-party agent blueprints as trusted with the permissions of the agents created from them; a blueprint credential can expose associated identities across tenants.
- Restrict high-risk permissions and carefully control who can manage agent identities and add credentials to blueprints.
MITRE ATT&CK
T1078.004 · Cloud AccountsThe attacker uses the compromised Agent ID Administrator account and later the Global Administrator account to access cloud tenants.T1087.004 · Cloud AccountThe attacker enumerates agent service principals and user accounts in the subsidiary tenant through Microsoft Graph.T1098.001 · Additional Cloud CredentialsThe attacker adds a credential to the People Team Agents blueprint using Microsoft Graph's addPassword endpoint.
Vendors
Products
Azure PortalThe attacker navigates to https://portal.azure.com and signs in with the "globaladmin" account. After entering the target username, the sign-in page prompts for the TAP to sign in to the Azure Portal.Entra IDIn our scenario, an attacker has compromised a user with the Agent ID Administrator role in a target corporate Entra ID tenant.Microsoft GraphThe subsidiary tenant's agent, Temporary Access Agent, is granted the ability to fetch user details and update user passwords with Microsoft Graph permissions (UserAuthMethod-TAP.ReadWrite.All, User.Read.All).