
ClickFix Campaigns Deploy BabaDeda, Lorem Ipsum and Potemkin Loaders
Summary
Researchers detail three ClickFix campaigns using BabaDeda, Lorem Ipsum and Potemkin loaders to deliver stealers, RATs and backdoors through fake update lures, compromised sites, staged payloads and techniques including DLL side-loading and DGA-based C2.
Key points
- Researchers report that BabaDeda campaigns observed in April 2026 targeted education and financial organizations, using ClickFix prompts to trick users into running PowerShell commands.
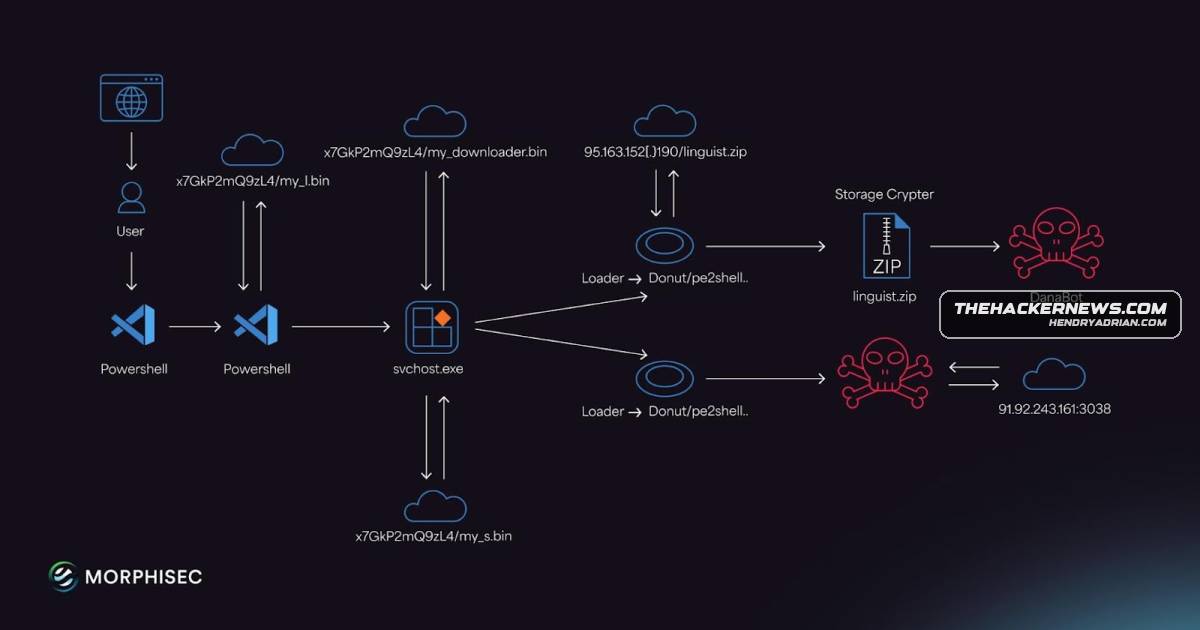
- BabaDeda Loader profiles hosts, checks for security products and can inject payloads into trusted Windows processes; associated malware can steal browser data and files, capture screenshots and execute commands.
- A separate BabaDeda delivery chain uses DLL side-loading and a staged component called Storage Crypter to deliver DanaBot and SectopRAT.
- The Lorem Ipsum campaign uses compromised WordPress sites and fake Edge update lures; its JavaScript payload chain leads to a backdoor and, according to researchers, Rapid Brigantine’s post-exploitation tools and ransomware deployments.
- Potemkin is delivered through an MSI package and HTA payload; the loader uses DGA-based C2 discovery and in-memory loading to deliver EtherRAT and RMMProject.
- In the Potemkin activity, researchers report Defender exclusions, Chisel reverse SOCKS tunnels, a Cloudflare tunnel and lateral movement via WMIExec and SMBExec; EtherRAT was propagated across more than 11 hosts.
- ClickFix is also reported in campaigns targeting Windows and macOS users. Apple added a macOS Tahoe 26.4 warning for users attempting to paste commands into Terminal.
Article Details
- Attack Vectors
- ClickFix lures trick users into pasting attacker-supplied PowerShell commands or commands shown in fake browser security-update prompts.
- BabaDeda Loader campaigns use hidden PowerShell, in-memory shellcode, DLL side-loading, and externally stored payloads to deploy stealers and RATs.
- Lorem Ipsum Loader is delivered from compromised WordPress sites through a downloaded ZIP archive and an outdated Node.js version that runs JavaScript payloads.
- A JavaScript dropper launches a batch script that establishes persistence and starts a DLL side-loading chain to decode Lorem Ipsum Loader.
- A ClickFix-delivered MSI package drops Potemkin through an HTA payload; Potemkin uses DGA-based C2 discovery and reflectively loads modules in memory.
- Potemkin activity includes configuring Microsoft Defender exclusions, deploying Chisel reverse SOCKS tunnels and a Cloudflare tunnel, and using WMIExec and SMBExec for lateral movement.
- The campaigns deliver or deploy DanaBot, SectopRAT, EtherRAT, RMMProject, and the Lorem Ipsum Backdoor.
- Defensive Notes
- Apple introduced a macOS Tahoe 26.4 security pop-up warning users who attempt to paste commands into Terminal.
- Treat requests to paste commands from websites, chat agents, messaging apps, or email as a potential threat; Apple says its alert is intended to help prevent users from running unexpected commands.
MITRE ATT&CK
T1005 · Data from Local SystemThe delivered malware reads selected local files and collects browser artifacts, including cookies, history, and saved credentials.T1021.002 · SMB/Windows Admin SharesThe actor used SMBExec to move laterally and propagate EtherRAT across hosts.T1047 · Windows Management InstrumentationThe actor used WMIExec during lateral movement toward the domain controller.T1055 · Process InjectionBabaDeda Loader injects its retrieved payload into a trusted Windows process such as svchost.exe.T1059.001 · PowerShellBabaDeda campaigns use hidden PowerShell commands, and fake-update lures prompt users to run malicious commands.T1059.007 · JavaScriptThe Lorem Ipsum chain uses Node.js to execute JavaScript payloads from a downloaded archive.T1082 · System Information DiscoveryBabaDeda Loader profiles the host, and its delivered malware collects detailed system information.T1090 · ProxyThe reported activity used Chisel reverse SOCKS tunnels and a Cloudflare tunnel for persistent access.T1105 · Ingress Tool TransferThe campaigns download ZIP archives, payloads, and additional modules, including modules retrieved from a URL at runtime.T1113 · Screen CaptureThe delivered malware and RMMProject can capture screenshots.T1204.004 · Malicious Copy and PasteClickFix lures persuade users to paste attacker-supplied commands and run them.T1562.001 · Disable or Modify ToolsThe reported hands-on-keyboard activity includes configuring Microsoft Defender exclusions.T1568.002 · Domain Generation AlgorithmsPotemkin uses a domain generation algorithm to locate its C2.T1574.002 · DLL Side-LoadingBabaDeda and Lorem Ipsum delivery chains use DLL side-loading to launch malicious components.T1620 · Reflective Code LoadingPotemkin reflectively loads follow-on modules in memory.
People
Anna PhamHuntress researcher who described the Potemkin loader and its C2 and loading capabilities.Joshua GreenBlueVoyant researcher who reported on the Lorem Ipsum Loader campaign and its shift to ClickFix lures.Shmuel UzanMorphisec researcher who described the evolution of BabaDeda Loader and its stealth, evasion, and payload capabilities.Thomas ElkinsBlueVoyant researcher who reported on the Lorem Ipsum Loader campaign and its shift to ClickFix lures.Zach RogersHuntress researcher who described the Potemkin loader and its C2 and loading capabilities.
Threat Actors
Forging MarauderThe article identifies Forging Marauder as an alias of Fox Tempest, which it says advertised a malware-signing-as-a-service operation.Fox TempestThe article says Microsoft disrupted Fox Tempest, which advertised a malware-signing-as-a-service operation using fraudulently signed Microsoft Trusted Signing certificates; the delivery shift is attributed to that disruption.Rapid BrigantineThe article identifies Rapid Brigantine as an alias of Vanilla Tempest and says the Lorem Ipsum chain hands off to its established post-exploitation tooling.Vanilla TempestThe Lorem Ipsum ecosystem is attributed with high confidence to this financially motivated threat actor, which is associated in the article with ransomware deployments including Rhysida.Vice SocietyThe article identifies Vice Society as an alias of Vanilla Tempest, to which the Lorem Ipsum ecosystem is attributed with high confidence.VICE SPIDERThe article identifies Vice Spider as an alias of Vanilla Tempest, to which the Lorem Ipsum ecosystem is attributed with high confidence.
Malware
BabaDeda LoaderResearchers have uncovered multiple ClickFix campaigns distributing the BabaDeda Loader, Lorem Ipsum Loader, and Potemkin loader to deliver stealers, RATs, and backdoors through deceptive PowerShell and browser-updateDanabot#BabaDedaLoaderEtherRAT#BabaDedaLoaderLorem Ipsum Backdoor“The Lorem Ipsum Loader is designed to retrieve the next-stage Lorem Ipsum Backdoor from C2 infrastructure obtained from attacker-controlled profiles hosted on social networking platforms,” BlueVoyant said, adding theLorem Ipsum LoaderResearchers have uncovered multiple ClickFix campaigns distributing the BabaDeda Loader, Lorem Ipsum Loader, and Potemkin loader to deliver stealers, RATs, and backdoors through deceptive PowerShell and browser-updatePotemkinhave uncovered multiple ClickFix campaigns distributing the BabaDeda Loader, Lorem Ipsum Loader, and Potemkin loader to deliver stealers, RATs, and backdoors through deceptive PowerShell and browser-update lures.Rhysida#BabaDedaLoaderRMMProject#BabaDedaLoaderSectopRAT#BabaDedaLoaderStorage CrypterWhat’s notable about these attacks is the use of a staged loader component dubbed Storage Crypter that reads the payload material from external storage-like files such as “List.Control.dat.”
Vendors
Applecommands into the Terminal app from websites (or chat agents, or messaging or email apps) has prompted Apple to introduce a new security pop-up in macOS Tahoe 26.4 that warns Mac users attempting to do so.BlueVoyantcalled BabaDeda Loader, Lorem Ipsum Loader, and Potemkin, per independent reports from Morphisec, BlueVoyant, and Huntress, respectively.HuntressLoader, Lorem Ipsum Loader, and Potemkin, per independent reports from Morphisec, BlueVoyant, and Huntress, respectively.MicrosoftThe attacks mark a departure from prior opportunistic campaigns that employed trojanized Microsoft Teams installers through fake download portals promoted via SEO poisoning and malvertising.Morphisecmalware loaders called BabaDeda Loader, Lorem Ipsum Loader, and Potemkin, per independent reports from Morphisec, BlueVoyant, and Huntress, respectively.
Products
macOS Tahoe 26.4chat agents, or messaging or email apps) has prompted Apple to introduce a new security pop-up in macOS Tahoe 26.4 that warns Mac users attempting to do so.Microsoft Defender Antimalware Platformthe unknown threat actor is said to have engaged in hands-on keyboard activity to configure Microsoft Defender exclusions, deploy Chisel reverse SOCKS tunnels, conduct additional reconnaissance, set up aMicrosoft TeamsThe attacks mark a departure from prior opportunistic campaigns that employed trojanized Microsoft Teams installers through fake download portals promoted via SEO poisoning and malvertising.Microsoft Trusted Signingoperation to help deliver malware without raising any red flags using fraudulently signed Microsoft Trusted Signing certificates.Microsoft WindowsIt hides payloads, evades security checks, and injects into trusted Windows processes.Node.jssecurity update lures to run a malicious command that downloads a ZIP file and an outdated version of Node.js released in 2017 (version 7.10.1) to execute JavaScript-based payloads present within the archive whileWordPressLorem Ipsum Loader spreads through compromised WordPress sites and fake browser update lures.
Tools
Chiselis said to have engaged in hands-on keyboard activity to configure Microsoft Defender exclusions, deploy Chisel reverse SOCKS tunnels, conduct additional reconnaissance, set up a Cloudflare tunnel for persistentsmbexecreconnaissance, set up a Cloudflare tunnel for persistent access, and spread laterally via WMIExec and SMBExec to reach the domain controller and propagate EtherRAT across over 11 hosts.wmiexecadditional reconnaissance, set up a Cloudflare tunnel for persistent access, and spread laterally via WMIExec and SMBExec to reach the domain controller and propagate EtherRAT across over 11 hosts.
Industries
ArchitectureThe hacked websites span multiple sectors, including architecture, legal services, and construction technology.Construction technologyThe hacked websites span multiple sectors, including architecture, legal services, and construction technology.Cryptocurrencythat was first documented by Morphisec in November 2021 in connection with a campaign targeting the cryptocurrency and Web3 sectors to distribute information stealers, RATs, and LockBit ransomware.EducationAttacks involving BabaDeda Loader, observed in April 2026, have targeted education and financial organizations.Legal servicesThe hacked websites span multiple sectors, including architecture, legal services, and construction technology.Web3documented by Morphisec in November 2021 in connection with a campaign targeting the cryptocurrency and Web3 sectors to distribute information stealers, RATs, and LockBit ransomware.