cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2376 articles

Threat Research · cloud.google.com

Mandiant Observes Threat Actors Using ARTEX and Other Agentic Attack Frameworks

Google Threat Intelligence Group and Mandiant report actors using ARTEX, PentAGI and related LLM-driven frameworks for reconnaissance, privilege escalation, lateral movement and data theft, and recommend controls including short-lived credentials and behavioral dete
Oct 30, 2026
Threat Research · fieldeffect.com

Trojanized Claude Code Extension Distributed Through Cursor Marketplace

A trojanized Claude Code 2.1.313 extension was available in Cursor’s marketplace on Oct. 29, 2026; up to 5,000 users may have installed it. Its loader collected host data, added an SSH key, installed persistence and attempted a reverse tunnel.

Oct 30, 2026
Threat Research · hunt.io

PHP2Shell Investigation Maps Exploit Tooling and Reported PAN-OS Compromises

Hunt IO mapped 616 PHP2Shell-related files and analyzed exploit kits and operator activity. Dream Research reported PHP2Shell and Fragnesia were used to root 25 PAN-OS servers; Unit 42 later reported verifying the tooling and results.

Oct 30, 2026
Threat Research · reversinglabs.com

Researchers Detail AnimateClipper and Efimer Crypto-Clipboard Malware

ReversingLabs examines how AnimateClipper and Efimer replace copied cryptocurrency wallet addresses, including address-matching methods, evasion features, distribution, and ways users can reduce risk.

Oct 30, 2026
Threat Research · stepsecurity.io

Trojanized Claude Code Extension 2.1.313 Planted a Persistent SSH Backdoor

StepSecurity's sandbox and registry analysis found that official Claude Code extension 2.1.313, distributed via Open-VSX and Cursor, ran a loader that installed SSH access, persistence and a reverse tunnel. Cursor said up to 5,000 users received it.

Oct 30, 2026
Threat Research · rogueauthority.org

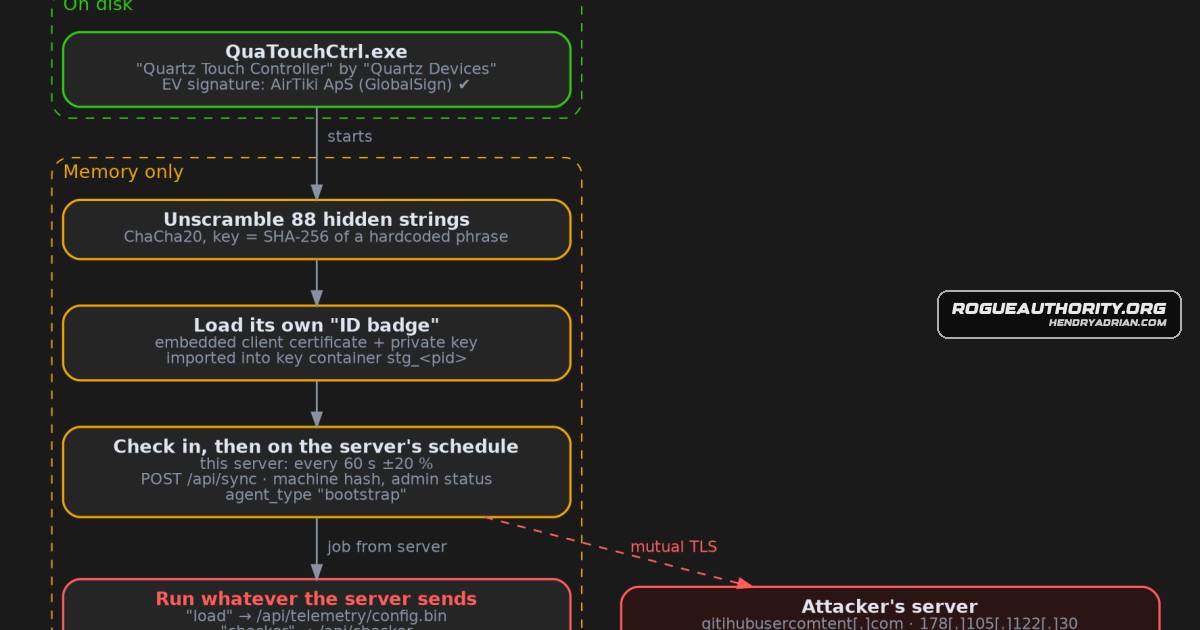
Signed QuaTouchCtrl Loader Uses Mutual TLS to Reach Its Command Server

Analysis identifies QuaTouchCtrl.exe as a signed loader with encrypted strings and an embedded client certificate for mutual TLS. It can run server-provided modules in memory; the observed server replied with no jobs.

Oct 29, 2026
Threat Research · infostealers.com

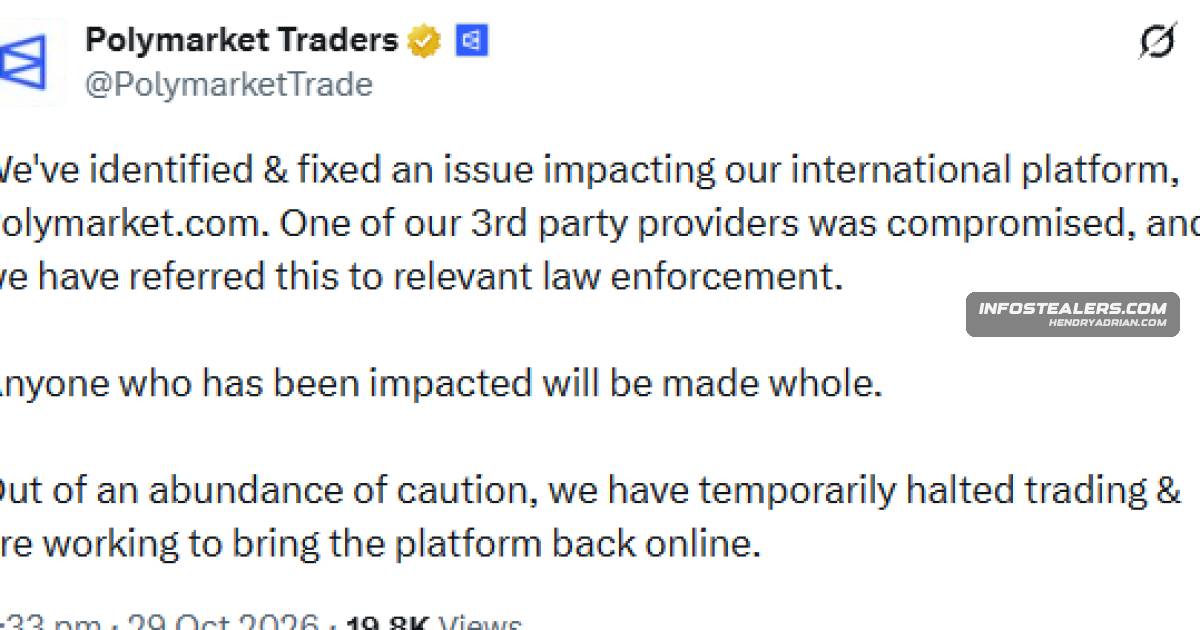
Researchers Find Wallet-Draining Code in Polymarket-Associated Third-Party Script

Hudson Rock reports that a retrieved DebugBear-associated script contained code targeting Polymarket trading sessions to sell or transfer assets. Polymarket build metadata records removal of the integration; affected users and losses remain unverified.

Oct 29, 2026
Threat Research · thehackernews.com

Yoba Campaign Uses Fake ChatGPT and Claude Apps to Deliver Crypto Miners

Check Point describes Yoba, a campaign using fake ChatGPT and Claude desktop-app projects to distribute YobaLoader and XMRig miners, with DLL sideloading, anti-analysis checks, scheduled-task persistence, and payload injection.

Oct 29, 2026
Threat Research · wiz.io

Wiz Details How AI Agents Are Used in Real-World Intrusions

Wiz analyzes public reports and three investigations involving agentic attack workflows, identifying patterns such as machine-paced iteration, adaptive scripts, broad probing and self-documenting tools that may offer defenders detection opportunities.

Oct 29, 2026
Threat Research · infoblox.com

Researchers Trace UltraViewer and UltraMailer Abuse to QuickBooks Phishing and Trojanized Installers

Infoblox traced a QuickBooks phishing campaign using UltraMailer’s chanret[.]com tracker across more than 350 lookalike domains, and found trojanized UltraMailer and UltraViewer installers carrying njRAT and DarkKometa. Researchers found no evidence implicating either’s

Oct 29, 2026
Threat Research · blog.talosintelligence.com

Cisco Talos Details NIK C2, an AI-Integrated Windows Implant

Cisco Talos analyzed NIK C2, a Go-based Windows implant observed in the wild. It can steal credentials and other data, route operator prompts through OpenAI's API, maintain dual-channel C2, evade defenses, and deploy a persistent screen locker.

Oct 29, 2026
Threat Research · thehackernews.com

Cisco SD-WAN Flaw Exploited to Deploy Malware Designed to Steal Traffic Encryption Keys

Talos says attackers exploited CVE-2026-20127 in Cisco Catalyst SD-WAN to deploy KeyDrift, which reads AES-256 key material from decrypted controller traffic. Whether any keys were sent is unknown; Cisco provides fixes and detection guidance.

Oct 29, 2026
Threat Research · securelist.com

Kaspersky Details NetamLoader XAML Chain Targeting Custom Asian Government Windows Build

Kaspersky detailed NetamLoader, a multi-stage .NET/XAML loader that abuses deserialization and AMSI, runs through a Patch My PC process, and communicates with C2. KSN telemetry showed one Asian victim; attribution remains unknown.

Oct 29, 2026
Threat Research · socket.dev

Investigation Links 319 Search-Hijacking Extensions to About 13.4 Million Installs

Socket’s investigation identified 319 search-hijacking Chrome extensions with about 13.4 million installs over a decade. They route queries through operator-controlled proxies for referral revenue; researchers warn this could enable selective malicious redirects, but do

Oct 29, 2026
Threat Research · crowdstrike.com

VAPOR PANDA Uses ARTEX and LLMs to Scale Global Espionage Campaign

CrowdStrike reports VAPOR PANDA used ARTEX with DeepSeek and another LLM for parallel intrusions against 200+ organizations; it confirmed post-exploitation at nine and BLOODALCHEMY deployment at two ministries, with endpoint-sensor evasion built into workflows.

Oct 29, 2026
Threat Research · sophos.com

Sophos Details AI-Assisted Aur0ra Ransomware Operations

Sophos researchers describe GOLD OGRE’s use of Cursor and other AI agents in Aur0ra ransomware operations, including Active Directory discovery, credential abuse and lateral movement. Three victims were later named on Aur0ra’s leak site.

Oct 29, 2026
Threat Research · global.ptsecurity.com

StingyBasilisk Uses COM Hijacking and Named-Pipe C2 to Hide Windows Malware

PT ESC IR describes StingyBasilisk, active since at least April 2022, using COM hijacking, Windows Time Providers, SMB lateral movement and named-pipe C2; its loaders capture network traffic and execute encrypted payloads in memory.

Oct 29, 2026
Threat Research · bleepingcomputer.com

Cisco SD-WAN Flaw Exploited to Deploy KeyDrift Malware

Cisco Talos reports that UAT-11473 exploited CVE-2026-20127 to deploy KeyDrift on Cisco SD-WAN controllers. The framework can intercept control traffic and collect keying material; Cisco recommends applying the available update.

Oct 29, 2026
Threat Research · recordedfuture.com

Researchers Detail Three Traffer Teams’ Fake Prediction-Market Operations

Recorded Future details how AtlasCore, PolyFucked and Magnetic Team use fake prediction-market platforms to rig outcomes, block withdrawals and collect identity/payment data. They use AI for promotion and victim support; revenue figures and suspected AI-assisted code do

Oct 29, 2026
Threat Research · securitylabs.datadoghq.com

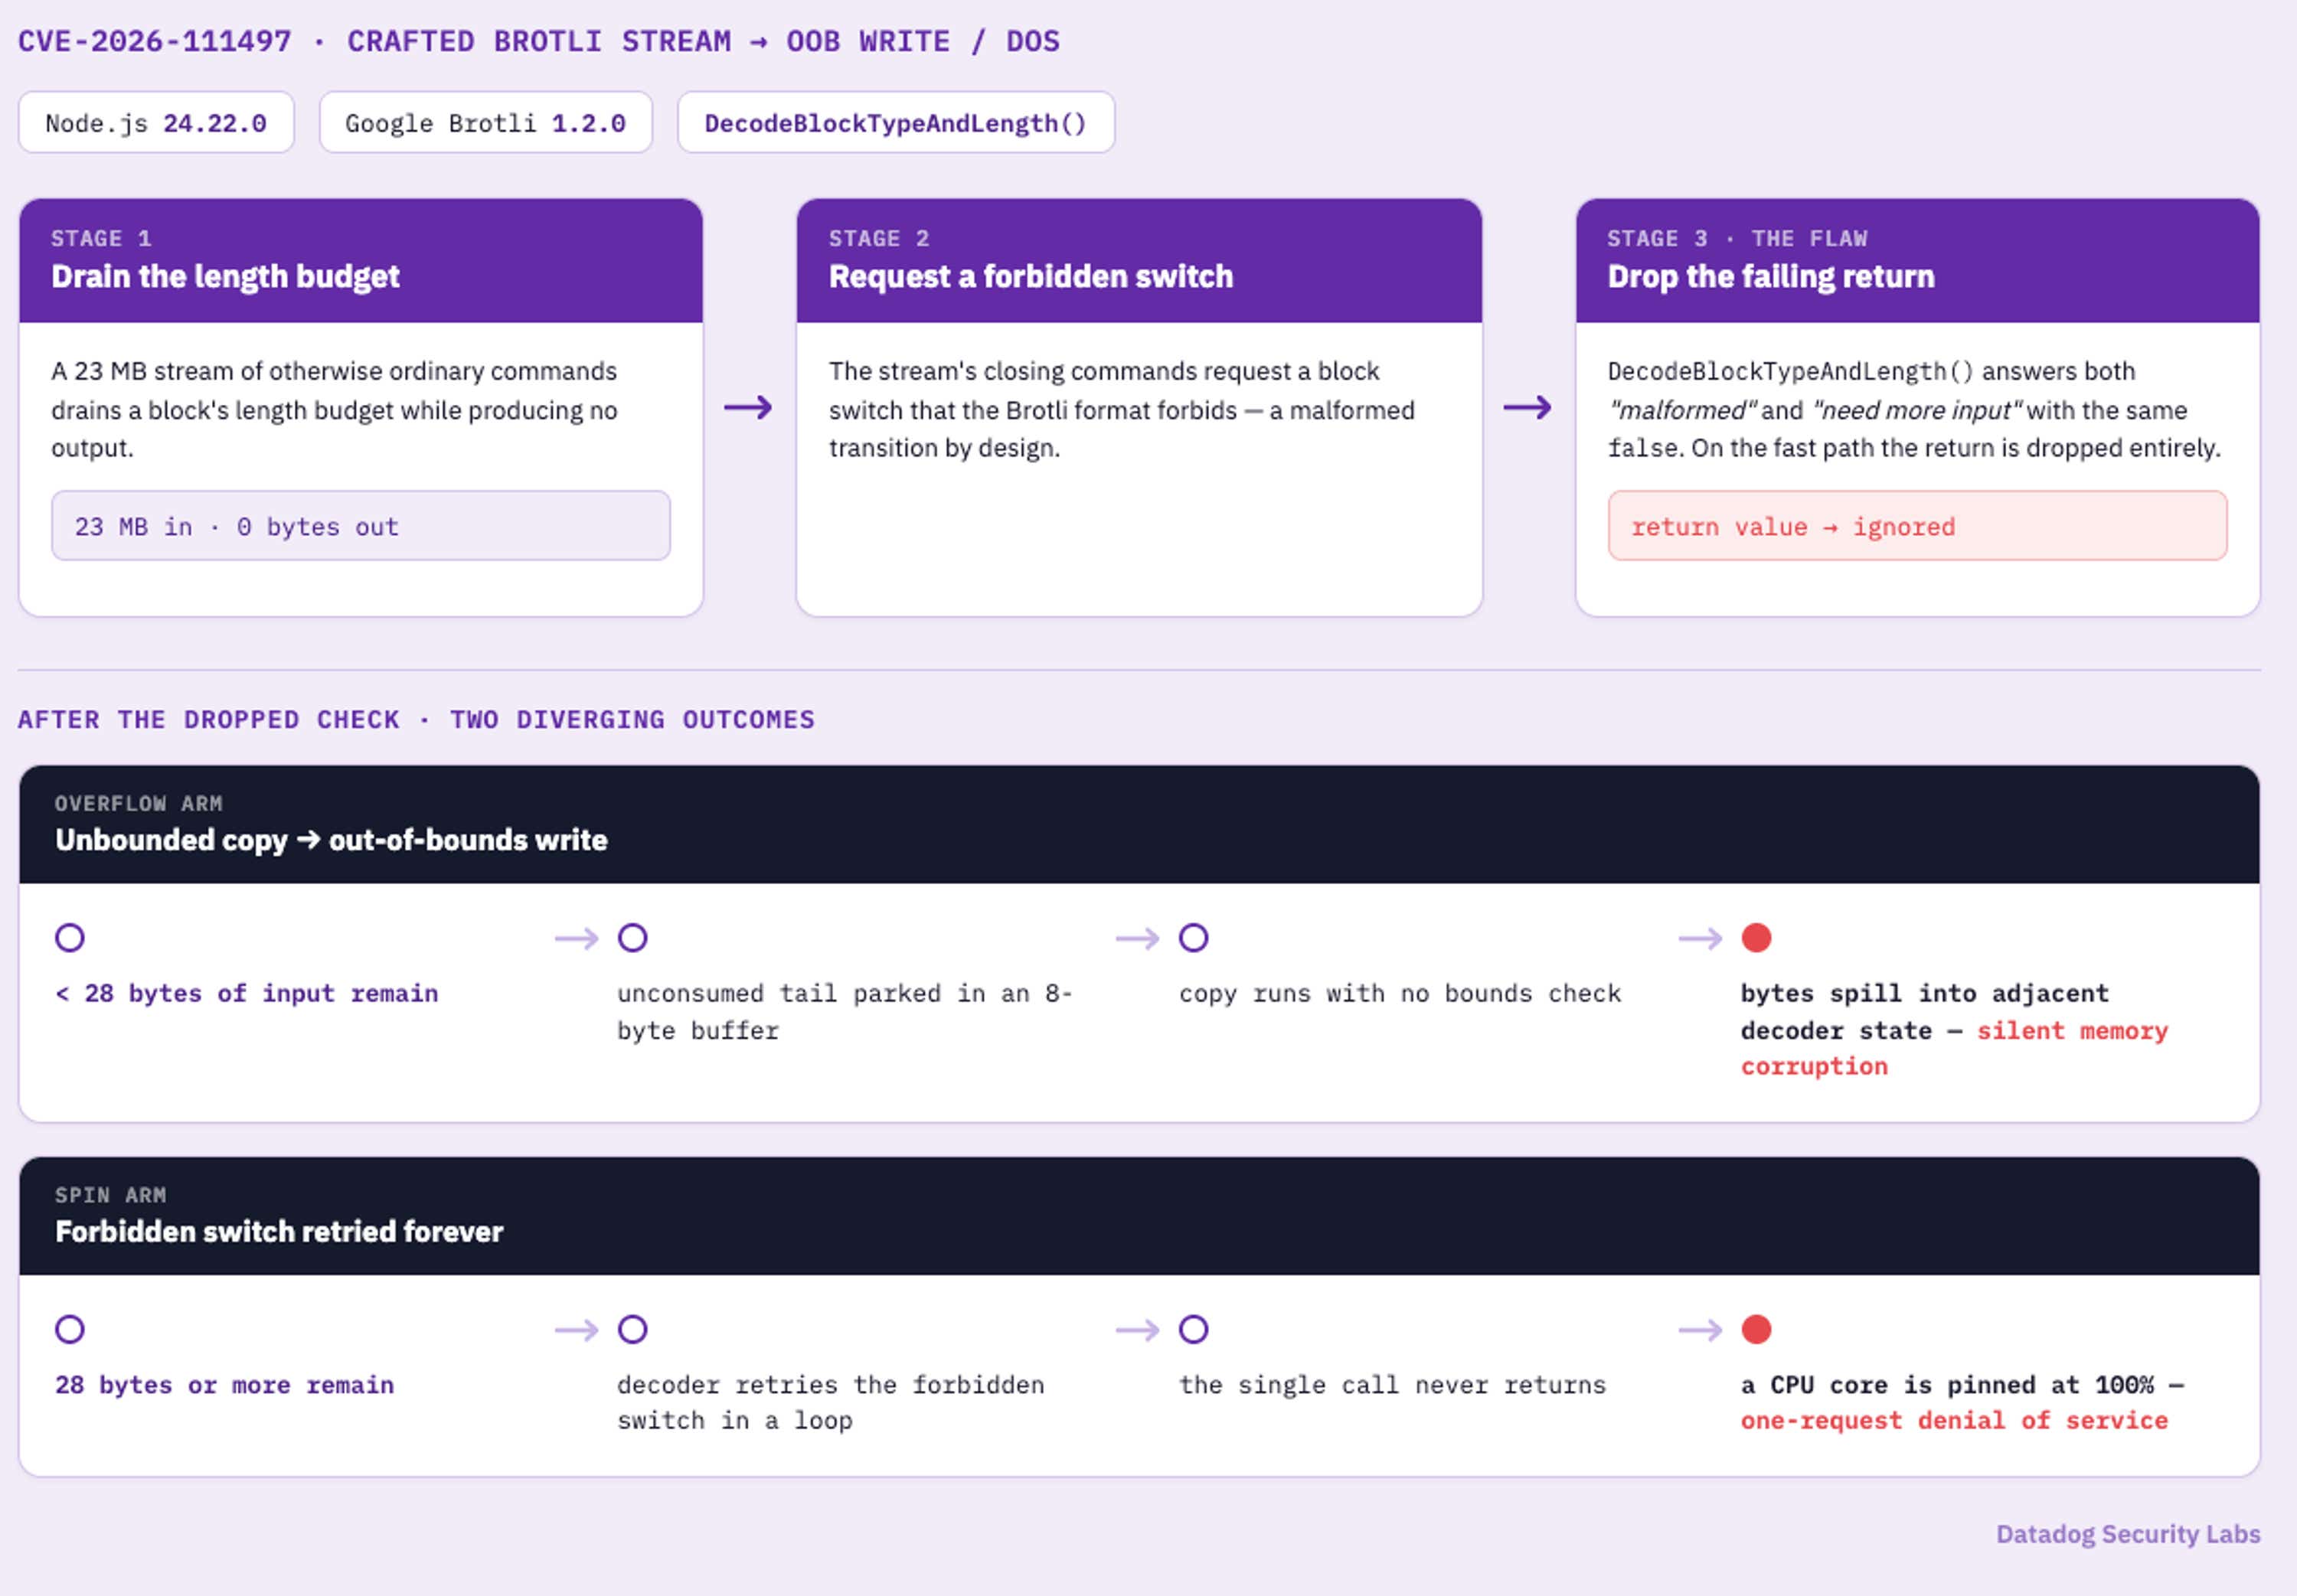
Node2Shell CVE-2026-111497: Brotli Decoder Flaw Affects Multiple Runtimes

Datadog Security Labs reproduces CVE-2026-111497, an out-of-bounds write in Google’s Brotli decoder affecting Node.js and other runtimes. The article details exploitation paths, detection limits, and patches, which it identifies as the only complete fix.

Oct 29, 2026
Threat Research · zimperium.com

Zimperium Analyzes Coruna and DarkSword iOS Exploit Chains

Zimperium’s zLabs analyzed Coruna and DarkSword iOS exploit chains, documenting hidden-frame delivery, version-specific exploits, native capabilities and confirmed exfiltration of Notes data and an app inventory from an iOS 18.6.2 test device.

Oct 29, 2026
Threat Research · cofense.com

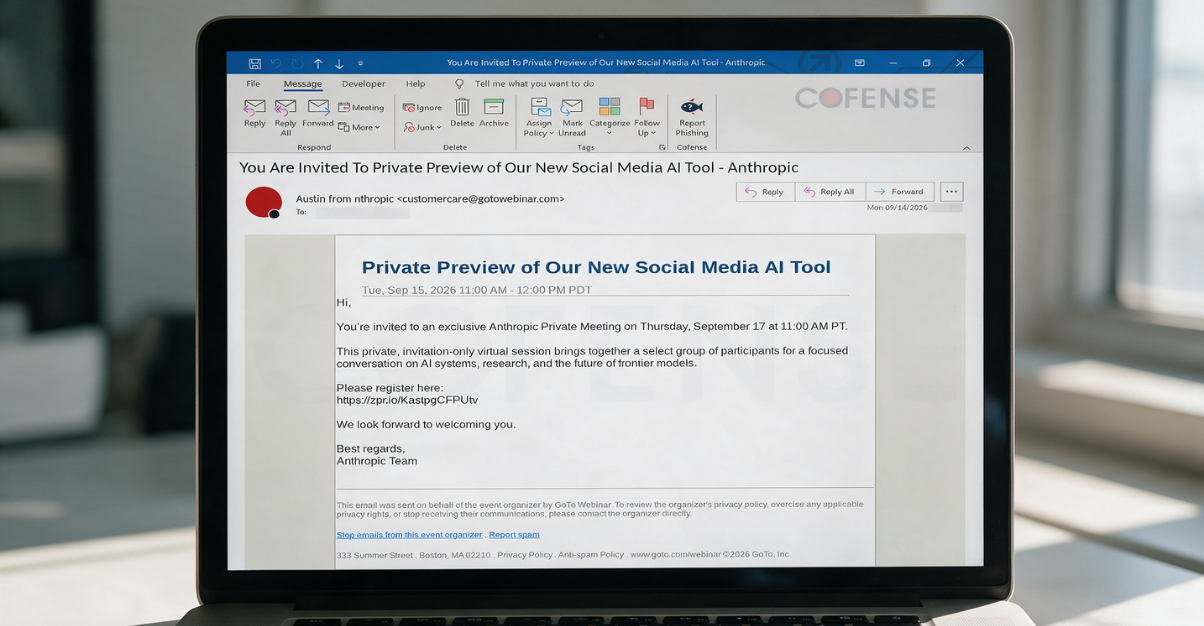
Fake Anthropic AI Preview Emails Target Google and Microsoft Credentials

Cofense describes a phishing campaign using fake Anthropic preview invitations, GoTo Webinar branding, URL shorteners and two CAPTCHAs to reach spoofed Google and Microsoft login pages. The Google page captures usernames; the Microsoft page requests usernames and pas

Oct 29, 2026
Threat Research · security.com

Unauthorized AI Relays Disable Sandboxing in Codex and Claude Code

Symantec reports unauthorized relays reconfiguring genuine Codex and Claude Code CLIs at about a dozen organizations, disabling sandboxing and routing prompts and credentials through third-party servers. No operator abuse was observed, but the setup creates significant,

Oct 29, 2026
Threat Research · cloudsek.com

Fake Adobe and Document-Review Lures Deliver Tenant-Configured ScreenConnect Clients

CloudSEK linked fake document-review pages to genuine, signed ScreenConnect installers configured for unauthorized tenants. The pages profiled visitors and sent details to Telegram; no victim compromise was confirmed.

Oct 29, 2026
PreviousPage 4 of 99 Next
© 2026 cyber.hendryadrian.com