
Yoba Campaign Uses Fake ChatGPT and Claude Apps to Deliver Crypto Miners
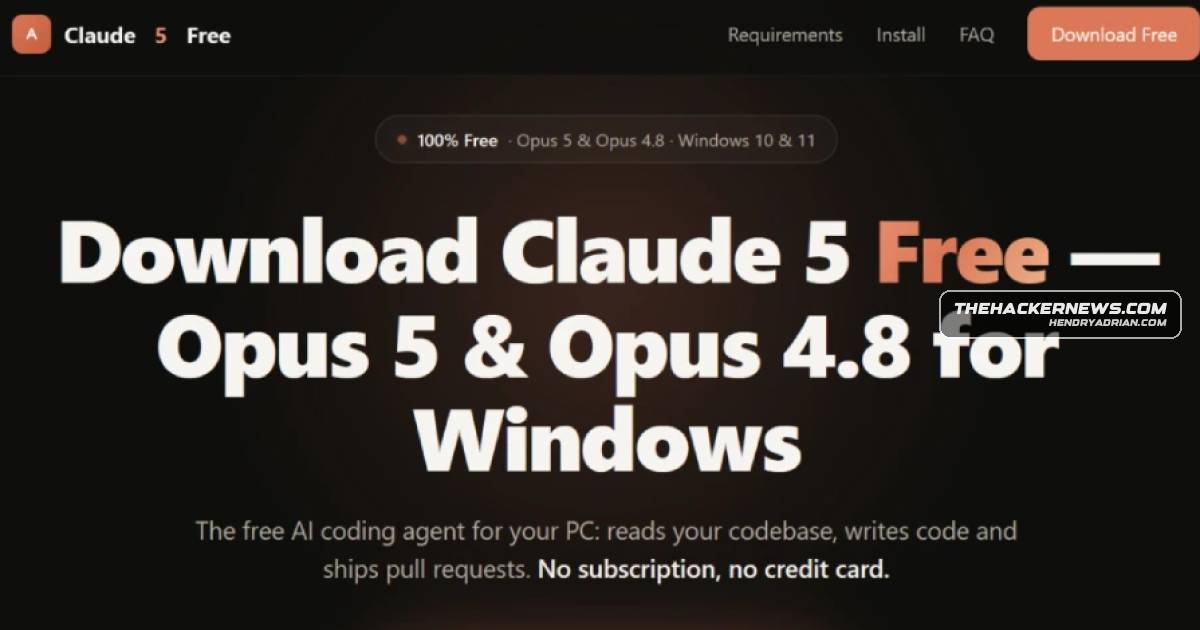
Summary
Check Point describes Yoba, a campaign using fake ChatGPT and Claude desktop-app projects to distribute YobaLoader and XMRig miners, with DLL sideloading, anti-analysis checks, scheduled-task persistence, and payload injection.
Key points
- Attackers used fake GitHub projects posing as ChatGPT and Claude desktop apps to distribute ZIP archives containing Yoba malware.
- YobaDropper sideloads through legitimate executables and checks that its host executable is Setup.exe.
- The malware uses a lengthy sleep routine and excludes systems with specified keyboard layouts; earlier YobaLoader versions also included anti-debugging and anti-VM checks.
- YobaDropper creates a WMProcess directory under ProgramData, extracts a payload, and establishes persistence with a scheduled task.
- YobaLoader checks that it is launched by wmpdmc.exe, then downloads a payload using DoH and file-hosting services and injects it into svchost.exe.
- The injected payload runs an XMRig cryptocurrency miner; Check Point said the first repository appeared around July 2026, with malicious releases uploaded from late August.
Article Details
- Attack Vectors
- Fake GitHub projects and pages impersonated desktop applications for ChatGPT and Claude and hosted ZIP archives containing Yoba malware.
- SEO poisoning was suspected of helping links to the fake projects appear prominently in Google search results.
- YobaDropper and YobaLoader used DLL sideloading alongside legitimate signed executables.
- YobaDropper extracted and decrypted an embedded payload, then established persistence with a scheduled task.
- YobaLoader used DNS-over-HTTPS and file-hosting platforms for command-and-control and payload delivery.
- The downloaded payload was injected into svchost.exe and executed an XMRig cryptocurrency miner.
- The malware used long sleep delays, executable-hash checks, and language or keyboard-layout exclusions to evade analysis or limit infection.
MITRE ATT&CK
T1053.005 · Scheduled TaskYobaDropper establishes persistence with a scheduled task that launches a legitimate executable to load the malicious payload.T1055 · Process InjectionThe downloaded payload is injected into svchost.exe.T1071.004 · DNSThe campaign uses a DNS-over-HTTPS service for command-and-control traffic.T1105 · Ingress Tool TransferYobaLoader downloads a payload using DoH and file-hosting platforms.T1140 · Deobfuscate/Decode Files or InformationYobaDropper extracts and decrypts an embedded payload.T1496 · Resource HijackingThe injected payload executes an XMRig cryptocurrency miner.T1497.003 · Time Based ChecksThe dropper and loader use 200,000 Sleep(5500) iterations, amounting to about 12.73 days, as an anti-analysis delay.T1574.002 · DLL Side-LoadingYobaDropper and YobaLoader use DLL sideloading alongside legitimate signed executables.T1608.006 · SEO PoisoningCheck Point Research said signs point to SEO poisoning to elevate links to the fake GitHub projects in Google search results.T1614.001 · System Language DiscoveryThe malware checks keyboard layout and language identifiers and skips machines associated with specified countries and Tatar.
Malware
XMRigThe downloaded payload is then injected into "svchost.exe," resulting in the execution of an XMRig cryptocurrency miner.YobaDropperThe DLL is a dropper codenamed YobaDropper, which implements checksum value checks by hashing the basename of its host executable and if it matches a hard-coded value "0xE6C2F326." In other words, the check requires itYobaLoaderThe activity involves creating fake GitHub projects that claim to be desktop applications like GPT-5.6 Sol, GPT-6 Astra, and Claude Opus, only to deliver a malware family called YobaLoader.
Vendors
AnthropicThreat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba.OpenAIThreat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba.
Products
ChatGPTThreat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba.ClaudeThreat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba.GitHubThe activity involves creating fake GitHub projects that claim to be desktop applications like GPT-5.6 Sol, GPT-6 Astra, and Claude Opus, only to deliver a malware family called YobaLoader.
Countries
Armeniadays, and skipping machines whose keyboard layout corresponds to that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.Azerbaijanskipping machines whose keyboard layout corresponds to that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.Belaruswhich amounts to 12.73 days, and skipping machines whose keyboard layout corresponds to that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.Georgiamachines whose keyboard layout corresponds to that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.Kazakhstanwhose keyboard layout corresponds to that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.Kyrgyzstanlayout corresponds to that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.Russiawhich amounts to 12.73 days, and skipping machines whose keyboard layout corresponds to that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.Tajikistanto 12.73 days, and skipping machines whose keyboard layout corresponds to that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.Turkmenistanto that of Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.UkraineAnother language ID excluded from the infection process is Tatar. Notably missing from the list is Ukraine, which used to be historically included in such checks.Uzbekistanof Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan.