
Fake Anthropic AI Preview Emails Target Google and Microsoft Credentials
Summary
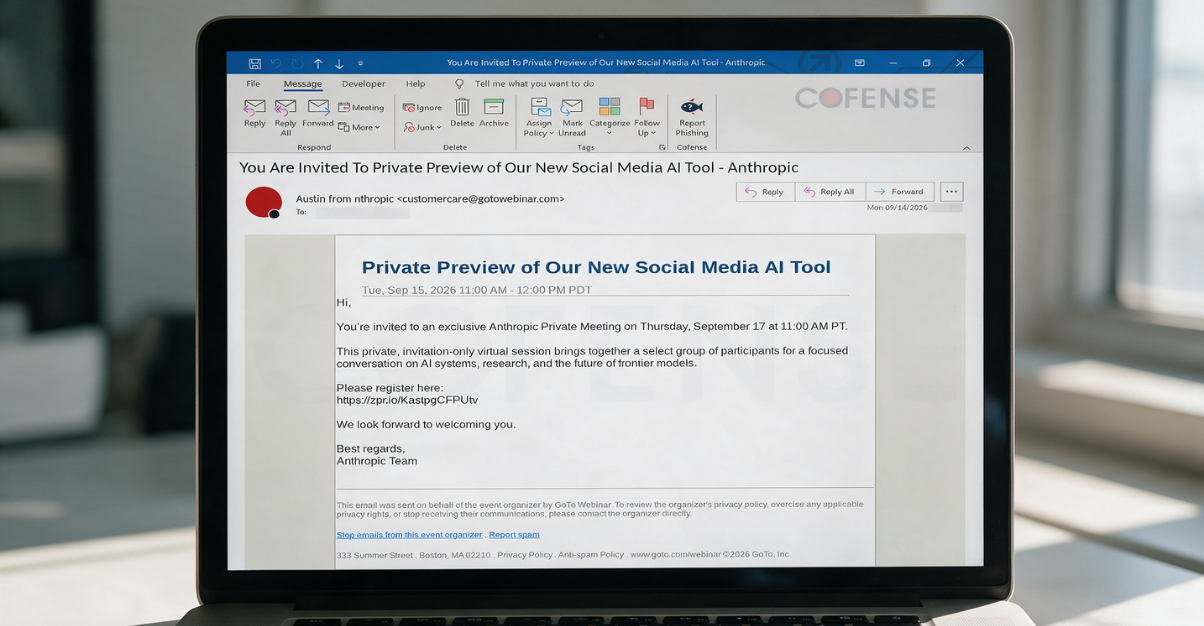
Cofense describes a phishing campaign using fake Anthropic preview invitations, GoTo Webinar branding, URL shorteners and two CAPTCHAs to reach spoofed Google and Microsoft login pages. The Google page captures usernames; the Microsoft page requests usernames and pas
Key points
- Cofense reports that the campaign, observed since September 2026, uses invitations to a fake private Anthropic AI preview as a phishing lure.
- The emails appear to abuse GoTo Webinar, while shortened links—including zpr[.]io—help route recipients toward phishing pages.
- Two CAPTCHA checkpoints, including a custom slider CAPTCHA, obstruct automated analysis before recipients reach the credential pages.
- The campaign presents a Zoom-spoofing registration page; Cofense notes that its Zoom branding conflicts with the GoTo Webinar-branded email.
- The Google-themed page captures usernames only, while the Microsoft-themed page requests usernames and passwords. Cofense says the Microsoft page sends submitted credentials to the threat actor.
- Lookalike domains such as goo[.]gle-access-eventregister[.]icu and office[.]com-access-sharepoint[.]com are used to imitate legitimate login destinations.
- Cofense recommends checking branding consistency and login-page domains, and describes using human-vetted threat intelligence alongside automated defenses.
Article Details
- Attack Vectors
- Phishing emails lured recipients with an invitation to a private Anthropic AI preview and linked to credential-phishing pages.
- The campaign abused GoTo Webinar and a URL-shortening service to deliver or obscure the phishing link.
- Two CAPTCHA checkpoints hindered automated analysis before displaying fake meeting and login pages.
- Fake Google and Microsoft login pages captured usernames; the Microsoft page also captured passwords.
- Defensive Notes
- Check that branding remains consistent from an invitation email through the meeting and login pages.
- Verify both the URL and domain before entering credentials, including after redirects.
- Use human-vetted threat intelligence to add context to automated detections.
- Cofense recommends Cofense Vision to cluster structurally related messages despite changes to senders, subjects, URLs, and page elements.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | goo[.]gle-access-eventregister[.]icu | Domain hosting the fake Google credential-phishing page, which captures usernames. |
| DOMAIN | office[.]com-access-sharepoint[.]com | Domain hosting the fake Microsoft credential-phishing page, which captures usernames and passwords. |
| DOMAIN | us968web-zoom[.]us | Malicious domain used for the Zoom-spoofing meeting page in the phishing flow. |
MITRE ATT&CK
T1036.005 · Match Legitimate Resource Name or LocationPhishing domains used Zoom, Google, and Microsoft-related naming to resemble legitimate meeting or login services.T1056.003 · Web Portal CaptureFake Google and Microsoft login pages collected credentials; the Google page captured usernames, while the Microsoft page captured usernames and passwords.T1566.002 · Spearphishing LinkThe campaign sent invitation emails containing links that led recipients through a phishing flow.
Vendors
AnthropicWould Your Employees Join a Fake Anthropic AI Preview?CloudflareFigure 2: Cloudflare CAPTCHA page to hinder automated analysis (ATR 423868).CofenseCofense Intelligence consolidates campaign data, including indicators of compromise (IOCs) such as malicious web addresses, phishing email content, and broader campaign context, into Active Threat Reports (ATRs),Googlethat appear to be an invitation to a private Anthropic AI meeting, but are actually attempts to steal Google and Microsoft login credentials. Exclusive access to new AI technology is valuable to many organizations,GoTo WebinarThe video teleconference software GoTo Webinar, which is used to send legitimate meeting emails and is usually not blocked by email security technologies, was abused to send a threat actor’s URL instead.Microsoftto be an invitation to a private Anthropic AI meeting, but are actually attempts to steal Google and Microsoft login credentials. Exclusive access to new AI technology is valuable to many organizations, which is whyZapierThe link in the email appears to be generated by Zapier’s URL shortener service. Zapier is a legitimate business process automation company, and their URL Shortener is designed to work with Claude, ChatGPT, and otherZoomFigure 3: Zoom-spoofing page with Anthropic meeting information (ATR 423475).
Products
Anthropic AIWould Your Employees Join a Fake Anthropic AI Preview?Cloudflare CAPTCHAFigure 2: Cloudflare CAPTCHA page to hinder automated analysis (ATR 423868).Cofense VisionUse Cofense Vision. Vision AI can cluster structurally related messages even when threat actors rotate senders, subjects, URLs, and page elements.GoTo WebinarThe video teleconference software GoTo Webinar, which is used to send legitimate meeting emails and is usually not blocked by email security technologies, was abused to send a threat actor’s URL instead.URL ShortenerThe URL shortener zpr[.]io, which turns long URLs into short links, has been abused to help these phishing emails bypass current email security technologies. ZoomFigure 3: Zoom-spoofing page with Anthropic meeting information (ATR 423475).