cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2377 articles

Threat Research · thehackernews.com

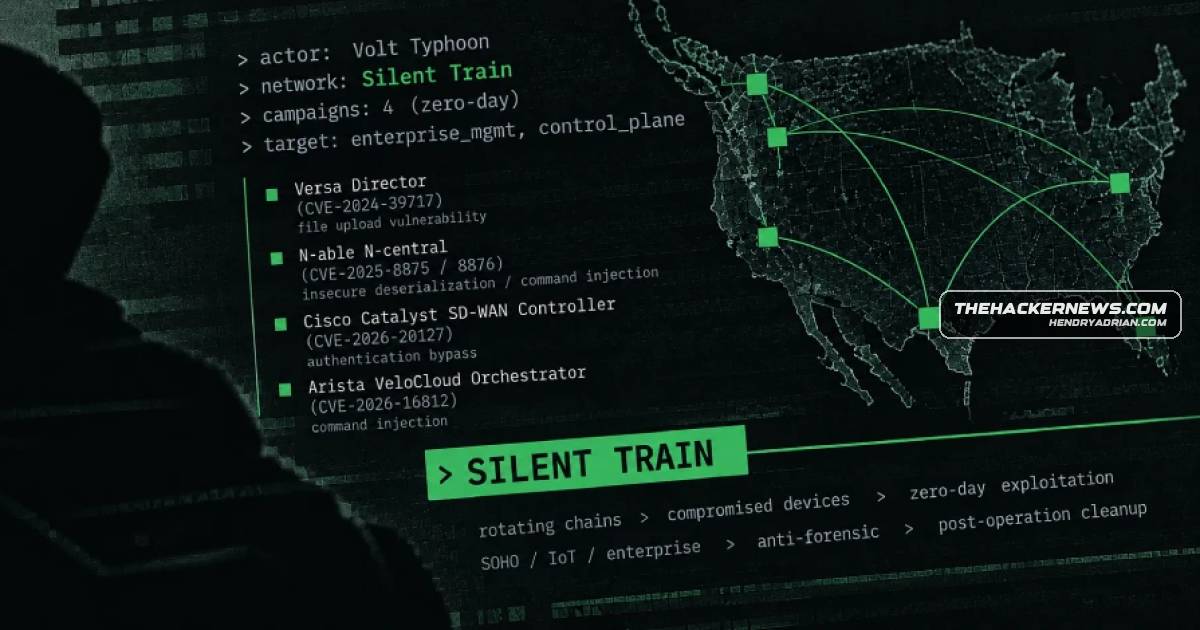
Black Lotus Labs Links Volt Typhoon to Silent Train Network Used in Zero-Day Campaigns

Lumen’s Black Lotus Labs links Volt Typhoon to Silent Train, a covert network of compromised devices used for four reported zero-day campaigns. The report describes its rotating relay chains, operational methods and evolution.

Oct 28, 2026
Threat Research · infostealers.com

Analysis of Purported Wagyu Data Finds Crypto Orders Linked to Monero and IPs

Hudson Rock analyzed purported Wagyu[.]xyz data associated with a WhiteArmor claim, finding records linking crypto deposits, Monero destinations and IP/session metadata. The files' origin is unverified and they do not by themselves identify users or show Monero was able

Oct 28, 2026
Threat Research · thehackernews.com

Researcher Details Microsoft Edge Sandbox Escape Built from Logic Flaws

Orange Tsai detailed a non-memory-corruption chain using Edge logic flaws to achieve UXSS, escape the sandbox and execute code on Windows. Demonstrated at Pwn2Own Berlin, it was patched in Edge 148.0.3967.70; there is no evidence it was used against real users.

Oct 28, 2026
Threat Research · dti.domaintools.com

DomainTools Assesses MrHex as Handala-Aligned, Cites Evidence of Industrial HMI Access

DomainTools assesses MrHex as an Iran-aligned hack-and-leak network connected to Handala. Shared infrastructure and actor promotion link its data sites; video supports access to an industrial HMI, but claims of physical damage remain unverified.

Oct 28, 2026
Threat Research · securityweek.com

Dream Reports China-Nexus Hackers Used PHP2Shell to Root Firewalls

Dream reports an unattributed China-nexus operation chained PHP2Shell and Fragnesia to root firewalls, then accessed a management server to obtain firewall configurations and credentials and target Active Directory.

Oct 28, 2026
Threat Research · securelist.com

Unauthenticated Intelbras Camera Firmware Endpoint Enables Denial of Service

Researchers found an unauthenticated firmware-update endpoint in Intelbras IP cameras that can reboot devices offline; periodic requests can sustain the denial of service. Intelbras fixed it in firmware R.260804.

Oct 28, 2026
Threat Research · reliaquest.com

Residential Proxies Help Social Engineers Evade Location-Based Sign-In Checks

ReliaQuest says attackers use victim-matched residential proxies to make socially engineered logins and device registrations appear local, then rapidly access SaaS data through built-in APIs. It recommends phishing-resistant MFA and managed-device controls.

Oct 28, 2026
Threat Research · socradar.io

SOCRadar Details n0n’s AI-Assisted Ransomware Operation

SOCRadar says an exposed workspace linked n0n to 23 organizations, including access attempts, and revealed credential-based intrusions, data theft and destruction tooling, and AI-assisted scripting. The analysis includes technical findings and defenses; some claims are未

Oct 28, 2026
Threat Research · thehackernews.com

Researchers Say ShinyHunters-Exploited PeopleSoft Zero-Day Chains Three Flaws

ZDI says three PeopleSoft flaws were patched under CVE-2026-35273. Mandiant and GTIG attribute exploitation to ShinyHunters; the article details the SSRF-to-RCE chain and warns patching may not remove attackers already inside.

Oct 28, 2026
Threat Research · cyble.com

INJ3CTOR3 Campaign Adds Credential Theft to FreePBX Toll-Fraud Implant

Cyble reports that September 2026 INJ3CTOR3 builds of the JOMANGY FreePBX implant upload 17 configuration files to two staging hosts, exposing SIP, AMI, database and mail credentials; it details detection and cleanup steps.

Oct 28, 2026
Threat Research · cyfirma.com

CYFIRMA Profiles Star Blizzard’s RedFlick Campaigns and Evolving Tradecraft

CYFIRMA profiles Star Blizzard's 2023–2026 espionage activity, detailing RedFlick delivery, malware and phishing, with hunting queries and mitigations. Microsoft reported at least 13 campaigns against 100+ organizations since January 2026; its broader-targeting assess

Oct 28, 2026
Threat Research · crowdstrike.com

CrowdStrike Researchers Use AI Guardrail Signals to Locate Vulnerabilities

CrowdStrike researchers describe Guardrail-based Vulnerability Discovery, which uses changes in AI model responses to localize flaws. They report correct results in 73 of 86 test scenarios and similar findings in open-source projects.

Oct 28, 2026
Threat Research · bleepingcomputer.com

Volt Typhoon Uses ‘Silent Train’ Relay Framework in Zero-Day Attacks

Black Lotus Labs reports that Volt Typhoon has used Silent Train for three years, chaining compromised devices as relays and exploiting at least four zero-days against edge and management systems.

Oct 28, 2026
Threat Research · cloudsek.com

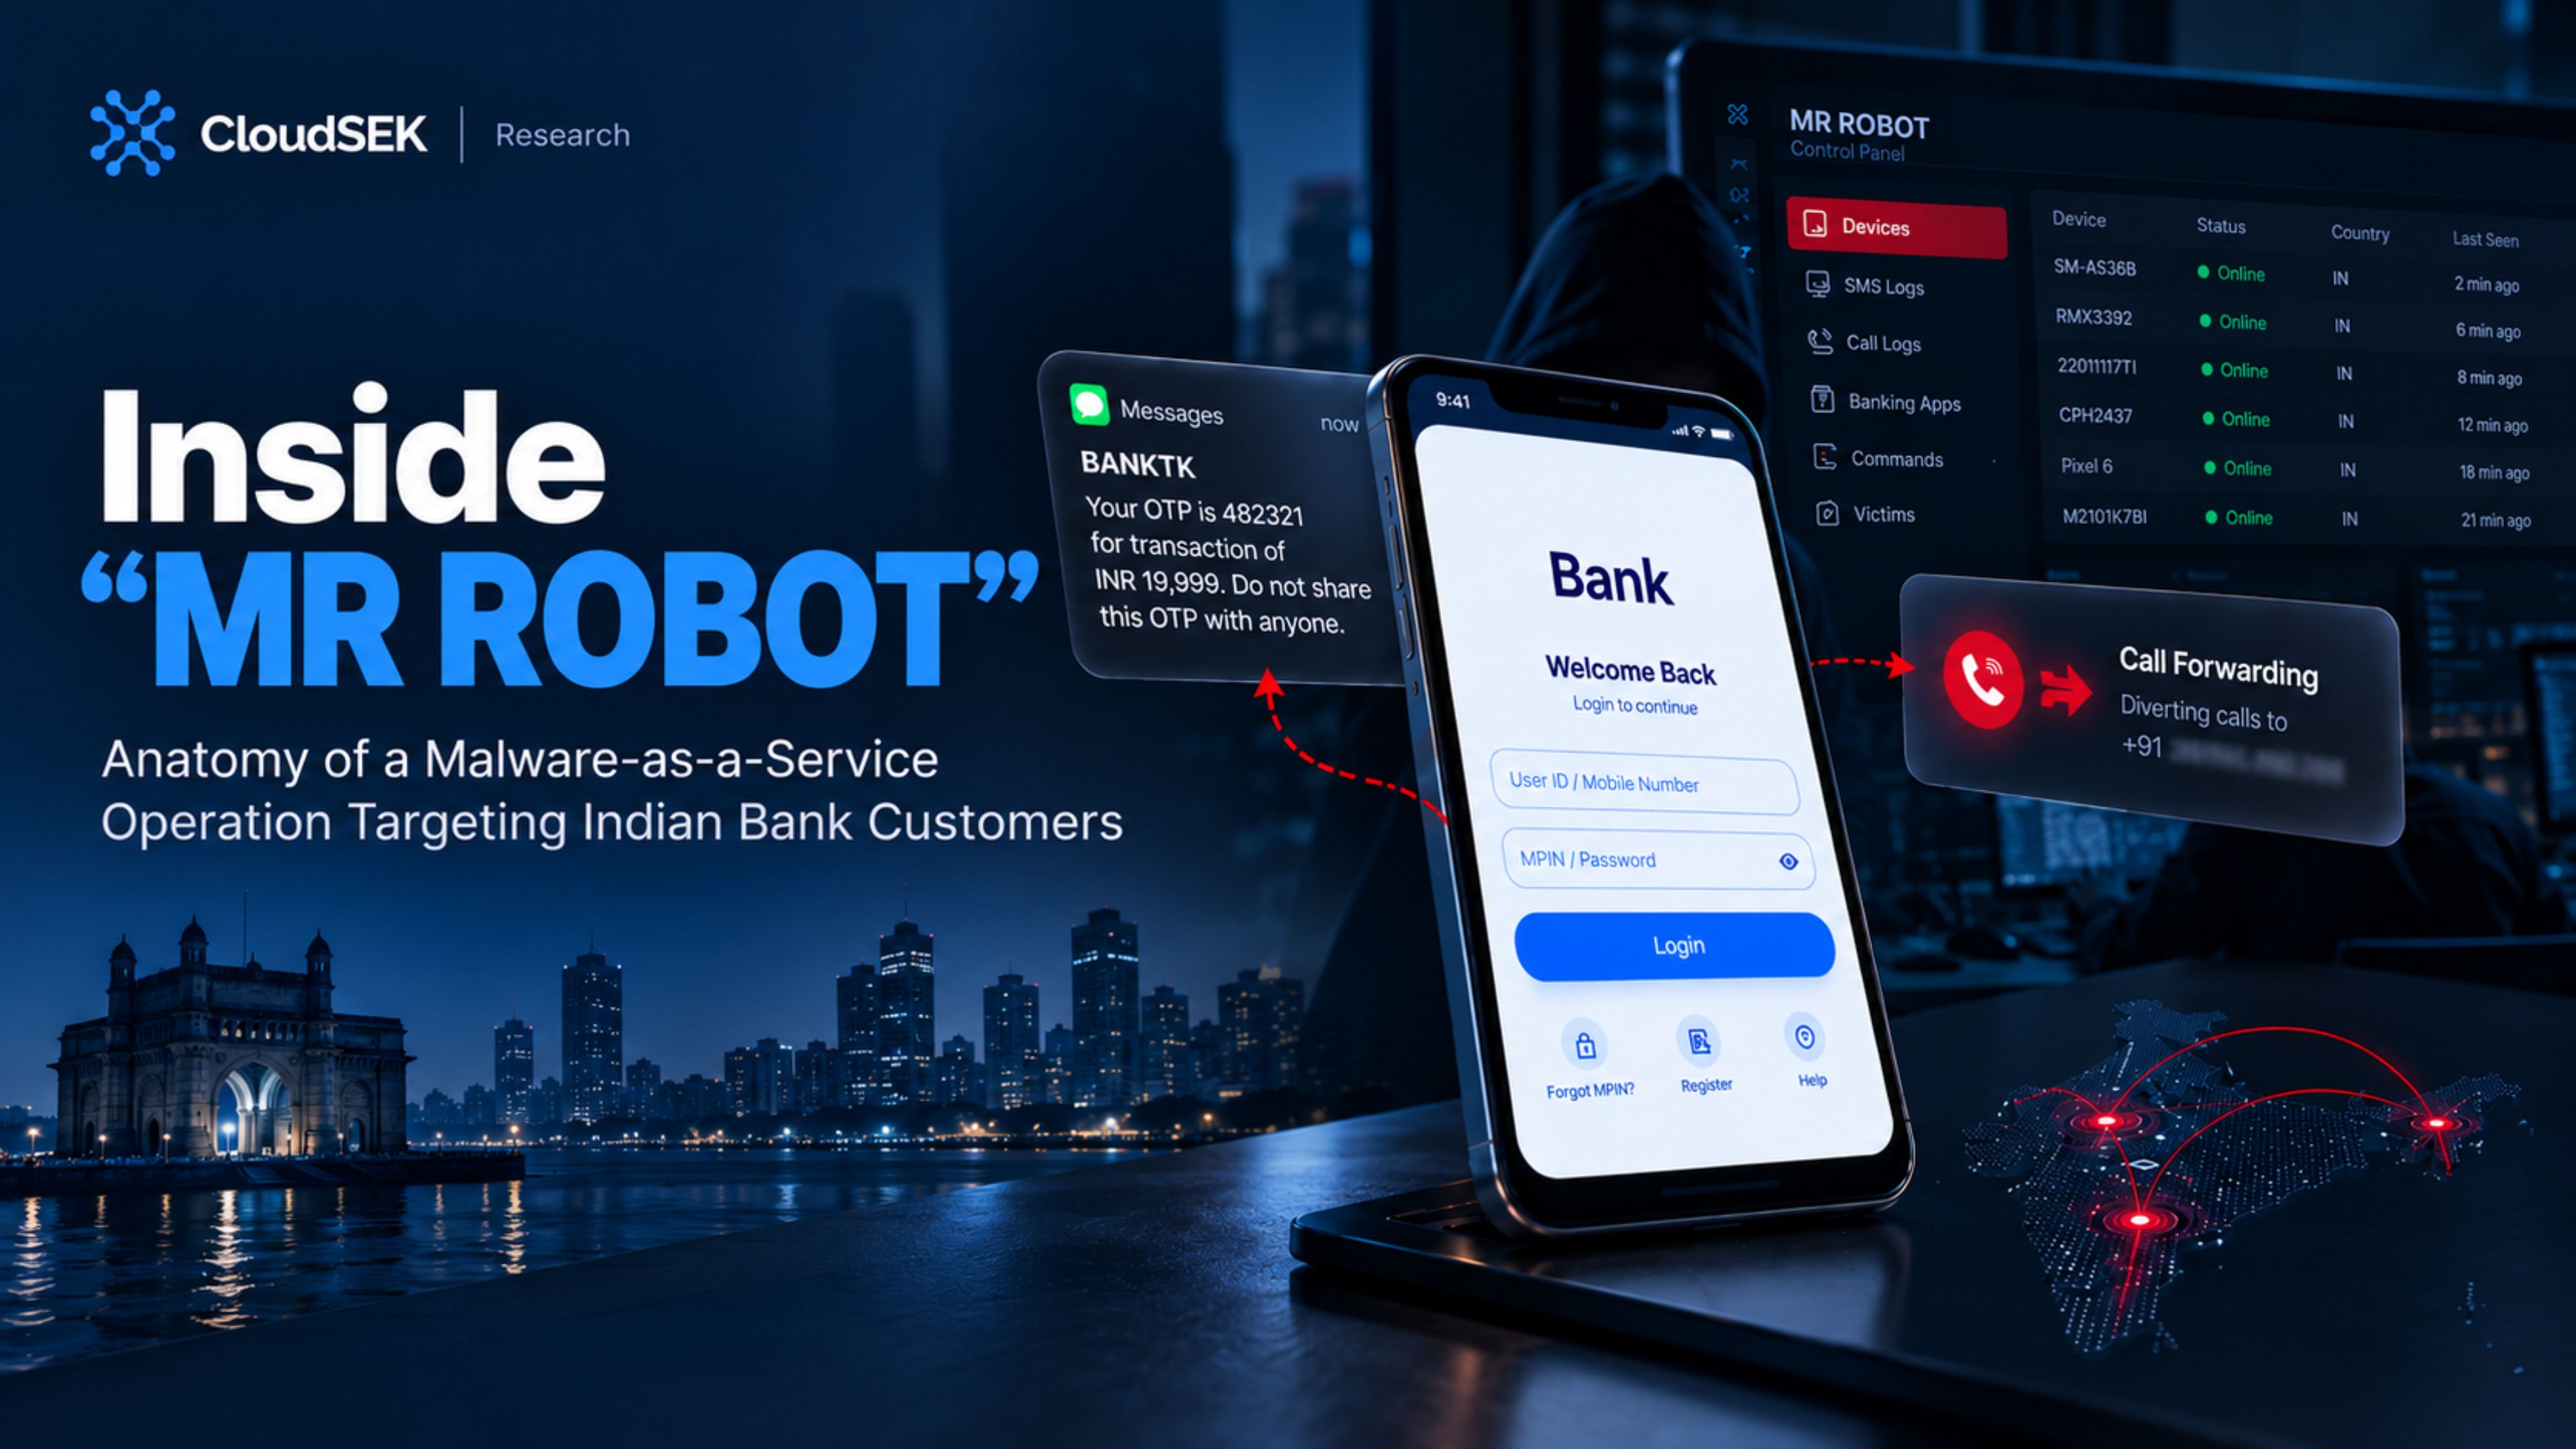
MR ROBOT Android MaaS Uses SMS Theft and Call Forwarding to Target Indian Bank Customers

CloudSek traces MR ROBOT, an Android MaaS operation targeting Indian bank customers, and details its custom trojans, SMS/OTP and credential theft, silent call forwarding, Firebase/Telegram exfiltration, and affiliate control panel.

Oct 28, 2026
Threat Research · cloudsek.com

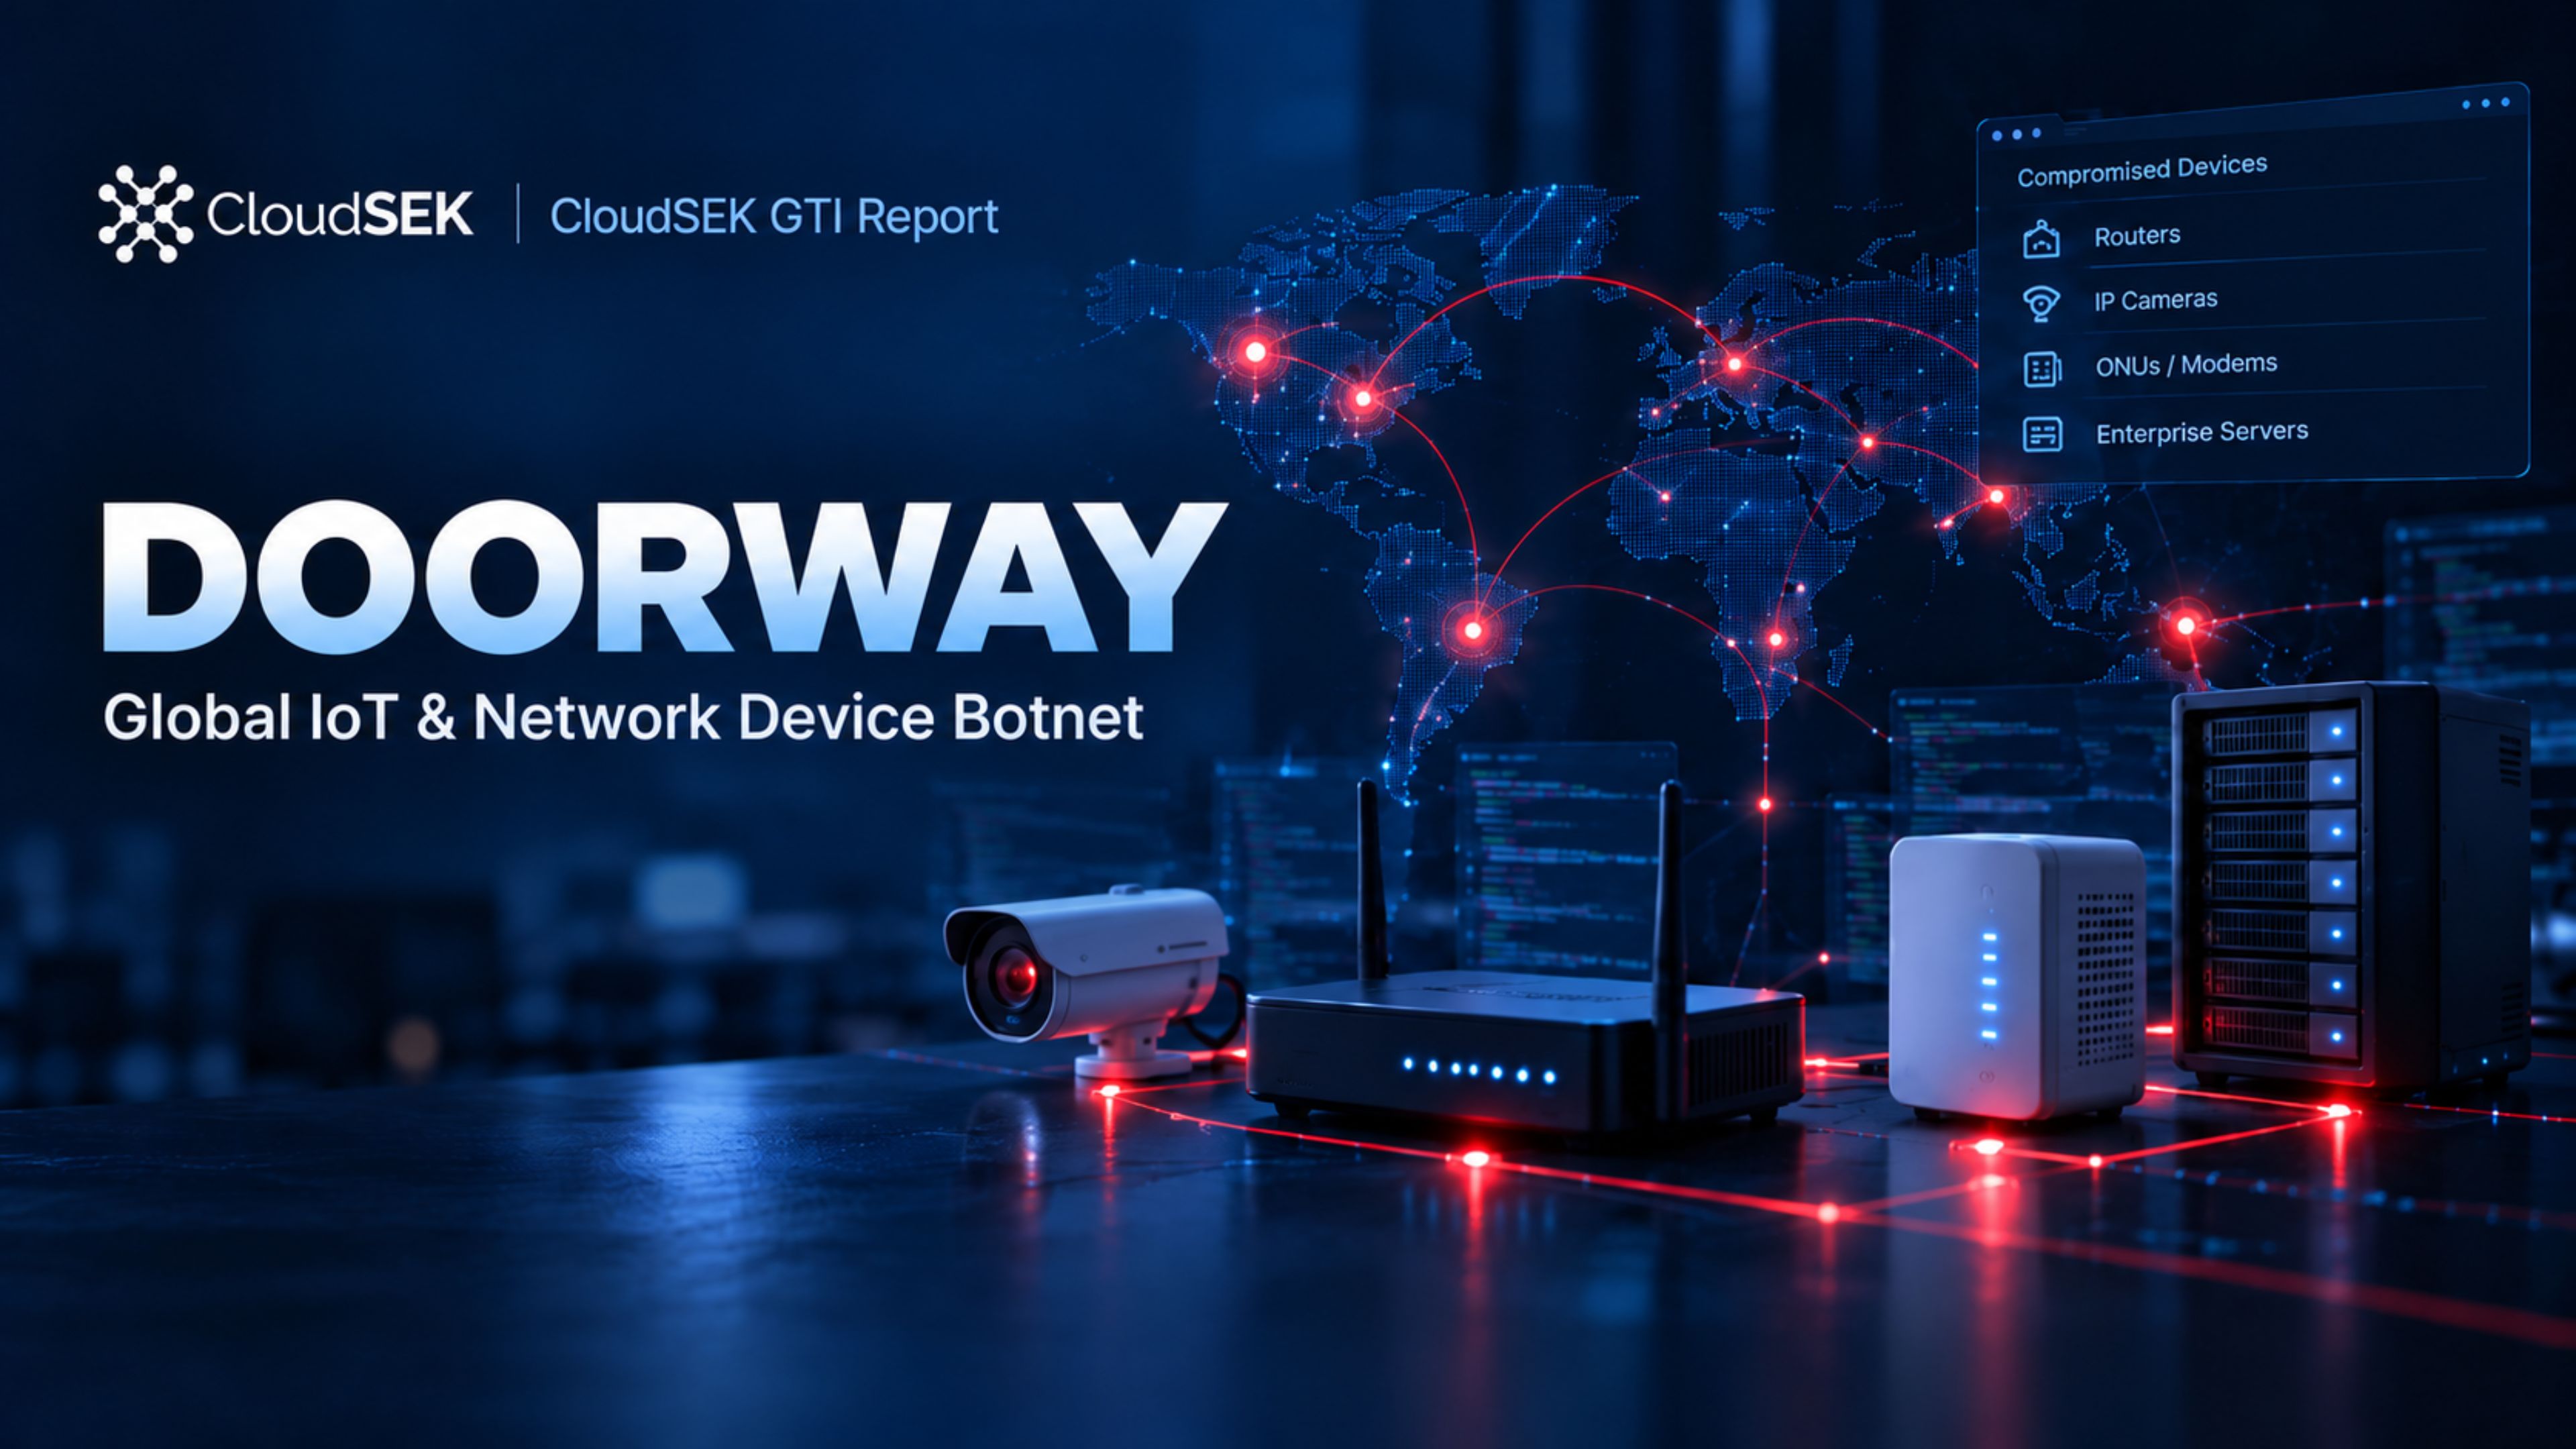
CloudSEK Investigates Doorway Botnet Targeting IoT Devices and Servers

CloudSEK analyzed exposed Doorway workspaces, finding a Rust exploitation engine, staged loaders and evidence of compromised devices and Java services. The final clients' capabilities and large-scale RouterOS reverse-shell deployment remain unconfirmed.

Oct 28, 2026
Threat Research · hunt.io

Exposed Staging Server Reveals Transfer of Philippine Agency-Linked Backups and GodPotato Tooling

Hunt.io found logs showing a 68.837 GiB transfer of backups named for Philippine overseas-employment systems. An exposed server also held a rebranded GodPotato payload; the backup source and payload execution remain unconfirmed.

Oct 28, 2026
Threat Research · huntress.com

Attackers Abuse MDM Platforms to Deploy Remote-Access Tools

Huntress describes two incidents in which phishing or a deceptive link led to unauthorized Hexnode or Rippling MDM enrollment, letting attackers install ScreenConnect and restore remote access after removal.

Oct 28, 2026
Threat Research · acronis.com

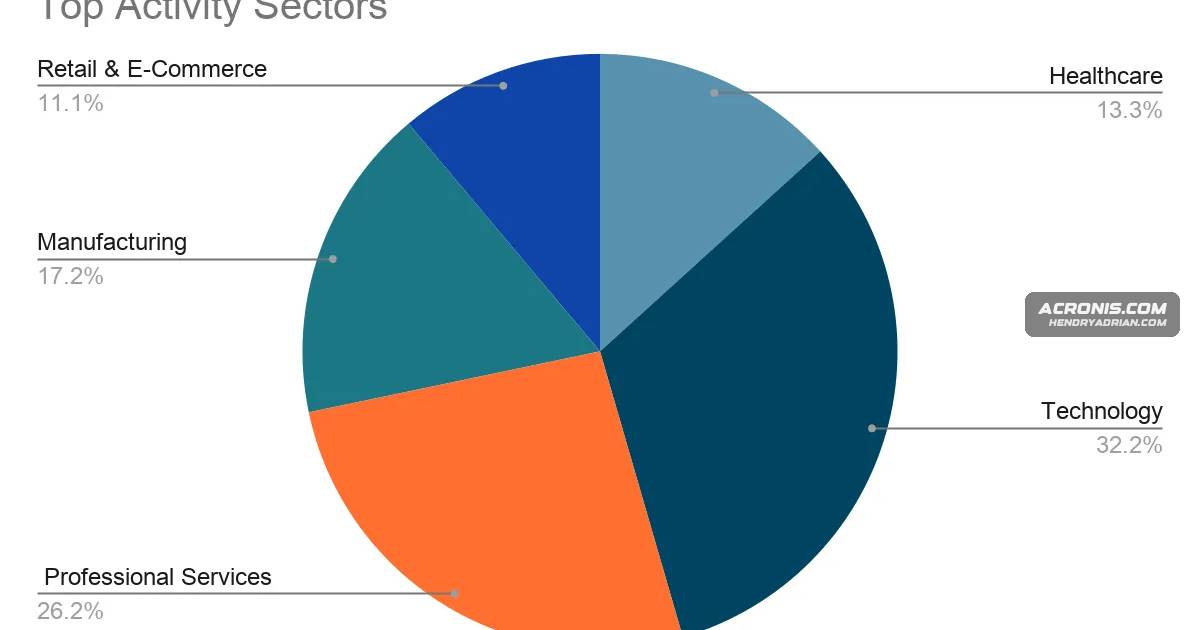
Acronis Analyzes Qilin Ransomware’s Windows and ESXi Capabilities

Acronis analyzes Qilin/Agenda’s affiliate operation and ransomware sample, detailing Windows and ESXi targeting, access methods, configurable encryption, double extortion and defensive recommendations.

Oct 28, 2026
Threat Research · socket.dev

Malicious Firefox Extensions Impersonate Crypto Wallets to Steal Recovery Phrases and Private Keys

Socket researchers analyzed three malicious Firefox add-ons impersonating Phantom, Jupiter and Bitget that steal wallet recovery phrases and private keys; the Phantom variant also fetches and executes a remote payload. The listings were removed by publication.

Oct 27, 2026
Threat Research · rogueauthority.org

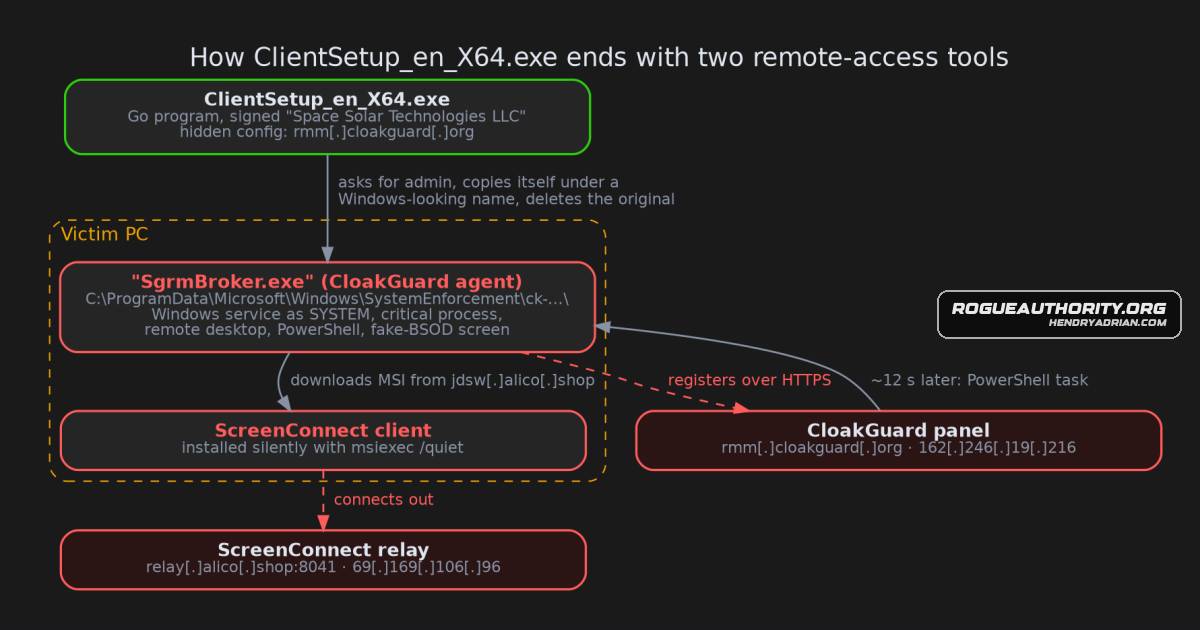
CloakGuard Malware Uses Fake Blue Screens to Hide Remote Access

Analysis of the signed Go-based CloakGuard agent found it disguises itself as a Windows service, can disable Defender, hides operator activity behind fake crash or update screens, and installed ScreenConnect in a sandbox.

Oct 27, 2026
Threat Research · wiz.io

Wiz Details Failed PHP2Shell Exploit Attempts and Falling Exposure

Wiz observed PHP2Shell attempts that triggered memory exhaustion but did not complete the exploit chain in its telemetry. Exposed vulnerable machines fell about 67% after disclosure, though the vulnerabilities remain a risk.

Oct 27, 2026
Threat Research · research.checkpoint.com

Yoba Campaign Abuses Fake AI Apps and Signed Binaries to Deliver XMRig

Check Point Research details Yoba, a campaign using fake ChatGPT and Claude GitHub apps and signed binaries for DLL sideloading. Its loader uses Telegram-seeded domain generation and DNS-over-HTTPS to fetch payloads, including an XMRig miner.

Oct 27, 2026
Threat Research · infostealers.com

FortiBleed 2.0 Analysis Finds 40,573 Cleartext Secrets in FortiGate Configuration Records

Hudson Rock's FortiBleed 2.0 analysis of 1,703 configuration reports found 40,573 cleartext secret records and 975 domain labels absent from its FortiBleed 1.0 comparison. The records do not establish successful internal compromise or current access.

Oct 27, 2026
Threat Research · socradar.io

SOCRadar Finds PHP2Shell Tools Added After Japanese Real Estate Extortion Campaign

SOCRadar found an exposed operator server containing evidence of an October 2026 extortion campaign affecting nearly 20 Japanese sites and stolen customer data. PHP2Shell tools appeared after the campaign; the files showed no successful live exploitation.

Oct 27, 2026
PreviousPage 5 of 100 Next
© 2026 cyber.hendryadrian.com