Huntress Tracks Ongoing Microsoft 365 Device-Code Phishing via BL Networks
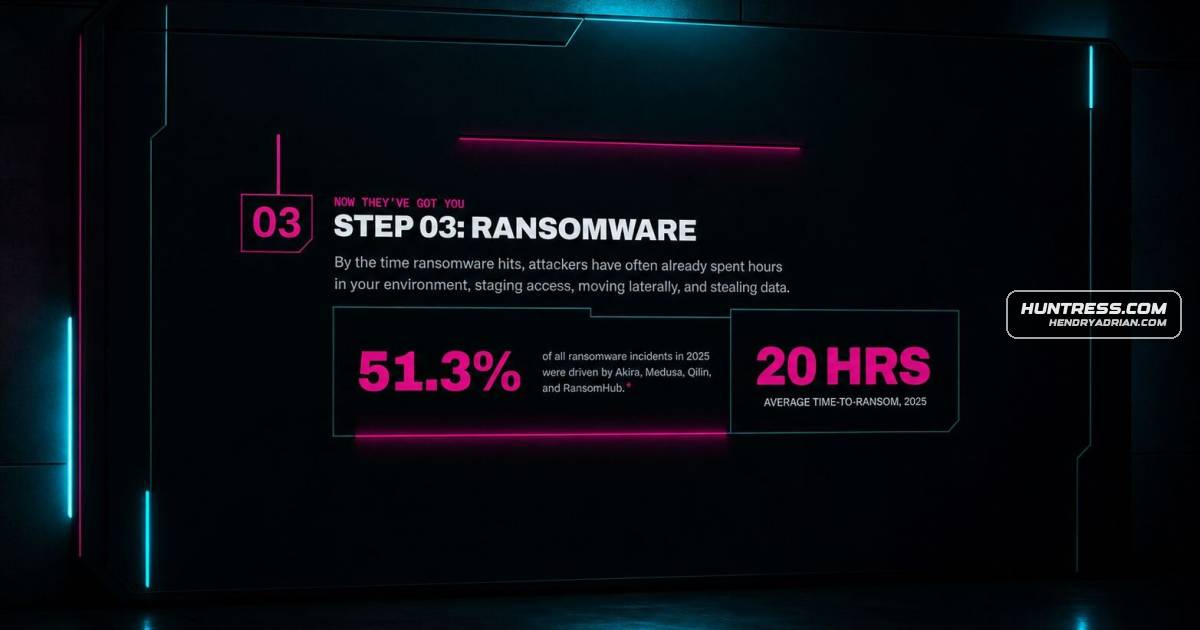
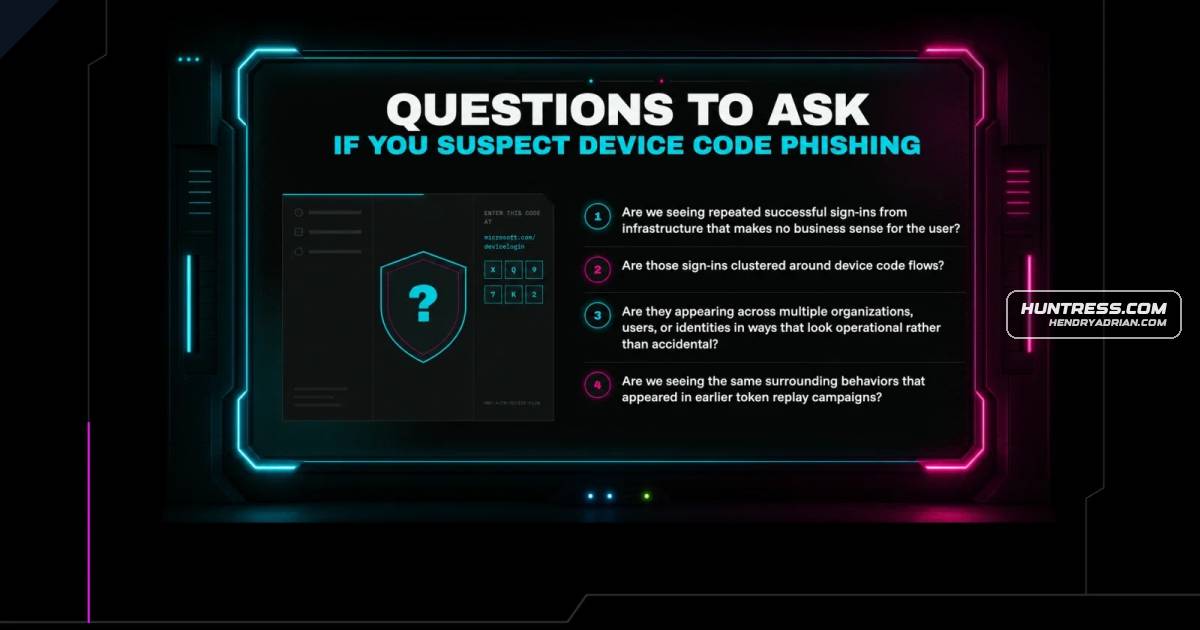
Huntress reports a continuing 2026 Microsoft 365 device-code phishing wave using BL Networks infrastructure to abuse legitimate authentication flows and steal or replay tokens. It recommends restricting unnecessary device-code authentication and investigating suspicious