Ransomware Attacks Often Begin Long Before Encryption, Huntress Says
Summary
Huntress explains how ransomware intrusions can build through brokered access, identity abuse and trusted-tool misuse before encryption. The article cites six intrusions linked to an exposed Citrix gateway and summarizes 2025 threat trends.
Key points
- Huntress traced six unrelated ransomware intrusions to an exposed Citrix NetScaler gateway and a reusable active-session theft technique; DragonForce ransomware was involved in the cases.
- Initial access brokers may sell network access obtained through infostealers, phishing, social engineering or unpatched systems.
- The article highlights identity abuse and says 37.2% of identity-based attacks in 2025 involved suspicious login activity, citing the Huntress 2026 Cyber Threat Report.
- Attackers may use legitimate tools such as PowerShell and remote monitoring and management software to blend in; Huntress reported a 277% year-over-year increase in RMM abuse in 2025.
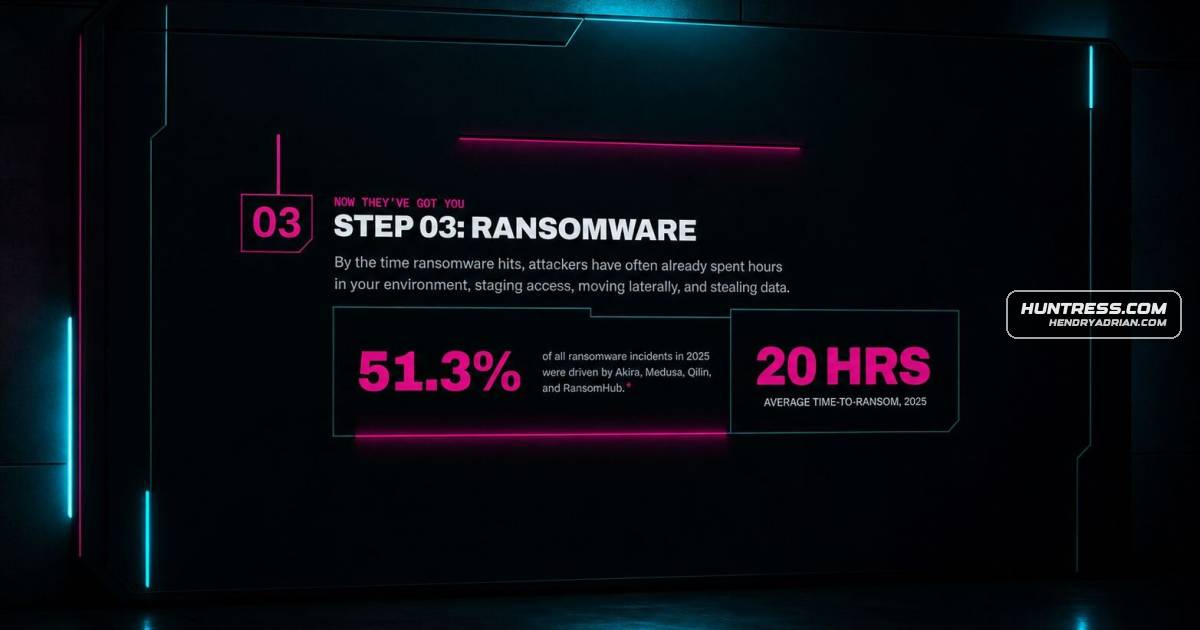
- Attackers spent an average of 20 hours in target environments before launching ransomware in 2025, according to the article.
- Akira, Medusa, Qilin and RansomHub accounted for 51.3% of ransomware incidents in 2025, the article says.
Article Details
- Topic
- How ransomware attacks develop through initial access, identity abuse, trusted-tool misuse, and delayed encryption
Threat Actors
AkiraNamed as one of four groups that drove ransomware incidents in 2025.DragonForceNamed in connection with DragonForce ransomware at the end of a described ransomware intrusion.MedusaNamed as one of four groups that drove ransomware incidents in 2025.QilinNamed as one of four groups that drove ransomware incidents in 2025.RansomHubNamed as one of four groups that drove ransomware incidents in 2025.