Fake Claude Install Guide Delivers MacSync Stealer and RAT to macOS Users
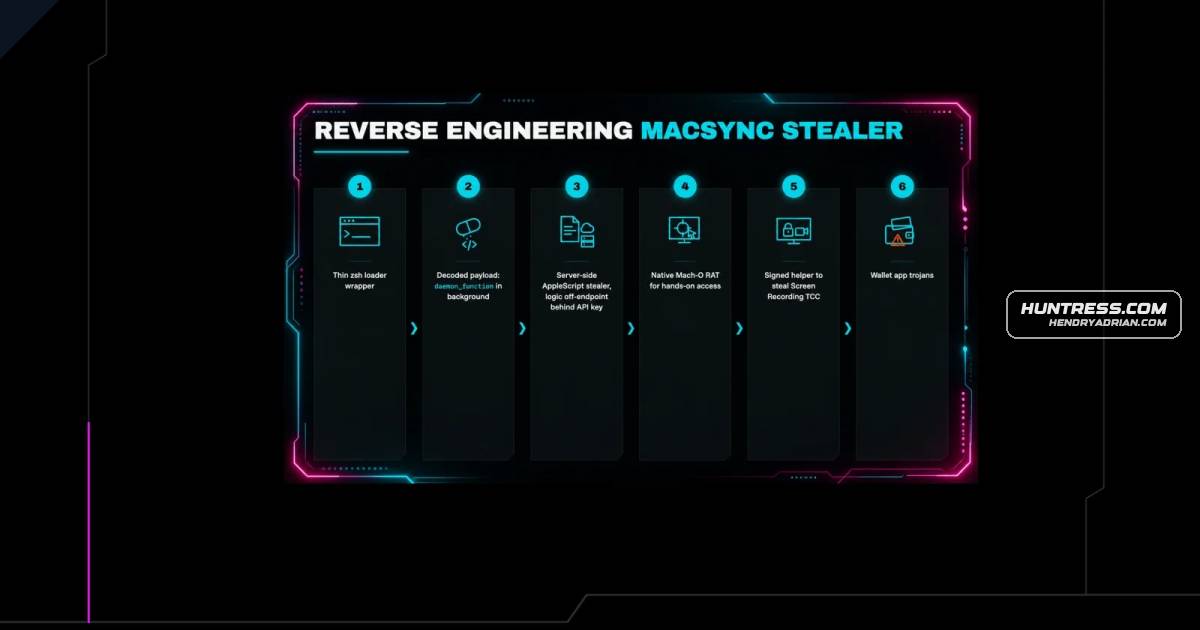
Summary
Huntress reverse-engineered MacSync, a six-stage macOS malware chain delivered through a fake Claude install guide in a sponsored search result. It steals credentials and wallet recovery phrases, installs a persistent RAT, and can trojanize wallet apps.
Key points
- A victim clicked a sponsored Google result leading to a fake Apple Support guide on a public Claude share, then ran a curl command in Terminal to install the malware.
- MacSync’s six-stage chain uses a zsh loader, a server-delivered AppleScript stealer, a persistent native RAT, a Screen Recording permission helper, and wallet-app trojans.
- The stealer targets browser cookies and logins, keychain secrets, Telegram sessions, SSH and cloud keys, files, and desktop and browser-based cryptocurrency wallets.
- The malware can prompt for Full Disk Access and the victim’s account password, then use a LaunchAgent for persistent access and a helper to capture screenshots.
- Trojanized Ledger and Trezor apps display fake recovery flows that steal wallet seed phrases and send them to attacker-controlled infrastructure.
- Huntress recommends behavioral detection, including suspicious curl-to-zsh execution, curl-to-osascript activity, unexpected LaunchAgents, and ad-hoc-signed wallet apps.
Article Details
- Attack Vectors
- A paid Google search placement directed a user seeking Claude installation instructions to a malicious public Claude conversation impersonating Apple Support.
- The installation guide induced the user to paste a command into Terminal that decoded a delivery URL, downloaded a loader, and piped it directly into zsh.
- A Base64-encoded, gzip-compressed loader fetched server-hosted AppleScript and executed it through osascript without saving the AppleScript to disk.
- Deceptive system-style dialogs persuaded the user to grant Full Disk Access and disclose an account password, which the malware validated through dscl . authonly.
- The stealer installed a persistent native RAT and a separately signed helper designed to obtain Screen Recording permission.
- Installed wallet applications were modified and ad-hoc re-signed so subsequent launches displayed branded recovery-phrase phishing forms.
- Defensive Notes
- Prioritize behavioral and network detections over file hashes and eight-character identifiers, which change between builds.
- Monitor Base64-decoded curl URLs piped into zsh, curl requests to /dynamic piped into osascript, and loader commands appended to ~/.zshrc.
- Inspect ~/.zshrc after repeated Full Disk Access prompts: a cleanup bug can leave the malicious startup command in place.
- Detect ~/.local/com.apple.<8hex>.hcpi paired with ~/.local/.mpwd and a LaunchAgent pointing to the binary. LaunchAgent labels may impersonate existing third-party updaters rather than use a com.apple prefix.
- Monitor /usr/sbin/screencapture -x launched by a non-Apple parent, newly installed com.apple.<8hex>.capture.app bundles, and /tmp/.com.apple.tcc.* marker files.
- Investigate wallet applications with ad-hoc signatures, no Team ID, mismatched ElectronAsarIntegrity values, or injected recovery-step-* files.
- Monitor outbound requests to the reported delivery and RAT infrastructure and POST requests containing seedwords JSON to /modules/wallets.
- Retain process telemetry: the malware deletes staging directories, temporary credential files, collection archives, and other artifacts after use.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | agenticsora[.]com | Attacker delivery domain serving the loader, AppleScript stealer, RAT, capture helper, and wallet payloads. |
| DOMAIN | malwareaudit[.]com | Delivery domain observed in a second Huntress incident using the same stealer chain and shared api-key. |
| DOMAIN | sdhomeinspectors[.]com | Attacker-registered seed-drop domain used to receive stolen wallet recovery phrases. |
| DOMAIN | southcarolinacounselor[.]com | Attacker-registered seed-drop domain used to receive stolen wallet recovery phrases. |
| HOSTNAME | main[.]sdhomeinspectors[.]com | Attacker-controlled host receiving recovery phrases from trojanised Ledger applications. |
| HOSTNAME | main[.]southcarolinacounselor[.]com | Attacker-controlled host receiving recovery phrases from trojanised Trezor Suite. |
| IPV4 | 103[.]216[.]221[.]95 | Operator/panel IP recorded in the AppleScript stealer's beacon information file. |
| IPV4 | 85[.]206[.]161[.]241 | Hardcoded RAT C2 IP contacted over TLS on port 8443. |
| SHA256 | 071bd109208eb1080ef525b5be394244cec467c59ffef5b8782cfb5e4850401d | Source-listed SHA-256 value for the Ledger Wallet trojan payload. |
| SHA256 | 230dff4bf9442a951dcd6898b2110924969a20668c20a43e3ceed6fcef65963e | Source-listed SHA-256 value for the Trezor Suite trojan payload. |
| SHA256 | 31566a1df7070f30cb990aa5eab310c1d4e0266c8776e9438138e5438ec1cff8 | Source-listed SHA-256 value for the Ledger Live trojan payload. |
| SHA256 | 3ae26ed89d3a1a140edc89ca78513aba2895789ed0d0f64cad6605b6f2347c7e | Source-listed SHA-256 value for the universal Mach-O agent RAT. |
| SHA256 | 3db8befc08dc02ab7a76b5193abd81653775e8f3ceac5864c7c2188b2dbd3c54 | Source-listed SHA-256 value for the dynamic AppleScript stealer. |
| SHA256 | 78dea0693ac2d70bdf8be7588667a75910e43fd84397ad484e710e37369a30f7 | Source-listed SHA-256 value for the malicious capture agent bundle. |
| SHA256 | 9c09c303fa058c2d3e179969bd58ca5523775ff2d310fb2f8266ac74cb21ee81 | Source-listed SHA-256 value for the ScreenCap Mach-O helper. |
| URL | hxxp[:]//agenticsora[.]com/curl/<token> | Source-provided tokenized URL pattern serving the zsh loader. |
| URL | hxxp[:]//agenticsora[.]com/dynamic?txd=<token> | Source-provided URL pattern returning the AppleScript stealer for execution through osascript. |
| URL | hxxp[:]//agenticsora[.]com/dynamic?txd=<token>[&pwd=<pw>] | IOC-table URL pattern for the AppleScript stage, including optional submission of the captured account password. |
| URL | hxxp[:]//agenticsora[.]com/gate?buildtxd=<token>&upload_id=[.][.][.] | Source-provided endpoint pattern receiving chunked HTTP PUT uploads of stolen data. |
| URL | hxxps[:]//agenticsora[.]com/ledger/<token> | Source-provided download URL pattern for a trojanised wallet payload. |
| URL | hxxps[:]//agenticsora[.]com/loader/agent/<token> | Source-provided download URL pattern for the native Mach-O RAT. |
| URL | hxxps[:]//agenticsora[.]com/loader/capture-agent/<token> | Source-provided download URL pattern for the malicious screen-capture helper. |
| URL | hxxps[:]//main[.]sdhomeinspectors[.]com/modules/wallets | Recovery-phrase exfiltration URL embedded in the trojanised Ledger phishing page. |
MITRE ATT&CK
T1005 · Data from Local SystemThe stealer copies local browser profiles, wallet data, Apple Notes, shell dotfiles, and selected user files.T1027 · Obfuscated Files or InformationLoader content is Base64-encoded and gzip-compressed, while the RAT hides its delivery domain and paths with single-byte XOR.T1036 · MasqueradingMalicious components use com.apple identifiers, a Screen Recording display name, and legitimate updater labels; wallet phishing pages reuse genuine branding.T1041 · Exfiltration Over C2 ChannelThe loader uploads the stolen-data archive in 10 MiB HTTP PUT chunks to /gate, and the RAT submits the captured password over its control channel.T1056.002 · GUI Input CaptureA fake System Preferences dialog captures the account password, and injected wallet forms capture recovery phrases.T1059.002 · AppleScriptThe loader pipes server-provided AppleScript into osascript to perform credential theft, collection, and installation.T1059.004 · Unix ShellThe pasted loader runs through zsh; the RAT supports remote shell commands and an interactive /bin/zsh session through forkpty.T1070.004 · File DeletionThe malware deletes temporary password and keychain scripts, collection staging directories, and the archive after successful upload.T1071.001 · Web ProtocolsDelivery and exfiltration use HTTP requests, while RAT control uses WebSocket frames over TLS.T1074.001 · Local Data StagingCollected data is staged beneath a randomized /tmp/sync directory before archiving.T1082 · System Information DiscoveryThe stealer collects system_profiler software, hardware, and display information; the RAT reports host and OS inventory.T1105 · Ingress Tool TransferThe chain downloads the AppleScript, native RAT, capture helper, and trojanised wallet payloads from attacker delivery infrastructure.T1113 · Screen CaptureThe capture helper invokes /usr/sbin/screencapture -x, and screenshots can leave through the RAT's upload channel.T1140 · Deobfuscate/Decode Files or InformationThe loader decodes Base64 and inflates gzip content; the stealer decodes the embedded keychain script.T1204 · User ExecutionThe victim manually runs the fake installation command and interacts with deceptive permission and password dialogs.T1539 · Steal Web Session CookieMacSync collects browser cookie stores and Telegram Desktop session data.T1543.001 · Launch AgentA LaunchAgent with RunAtLoad and KeepAlive starts the RAT at login and relaunches it if it exits.T1546.004 · Unix Shell Configuration ModificationThe stealer appends a curl-to-zsh command to ~/.zshrc so opening a new interactive shell reruns the chain after Full Disk Access is granted.T1548 · Abuse Elevation Control MechanismDeceptive dialogs obtain Full Disk Access, while the signed capture helper requests and tracks Screen Recording permission.T1552.001 · Credentials In FilesCollection includes ~/.ssh, ~/.aws, ~/.kube, keychain files, and files selected by credential-related extensions such as pem, seed, and kdbx.T1553 · Subvert Trust ControlsThe installer ad-hoc re-signs modified wallet applications and alters Trezor Suite's permitted-origins list to allow the seed-drop host.T1554 · Compromise Host Software BinaryThe installer replaces app.asar and Info.plist inside installed wallet applications so trusted launches execute the phishing payload.T1555.001 · KeychainThe keychain script extracts browser Safe Storage secrets and can unlock the login keychain using the validated account password.T1555.003 · Credentials from Web BrowsersThe stealer copies browser Login Data and obtains Safe Storage keys intended to decrypt collected browser credentials.T1560.001 · Archive via UtilityThe AppleScript uses ditto -c -k --sequesterRsrc to create /tmp/osalogging.zip from the staging tree.T1571 · Non-Standard PortThe RAT contacts its hardcoded raw-IP TLS C2 on port 8443.T1573.001 · Symmetric CryptographyRAT messages are encrypted with AES-256-CBC using a key derived from the embedded token and a fresh random IV.T1573.002 · Asymmetric CryptographyThe RAT uses its bundled OpenSSL implementation for a TLS connection to the raw-IP C2 endpoint.T1657 · Financial TheftWallet trojans collect recovery phrases intended to give the operator control over the victim's derived cryptocurrency accounts.
People
Malware
AMOS StealerIf this feels familiar, that's because it is. Huntress previously documented cases of AMOS Stealer delivered through poisoned ChatGPT and Grok conversations, and SectopRAT delivered through a fake Claude desktopAtomic Stealertheir own bugs against real hosts. It's also the first of several things tying the kit to the AMOS/Atomic Stealer lineage, and more on that once the whole chain is on the table.MacSyncHomeBlogFake Claude Install Guide Leads to MacSync Stealer and RAT: What We Pulled From the Attacker’s ServersSectopRATdocumented cases of AMOS Stealer delivered through poisoned ChatGPT and Grok conversations, and SectopRAT delivered through a fake Claude desktop malvertising campaign. In each of those cases, poisoned search
Vendors
AnthropicIn between was an ad, and the ad is the whole trick. The result they clicked was not the organic anthropic.com listing but a paid Google Ads placement.CloudflareThe operation spans three separate infrastructure tiers: Cloudflare-fronted delivery (agenticsora[.]com in this case and malwareaudit[.]com in a second Huntress incident running the same chain), an operator IP recordedGoogleHuntress recently investigated an incident where the victim searched Google for how to install Claude on a Mac, clicked a sponsored result, and landed on a weaponised claude.ai/share conversation dressed up as an AppleUnstoppable Domainsdespite their innocuous-seeming small-business names. VirusTotal shows both re-registered through Unstoppable Domains on 2026-02-13, roughly five months before the intrusion, and both sit behind the same Cloudflare
Products
Apple Notespaths this stealer is built to collect, from the browser cookie stores to Safari's history to Apple Notes' database. Without it, the collection would result in the user being alerted by a series of GUI promptsArc# repeated for Brave, Edge, Vivaldi, Opera, OperaGX, Yandex, Arc, Chromium,AtomicBefore collection, the script takes an atomic lock with mkdir /tmp/macsync_<token>.lock. On the host that appeared as /tmp/macsync_e9967985....lock. That mutex is the artifact that gives the MacSync malware family itsBitcoin CoreExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Brave# repeated for Brave, Edge, Vivaldi, Opera, OperaGX, Yandex, Arc, Chromium,Chrome Beta# Chrome Beta/Canary/Dev, CocCoc ...Chrome CanaryChromiumruns it. We decoded that blob, a 3,434-byte /bin/sh script, and discovered that it pulls each browser's Chromium "Safe Storage" AES key out of the login keychain:ClaudeHomeBlogFake Claude Install Guide Leads to MacSync Stealer and RAT: What We Pulled From the Attacker’s ServersClaude CodeThe victim went looking for Claude. Their browser history opens with a Google search for how to install Claude Code on a Mac and, two clicks later, lands on a page that appears to show the answer. In between was an ad,CocCoc# Chrome Beta/Canary/Dev, CocCoc ...CoinomiExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Edge# repeated for Brave, Edge, Vivaldi, Opera, OperaGX, Yandex, Arc, Chromium,ElectrumExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.ExodusExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Google Adsthe ad is the whole trick. The result they clicked was not the organic anthropic.com listing but a paid Google Ads placement.Google ChromeKEY=$(security find-generic-password -w -s "Chrome Safe Storage" 2>/dev/null)Google ChromeGuardaExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Ledger LiveExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Ledger WalletExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.LibreWolfIDs (MetaMask nkbihfbeogaeaoehlefnkodbefgpgknn and many more). Gecko-based browsers (Firefox, Zen, LibreWolf, Waterfox) do not support cookies.sqlite, key4.db,logins.json, places.sqlite, formhistory.sqlite,macOSIn mid-July, Huntress investigated a macOS intrusion in which the victim thought they were installing Claude, but instead ran a full stealer and remote access tool called MacSync. The path in was relativelyMetaMaskstorage for a hardcoded list of 40 general extension IDs, then a second list of 89 wallet extension IDs (MetaMask nkbihfbeogaeaoehlefnkodbefgpgknn and many more). Gecko-based browsers (Firefox, Zen, LibreWolf,MoneroExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Mozilla Firefox89 wallet extension IDs (MetaMask nkbihfbeogaeaoehlefnkodbefgpgknn and many more). Gecko-based browsers (Firefox, Zen, LibreWolf, Waterfox) do not support cookies.sqlite, key4.db,logins.json, places.sqlite,Opera# repeated for Brave, Edge, Vivaldi, Opera, OperaGX, Yandex, Arc, Chromium,OperaGX# repeated for Brave, Edge, Vivaldi, Opera, OperaGX, Yandex, Arc, Chromium,Safarione that unlocks the protected paths this stealer is built to collect, from the browser cookie stores to Safari's history to Apple Notes' database. Without it, the collection would result in the user being alerted bySparrowExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Telegram DesktopThe entire Telegram Desktop tdata/ session directory, ~/Library/Keychains/*.keychain-db, ~/.ssh, ~/.aws, ~/.kube, a file-grabber that sweeps Desktop, Documents, and Downloads by extension (including seed, kdbx, pem,Terminalclaude.ai/share conversation dressed up as an Apple Support install guide. It told them to open Terminal and paste a single curl command. Trezor SuiteExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Vivaldi# repeated for Brave, Edge, Vivaldi, Opera, OperaGX, Yandex, Arc, Chromium,WasabiExodus, Electrum, Atomic, Guarda, Coinomi, Sparrow, Wasabi, Bitcoin Core, Monero, Ledger Live, Ledger Wallet, Trezor Suite, and others.Waterfoxnkbihfbeogaeaoehlefnkodbefgpgknn and many more). Gecko-based browsers (Firefox, Zen, LibreWolf, Waterfox) do not support cookies.sqlite, key4.db,logins.json, places.sqlite, formhistory.sqlite, cert9.db,Yandex# repeated for Brave, Edge, Vivaldi, Opera, OperaGX, Yandex, Arc, Chromium,Zenextension IDs (MetaMask nkbihfbeogaeaoehlefnkodbefgpgknn and many more). Gecko-based browsers (Firefox, Zen, LibreWolf, Waterfox) do not support cookies.sqlite, key4.db,logins.json, places.sqlite,