Huntress Tracks Ongoing Microsoft 365 Device-Code Phishing via BL Networks
Summary
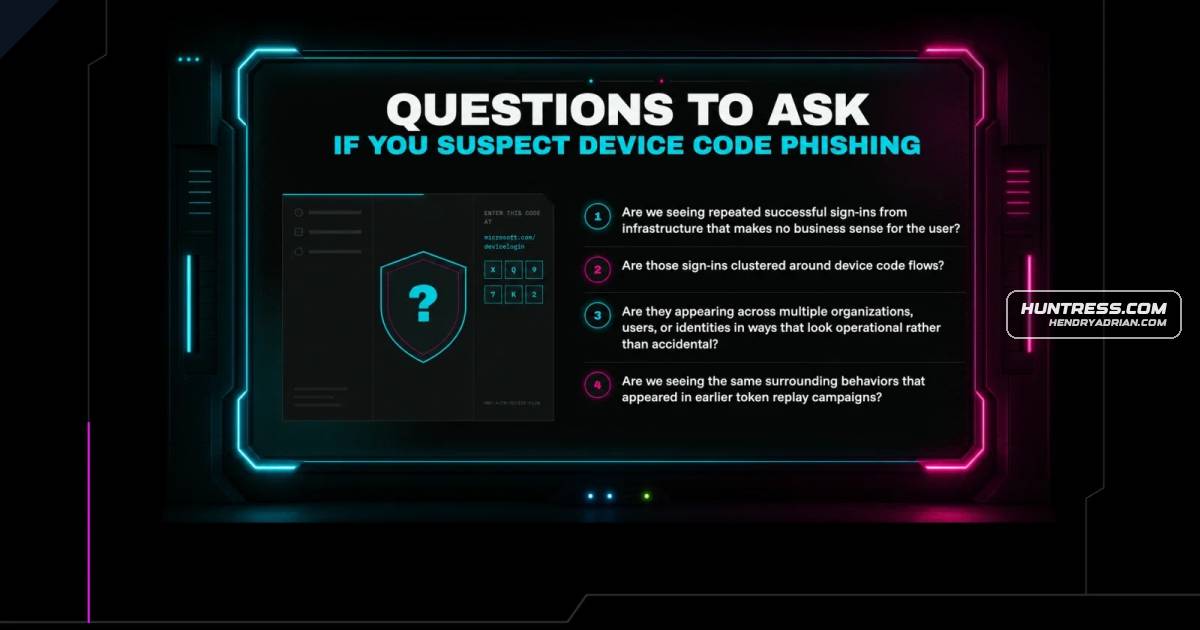
Huntress reports a continuing 2026 Microsoft 365 device-code phishing wave using BL Networks infrastructure to abuse legitimate authentication flows and steal or replay tokens. It recommends restricting unnecessary device-code authentication and investigating suspicious
Key points
- Huntress observed suspicious Microsoft 365 authentication activity linked to BL Networks from April 13, 2026, continuing as of the article’s publication.
- Activity expanded from one IP address to several; Huntress recorded 26 critical-severity incidents across 23 identities from July 3 to July 27.
- The attacks abuse legitimate Microsoft authentication flows to obtain or replay tokens; MFA may still occur, and passwords do not necessarily need to be phished.
- Huntress recorded 533 events tied to 216.203.20[.]95 from April 13–30, including 113 successful logins in a 48-hour period.
- The activity follows an earlier device-code phishing wave linked to Railway infrastructure and the EvilTokens phishing-as-a-service platform.
- Huntress recommends restricting device-code authentication where unnecessary, investigating unusual successful sign-ins and infrastructure clusters, and promptly revoking affected sessions and tokens.
Article Details
- Event Type
- Ongoing device code phishing and token-abuse activity linked to BL Networks infrastructure, following an earlier Railway-linked wave.
- Impact
- Huntress reported 533 events linked to BL Networks from April 13–30, 2026, including 113 successful logins in a 48-hour period. From July 3–27, it observed 26 critical-severity incidents spanning 23 identities. The activity involved successful Microsoft 365 sign-ins and token abuse.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 193[.]149[.]176[.]151 | IP Huntress identified as part of the BL Networks infrastructure used in device code phishing attacks. |
| IPV4 | 193[.]149[.]176[.]238 | IP Huntress identified as part of the BL Networks infrastructure used in device code phishing attacks. |
| IPV4 | 216[.]203[.]20[.]95 | BL Networks-linked IP associated by Huntress with malicious authentication activity and successful sign-ins. |
| IPV4 | 45[.]61[.]136[.]129 | IP Huntress identified as part of the BL Networks infrastructure used in device code phishing attacks. |