Huntress Details Conditional Access Gaps Behind Railway and LSHIY Microsoft 365 Attacks
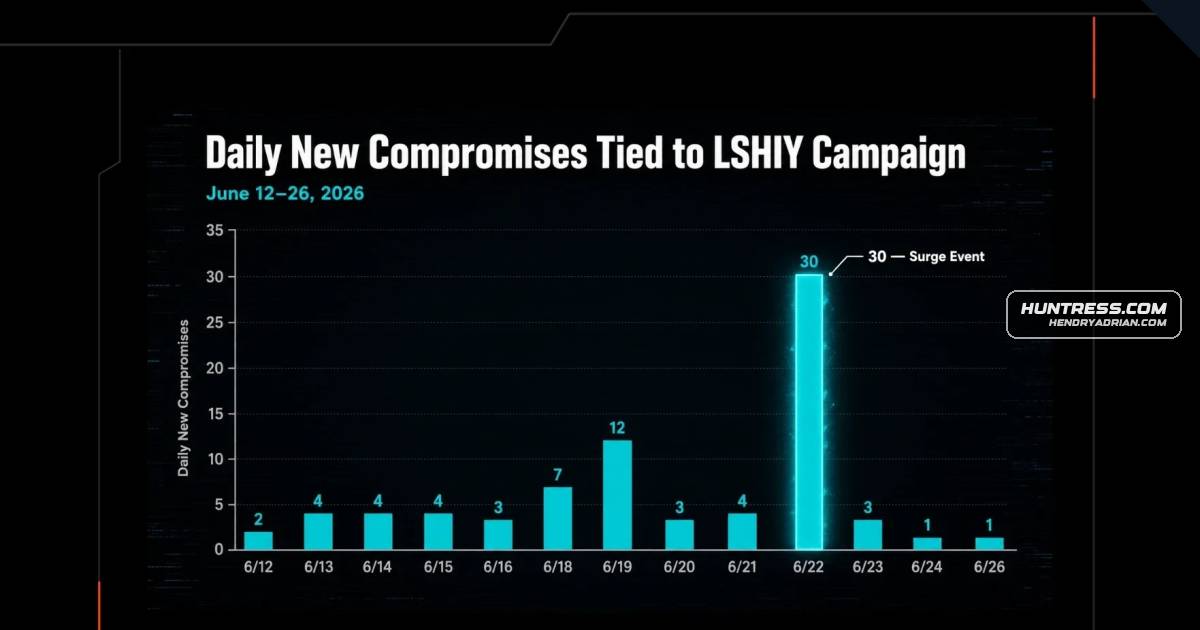
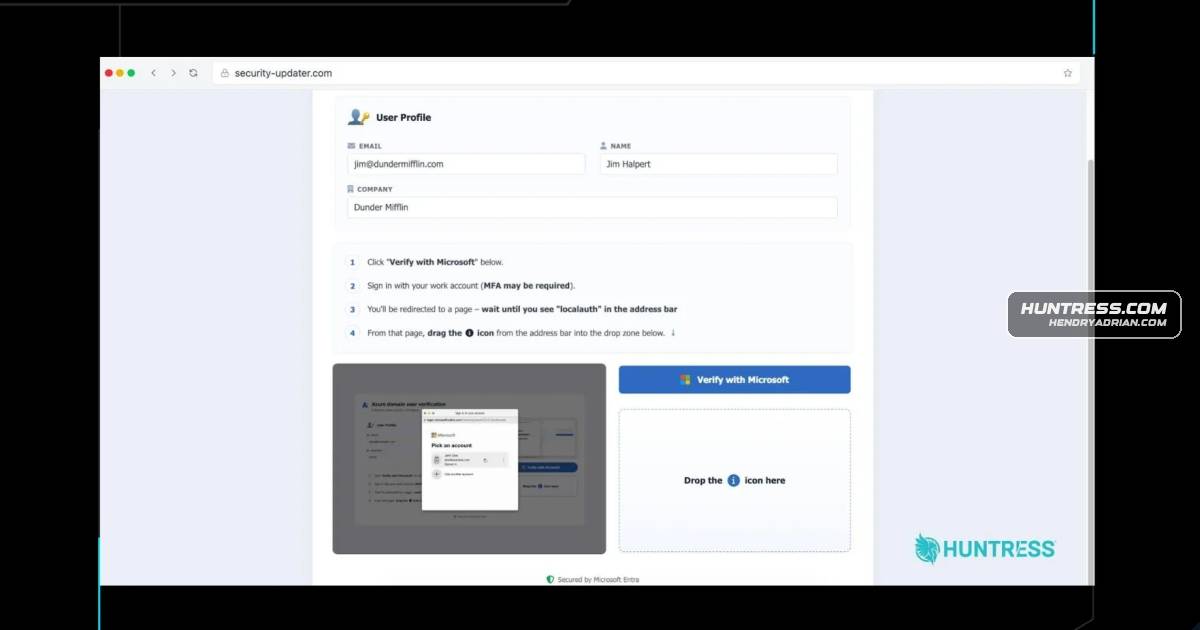
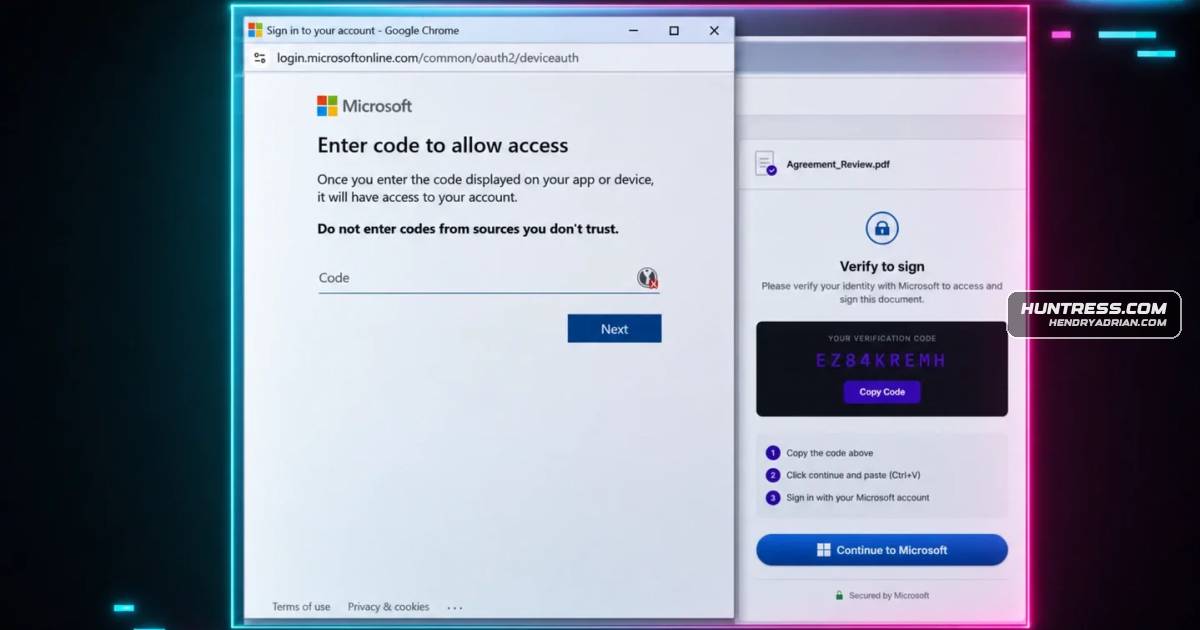
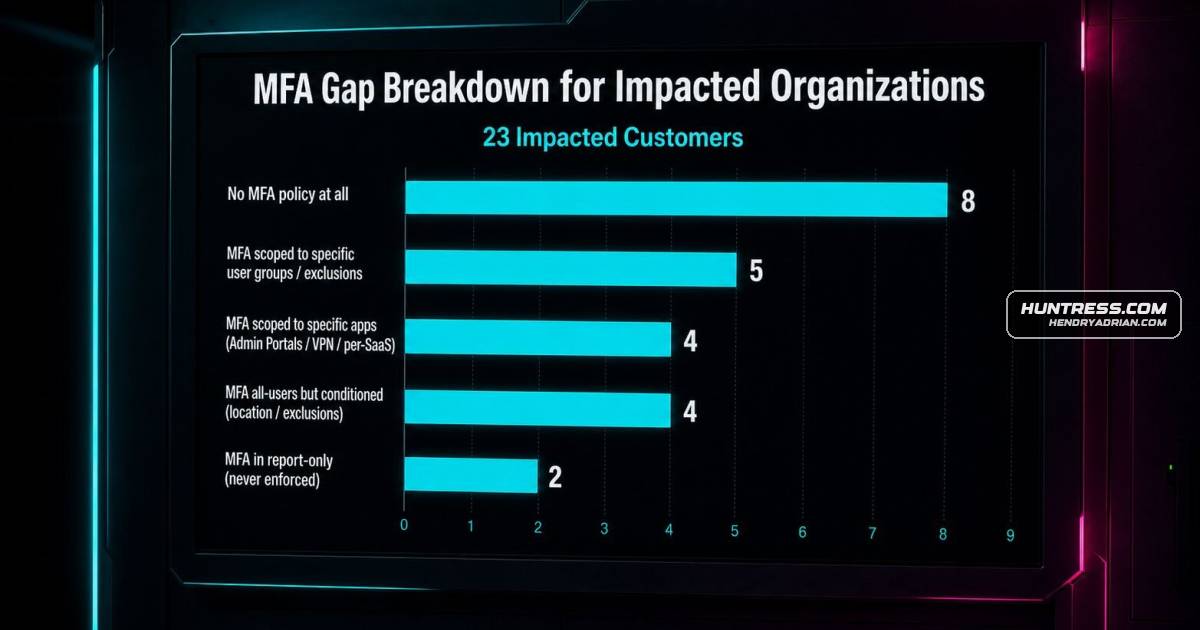
Huntress links two Microsoft 365 campaigns to Conditional Access gaps: device-code phishing using Railway[.]com infrastructure and ROPC password spraying via Azure CLI. It recommends blocking device code flow and applying MFA policies across users, cloud apps, and auth.