Huntress Adds Custom HTML Phishing Simulations to Security Training
Summary
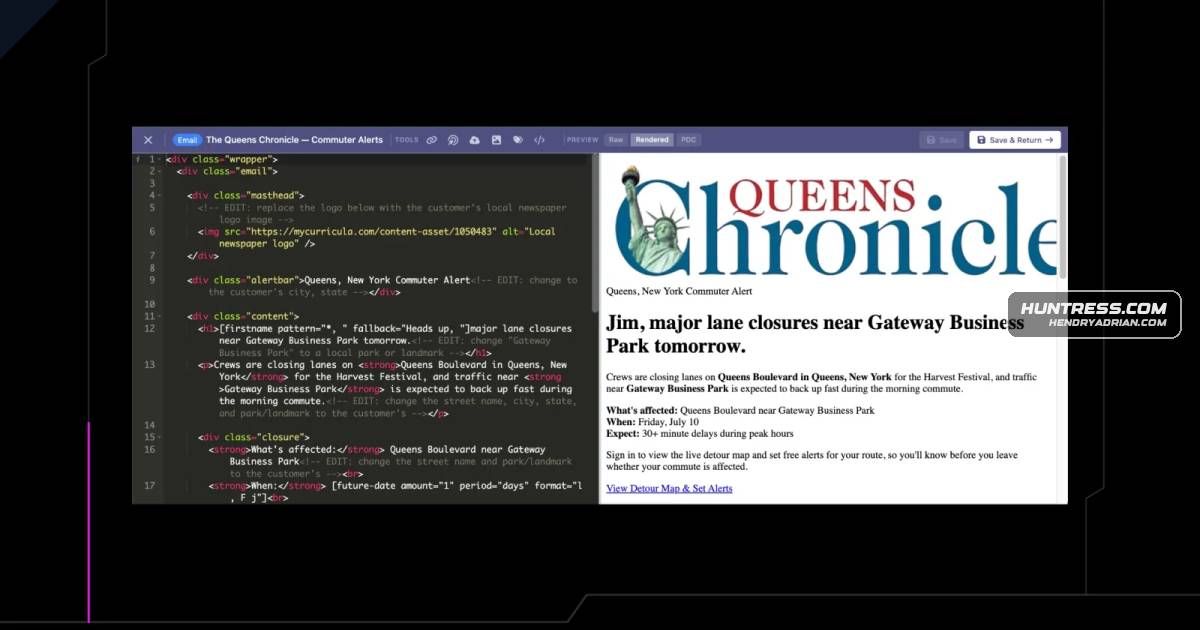
Huntress added an HTML editor to Managed SAT, allowing administrators to create tailored phishing simulations. The company says custom scenarios complement its expert-curated campaigns and are subject to link sanitization.
Key points
- The feature lets Managed SAT administrators build phishing email scenarios from scratch using HTML, rather than selecting only fixed templates.
- Organizations can tailor simulations to their vendors, tools, internal communications, or phishing scenarios they have encountered.
- Huntress says custom scenarios undergo link sanitization to prevent them from being used to phish employees.
- The company recommends pairing custom scenarios with its monthly, expert-curated Managed Phishing campaigns.
- Huntress reports click-to-compromise rates of about 10%–20% for its better-performing custom scenarios, compared with 25% or higher on average for managed scenarios.
Article Details
- Event Type
- Huntress announced the launch of Custom HTML for Custom Phishing, a feature in Huntress Managed SAT that lets administrators create tailored phishing simulation scenarios using an HTML editor.
- Impact
- The feature enables organizations to create simulations that reflect their own vendors, communication styles, and risk factors. Huntress says each custom scenario undergoes link sanitization to prevent its use for phishing. The article reports click-to-compromise rates of around 10% to 20% for better-performing custom HTML scenarios, 25% or higher on average for Huntress Managed scenarios, 33% for a Deepfake Meeting Invite scenario, and 65% for a Google Drive Document Invite scenario and one other recent managed scenario.
People
Brett LeathermanIdentified as Assistant Director of the FBI Cyber Division and a participant in a promoted event.James O’LearyNamed as the article's author.John HammondNamed as a participant in a promoted event about partnerships disrupting cybercrime.Kyle HanslovanNamed as a participant in a promoted event about partnerships disrupting cybercrime.
Vendors
Products
Industries
Financial ServicesOne financial services customer built a scenario mimicking internal IT support requests, matching the exact tone their help desk uses. HealthcareA healthcare customer went a different direction, styling a fake vendor portal update imitating a supplier that its staff deals with every weekManufacturingA manufacturing customer recreated an operational alert formatted to match the notices its own facilities send out.