
Researchers Link Coruna iOS Exploit Framework to Operation Triangulation
Summary
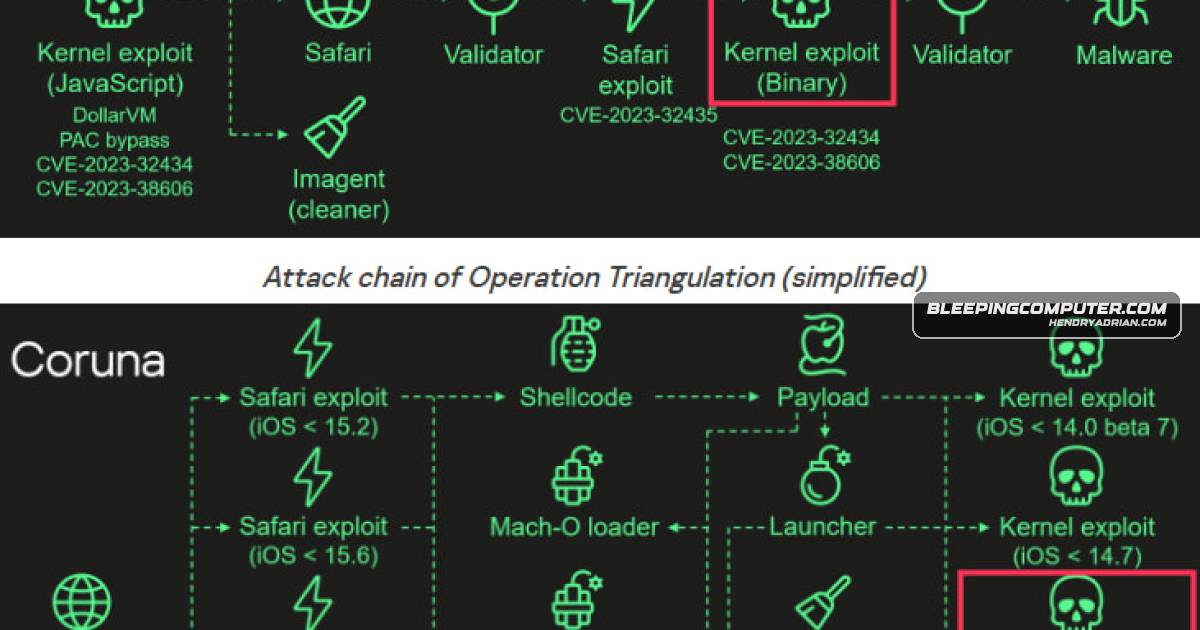
Kaspersky researchers link Coruna to Operation Triangulation through updated exploit code and code similarities. The maintained iOS kit has five chains using 23 vulnerabilities, targets newer Apple hardware and iOS, and has also been used in crypto-theft campaigns.
Key points
- Kaspersky researchers say Coruna’s kernel exploits for CVE-2023-32434 and CVE-2023-38606 are updated versions of exploits used in Operation Triangulation.
- The framework contains five iOS exploit chains using 23 vulnerabilities and checks for newer hardware, including A17 and M3-series chips, and iOS versions up to 17.2.
- The described attack begins in Safari with device fingerprinting, then selects suitable remote-code-execution and PAC exploits.
- The payload decrypts components with ChaCha20, decompresses them with LZMA, and uses device architecture and iOS version to select a kernel exploit and Mach-O loader.
- Kaspersky says the framework, initially associated with espionage, has also been used in financially motivated campaigns targeting cryptocurrency through fake exchange websites.
- Apple says security updates for the latest and earlier iOS versions address the flaws in the recently uncovered exploit kits.
Article Details
- Attack Vectors
- Coruna begins in Safari with a stager that fingerprints the device and selects suitable RCE and PAC exploits.
- The framework selects and executes a kernel exploit based on the device architecture and iOS version, then uses a Mach-O loader and launcher to deploy a spyware implant.
- The payload retrieves encrypted components, decrypts them with ChaCha20, decompresses them with LZMA, and parses custom containers.
- Coruna has also been used in financially motivated campaigns to steal cryptocurrency through fake exchange websites.
- Defensive Notes
- Apple has made fixes for the flaws in security updates for recent and earlier iOS versions; install applicable iOS updates.
MITRE ATT&CK
T1140 · Deobfuscate/Decode Files or InformationCoruna decrypts downloaded components with ChaCha20 and decompresses them with LZMA before parsing their contents.T1404Coruna executes a kernel exploit selected for the device architecture and iOS version.T1407The payload retrieves additional encrypted components for subsequent stages.
CVE
CVE-2023-32434Apple · iOS and iPadOS; Apple · macOS; +1 moreThe kit includes five full iOS exploit chains leveraging 23 vulnerabilities, including CVE-2023-32434 and CVE-2023-38606.CVE-2023-38606Apple · iOS and iPadOS; Apple · macOS; +2 moreThe kit includes five full iOS exploit chains leveraging 23 vulnerabilities, including CVE-2023-32434 and CVE-2023-38606.
People
Vendors
AppleCoruna is a maintained successor to the Operation Triangulation iOS exploit framework, expanding its capabilities to target modern Apple chips and iOS versions.KasperskyAfter analyzing the exploit code for the two security issues, Kaspersky researchers determined that Coruna ran an updated version of the exploit used in Operation Triangulation that had started since 2019.
Products
iOSCoruna is a maintained successor to the Operation Triangulation iOS exploit framework, expanding its capabilities to target modern Apple chips and iOS versions.SafariAttacks begin in Safari with device fingerprinting, then select RCE/PAC exploits and decrypt payloads using ChaCha20 and LZMA before deploying Mach-O loaders.