
Unit 42 Details Three Cyberespionage Clusters Targeting a Southeast Asian Government
Summary
Unit 42 analyzed three cyberespionage clusters targeting a Southeast Asian government in June–August 2025, detailing USBFect/PUBLOAD, CL-STA-1048 tools and CL-STA-1049’s Hypnosis loader and likely FluffyGh0st payload. Links to China-aligned actors remain assessments.
Key points
- Unit 42 attributed USBFect activity deploying PUBLOAD across multiple government endpoints from June 1 to August 15, 2025, with high confidence to Stately Taurus.
- USBFect, which Unit 42 assesses is the same malware family as HIUPAN, propagates through removable media; ClaimLoader loads PUBLOAD into memory.
- CL-STA-1048 deployed EggStremeFuel, Masol RAT, EggStreme loader/Gorem RAT and the TrackBak infostealer. Unit 42 noted overlaps with publicly reported China-affiliated activity but said it could not establish that the reports involved the same group.
- CL-STA-1049 used the newly named Hypnosis loader, sideloaded by the legitimate Bitdefender seccenter.exe. The suspected final payload was not recovered; evidence suggests it may be FluffyGh0st.
- Observed capabilities included persistence through registry autorun keys, in-memory payload execution, keylogging, clipboard and file collection, and command-and-control over TCP, HTTP and gRPC.
- Telemetry showed the suspected CL-STA-1049 payload communicating with webmail.rpcthai[.]com; Unit 42 assessed that attackers may have hijacked the domain for command-and-control.
- Unit 42 assessed that the clusters showed overlaps with China-aligned campaigns and may have shared a target of interest; it did not establish direct links between all clusters.
Article Details
- Attack Vectors
- USBFect propagated through removable media, monitoring for drive insertion and copying its components to removable drives.
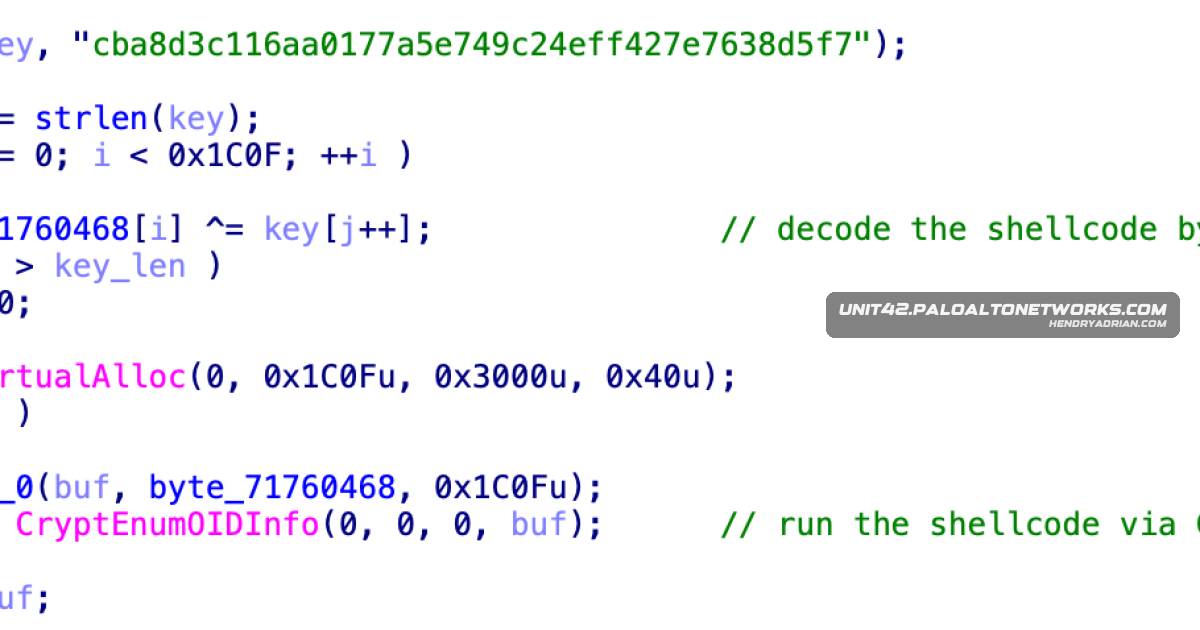
- ClaimLoader established persistence by registering a copied legitimate application in a Windows registry autorun key, then decrypted and executed embedded shellcode that loaded PUBLOAD.
- Hypnosis loader used DLL side-loading through the legitimate seccenter.exe executable, then loaded the likely final payload bdusersy.dll.
- EggStreme loader used DarkLoadLibrary and libpeconv for in-memory payload execution; CoolClient loaders retrieved payloads from an encrypted local file.
- The malware used C2 over TCP, HTTP POST, and gRPC. The deployed tools collected host information, files, keystrokes, and clipboard data for theft.
- Defensive Notes
- The article says Advanced WildFire models and analysis techniques were reviewed and updated based on the reported indicators.
- Advanced URL Filtering and Advanced DNS Security identify known domains and URLs associated with the activity as malicious.
- Cortex XDR and XSIAM can use the Malware Prevention Engine, Advanced WildFire, Behavioral Threat Protection, and Local Analysis to prevent known and unknown malware.
- The article advises potentially compromised organizations to contact the Unit 42 Incident Response team.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | distrilyy[.]net | Listed as a C2 or attacker-controlled domain in the article's domain indicators. |
| DOMAIN | fikksvex[.]com | Listed as a C2 or attacker-controlled domain in the article's domain indicators. |
| DOMAIN | laichingte[.]net | C2 domain in an EggStremeFuel configuration. |
| DOMAIN | popnike-share[.]com | Listed as a C2 or attacker-controlled domain in the article's domain indicators. |
| DOMAIN | shepinspect[.]com | Listed as a C2 or attacker-controlled domain in the article's domain indicators. |
| DOMAIN | theuklg[.]com | Listed as a C2 or attacker-controlled domain in the article's domain indicators. |
| DOMAIN | webmail[.]homesmountain[.]com | C2 domain in the configuration of a malicious DLL attributed to FluffyGh0st. |
| DOMAIN | webmail[.]rpcthai[.]com | C2 hostname contacted by the likely final payload; the article assesses that attackers may have created it on a hijacked legitimate domain. |
| IPV4 | 103[.]122[.]164[.]106 | Listed as C2 infrastructure in the article's IPv4 indicators. |
| IPV4 | 103[.]131[.]95[.]107 | Listed as C2 infrastructure in the article's IPv4 indicators. |
| IPV4 | 103[.]15[.]29[.]17 | Listed as C2 infrastructure in the article's IPv4 indicators. |
| IPV4 | 109[.]248[.]24[.]177 | Listed as C2 infrastructure in the article's IPv4 indicators. |
| IPV4 | 120[.]89[.]46[.]135 | Listed as C2 infrastructure in the article's IPv4 indicators. |
| IPV4 | 58[.]69[.]38[.]83 | C2 IP address in an EggStremeFuel configuration. |
| SHA256 | 05995284b59ad0066350f43517382228f7eee63cd297e787b2a271f69ecf2dfc | Hash of the Masol RAT payload detected during CL-STA-1048 activity. |
| SHA256 | 11c7728697d5ea11c592fee213063c6369340051157f71ddc7ca891f5f367720 | Hash of a sample attributed to FluffyGh0st and found in an archive that also contained a Hypnosis loader sample. |
| SHA256 | 1aa37a477c539edf25656a300002a28d4246ec83344422dd705b42d3443a2623 | Hash of the EggStremeFuel backdoor DLL loaded into memory during CL-STA-1048 activity. |
| SHA256 | 34bf325492614dd4d842ec24f22a402ab73908cb91a74846945eae4775290ff2 | Hash of a DLL associated with FluffyGh0st samples communicating with the reported C2 domain. |
| SHA256 | 35ca351a831c67f0e0a658a186be0065043e0977cb70771c03a24b0523edcf30 | Hash of an additional malicious DLL masquerading as a log file in the Hypnosis loader activity. |
| SHA256 | 4b29b74798a4e6538f2ba245c57be82953383dc91fe0a91b984b903d12043e92 | Hash of the EVENT.dll USBFect/ClaimLoader sample observed in the campaign. |
| SHA256 | 6caa78943939bd7518f5e7eaa44fa778d0db8b822e260d7fe281cf45513f82d9 | Hash of the EggStreme loader associated with an attempted Gorem RAT deployment. |
| SHA256 | 835795aa494021752f21fbef63c81227c1b934437a02aa1f2a258c9f60b0b7a3 | Hash of a CoolClient loader DLL detected during the investigation. |
| SHA256 | 84e37e42312b9a502c40cf1f3fc181e3ebd4f3e35c58bbf182740dfe38d3b6b9 | Hash of the TrackBak infostealer payload. |
| SHA256 | 851d57a2bf514202f54dafa1eb83a862653be7512b6e9535914b8d1d719d495f | Hash of a CoolClient loader DLL detected during the investigation. |
| SHA256 | 9d7c8d3bc4ac108fb2602424a1f4918c051c2443f0526bbb2c970c8e57dbd90d | Hash of the Hypnosis loader DLL used in the side-loading activity. |
| SHA256 | c774fd7373084f93383593f0a40f56c8a8b95b73e59cd4fc7117daa6b7441e73 | Hash of bdusersy.dll, which the article describes as the likely final payload. |
MITRE ATT&CK
T1005 · Data from Local SystemTrackBak collects files from drives on the infected system.T1041 · Exfiltration Over C2 ChannelPUBLOAD sends encrypted host information over its C2 channel, while TrackBak exfiltrates collected data.T1056.001 · KeyloggingThe Gorem RAT keylogger captures keystrokes, and TrackBak collects key logs.T1071.001 · Web ProtocolsMasol RAT communicates with its C2 servers using encrypted HTTP POST requests.T1091 · Replication Through Removable MediaUSBFect monitors for removable drives and copies its components to them to propagate.T1105 · Ingress Tool TransferFluffyGh0st downloads plugins from C2 servers embedded in the sample.T1115 · Clipboard DataThe Gorem RAT keylogger captures clipboard contents, and TrackBak exfiltrates clipboard data.T1547.001 · Registry Run Keys / Startup FolderClaimLoader registers a copied legitimate application in a Windows registry autorun key for persistence.T1574.002 · DLL Side-LoadingHypnosis loader is loaded through DLL side-loading by the legitimate seccenter.exe executable.
Threat Actors
CL-STA-1048Unit 42's tracked malicious activity cluster deployed EggStremeFuel, Masol RAT, EggStreme loader/Gorem RAT, and TrackBak. Its links to publicly reported groups remain uncertain.CL-STA-1049Unit 42's tracked malicious activity cluster used Hypnosis loader to deploy FluffyGh0st; the article says it is likely associated with Unfading Sea Haze.Cluster BravoThe article reports that some CL-STA-1049 tooling overlaps with Cluster Bravo of Crimson Palace.Cluster CharlieThe article describes CL-STA-1048 as potentially linked to Cluster Charlie of Crimson Palace.Crimson PalaceThe article describes tooling and activity overlaps with Crimson Palace, but notes that public reporting does not establish that CL-STA-1048 is the same group; CL-STA-1049 may also be part of the campaign.Earth EstriesThe article cites public reporting associating Masol RAT and EggStreme with China-affiliated activity such as Earth Estries, while cautioning that shared tooling does not establish the same group.Mustang PandaUnit 42 attributed the USBFect and PUBLOAD activity to Stately Taurus with high confidence and also attributed separate CoolClient activity to the group based on shared anti-disassembly techniques.Unfading Sea HazeFluffyGh0st is associated with Unfading Sea Haze in the article, which assesses that CL-STA-1049 is likely associated with the group.
Malware
ClaimLoaderClaimLoader and CoolClient were used as shellcode loaders and tunneling/stealer tools, with CoolClient employing anti-disassembly techniques and loading payloads from an encrypted loader.ja file.CoolClientClaimLoader and CoolClient were used as shellcode loaders and tunneling/stealer tools, with CoolClient employing anti-disassembly techniques and loading payloads from an encrypted loader.ja file.EggStreme loaderThe campaigns deployed tools including EggStremeFuel, Masol, EggStreme loader (Gorem RAT), TrackBak stealer, and the Hypnosis loader delivering FluffyGh0st, with overlaps in TTPs suggesting links to China-aligned actorsEggStremeFuelThe campaigns deployed tools including EggStremeFuel, Masol, EggStreme loader (Gorem RAT), TrackBak stealer, and the Hypnosis loader delivering FluffyGh0st, with overlaps in TTPs suggesting links to China-aligned actorsFluffyGh0stMasol, EggStreme loader (Gorem RAT), TrackBak stealer, and the Hypnosis loader delivering FluffyGh0st, with overlaps in TTPs suggesting links to China-aligned actors such as Stately Taurus, Crimson PalaceGorem RATThe campaigns deployed tools including EggStremeFuel, Masol, EggStreme loader (Gorem RAT), TrackBak stealer, and the Hypnosis loader delivering FluffyGh0st, with overlaps in TTPs suggesting links to China-aligned actorsHIUPANJune–August 2025 targeting a Southeast Asian government organization, involving USB-propagated USBFect/HIUPAN that deployed the PUBLOAD backdoor and two additional clusters (CL-STA-1048 and CL-STA-1049) usingHypnosis loadertools including EggStremeFuel, Masol, EggStreme loader (Gorem RAT), TrackBak stealer, and the Hypnosis loader delivering FluffyGh0st, with overlaps in TTPs suggesting links to China-aligned actors such asMasol RATadditional clusters, CL-STA-1048 and CL-STA-1049, were identified: CL-STA-1048 deployed EggStremeFuel, Masol RAT, EggStreme loader/Gorem RAT and TrackBak stealer; CL-STA-1049 used the Hypnosis loader to deliverPubloada Southeast Asian government organization, involving USB-propagated USBFect/HIUPAN that deployed the PUBLOAD backdoor and two additional clusters (CL-STA-1048 and CL-STA-1049) using multiple loaders and RATs.RawCookieBackdr-NQ, EggStremeFuel, PUBLOAD, RawCookieTrackBakThe campaigns deployed tools including EggStremeFuel, Masol, EggStreme loader (Gorem RAT), TrackBak stealer, and the Hypnosis loader delivering FluffyGh0st, with overlaps in TTPs suggesting links to China-aligned actorsUSBFectfrom June–August 2025 targeting a Southeast Asian government organization, involving USB-propagated USBFect/HIUPAN that deployed the PUBLOAD backdoor and two additional clusters (CL-STA-1048 and CL-STA-1049) using
Vendors
Products
Advanced DNS SecurityAdvanced URL Filtering and Advanced DNS Security identify known domains and URLs associated with this activity as malicious.Advanced URL FilteringAdvanced URL Filtering and Advanced DNS Security identify known domains and URLs associated with this activity as malicious.Advanced WildFireAdvanced WildFire analysis revealed this DLL file has an embedded network configuration pointing to webmail.homesmountain[.]com, which matches the domain structure of the C2 server that the likely final payloadCortex XDRTwenty minutes after we observed the EggStremeFuel deployment, Cortex XDR detected another malicious payload on the same agent at the following path C:WindowsSystem32AxInstSVs.dll (SHA256 hash:Microsoft Windows[T1547 ] Registry Run Keys / Startup Folder – ClaimLoader registers a copied legitimate application in a Windows registry autorun key to establish persistence (‘…registers the copied legitimate application in a WindowsXSIAMCortex XDR and XSIAM can help prevent the threats described in this article by employing the Malware Prevention Engine.
Tools
DarkLoadLibraryEggStreme loader leverages multiple publicly available tools, such as DarkLoadLibrary and libpeconv, to achieve an in-memory payload execution.libpeconvEggStreme loader leverages multiple publicly available tools, such as DarkLoadLibrary and libpeconv, to achieve an in-memory payload execution.