cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2491 articles

Threat Research · wiz.io

Six Accounts, One Actor: Inside the prt-scan Supply-Chain Campaign

Wiz Research traced six waves of a campaign abusing GitHub’s pull_request_target workflows to steal credentials and compromise at least two npm packages. The actor opened over 500 malicious PRs, with a reported success rate below 10%.
Apr 4, 2026
Threat Research · malwarebytes.com

Fake Coca-Cola and Ferrari Job Offers Target Google and Facebook Credentials

Malwarebytes describes two job-themed phishing campaigns impersonating Coca-Cola and Ferrari. One relays Google Workspace credentials and MFA challenges through a fake Chrome window; the other uses a fake careers portal to target Facebook logins.

Apr 4, 2026
Threat Research · thehackernews.com

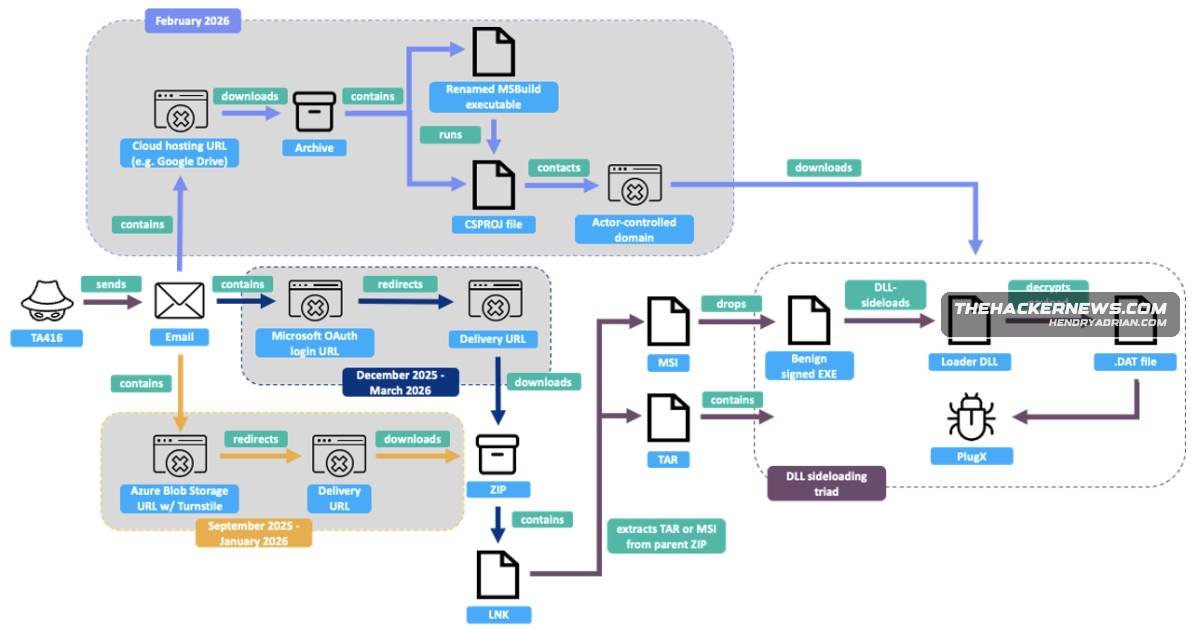
TA416 Uses Evolving PlugX Delivery Chains to Target European Governments

Proofpoint reports that TA416 resumed targeting European government and diplomatic organizations in mid-2025, using evolving phishing and PlugX delivery methods. The group also targeted Middle Eastern entities in early 2026.

Apr 4, 2026
Threat Research · securityonline.info

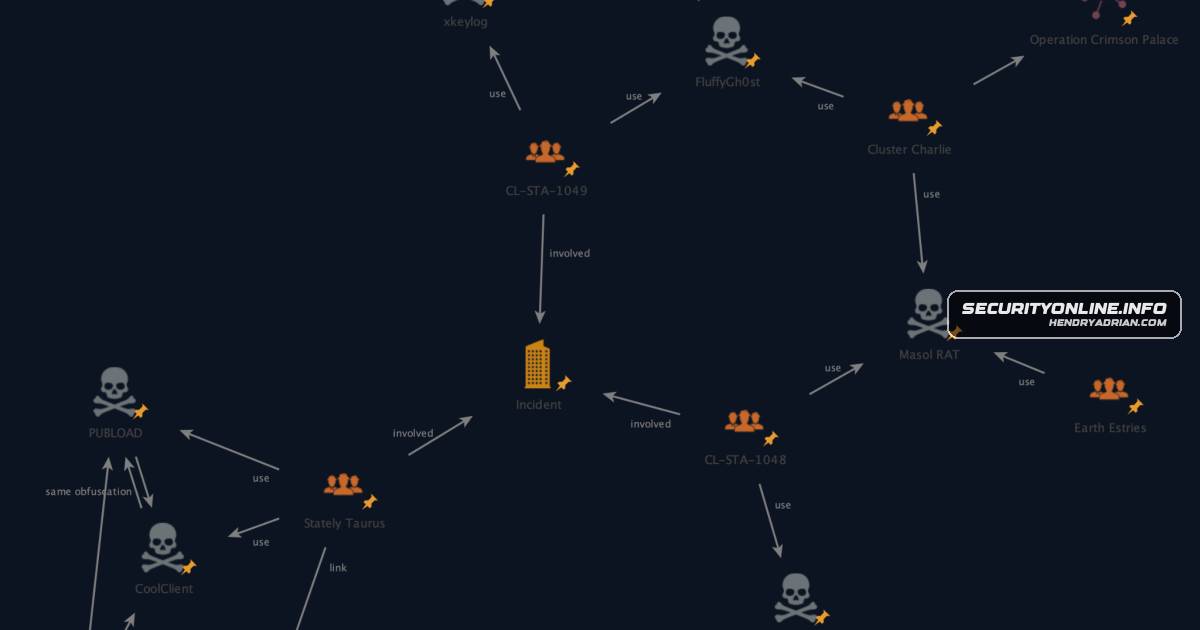
Unit 42 Details Three-Cluster Cyberespionage Campaign Targeting Southeast Asian Government

Unit 42 describes three clusters active from June to August 2025 against a Southeast Asian government target, using infected USB drives, varied backdoors and RATs, and DLL side-loading to maintain access and exfiltrate data.

Apr 3, 2026
Threat Research · trendmicro.com

Fake Claude Code Downloads Deliver Vidar Stealer and GhostSocks Malware

Trend Micro reports that attackers used fake GitHub repositories and trojanized 7z downloads, exploiting interest in Anthropic’s leaked Claude Code source to distribute a dropper that installs Vidar stealer and GhostSocks.

Apr 3, 2026
Threat Research · rapid7.com

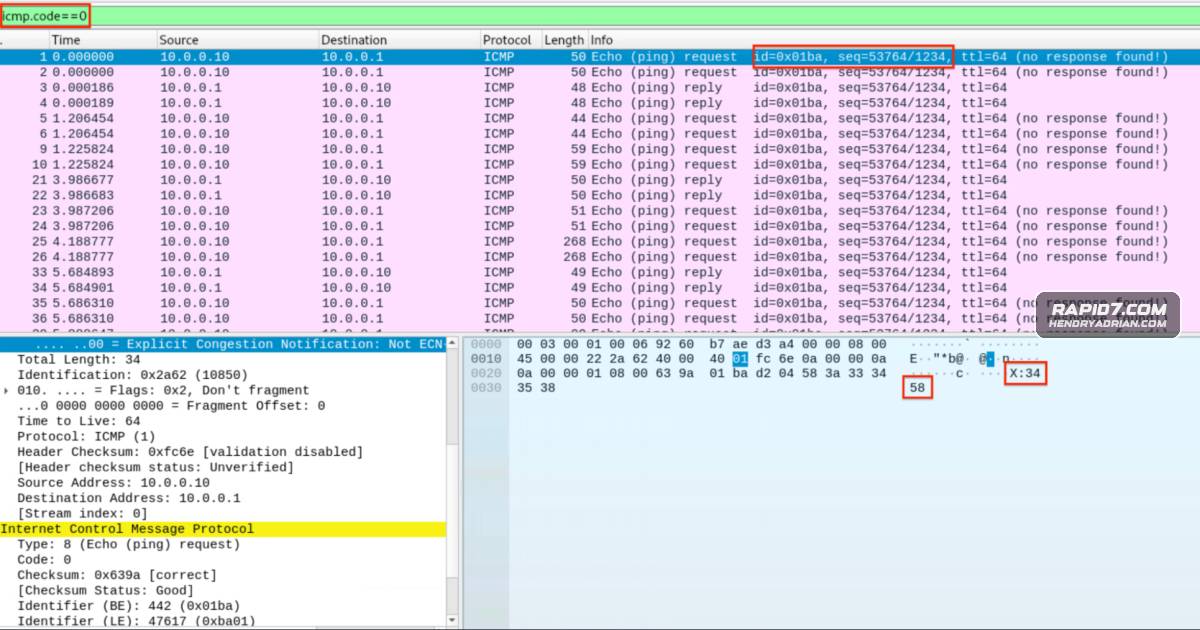
Rapid7 Details New BPFDoor Variants Using Protocol Tunneling and Stealthy C2

Rapid7 analyzes seven BPFDoor variants, detailing stealth techniques, multi-protocol triggers, ICMP shell tunneling, and an active beacon that disguises C2 as NTP-over-SSL. The research also identifies host and network detection markers.

Apr 2, 2026
Threat Research · esentire.com

Tycoon 2FA Operators Pivot to ProxyLine After Infrastructure Takedown

eSentire's TRU reports that Tycoon 2FA operators shifted authentication infrastructure after a global takedown while retaining the same phishing kit. Observed tactics include proxy rotation, geolocation-based evasion, and WebSocket capture of credentials and 2FA tokens.

Apr 2, 2026
Threat Research · thecyberexpress.com

FBI Details AVrecon Router Malware Used by SocksEscort Proxy Network

The article describes FBI findings that AVrecon infected routers in 163 countries for SocksEscort’s proxy network, detailing its infection and persistence methods, criminal uses, and recommended defenses.

Apr 2, 2026
Threat Research · thecyberexpress.com

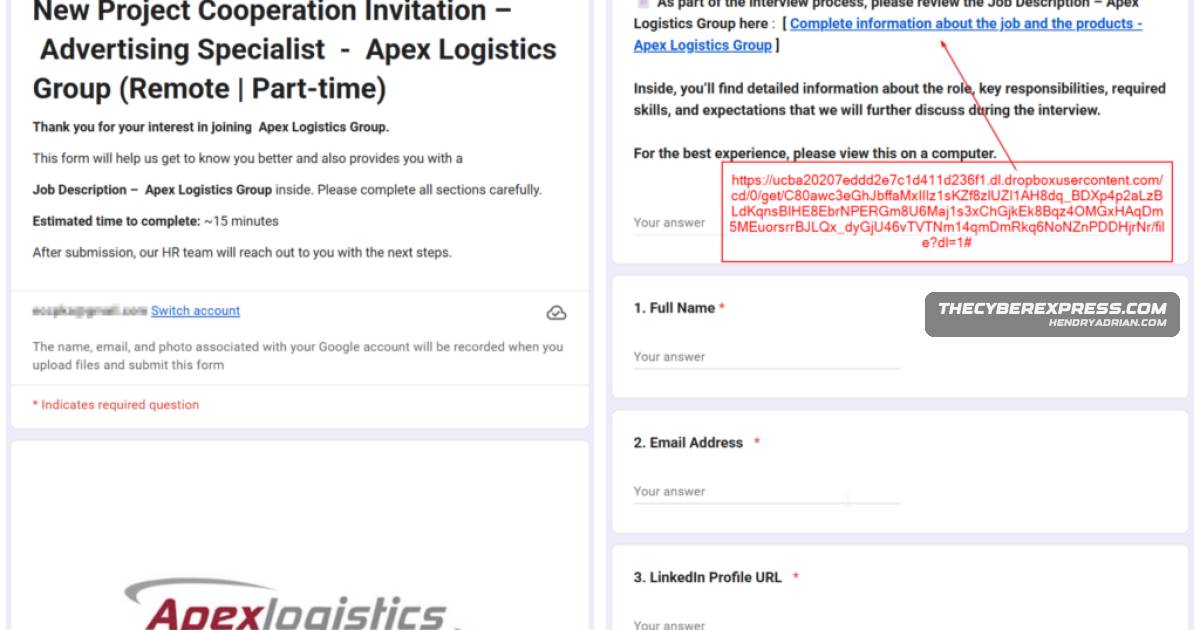
PXA Stealer Campaign Uses LinkedIn Recruiter Lures to Target Professionals

Cyble researchers attribute a multi-stage PXA Stealer campaign to Vietnam-linked actors using fake LinkedIn recruiters, Google Forms and DLL sideloading. The malware steals credentials and wallet data; researchers estimate more than 94,000 systems were infected.

Apr 2, 2026
Threat Research · microsoft.com

Malicious Axios npm Releases Deliver Sapphire Sleet RATs Across Three Operating Systems

Microsoft reports that malicious Axios releases 1.14.1 and 0.30.4 added a post-install dependency that fetched OS-specific RATs from a Sapphire Sleet C2. The investigation details the attack chain, Defender protections, and remediation.

Apr 2, 2026
Threat Research · thehackernews.com

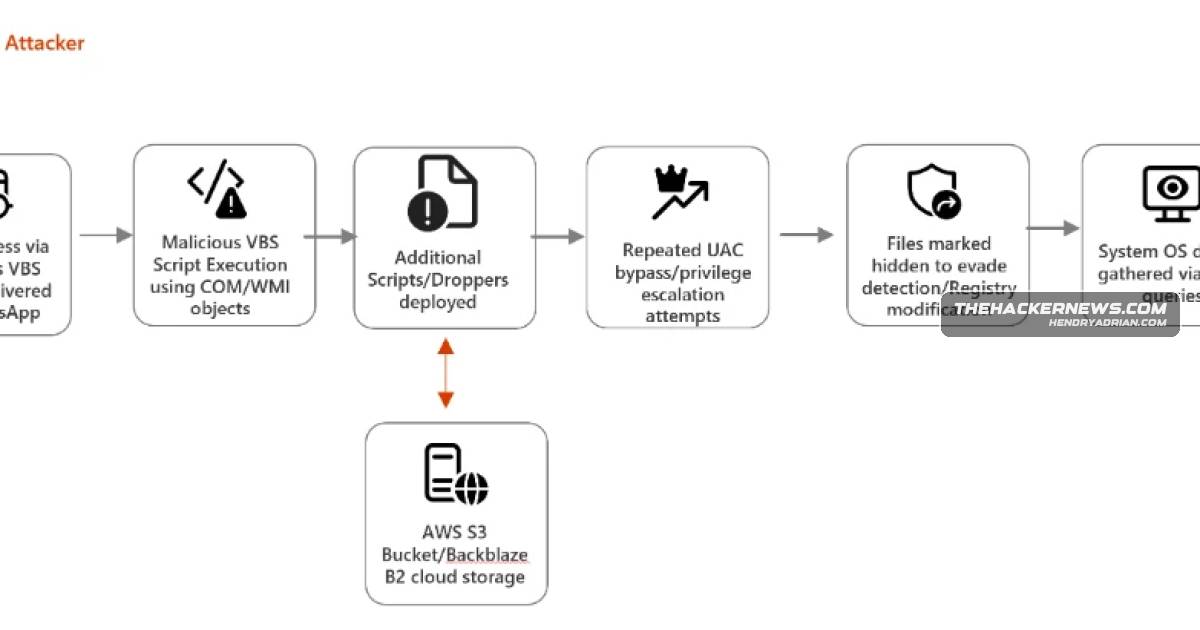
Microsoft Details WhatsApp-Delivered VBS Campaign Using UAC Bypass

Microsoft says a campaign active since late February 2026 uses WhatsApp-delivered VBS files, renamed Windows utilities and cloud-hosted payloads to alter UAC and registry settings and install unsigned MSI packages for persistent remote access.

Apr 2, 2026
Threat Research · asec.ahnlab.com

Kimsuky LNK Campaign Adds Multi-Stage Scripts to Deliver Python Backdoor

ASEC reports that a Kimsuky-attributed LNK campaign adds XML, VBS, PowerShell and BAT stages, uses scheduled tasks and Dropbox, and delivers Python malware with a custom C2 protocol supporting remote commands and file operations.

Apr 2, 2026
Threat Research · global.ptsecurity.com

Mythic Likho Uses Sophisticated Malware and Social Engineering to Attack Russian Critical Infrastructure

Positive Technologies researchers detail Mythic Likho’s phishing, custom loaders and Loki backdoor, credential theft, data exfiltration, and LockBit deployment against Russian organizations, and report evidence of links to (Ex)Cobalt.

Apr 2, 2026
Threat Research · unit42.paloaltonetworks.com

Axios Supply-Chain Attack Deploys Cross-Platform RAT via Malicious npm Dependency

Unit 42 details how hijacked Axios npm releases installed plain-crypto-js, whose obfuscated dropper downloaded platform-specific RATs. Researchers report WAVESHAPER overlap and recommend package audits, credential rotation, system rebuilds and blocking C2 at sfrclak[.]‌

Apr 1, 2026
Threat Research · cloud.google.com

GTIG Details Axios Supply-Chain Attack Delivering WAVESHAPER.V2 Backdoor

GTIG reports that a malicious dependency added to two axios releases on March 31, 2026, delivered the SILKBELL dropper and WAVESHAPER.V2 backdoor across Windows, macOS and Linux; it attributes the campaign to UNC1069 and recommends containment and credential rotation.

Apr 1, 2026
Threat Research · proofpoint.com

TA416 Resumes Espionage Campaigns Against European Governments, Expands Into Middle East

Proofpoint details TA416’s renewed espionage targeting of European governments from mid-2025 and Middle Eastern entities in March 2026, describing evolving phishing and malware-delivery chains that deploy a custom PlugX backdoor.

Apr 1, 2026
Threat Research · bleepingcomputer.com

NoVoice Malware Found in 50+ Google Play Apps With 2.3 Million Installs

McAfee detailed NoVoice, found in 50+ Google Play apps with at least 2.3 million installs. It uses exploits to root Android devices, persist through factory resets, and steal WhatsApp session data; the apps have been removed.

Apr 1, 2026
Threat Research · socket.dev

Compromised Axios npm Releases Deliver Trojanized Dependency and RAT

Socket traced compromised Axios releases 1.14.1 and 0.30.4 to [email protected], whose postinstall dropper delivers platform-specific payloads. Analysis of the macOS RAT found command execution, host-data collection and persistence capabilities.

Apr 1, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details TeamPCP Supply-Chain Attacks on Trivy, KICS, LiteLLM and Telnyx

Unit 42 details TeamPCP’s Feb–Mar 2026 compromise of Trivy, KICS, LiteLLM and Telnyx packages, describing credential theft, CanisterWorm’s ICP-based C2 and wiper, and mitigations. Exfiltration scale is reported, not independently established here.

Apr 1, 2026
Threat Research · securelist.com

CrystalX RAT Combines Stealer, Spyware and Prankware Capabilities

Kaspersky describes CrystalX, a MaaS RAT promoted since early 2026, with credential theft, keylogging, clipboard manipulation, remote control and prankware. Its initial infection vector is unknown; telemetry indicates dozens of victims and ongoing development.

Apr 1, 2026
Threat Research · elastic.co

Elastic Details axios npm Supply-Chain Compromise Delivering Cross-Platform RAT

Elastic Security Labs details how a compromised axios maintainer account published backdoored npm releases that installed a cross-platform RAT via plain-crypto-js; its three variants shared C2 behavior, while a spoofed IE8 user-agent offers a detection signal.

Apr 1, 2026
Threat Research · research.checkpoint.com

TrueConf Zero-Day Exploited in Southeast Asian Government Campaign

Check Point Research reports CVE-2026-3502 was exploited through TrueConf’s on-premises update flow against Southeast Asian government entities, with the missing final payload assessed as likely Havoc. TrueConf fixed the flaw in Windows client 8.5.3.

Apr 1, 2026
Threat Research · team-cymru.com

Team Cymru Maps Yurei Ransomware Operators’ Toolkit and Attack Chain

Team Cymru analyzed files from two Yurei operator open directories, mapping likely credential use, reconnaissance, privilege escalation, persistence, defense evasion and lateral movement. The directories suggest activity in January 2026, though no new victims had been.

Apr 1, 2026
Threat Research · cloudsek.com

Supply-Chain Attacks Turn Security and DevSecOps Tools into Credential-Theft Paths

An analysis of supply-chain compromises affecting XZ Utils, GitHub Actions dependencies, Trivy, and LiteLLM describes how attackers abused trusted tools and release paths to steal credentials, and outlines defensive measures.

Apr 1, 2026
PreviousPage 73 of 104 Next
© 2026 cyber.hendryadrian.com