cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2491 articles

Threat Research · thecyberexpress.com

ClickFix-Style macOS Attack Uses Script Editor to Deliver Atomic Stealer

A reported ClickFix-style macOS campaign uses an Apple-themed webpage and applescript:// workflow to launch an obfuscated script in Script Editor, download a Mach-O binary, and run an Atomic Stealer variant.
Apr 9, 2026
Threat Research · socket.dev

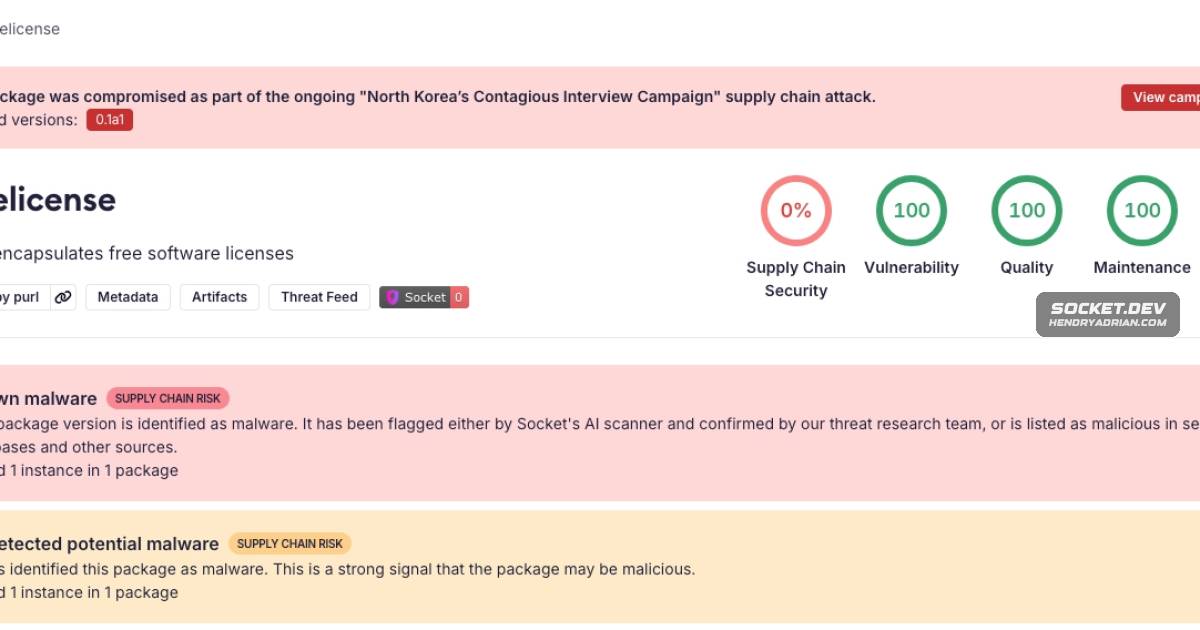
Contagious Interview Campaign Spreads Malicious Packages Across Five Ecosystems

Socket's investigation links Contagious Interview packages across npm, PyPI, Go Modules, crates.io and Packagist. The loaders hide in routine APIs and fetch second-stage payloads; a Windows variant includes RAT capabilities. Some packages were removed after reporting.

Apr 9, 2026
Threat Research · rapid7.com

Rapid7 Details FortiGate CVE-2025-59718 Exploitation and Incident Response Findings

Rapid7’s incident response team reports that attackers exploited CVE-2025-59718 to bypass FortiGate SSO, create accounts, download configurations, and enter an internal network. The investigation traces credential theft, lateral movement, and detection opportunities.

Apr 9, 2026
Threat Research · microsoft.com

Forest Blizzard Used Compromised SOHO Routers for DNS Hijacking and TLS AiTM Attacks

Microsoft reports that Forest Blizzard and Storm-2754 compromised SOHO routers to hijack DNS and selectively conduct TLS AiTM attacks. The activity affected over 200 organizations and 5,000 consumer devices; Microsoft also shared detection and mitigation guidance.

Apr 9, 2026
Threat Research · cloudsek.com

CloudSek Report Warns of Iranian-Linked Cyber Pre-Positioning Across Gulf Networks

CloudSek describes alleged APT35 access across several Gulf networks, outlines Iranian-linked actors, malware and exploited vulnerabilities, and recommends urgent patching, IOC blocking, credential rotation and compromise assessments.

Apr 9, 2026
Threat Research · zscaler.com

Fake Acrobat Download Uses Obfuscated Loaders to Install ScreenConnect

Zscaler ThreatLabz details a February 2026 attack using a fake Acrobat download to deliver ScreenConnect through obfuscated scripts, in-memory .NET execution, process masquerading, and a COM-based UAC bypass.

Apr 9, 2026
Threat Research · gendigital.com

Researchers Link Remus 64-Bit Infostealer to Lumma Stealer

Gen Threat Labs attributes the 64-bit Remus infostealer to Lumma based on shared code and techniques, including an Application-Bound Encryption bypass. The analysis details Remus’s EtherHiding C2 resolution and added anti-analysis checks.

Apr 8, 2026
Threat Research · securityweek.com

Trellix Details Masjesu DDoS Botnet’s IoT Infection and Evasion Techniques

Trellix details Masjesu, an IoT botnet active since at least 2023. It spreads by scanning for vulnerable devices, uses process masquerading and cron jobs for persistence, and supports multiple DDoS attack types.

Apr 8, 2026
Threat Research · opensourcemalware.com

Malicious Code in Velora SDK 9.4.1 Downloads and Runs a Remote Shell Script

An analysis found that @velora-dex/sdk 9.4.1 runs an obfuscated payload on import, downloading and executing a shell script from 89.36.224.5. The article says versions 9.4.2 and later are clean.

Apr 8, 2026
Threat Research · hunt.io

Researchers uncover Canis cross-platform surveillance framework targeting Japan

Hunt.io researchers found an exposed, unauthenticated C2 and source code for Canis, a cross-platform surveillance framework delivered through Japanese-themed phishing. Its API was secured on March 21, while related phishing infrastructure appeared afterward.

Apr 8, 2026
Threat Research · lookout.com

Lookout Links MENA Civil Society Espionage Campaign to BITTER-Associated Hack-for-Hire Operation

Lookout and Access Now describe a campaign targeting Middle Eastern civil society members since at least 2022, using spearphishing, credential theft and Android spyware called ProSpy. Lookout assesses links to BITTER with moderate confidence.

Apr 8, 2026
Threat Research · blog.sekoia.io

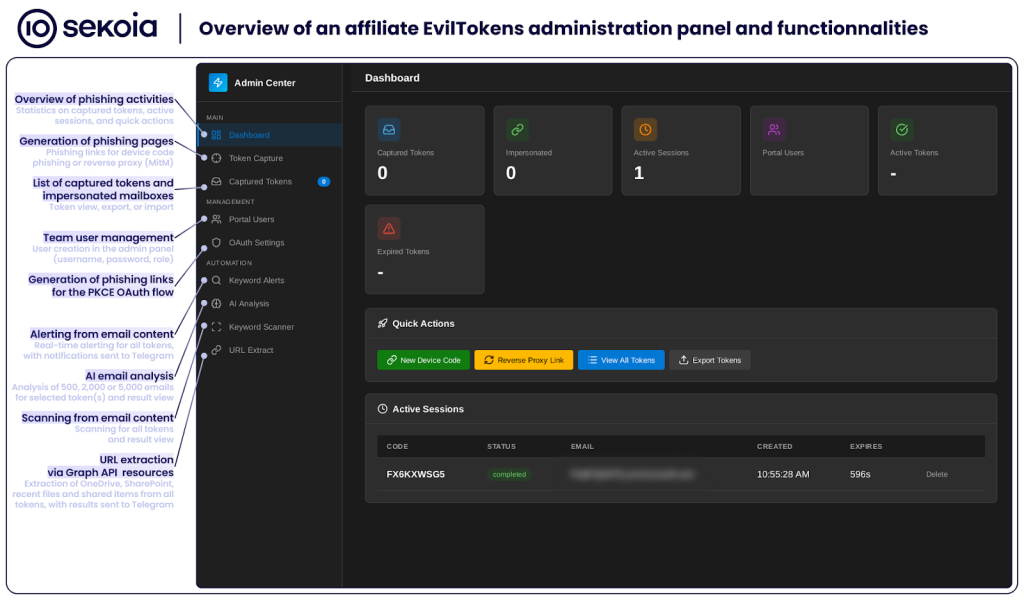
Sekoia Details EvilTokens PhaaS That Automates BEC Reconnaissance with AI

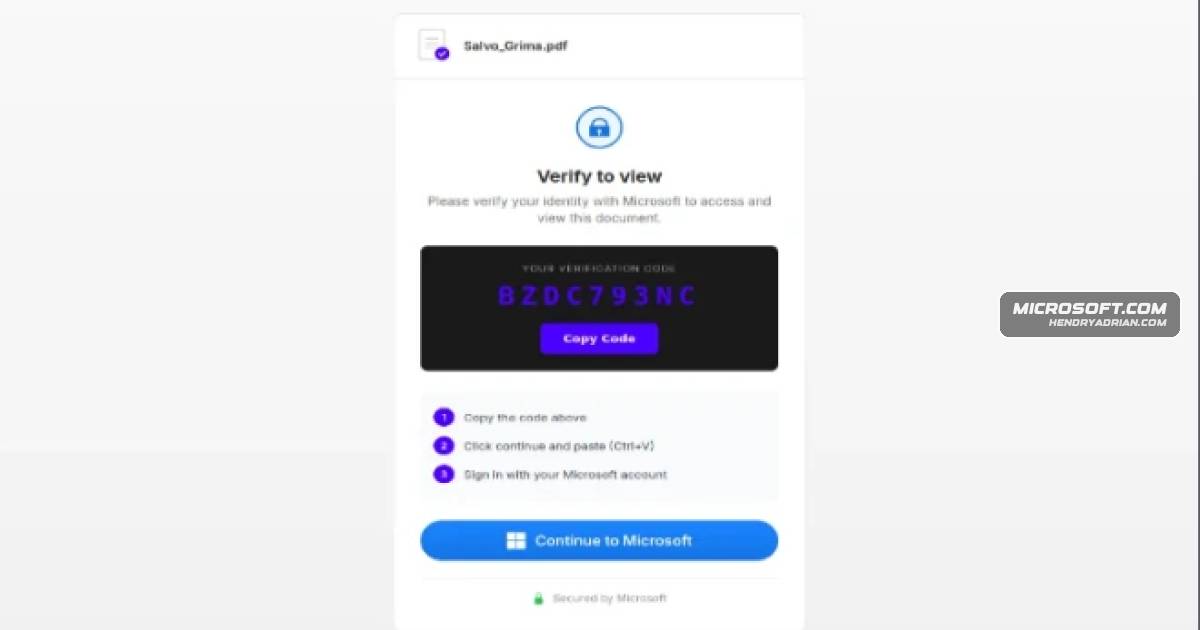
Sekoia analyzes EvilTokens, a Microsoft device-code phishing service that uses harvested tokens for mailbox access and Graph reconnaissance, then applies chained LLMs to identify financial threads and draft tailored BEC scenarios.

Apr 7, 2026
Threat Research · microsoft.com

Microsoft Details Storm-1175’s Exploitation and Medusa Ransomware Operations

Microsoft describes Storm-1175 exploiting web-facing vulnerabilities, using remote-management and credential-theft tools, and deploying Medusa ransomware. The report details observed attack techniques and recommends perimeter, credential, and endpoint defenses.

Apr 7, 2026
Threat Research · ncsc.gov.uk

APT28 Exploits SOHO Routers to Hijack DNS and Steal Credentials

NCSC details how APT28 exploited SOHO routers, including TP-Link devices, to redirect DNS queries and conduct adversary-in-the-middle attacks aimed at stealing passwords and authentication tokens.

Apr 7, 2026
Threat Research · netskope.com

Netskope Details ClickFix Campaign Delivering Modular Node.js RAT

Netskope Threat Labs details a ClickFix campaign using a silently installed Node.js payload on Windows. Dynamic modules, gRPC-over-Tor C2 and leaked protocol files expose RAT capabilities and a multi-operator MaaS backend.

Apr 7, 2026
Threat Research · microsoft.com

Microsoft Details Storm-2372’s AI-Enabled OAuth Device-Code Phishing Campaign

Microsoft describes Storm-2372’s device-code phishing campaign, detailing how dynamic code generation enabled token theft and how attackers used compromised accounts for reconnaissance, persistence and email exfiltration.

Apr 7, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details Kubernetes Token Theft and React2Shell Attacks Enabling Cloud Compromise

Unit 42 reports a 282% year-over-year rise in Kubernetes-related token-theft activity and details two attack cases involving service-account token abuse and React2Shell. The article explains cloud-pivot techniques and defensive controls.

Apr 7, 2026
Threat Research · stepsecurity.io

Malicious @velora-dex/sdk 9.4.1 Uses Import-Time Payload to Install macOS Backdoor

StepSecurity analyzed malicious @velora-dex/sdk 9.4.1, which runs on import and contacts a C2 server. Its macOS payload drops an architecture-specific binary and registers launchctl persistence; the article provides investigation findings and recovery steps.

Apr 7, 2026
Threat Research · huntress.com

Huntress Finds NightSpire Ransomware Tactics Vary Across Attacks

Huntress compares two NightSpire ransomware incidents, detailing RDP access and attacker tools used for persistence, file collection and likely exfiltration. Different tactics and ransom-note files leave NightSpire’s RaaS status uncertain.

Apr 7, 2026
Threat Research · cloudsek.com

Traffic Broker Uses Localized Brand-Themed Lures to Funnel Users to Scams

Researchers identified a traffic-broker operation using hundreds of short-lived, localized promotional sites that impersonate familiar brands to attract mobile users and route traffic to downstream scams, including pig-butchering schemes and Telegram account hacking.

Apr 7, 2026
Threat Research · dti.domaintools.com

Handala, Homeland Justice and Karma Assessed as One Iran-Aligned Cyber Influence Ecosystem

The assessment links Homeland Justice, Karma and Handala to a unified MOIS-aligned ecosystem combining low-complexity intrusions, surveillance, data leaks and coordinated messaging to magnify psychological and reputational impact.

Apr 6, 2026
Threat Research · cisecurity.org

Vimeo-Themed Phishing Campaign Steals Personal and Banking Data

CIS analyzed a phishing campaign targeting U.S. SLTT entities with Vimeo-themed lures to harvest personal and banking data, alongside related tax-themed infrastructure delivering Datto RMM. CIS shared indicators and blocked associated domains.

Apr 6, 2026
Threat Research · hexastrike.com

Reddit TradingView Lures Deliver Vidar and AMOS Stealers

A threat actor used Reddit posts promoting cracked TradingView builds to distribute Vidar on Windows and AMOS on macOS. The active campaign used hijacked websites, password-protected archives, and social engineering to steal credentials and other data.

Apr 5, 2026
Threat Research · thehackernews.com

36 Malicious npm Packages Abuse Redis and PostgreSQL to Target Strapi Installations

SafeDep identified 36 malicious npm packages impersonating Strapi plugins. Their install hooks attempted Redis and PostgreSQL exploitation, credential theft, and persistent access, with cryptocurrency-related data among the targets. Users who installed them are advised,

Apr 5, 2026
PreviousPage 72 of 104 Next
© 2026 cyber.hendryadrian.com