
Unit 42 Details Three-Cluster Cyberespionage Campaign Targeting Southeast Asian Government
Summary
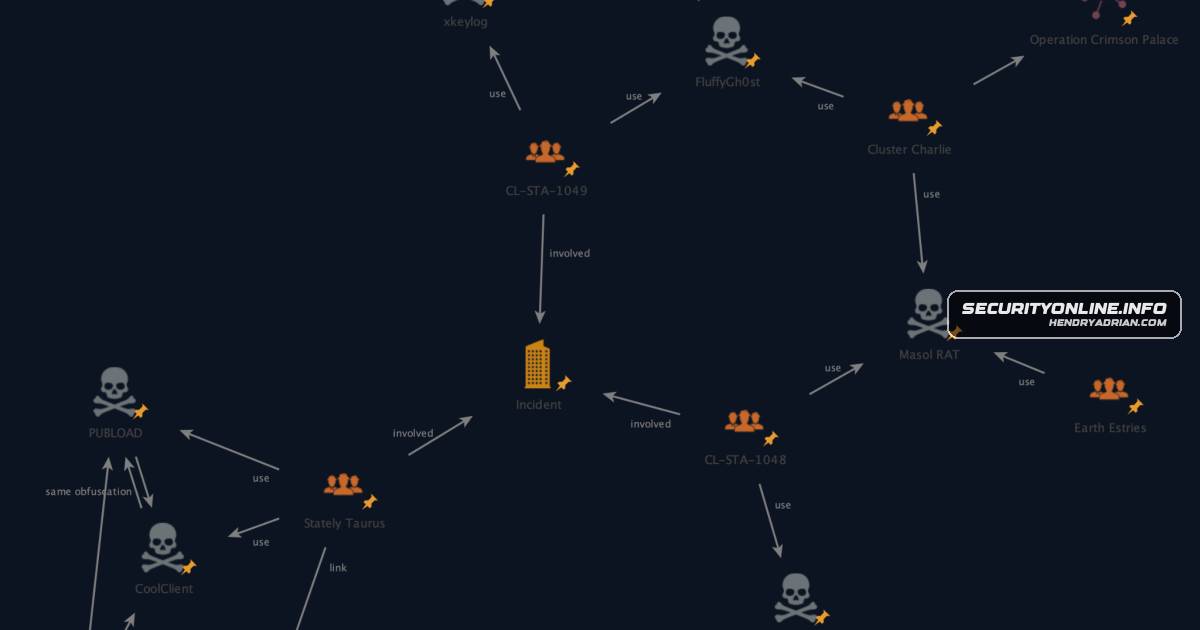
Unit 42 describes three clusters active from June to August 2025 against a Southeast Asian government target, using infected USB drives, varied backdoors and RATs, and DLL side-loading to maintain access and exfiltrate data.
Key points
- Unit 42 reported three concurrent activity clusters targeting a Southeast Asian government organization from June to August 2025, with links to China-aligned actors.
- Stately Taurus was attributed with high confidence to a cluster using infected USB drives and the USBFect worm to spread PUBLOAD.
- PUBLOAD reportedly used a fake TLS header to mask communications while exfiltrating system data.
- CL-STA-1048 used EggStremeFuel, Masol RAT, Gorem RAT, and TrackBak, which the article describes as tools for backdoor access, remote control, and information theft.
- CL-STA-1049 used the Hypnosis loader to DLL-side-load FluffyGh0st through a legitimate Bitdefender executable and keep the host process running.
- The report characterizes the campaign's objective as persistent, stealthy data collection and exfiltration rather than disruption.
Article Details
- Attack Vectors
- USBFect (HIUPAN) spread through infected removable media and deployed the PUBLOAD backdoor.
- CL-STA-1048 used a multi-payload strategy involving EggStremeFuel, Masol RAT, Gorem RAT, and TrackBak.
- CL-STA-1049 used DLL side-loading against a legitimate Bitdefender executable to deploy the Hypnosis loader and FluffyGh0st RAT.
MITRE ATT&CK
T1001.003 · Protocol or Service ImpersonationPUBLOAD used a fake TLS header (17 03 03) over TCP to mask its communications.T1005 · Data from Local SystemThe campaign's backdoors and infostealer collected system data, keylogs, and clipboard data.T1036 · MasqueradingTrackBak masqueraded as an MS Edge log file.T1041 · Exfiltration Over C2 ChannelPUBLOAD exfiltrated system data while communicating with a fake TLS header.T1056.001 · KeyloggingTrackBak gathered keystrokes.T1071.001 · Web ProtocolsMasol RAT is described as an HTTP-based Trojan.T1091 · Replication Through Removable MediaUSBFect propagated through infected removable media.T1115 · Clipboard DataTrackBak gathered clipboard data.T1574.002 · DLL Side-LoadingHypnosis used DLL side-loading against a legitimate Bitdefender executable to deploy FluffyGh0st.
Threat Actors
CL-STA-1048This activity cluster deployed EggStremeFuel, Masol RAT, Gorem RAT, and TrackBak in the campaign.CL-STA-1049This activity cluster used the Hypnosis loader and DLL side-loading to deploy FluffyGh0st.Mustang PandaThe article attributes the USBFect/PUBLOAD activity to Stately Taurus with high confidence.Unfading Sea HazeThe article links the campaign's activity clusters to groups including Unfading Sea Haze; it does not specify this group's particular actions.
Malware
EggStremeFuelThe clusters used USBFect/PUBLOAD via infected removable media, a multi-payload toolkit including EggStremeFuel and Masol/Gorem/TrackBak, and the Hypnosis loader delivering FluffyGh0st to maintain stealthy, long-termFluffyGh0sttoolkit including EggStremeFuel and Masol/Gorem/TrackBak, and the Hypnosis loader delivering FluffyGh0st to maintain stealthy, long-term data exfiltration.Gorem RATCL-STA-1048 deployed diverse tooling—EggStremeFuel, Masol RAT, Gorem RAT, and TrackBak—to bypass XDR and establish footholds.HIUPANStately Taurus used infected USB drives and the USBFect (HIUPAN) worm to deploy the PUBLOAD backdoor and exfiltrate data with a fake TLS header.Hypnosisremovable media, a multi-payload toolkit including EggStremeFuel and Masol/Gorem/TrackBak, and the Hypnosis loader delivering FluffyGh0st to maintain stealthy, long-term data exfiltration.Masol RATCL-STA-1048 deployed diverse tooling—EggStremeFuel, Masol RAT, Gorem RAT, and TrackBak—to bypass XDR and establish footholds.PubloadThe clusters used USBFect/PUBLOAD via infected removable media, a multi-payload toolkit including EggStremeFuel and Masol/Gorem/TrackBak, and the Hypnosis loader delivering FluffyGh0st to maintain stealthy, long-termTrackBakvia infected removable media, a multi-payload toolkit including EggStremeFuel and Masol/Gorem/TrackBak, and the Hypnosis loader delivering FluffyGh0st to maintain stealthy, long-term data exfiltration.USBFectThe clusters used USBFect/PUBLOAD via infected removable media, a multi-payload toolkit including EggStremeFuel and Masol/Gorem/TrackBak, and the Hypnosis loader delivering FluffyGh0st to maintain stealthy, long-term