
CrystalX RAT Combines Stealer, Spyware and Prankware Capabilities
Summary
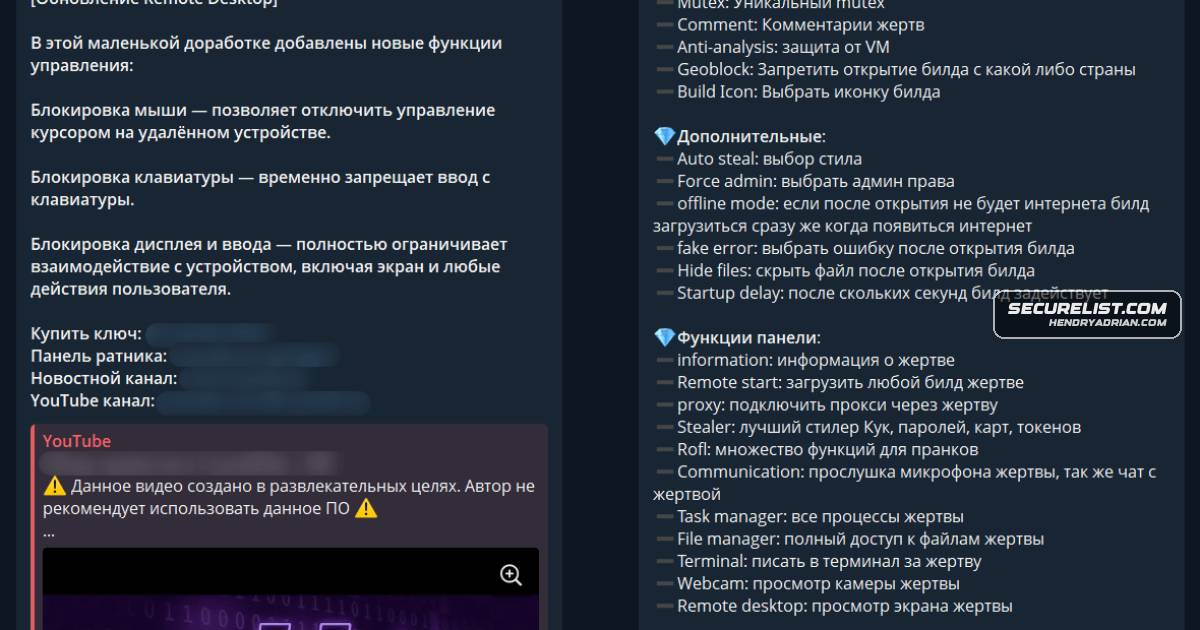
Kaspersky describes CrystalX, a MaaS RAT promoted since early 2026, with credential theft, keylogging, clipboard manipulation, remote control and prankware. Its initial infection vector is unknown; telemetry indicates dozens of victims and ongoing development.
Key points
- CrystalX RAT, initially promoted as Webcrystal RAT, is sold as malware-as-a-service through Telegram and a YouTube channel.
- Its builder supports geoblocking and anti-analysis features; implants are compressed with zlib and encrypted with ChaCha20.
- The RAT can steal credentials and browser data, log keystrokes, and send collected information to its command-and-control server over WebSocket. Builds observed when the article was written lacked the stealer component.
- A clipper can inject a malicious extension into Chrome or Edge through the Chrome DevTools Protocol to replace cryptocurrency wallet addresses.
- Remote-access features include file upload, command execution, VNC, and background microphone and camera capture.
- The “Rofl” module can disrupt normal desktop use with actions such as rotating the display, remapping mouse buttons, and disabling system components.
- The initial infection vector is unknown. Researchers report infection attempts in Russia, dozens of victims, and telemetry indicating continued development.
Article Details
- Attack Vectors
- The initial infection vector is not known. Infection attempts had been observed in Russia.
- CrystalX RAT communicates with its C2 over WebSocket using a hard-coded URL; the article does not provide the URL.
- The malware can steal credentials and browser data, log keystrokes, access and modify the clipboard, and capture microphone audio and camera video.
- The RAT supports remote file upload, command execution through cmd.exe, filesystem browsing, and remote desktop control through its integrated VNC.
- A clipper can inject a malicious browser extension into Chrome or Edge through the Chrome DevTools protocol to replace cryptocurrency wallet addresses.
- Defensive Notes
- Kaspersky products detect the threat as Backdoor.Win64.CrystalX.*, Trojan.Win64.Agent.*, and Trojan.Win32.Agentb.gen.
- The malware checks for proxies, analysis processes and certificates, virtual-machine indicators, and debugging conditions; it also patches AmsiScanBuffer, EtwEventWrite, and MiniDumpWriteDump.
- The article reports that builds available at the time lacked the stealer component, which the author had reportedly removed while updating it.
- The article lists three C2 domains and six implant MD5 hashes as indicators.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | crystalxrat[.]top | Listed as CrystalX RAT C2 infrastructure. |
| DOMAIN | webcrystal[.]lol | Listed as CrystalX RAT C2 infrastructure. |
| DOMAIN | webcrystal[.]sbs | Listed as CrystalX RAT C2 infrastructure. |
| MD5 | 1a68ae614fb2d8875cb0573e6a721b46 | Listed as a CrystalX RAT implant hash. |
| MD5 | 2dbe6de177241c144d06355c381b868c | Listed as a CrystalX RAT implant hash. |
| MD5 | 47accb0ecfe8ccd466752dde1864f3b0 | Listed as a CrystalX RAT implant hash. |
| MD5 | 49c74b302bfa32e45b7c1c5780dd0976 | Listed as a CrystalX RAT implant hash. |
| MD5 | 88c60df2a1414cbf24430a74ae9836e0 | Listed as a CrystalX RAT implant hash. |
| MD5 | e540e9797e3b814bfe0a82155dfe135d | Listed as a CrystalX RAT implant hash. |
MITRE ATT&CK
T1021 · Remote ServicesThe RAT's integrated VNC allows the operator to view and control the victim's desktop remotely.T1027 · Obfuscated Files or InformationThe builder compresses implants with zlib and encrypts them with ChaCha20.T1041 · Exfiltration Over C2 ChannelThe malware sends collected data to its C2 over the established channel as plain-text JSON.T1056.001 · KeyloggingThe keylogger captures user input and transmits it to the C2 over WebSocket.T1059.003 · Windows Command ShellThe operator can execute commands through cmd.exe using the RAT.T1071.001 · Web ProtocolsCrystalX RAT uses WebSocket over a hard-coded URL to communicate with its C2.T1113 · Screen CaptureThe operator can view the victim's screen through the RAT's remote-access capabilities.T1115 · Clipboard DataThe malware can read and modify the victim's clipboard and replace cryptocurrency addresses through its clipper.T1123 · Audio CaptureThe malware can capture audio from the victim's microphone in the background.T1125 · Video CaptureThe malware can capture video from the victim's camera in the background.T1497 · Virtualization/Sandbox EvasionThe malware checks for virtual-machine indicators, including running processes, guest tools, and hardware characteristics.T1555.003 · Credentials from Web BrowsersThe stealer extracts credentials for Steam, Discord, and Telegram and gathers data from Chromium-based browsers using ChromeElevator.T1562 · Impair DefensesThe malware patches AmsiScanBuffer, EtwEventWrite, and MiniDumpWriteDump.
Malware
CrystalX RATCrystalX RAT combines standard RAT features (remote access, VNC, file operations) with stealer, keylogger, clipper, spyware, and unusual prankware capabilities accessible from the operator panel.Webcrystal RATThe author actively promoted their creation, called Webcrystal RAT, by attaching screenshots of the web panel.
Vendors
Products
DiscordThe stealer exfiltrates credentials for Steam, Discord, Telegram and data from Chromiumâbased browsers (using ChromeElevator); builds available at the time lacked the stealer while the author updates that component.EdgeMoreover, it can inject a malicious clipper into the Chrome or Edge browser.Google ChromeKeylogger and clipboard functionality transmit input and clipboard changes via WebSocket to C2; a clipper injects a malicious browser extension via the Chrome DevTools protocol to swap crypto wallet addresses.OperaFor Yandex and Opera browsers, the stealer has a separate proprietary implementation with base decryption directly on the victim’s system.SteamThe stealer exfiltrates credentials for Steam, Discord, Telegram and data from Chromiumâbased browsers (using ChromeElevator); builds available at the time lacked the stealer while the author updates that component.Telegraman active MaaS campaign promoting CrystalX (initially marketed as Webcrystal/WebRAT) via private Telegram chats and a YouTube channel; the RAT offers a builder and a wide feature set including stealer,YandexFor Yandex and Opera browsers, the stealer has a separate proprietary implementation with base decryption directly on the victim’s system.