
TA416 Uses Evolving PlugX Delivery Chains to Target European Governments
Summary
Proofpoint reports that TA416 resumed targeting European government and diplomatic organizations in mid-2025, using evolving phishing and PlugX delivery methods. The group also targeted Middle Eastern entities in early 2026.
Key points
- Proofpoint attributed multiple waves of web-bug and malware-delivery campaigns against European diplomatic and government organizations to TA416.
- Reported delivery methods included Cloudflare Turnstile pages, OAuth redirects, and malicious archives hosted on cloud storage or compromised SharePoint.
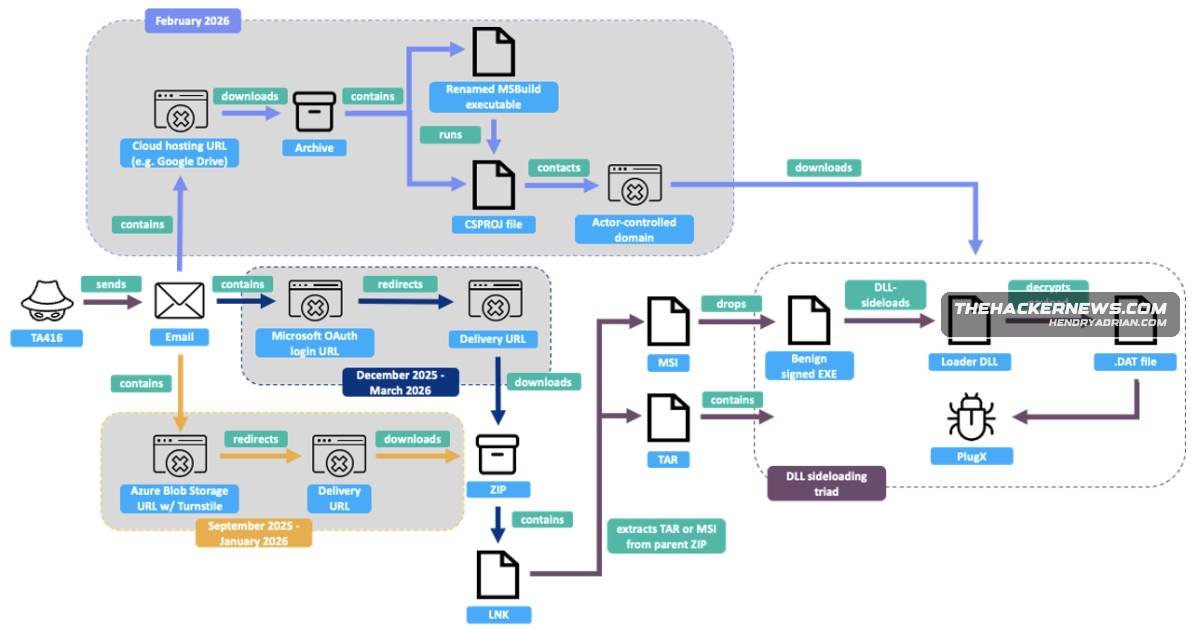
- In February 2026 activity, a malicious C# project file reportedly decoded URLs, retrieved DLL side-loading components, and launched PlugX through a legitimate executable.
- PlugX variants reportedly perform anti-analysis checks, communicate with a command-and-control server, and support system reconnaissance, payload execution, beacon adjustment, reverse shells, and removal.
- Proofpoint reported that TA416 also targeted Middle Eastern government entities in early 2026, likely in response to regional geopolitical developments.
Article Details
- Attack Vectors
- TA416 used web bugs in emails to determine whether intended recipients opened messages.
- Phishing emails used OAuth redirects through Microsoft Entra ID applications to lead recipients to attacker-controlled domains and malicious archives.
- Malicious archives delivered PlugX, including through Azure Blob Storage, Google Drive, attacker-controlled domains, and compromised SharePoint instances.
- A malicious C# project file used MSBuild to decode Base64-encoded URLs, download a DLL side-loading triad, and launch PlugX using a legitimate executable.
- PlugX performed anti-analysis checks and established an encrypted C2 channel.
MITRE ATT&CK
T1059.003 · Windows Command ShellA PlugX command opened a reverse command shell.T1082 · System Information DiscoveryA PlugX command captured system information.T1105 · Ingress Tool TransferThe C# project file downloaded a DLL side-loading triad from a TA416-controlled domain, and PlugX could download and execute additional payloads.T1127.001 · MSBuildA malicious C# project file was executed through the legitimate MSBuild executable to download components used to deploy PlugX.T1566.002 · Spearphishing LinkTA416 phishing emails linked to OAuth redirects that led recipients to attacker-controlled domains and malicious archives.T1573 · Encrypted ChannelPlugX established an encrypted communication channel with its C2 server.T1574.002 · DLL Side-LoadingTA416 used legitimate executables to load PlugX through DLL side-loading.
People
Threat Actors
CerenaKeeperThe article explicitly identifies CerenaKeeper as an alternate name for Mustang Panda.DarkPeonyThe article describes DarkPeony as an activity cluster with technical or activity overlap with TA416; it does not state that DarkPeony conducted the reported campaigns.Mustang PandaThe article describes Mustang Panda as a cluster with historical technical overlap with TA416 and says it has deployed TONESHELL, PUBLOAD, and COOLCLIENT. The article explicitly lists CerenaKeeper, Red Ishtar, and UNK_SteadySplit as alternate names for Mustang Panda.Red IshtarThe article explicitly identifies Red Ishtar as an alternate name for Mustang Panda.Red LichThe article describes Red Lich as an activity cluster with technical or activity overlap with TA416; it does not state that Red Lich conducted the reported campaigns.RedDeltaThe article describes RedDelta as an activity cluster with technical or activity overlap with TA416; it does not state that RedDelta conducted the reported campaigns.SmugXThe article describes SmugX as an activity cluster with technical or activity overlap with TA416; it does not state that SmugX conducted the reported campaigns.TA416The article attributes campaigns targeting European government and diplomatic organizations from mid-2025, and Middle Eastern government entities in 2026, to TA416.UNC6384The article describes UNC6384 as an activity cluster with technical or activity overlap with TA416; it does not state that UNC6384 conducted the reported campaigns.UNK_SteadySplitThe article explicitly identifies UNK_SteadySplit as an alternate name for Mustang Panda.Vertigo PandaThe article describes Vertigo Panda as an activity cluster with technical or activity overlap with TA416; it does not state that Vertigo Panda conducted the reported campaigns.
Malware
CoolClientWhile TA416’s attacks are characterized by the use of bespoke PlugX variants, the Mustang Panda cluster has repeatedly deployed tools like TONESHELL, PUBLOAD, and COOLCLIENT in recent attacks.PlugX#TA416PubloadWhile TA416’s attacks are characterized by the use of bespoke PlugX variants, the Mustang Panda cluster has repeatedly deployed tools like TONESHELL, PUBLOAD, and COOLCLIENT in recent attacks.TONESHELLWhile TA416’s attacks are characterized by the use of bespoke PlugX variants, the Mustang Panda cluster has repeatedly deployed tools like TONESHELL, PUBLOAD, and COOLCLIENT in recent attacks.
Vendors
CloudflareThe group repeatedly modified its infection techniques—abusing Cloudflare Turnstile, OAuth redirects, MSBuild/C# project files, and hosting payloads on Azure Blob Storage, Google Drive, and compromised SharePoint—whileGoogleTurnstile, OAuth redirects, MSBuild/C# project files, and hosting payloads on Azure Blob Storage, Google Drive, and compromised SharePoint—while expanding operations to Middle Eastern targets in early 2026.Microsoftaccounts to conduct reconnaissance and deploy the PlugX backdoor via malicious archives hosted on Microsoft Azure Blob Storage, Google Drive, domains under their control, and compromised SharePoint instances.
Products
Cloudflare TurnstileThe group repeatedly modified its infection techniques—abusing Cloudflare Turnstile, OAuth redirects, MSBuild/C# project files, and hosting payloads on Azure Blob Storage, Google Drive, and compromised SharePoint—whileGoogle DriveTurnstile, OAuth redirects, MSBuild/C# project files, and hosting payloads on Azure Blob Storage, Google Drive, and compromised SharePoint—while expanding operations to Middle Eastern targets in early 2026.Microsoft Azure Blob StorageCloudflare Turnstile, OAuth redirects, MSBuild/C# project files, and hosting payloads on Azure Blob Storage, Google Drive, and compromised SharePoint—while expanding operations to Middle Eastern targets inMicrosoft Entra IDAttacks carried out by TA416 in December 2025 have been found to leverage third-party Microsoft Entra ID cloud applications to initiate redirects that lead to the download of malicious archives.Microsoft SharePointMSBuild/C# project files, and hosting payloads on Azure Blob Storage, Google Drive, and compromised SharePoint—while expanding operations to Middle Eastern targets in early 2026.MSBuild.exeThe group repeatedly modified its infection techniques—abusing Cloudflare Turnstile, OAuth redirects, MSBuild/C# project files, and hosting payloads on Azure Blob Storage, Google Drive, and compromised SharePoint—while
Industries
Diplomacyand Mongolia, is consistent with a renewed intelligence-collection focus against EU and NATO-affiliated diplomacy entities,” Proofpoint said.GovernmentSince mid-2025 the China-aligned actor TA416 has resumed targeting European government and diplomatic organizations using web bugs and evolving malware delivery chains.